


Restrict Content Pro REST API - WordPress Plugin
This add-on provides a complete RESTful API that allows for developers and external applications to interact with membership data in Restrict Content Pro.

Plugin Features
The plugin is an addon designed for membership data interaction for Restrict Content Pro, enhancing its capabilities in managing user access to content based on membership levels. By utilizing REST API, it enables seamless communication between different systems, allowing for secure and efficient data exchange and integration. With this functionality, users can automate various processes related to membership management and content restriction, providing a more streamlined and dynamic user experience.
It integrates seamlessly with Restrict Content Pro, empowering website owners to extend the functionality of their membership sites by leveraging REST API capabilities. This integration opens up a plethora of possibilities for developers and site owners to customize and enhance the way membership data is handled and accessed. The plugin offers a robust set of features that enable efficient handling of user roles, access permissions, and content restrictions through smooth integration with REST API endpoints.
By incorporating this addon into your website, you can elevate the level of control and flexibility in managing membership data and content restrictions. It enables you to create personalized user experiences based on membership levels, granting access to exclusive content or features seamlessly. This leads to a more engaging and tailored interaction with users, fostering loyalty and increasing the value proposition of membership offerings on your site.
Moreover, Restrict Content Pro REST API REST API integration simplifies the process of data retrieval and manipulation, allowing for a more dynamic and responsive membership management system. Users can benefit from real-time updates on their membership status, access rights, and personalized content recommendations, enhancing user engagement and retention rates. The seamless communication facilitated by the REST API ensures a cohesive user experience across different platforms and devices, improving accessibility and usability for members.
In conclusion, this addon for Restrict Content Pro plays a pivotal role in enhancing the functionality and performance of membership sites by leveraging the power of REST API. It empowers site owners to create a more personalized and interactive environment for their members, optimizing the management of user access and content restrictions. By integrating this addon into your website, you can unlock a new realm of possibilities for managing membership data and delivering exceptional user experiences.
Specifications:
| Release date: | 11-10-2019 | |
| Last updated: | 25-02-2026 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Access & Security for Restrict Content Pro | |
| Compatibility: | W5.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | Restrict Content Pro | |
| Rating: | ||
Share with your friends!
A Guide to Restrict Content Pro REST API for Protected WordPress Data
Restrict Content Pro REST API is not about adding a nice-looking block to a page. It is for technically connecting a membership site to external services, user portals, reports, mobile apps, and internal tools. In this guide, we will look at how to approach installation and REST access testing, which Restrict Content Pro and WordPress settings matter before the first request, how to safely test responses, and where access logic most often breaks down.
This guide is intended for membership site owners, WordPress administrators, and developers who need to connect protected content, members, access levels, and an external system without manually exporting tables. We will not repeat the general description of a membership plugin. What follows is a practical implementation map, along with testing steps, diagnostics, and criteria you can use to decide whether this API belongs in your project.

The main idea is simple: a REST integration is only useful when the core membership model is already configured and understood. If access levels, member statuses, registration pages, and content restrictions behave inconsistently in a normal browser session, the API will not fix that. It will only expose the same problem in a different form, such as an empty response, an access error, an incorrect member status, or an overly heavy request.
What Problem the API Solves on a Membership Site
Standard Restrict Content Pro protects pages, posts, content fragments, registration forms, and account areas inside WordPress. That is enough when the entire user journey lives on one site: a visitor signs up, pays for access, reads protected content, and manages a profile on the plugin's built-in pages. The API becomes necessary in a different scenario, when the membership site must exchange data with a system that is not a normal WordPress page.
Typical use cases include an external portal checking whether a member is active, a support team wanting to see the member's access level next to a ticket, an editorial team building a report on active subscribers, a mobile app showing only the content available to the current user, or an internal dashboard quickly finding a member by email and updating an internal field. For those tasks, manual CSV exports are inconvenient because the data becomes outdated too quickly.
Restrict Content Pro REST API should be treated as an integration layer, not as a replacement for membership settings. It does not override WordPress rules, user roles, member statuses, or content restrictions. On the contrary, the API must respect those rules: if a user is not allowed to see protected content in the standard site experience, an external client should not receive it through JSON just because the request came through a different URL.
One important product-specific detail is that public documentation for the old standalone add-on page is not as easy to access as it should be. When planning an implementation, do not rely on hearsay about specific endpoints. Instead, verify the actual route on the installed site through the REST API root, the namespace list, and test requests. That is standard engineering practice in WordPress: the REST API documentation itself describes discovering site capabilities through /wp-json/ and the namespaces list.
When the API Is Actually Necessary
The API is justified when data exchange is ongoing and repeatable: an external app frequently reads statuses, creates records, syncs profiles, or builds reports. If the task happens once a month and does not require writing data back, the built-in member export or a careful admin report may be enough. API implementation adds responsibility: you need to store access keys, restrict roles, log errors, and understand which data is leaving the site.
- An external service needs to regularly check whether a user has an active membership.
- The support team wants to see a member's status quickly without logging into WordPress.
- An editorial or sales team builds reports by access level, payments, or registrations.
- A mobile app or separate storefront must display content according to the same rules as the site.
- You need to connect membership data with a CRM, learning platform, analytics system, or internal portal.
When Not to Start with the API
If the site has not gone through basic membership logic setup yet, the API will only make diagnosis harder. First, you need to make sure a normal user in a browser sees registration, the account page, protected content, the restriction message, membership status, and post-access-change emails exactly as expected. Only then does it make sense to connect an external system.
Another weak scenario is trying to use the API as a shortcut to data without a proper permissions model. That is the wrong approach. An external client should act on behalf of a user or a technical account with clearly defined capabilities. If you give the integration administrator rights just to launch faster, it will be much harder later to prove that access to members and payment history is limited to the minimum necessary scope.
What to Check Before Installation and the First Request
Preparing for Restrict Content Pro REST API does not start with Postman or with code. Start by checking the foundation: is the base membership plugin installed, is WordPress REST API working, are permalinks enabled, are access levels configured correctly, and is there any caching conflict? The API depends on this environment, so a problem at the base layer will almost always show up in the external request as well.
At this point, the Restrict Content Pro product line is tied to Kadence Memberships and the Liquid Web/Nexcess ecosystem. On WordPress.org, the plugin is listed as Kadence Memberships, but the name Restrict Content Pro still appears in interfaces, older links, knowledge base articles, and user discussions. In practical terms, that means one thing: do not verify only the ZIP filename. Also check the actual menu item, active add-ons, database version, and whether the required functionality exists in the installed instance.
Minimum Technical Checklist
| Check | Why it matters | What counts as a normal result |
|---|---|---|
| WordPress REST API | Without a working /wp-json/, the client will not see the product routes. |
The API root opens, returns JSON, and includes wp/v2. |
| Permalinks | Some sites use the fallback ?rest_route=/, and the client needs to account for that. |
API URLs work reliably under the chosen permalink structure. |
| Membership levels | The API is meaningless if statuses and levels do not reflect actual access. | A test member has the correct level and Active status. |
| Content restriction | You need to confirm that standard viewing and REST responses follow the same permission rules. | A guest sees the restriction, and a member sees the allowed content. |
| Caching and optimization | Cache may serve a protected or outdated page version to the wrong user. | Account, registration, and protected content pages are excluded from aggressive caching. |
A Dedicated Role for the Integration
You should not use the site owner's personal account for the API. Create a separate user with the minimum sufficient role and a clear name, such as integration-reports or crm-sync. If the integration only needs to read reports, it does not need full administrator capabilities. If the product routes in a specific setup still require elevated permissions, document that in the project documentation and compensate with stricter key storage, IP restrictions at the server or gateway level, and regular access rotation.
Safe rule: before connecting an external client, verify what data it needs to see, what actions it must perform, and who is responsible for revoking access. An API key created "just in case" with maximum permissions almost always turns into technical debt.
Installing and Running an Initial Restrict Content Pro REST API Check
The installation process depends on how the product is available in your setup: as a separate add-on from the older Restrict Content Pro line, or as part of the Pro features in Kadence Memberships/Restrict Content Pro. In both cases, the validation order is the same: activate the base plugin, confirm that membership functionality works on the site, then activate the API component and verify that routes appear in the REST index.
Do not start on the live site if the integration will create or modify members. It is better to spin up a staging copy, create a test membership level, a test user, one public page, and one protected post. That gives you a clear dataset for comparing browser behavior and API behavior without risking real profiles.
General Installation Order
- Make sure the base Restrict Content Pro or Kadence Memberships plugin is active and does not show critical notices in the admin dashboard.
- Create or verify at least one membership level, a test member with Active status, and a protected post tied to that level.
- Upload and activate the REST API component through
Plugins-Add New-Upload Pluginif it is delivered as a separate ZIP package. - Open
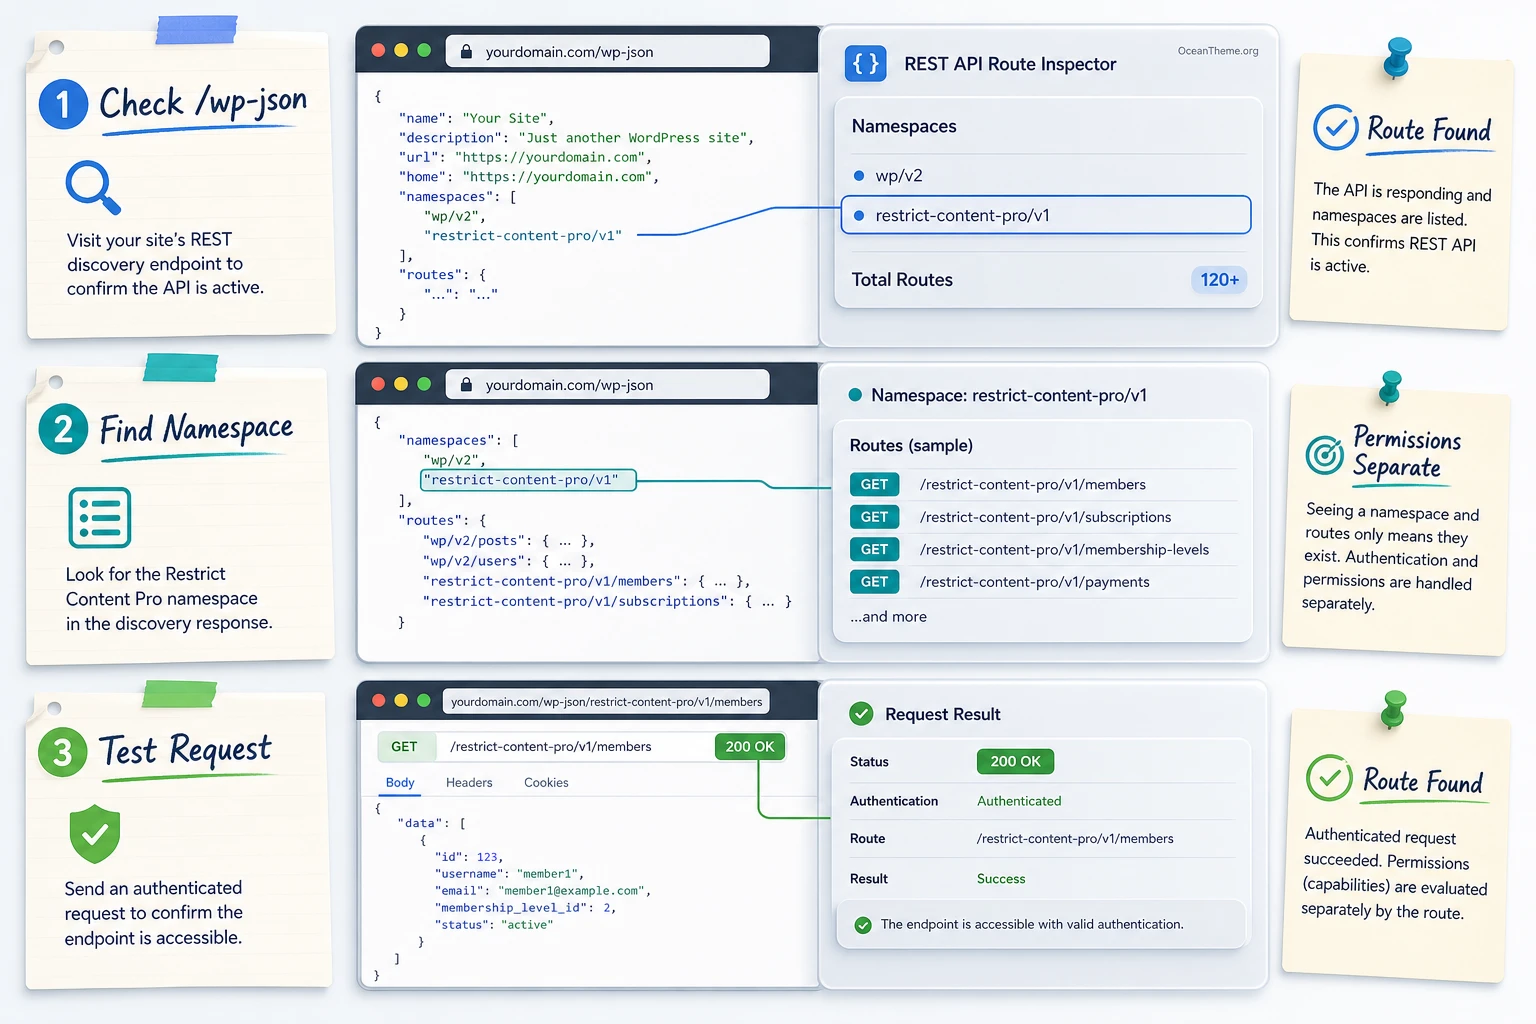
/wp-json/on the same domain and check whether product routes or a namespace related to Restrict Content Pro appears. - Test one safe GET request as the technical account, without sharing real keys in chats, tickets, or public logs.
If you do not see a new namespace after activation, that still does not prove the product is broken. Possible reasons include the component not being part of the current package, the route only being registered when the Pro core is active, the site blocking REST API, a conflict with a security plugin, or the current user not having permission to see part of the schema. So the correct sequence is to check the base WordPress routes first, then the presence of custom namespaces, and only then permissions.
Quick Check Without Exposing Secrets
Two requests are enough for an initial check. The first shows that WordPress REST API is responding at all. The second shows that authentication works. The article intentionally uses placeholders instead of real keys.
GET https://example.com/wp-json/

curl --user "api-user:APPLICATION_PASSWORD" \
  "https://example.com/wp-json/wp/v2/users/me?context=edit"
If the second request returns the current user and does not respond with an access error, authentication is working at the WordPress level. The next step is to replace the test WordPress route with the actual Restrict Content Pro route that appears in your site's index. Do not guess the endpoint from someone else's example if your current installation shows a different namespace.
Authentication, Permissions, and a Safe Access Model
WordPress REST API supports several authentication methods. Inside the admin dashboard, requests use cookie authentication and the wp_rest nonce. For external services, application passwords are usually more convenient: they are created in a user's profile, passed over HTTPS through Basic Auth, and can be revoked without changing the main password. This is not an "admin secret." It is a separate application password that should live in the external system's secret store.
When working with Restrict Content Pro REST API, it is important to separate two checks. The first is "who is making the request." The second is "what that subject is allowed to do with membership data." A successful login through an application password does not automatically grant permission to read payments, change membership levels, or view protected content. If the product routes use WordPress capabilities or their own access checks, the technical account must satisfy those requirements.
Cookie Authentication, Application Password, or a Separate Gateway
Cookie authentication is appropriate for inside-WordPress scenarios: a custom admin dashboard block, an internal settings page, or custom JavaScript that runs for a logged-in user. It is not suitable for a server-side CRM integration or a mobile app because it depends on a user session and a nonce.
Application passwords work well for server-to-server communication. Their advantage is straightforward access revocation and no need to pass the main password. The downside is that their scope is still tied to user capabilities. If you need a stricter model, place the external service behind your own intermediary layer: it stores the key, normalizes responses, limits operations, and does not expose direct WordPress access to clients.
For public mobile apps and external storefronts, do not embed an application password in client-side code. Anything that ends up in an app, browser, or public repository should be treated as exposed. In those cases, requests should go to your server-side layer first, and only then to WordPress.
How to Minimize Permissions in Practice
- Create a separate user for each integration instead of one shared key for every service.
- Name the application password by purpose:
CRM read-only sync,Reporting dashboard,Support lookup. - Store the key in environment variables, a secret store, or server settings that are not exposed through a public repository.
- Limit the operations on the external application side: if a service only reads statuses, do not add a screen for changing membership levels.
- Review the key usage log and revoke the application password after testing ends or when a contractor changes.
If the integration needs to write data, create a separate rollback test: create a member, change a field, verify the result in the admin dashboard, then restore the original state. Without a rollback procedure, any bulk API operation is risky.
How to Build an Endpoint Map Without Guessing
The most common mistake with a lightly documented API is to take an endpoint from an old blog post, paste it into the client, and try to bend the site around someone else's example. In WordPress, the better approach is discovery. The /wp-json/ root shows which namespaces are registered. Each namespace contains routes, methods, arguments, and sometimes the response schema. Even if product documentation is incomplete, the installed site still gives you a baseline map.
Your job is to turn that map into a short internal document. It should answer not "which URL should we try," but "which entities are available, which methods are allowed, which permissions are required, which fields are returned, which errors are expected, and which data must never be sent outside."
What to Look for in the REST API Index
Open the root JSON and find the namespaces block. It should include standard namespaces such as wp/v2 and, if the component registered its routes correctly, an additional product namespace. The name may vary by version and implementation, so the guide should not lock in an unverified string as an absolute fact. Then review the routes block and write down only the routes related to membership.
For each route, it is useful to record:
- Purpose: reading a member, listing levels, checking a payment, changing a status, or performing an internal action.
- Methods:
GET,POST,PUT,PATCH,DELETE. - Parameters: user ID, email, membership level, status, pagination, date filter, or search string.
- Permissions: which WordPress role or capability is required for reading and writing.
- Response: which fields the external client needs and which it should avoid storing.
Do Not Pull the Entire JSON If You Only Need One Status
WordPress REST API supports the global _fields parameter, which lets you request only the fields you actually need. That is especially important on a membership site: member, payment, and profile data may be sensitive, and large responses increase load on both the database and the network. If the external service only needs an ID, status, and access level, there is no reason to keep the full user object or payment history.
GET /wp-json/example-namespace/v1/members/123?_fields=id,status,levelThis example illustrates the principle, not the exact namespace on your site. After installation, replace example-namespace/v1 with the actual route from your REST index. The core practice is simple: discover the route first, then narrow the response to the minimum required fields.

Post-Installation Setup: From Membership Logic to an API Contract
Once the component is activated, it is not enough to say "the API works." For a real project, you need a contract: which data is the source of truth, how the external service matches users, how statuses are handled, and what happens when an error occurs. Otherwise, the integration may technically send requests while the business outcome remains unpredictable.
Membership Levels and Statuses
Start by checking which membership levels are used in the project and how they are named in the admin dashboard. Do not tie external code to the visible level name if a stable identifier exists. Editors, marketers, or translators may change the label, but the identifier is usually more stable. Your internal document should keep a mapping of "WordPress level" - "role in the external system" - "which content or feature is unlocked."
Member statuses should be handled explicitly. Active, Pending, Expired, Cancelled, and similar states should never be treated as the same thing. If a person has registered but is not yet approved, the external service must not treat them as a full member. If the membership has expired, it is better to show a clear message and a link to the account page instead of a blank screen.
User Fields and Personal Data
API integrations often begin with email because it is a familiar key for CRMs and support tools. But email can change. If the external service can store a WordPress user ID or member ID, use that as the primary key and keep email only as a searchable attribute. That reduces the risk of associating data with the wrong person after an address change.
Do not export more data than necessary. In a CRM, a name, email, membership status, and access level may be enough. Payment history, addresses, internal notes, and technical fields should only go where they are truly needed and where proper data handling rules are in place.
Cache, Protected Content, and REST Responses
On WordPress.org, the current plugin explicitly states that restrictions are applied to REST API requests as well. The changelog also includes fixes related to how protected posts are removed from WP REST API when the hide restricted posts option is enabled. The practical takeaway is that you should test not only the standard post page, but also the JSON responses for the posts list and for an individual post.
If the site uses caching at the plugin, server, or CDN level, exclude account, registration, checkout, and any endpoints where the response depends on the user. A cached public response for protected content can produce false results: a member may see the guest version, a guest may see an outdated fragment, and an external client may receive data for the wrong state.
Verification After Every Change
After changing an access level, member status, hidden-post setting, or cache exclusion, run three checks: a guest in a private window, a test member in a browser, and the technical account through the API. Only when all three results match can you say the access model is working end to end.
Quick setup summary: the API contract should describe not only the URL and method, but also the meaning of each status, the minimum field set, caching rules, the user matching method, and how the external client is expected to react to access denial.
Practical Scenario: Checking Member Access from an External Portal
Imagine a site with a protected lesson library. A user registers in WordPress, receives membership through Restrict Content Pro, and a separate external portal should show an "Open Materials" button only to active members. The task looks simple, but it exposes the main risks: authentication, user matching, membership status, caching, and proper error handling.
Goal
The external portal should find the member by email or stored identifier, verify the status and access level, and then display the allowed action. If access is not active, the portal should explain why: no membership, membership pending approval, membership expired, or user not found.
Preparation
- A test membership level such as "Library Access" has been created on the staging site.
- There is one test user with Active status and another with Pending or Expired status.
- WordPress REST API responds at
/wp-json/, and the product routes are visible in the index. - An application password has been created for the technical account, and the key is stored in environment settings rather than in code.
Implementation Steps
- The external portal sends its request to your server-side layer, not directly from the browser to WordPress with a secret.
- The server-side layer calls WordPress REST API and looks up the member by a stable identifier or email.
- The response is normalized: the external portal receives only
member_id,status,level, and an internalcan_accessflag. - If
can_accessis true, the portal shows a button linking to the protected section. - If access is denied, the portal shows a short explanation and a link to the WordPress account page.
In this scenario, there is no need to pass the full user object into the external portal. There is also no need to let client-side JavaScript read membership data directly from WordPress. The less data and fewer secrets that leave the server-side layer, the easier security is to control.
Verifying the Result
Verification should be both technical and user-focused. For an Active member, the external portal shows access, and the protected page in WordPress opens after login. For a Pending member, the portal explains that access has not been activated yet, and the protected page itself remains unavailable. For an Expired member, the portal suggests going to the account or renewal page, but it does not display protected materials.

A Detail People Often Miss
If access changes because of a payment, manual approval, or a user import, the external portal may receive outdated results. The fix is either short-term status caching with a clear TTL or an event-based check. For critical actions, such as viewing a protected lesson or issuing a certificate, it is better to run a fresh check right before the action instead of relying on a status saved earlier in the day.
Site Result and External Service Result: How to Tell Everything Works
A successful API installation is not the same as a successful implementation. You need a validation matrix that confirms the same rule from different angles. If a member is active, they should see protected content in the browser, appear in the admin dashboard with the correct status, and be returned as active through the API. If a member is not active, all three layers should consistently deny access.
Browser Check
Open the protected page in a private window as a guest. You should see a restriction message or a login form, depending on the settings. Then log in as a test member with the required level and confirm that the same URL displays the protected content. After that, log out and clear the page cache. This confirms the base Restrict Content Pro logic without involving the API.
REST Response Check
Open the API request for the same entity. In a public posts list, protected content must not suddenly expose private data. For an authenticated request, the response must match the current user's permissions. If the hide restricted posts setting is enabled, separately verify that the protected post disappears from the list in guest context.
External System Check
The external service should display exactly the result that follows from WordPress. Do not replace an access error with a generic "something went wrong" message. For both support staff and end users, it is important to distinguish between an invalid API key, a user not found, a user found but not active, a route not found, a WordPress server error, or a request that took too long.
| State | Browser | API | External portal |
|---|---|---|---|
| Guest | Sees the restriction. | Does not receive protected content. | Prompts the user to log in or sign up. |
| Active member | Sees content for their level. | Receives allowed data. | Shows the available action. |
| Pending or Expired | Sees a restriction or account message. | Is not treated as active. | Shows the reason without exposing content. |
API Performance on Large Sites
A membership site with a few hundred posts usually will not notice the load from test API requests. The picture changes with a large archive, a lot of metadata, complex restrictions, active search, and an external system polling lists every few minutes. On the WordPress.org support forum, there is a recent example of a complaint about a heavy REST request related to filtering protected content and a large volume of postmeta. That does not mean every site will have this problem, but it is a strong signal: the API should be designed as a workload, not as an unlimited data pipe.
WordPress REST API supports pagination and field selection. Use both whenever you read collections. Do not request "all members," "all posts," or "all payments" in a single call when the dataset is large. Batch synchronization should run in small pages and track the last processed identifier or modification time.
What Reduces Load
- The
_fieldsparameter, so you do not build unnecessary parts of the response. - Pagination through
pageandper_pagewhen the route supports it. - Filtering by changed data instead of scanning all members every time.
- Server-side caching in the external application for non-critical reference data, such as the list of levels.
- Separate requests for checking one user instead of heavy searches across all records.
When You Need a Developer
If opening /wp-json/wp/v2/posts or a product route produces a slow SQL query, heavy database load, or timeouts, do not try to fix it blindly by raising limits. What you need is analysis: what meta queries are being built, whether indexes exist, whether the hide restricted posts setting is enabled, how much data is in wp_postmeta, and which plugins are adding filters to REST requests. In some cases, the safer move is to temporarily reduce external sync frequency and move heavy reporting into a background task.
Practical speed check: measure not only API response time, but also the effect of the request on normal site pages. If one external report slows down member registration, the integration has been designed too broadly.
Integration Scenarios Where the API Delivers Real Value
An API component only makes sense when it supports a specific workflow. For Restrict Content Pro REST API, there are several such workflows, and each needs its own validation logic. Do not build a generic "sync everything" system that reads users, posts, payments, levels, and settings without a clear purpose. It is better to define one scenario, make it stable, and only then add the next one.
Support Sees the Member Status
This is one of the clearest use cases. A customer contacts support, the agent sees the email in the ticket, and needs to understand quickly whether access is active. The API request finds the member and returns a brief status, membership level, and a link to the profile in WordPress for the administrator. The agent does not receive payment details and cannot change membership from the helpdesk system unless the workflow explicitly requires that.
An important check here: if the member is not found, the system should not automatically create them in WordPress. User creation is a separate action with separate responsibility. For support, statuses like "found," "not found," "access active," "access inactive," and "check required in the admin dashboard" are often enough. That keeps the integration simple and prevents it from becoming a source of accidental duplicates.
CRM Receives Only an Access Confirmation
A CRM usually does not need the full membership model. It only needs to know whether a contact belongs in the active member segment, what level the person has, and when it makes sense to send a service message. If the CRM pulls the full WordPress user object, it starts storing unnecessary personal data and makes internal access control harder to manage.
A narrower contract works better: the CRM sends a stable identifier or email, the server-side layer asks WordPress, and returns a normalized result. If the CRM supports webhooks or background jobs, synchronization can run on a schedule in small batches. If it does not, it is better to check status on demand when a manager opens a contact card or when a specific email flow starts.
An External Learning Portal Checks Lesson Access
If lessons are physically hosted outside WordPress in an external portal, Restrict Content Pro remains the source of membership access. In that case, a general Active status is not enough. You need to map the membership level to a specific set of lessons. For example, one level unlocks the basic library, another unlocks the library plus consultations, and a third unlocks the recording archive. The external portal should verify not just "is this user active," but "does this user have access to this section."
This kind of scenario is best documented as a permissions table. The first column is the membership level in WordPress, the second is the external section, the third is the user action, and the fourth is the expected denial response. If a level changes, update the table first, then the external portal tests, and only after that the production configuration.
Reporting and Analytics Without Direct Database Access
Sometimes site owners want to connect a BI dashboard directly to the WordPress database because it seems "faster." On a membership site, that is risky: the table structure may change, meta fields are not always obvious, and direct database access bypasses the plugin's business rules. An API or a separate server-side reporting layer is safer if it returns an agreed set of fields and does not expose extra data.
Reporting especially needs volume limits. Export aggregated data if the external dashboard does not need a full list of users. If it does need the list, make the export paginated and store the last sync point. A report that rereads the entire member archive every hour will almost certainly become a problem as the site grows.
A good API scenario can be described in one sentence: "which system asks for which data in order to make which decision." If that sentence falls apart into ten unrelated tasks, the integration should be split.
Documenting the API Contract for the Team
After the first successful requests, stop and write down the contract. Otherwise, a few months later nobody will remember why that particular user was chosen for the application password, which endpoints are considered production-safe, which fields the external system is allowed to store, or what a given error means. The documentation does not need to be long, but it does need to be specific.
What to Include on the Internal Project Page
- Integration purpose: CRM, support, external portal, reporting, or another specific task.
- Responsible owner: who can change the key, disable the integration, and approve expanded access.
- Technical account: username without the password, role, purpose, and secret storage location.
- Route list: actual endpoints from
/wp-json/, methods, parameters, and expected response codes. - Response fields: what the external system stores, what it only reads, and what must never leave WordPress.
- Test users: at least one Active user, one Pending or Expired user, and one user with no membership.
- Rollback plan: how to revoke the application password, disable the external client, and verify that data is no longer changing.
This document helps more than just the developer. Support understands what to inspect when a complaint comes in. The site owner understands which data leaves WordPress. The administrator knows which key can be revoked without shutting down the whole site. And a new contractor does not have to start by guessing from old code.
Test Data Instead of Experiments on Real Members
API work always requires test members. Create several internal users with clear email addresses on the project domain or in a test environment. One should have active access, one should be awaiting approval, one should have expired or cancelled membership, and one should have no membership at all. That gives you a safe way to verify every logic branch without touching real accounts.
If the project involves payments, do not use real payment data to test the API. Internal statuses and a payment gateway sandbox are enough if one is needed. The API client should respond correctly to the state without attempting a real payment or creating a live order. For this guide, the key point is access verification, not a walkthrough of purchasing the product or processing payments.
Change Control
Any API contract change should be treated like a small release. Add a field and check whether the external service started storing too much. Change a status and confirm that Pending did not suddenly become Active in the CRM. Change the technical account role and rerun both the authentication test and the access denial test. Update Restrict Content Pro or Kadence Memberships and reopen the REST index to make sure routes and permissions have not changed unexpectedly.
The most useful habit is to keep the date of the last manual verification next to the contract, but not expose it in the public guide. The team needs it internally, while the reader on the product page needs to understand the process: where to check the route, how to confirm permission, how to narrow the response, and how to identify the cause of an error.
Safe Improvements Without Editing Core Files
For Restrict Content Pro REST API, do not add random PHP snippets from old forum posts. Public, confirmed extension points for this specific API component should be verified against the installed version and documentation. If you do not have that confirmation, it is safer to stay with WordPress settings, the server-side layer, and the external application. Below are improvements that do not require editing WordPress core, the plugin, or the theme.
Server-Side Normalization Layer
The best upgrade for an external storefront is an intermediary backend that stores the secret, calls WordPress, strips unnecessary fields, and returns a minimal response to the client. This is especially important for mobile apps and single-page interfaces. The user's browser should not see the application password or the full member JSON.
// Pseudo-schema of the server response for the external portal
{
  "member_id": 123,
  "status": "active",
  "access_level": "library",
  "can_access": true
}
Verification: compare this normalized response with the admin dashboard and the protected page. Rollback: disable the external layer and return the portal to a "check access in your account" message without changing any WordPress data.
Integration Error Log
Log technical context rather than personal data: time, route, response code, duration, request ID, and error type. Do not log the application password, the full user object, or payment details. If support needs to investigate a problem, a correlation ID and a response status are usually enough.
A Documented Access Revocation Checklist
Create a short internal procedure: where the application password was created, who owns the integration, how to revoke the key, what to disable in the external service, and how to verify that requests have stopped. It is not code, but it is exactly the kind of document that saves a project when a contractor changes or one of the services is no longer needed.
Diagnosing REST API and Membership Access Errors
API errors are easiest to troubleshoot as a chain: symptom - cause - check - fix. Do not begin with reinstalling the plugin. First determine whether the failure is in standard browser access, WordPress authentication, the product route, or the external logic.
Route Not Found or Namespace Missing
Symptom: /wp-json/ responds, but the expected Restrict Content Pro route is not there. Possible causes: the API component is not activated, the feature exists only in another package, the base Pro plugin is inactive, the site is blocking route registration, or you are looking for an old namespace name. Check the active plugin list, the product package, and the root REST index. The fix is to activate the required component, refresh permalinks, temporarily disable the REST API blocker that is causing the conflict, and reopen the index.
Access Error with the Correct Application Password
Symptom: the request passes Basic Auth, but the product endpoint returns a denial. The cause is often not the password, but the user's permissions. The technical account may be authenticated while still lacking the capability to read or modify membership data. Check the request to /wp-json/wp/v2/users/me?context=edit, the user's role, the requirements of the specific route, and the result in the admin dashboard. The fix is to grant the minimum sufficient role or change the architecture so that write operations happen only through a trusted server-side layer.
An Active Member Still Cannot See Protected Content
Symptom: the user is logged in but still sees the restriction message. In support discussions, similar cases are often tied to member status, the selected level, the restriction settings on the page, a theme conflict, or caching. Check for Active status, the correct membership level, the Restrict This Content block, clear the cache, and temporarily test with a minimal plugin set and a default theme. Roll back the most recent change made before access became inconsistent, whether that was a cache rule, a user import, a bulk level change, or a conflicting plugin.
The REST Request Is Too Heavy
Symptom: a list of posts or members loads slowly, the database receives a complex query, or the server returns a timeout. The cause may be large metadata tables, the hide restricted posts setting, complex filters, or an external client requesting too much data. Check the response size, the per_page and _fields parameters, sync frequency, and server logs. The fix is to narrow the response, split traversal into pages, cache reference data, and move heavy reporting into background jobs.
The External Service Shows an Outdated Status
Symptom: in WordPress, the member is already active or expired, but the external portal still shows the old state. Possible causes include external service caching, delayed background synchronization, an email-based matching error, or an unhandled post-payment or post-approval status. Check the source of truth in the admin dashboard, the user identifier, the time of the last synchronization, and a fresh API request. The fix is to use a stable ID, shorten cache duration for critical statuses, and run a fresh check before important actions.

Questions to Answer Before Launching Restrict Content Pro REST API
Can the API be used before membership is configured?
Technically, some routes may respond after the component is activated, but there is little practical value in that. First set up the levels, test members, protected pages, and restriction messages. The API should validate a working model, not replace it.
How do I find the exact list of endpoints?
Open /wp-json/ and review namespaces and routes. WordPress REST API is intentionally built around discovery. If the product's public documentation is incomplete, the actual REST index of the installed site becomes your main technical reference point.
Is it safe to use an application password?
Yes, if it is created for a separate technical account, transmitted only over HTTPS, stored in a secret store, and can be revoked. It should never be embedded in browser JavaScript, a mobile app, or a public repository.
Why does the API return a denial if the login and password are correct?
Authentication confirms identity, but it does not guarantee permission for a specific route. Check the user's role, the endpoint requirements, the member status, and whether the same action can be performed in the WordPress admin dashboard.
Do I need to disable cache for the entire site?
No. In most cases, it is enough to exclude pages and endpoints whose response depends on the user: account, registration, checkout, protected content, and sensitive API requests. Disabling all caching may hurt performance without providing any real benefit.
Can protected content be exposed to a mobile app through the API?
Yes, but only if the same access rules are enforced as on the site. The mobile app should not store a WordPress secret. It is better to use a server-side layer that verifies the member and returns only the allowed data to the app.
What should I do if there is no exact YouTube tutorial for this product?
Do not embed a random video about general REST API concepts or a different membership plugin. For this topic, your own route map, test scenario, and site-specific diagnostics are more useful than an irrelevant video.
When Restrict Content Pro REST API Is the Right Choice
Restrict Content Pro REST API is a good fit for projects where the membership model is already built on Restrict Content Pro/Kadence Memberships and now needs to be connected carefully to an external service. Strong use cases include validating active access, sending minimal status data to a CRM, support lookup, reporting, server-side synchronization, and separate portals that should not work directly with the WordPress database.
The product may be a poor fit if you are starting a new project and require highly detailed public API documentation, ready-made webhooks, a large number of modern tutorials, and fast support responses about integrations. In that case, it makes sense to compare alternatives before development begins, not after the external portal has already been built.
Before launch, run through a short final checklist: standard browser access works, the REST index shows the required routes, the technical account has minimum permissions, the external service receives only the fields it needs, cache does not break user-specific responses, and diagnostics are documented in the project notes. After that, you can download Restrict Content Pro REST API and test the integration on a staging site.
The main selection criterion is not the mere presence of a REST API, but predictable behavior. If you can explain which request is being made, on whose behalf, which data is returned, why access is allowed or denied, and how to roll back a change, the product becomes a practical tool. But if the endpoints are unknown, permissions are too broad, and testing comes down to "it looks like we got a response," it is better to delay the launch and close the technical gaps first.
Final Validation Scenario Before Connecting an External Integration
Before putting Restrict Content Pro REST API into use for an external portal, CRM, mobile app, or internal support tool, it is worth walking through one short end-to-end scenario. The goal is not to formally confirm that "the API responds," but to make sure the integration sees exactly the data it should see, handles restricted access correctly, and does not break the behavior of paid subscriptions.
Start with a separate test user who has a regular subscriber role rather than administrator privileges. Assign the access level that will be used in the real-world scenario, then test requests to the required REST endpoints from the external system or API client. The response should include only the expected fields: member identifier, subscription state, access level, expiration date, or other data the integration genuinely needs. If the external service asks for extra fields "just in case," it is better to narrow the contract immediately, because it becomes much harder to fix later without breaking already written code.
Be sure to test the negative path separately. Remove active access from the test user, repeat the request, and verify that the integration receives a clear denial rather than an empty success response. This matters especially for protected materials: the frontend or external portal should distinguish between an authorization error, a missing subscription, and a temporary technical issue. If all of those situations collapse into one generic message, support will quickly lose the ability to understand what happened for a specific user.
After a successful check, document the minimum integration contract in the project notes or team documentation: which endpoints are used, which fields are read, which actions are allowed, where the key or token is stored, and who is responsible for replacing it. That small document makes it much safer to update Restrict Content Pro, swap out the external service, and troubleshoot errors without guesswork. On the site side, keep a simple rollback path: the ability to disable the external client, replace the access key, and temporarily return subscription checks to manual verification through the WordPress admin dashboard.

