


Restrict Content Pro Hard Expiration Dates - WordPress Plugin
Restrict Content Pro Hard Expiration Dates is a plugin that enhances the management of restricted content on platforms by enabling precise control over access through fixed expiration schedules. This tool integrates seamlessly with content systems, setting definitive deadlines for restricted materials, thereby automating accessibility based on specified timelines and streamlining user management and subscription workflows.
Plugin Features
This tool stands out by imposing firm expiration limits, granting precise control over the lifecycle of content. By setting non-negotiable expiration dates, administrators ensure adherence to subscription terms, automatically revoking access rights as scheduled, thus reducing manual intervention. This functionality is vital for organizations managing membership-based content or subscription services where timely content access is crucial for operation.
The integration of this tool into existing infrastructures ensures efficient deployment without compromising performance. Users enjoy an intuitive interface that aligns effortlessly with membership strategies, simplifying navigation through date settings and configurations. Automated notifications can be set to alert both administrators and users of impending expirations, fostering transparency and communication.
Beyond basic expiration features, this tool can align content accessibility with business goals. By syncing with marketing campaigns or special releases, it boosts user engagement. Its flexible configuration suits diverse market strategies, benefiting content creators, educators, and publishers who need precise control over content visibility.
Furthermore, the intelligent design minimizes user friction during transactions. The streamlined operational framework automates subscription cycles, allowing administrators to prioritize content quality over access complexity. Whether regulating time-bound educational resources, exclusive content, or limited-time offers, this solution ensures access policies align with organizational goals.
In conclusion, Restrict Content Pro Hard Expiration Dates empowers site owners to manage memberships with precision and efficiency. Its role in enhancing membership retention and satisfaction is significant, supporting business models reliant on secure content distribution. Whether as a standalone solution or part of a broader content strategy, this tool is an essential asset for effective membership management on any WordPress site.
Specifications:
| Release date: | 20-01-2017 | |
| Last updated: | 01-09-2020 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Authoring & Content | |
| Compatibility: | W5.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | Restrict Content Pro | |
| Rating: | ||
Share with your friends!
Guide to Restrict Content Pro Hard Expiration Dates for Fixed-Date Access
Restrict Content Pro Hard Expiration Dates is a narrowly focused add-on for WordPress sites where access to protected content must end on one shared date for an entire subscription level. In the official materials, the product is more often called Hard-set Expiration Dates, so throughout this guide both names refer to the same idea: not an individual term counted from the registration date, but a hard end date for the selected level.

This guide does not repeat the product's short description. Instead, it breaks down the practical workflow: when a fixed date actually makes sense, what to check before installation, where to find the date field in the admin panel, how to test member behavior, and how not to confuse hard expiration with a standard subscription duration.
Special attention is paid to edge cases. With add-ons like this, the most common problem is not the install button but expectations: the site admin assumes that a late registrant will get a full access term, while the product does the exact opposite - it ends access at the same time as everyone else. That is why, before configuring it, you need to understand the membership model, user-facing messaging, payment behavior, and how to verify the result with a test account.
When a Fixed Date Works Better Than a Standard Subscription Term
In the default Restrict Content Pro logic, a membership level usually has a duration. If a user signs up today, their access term is calculated from their registration date or next renewal. Hard-set Expiration Dates changes that meaning: the date is no longer tied to the moment of purchase or registration. Everyone on the selected level reaches the same deadline, even if one person joined at the start of enrollment and another joined right before the end.
A fixed date is useful when the product sells participation in a shared time period rather than an individual subscription term. This matters for cohort-based courses, seasonal clubs, limited-time access to event materials, private libraries available only for the duration of a project, corporate training with a common end date, and programs where all participants must lose access at the same time.
Good-Fit Scenarios
The clearest example is a course cohort. A membership level may unlock lessons, webinar recordings, a private homework area, and a page with final materials. If the cohort ends on one shared day, a late participant should not get an extra month simply because they registered later. In that case, the standard duration logic would create different end dates, while Hard-set Expiration Dates keeps one shared deadline.
Another scenario is a seasonal club or temporary community. Members may join during the active period, but access to the forum, archive, and bonus materials closes for everyone at the same time. This approach is useful when a new level or new cohort opens after the season ends, and the old access should no longer continue.
It also fits access to event materials: a conference, marathon, intensive program, or private review session. Users are clearly told that the materials are available until a shared end date. In the admin panel, this is easier to manage at the membership level than manually editing dates for dozens of members.
When This Logic Can Cause Problems
If you sell a full access term starting from the moment of payment, a fixed date may trigger support questions. A user who pays late in the period will get less time than someone who joined at the beginning of enrollment. That is acceptable only when the condition is clearly explained in advance on the registration page and in emails.
You should not use Hard-set Expiration Dates as a replacement for full renewal management, installment plans, plan upgrades, or individual exceptions. If each person needs their own end date, it is better to keep the standard level duration, manual membership editing, or another tool designed for individual dates.
| Model | How the End Date Is Calculated | Where It Fits | Main Risk |
|---|---|---|---|
| Standard level duration | Based on the individual member's registration, payment, or renewal date. | Subscriptions, clubs with a full individual term, ongoing access. | Different people end up with different expiration dates. |
| Hard-set Expiration Dates | One date is set for the entire membership level. | Cohorts, seasons, events, shared access deadlines. | A late participant may get only a short access window. |
What to Check Before Installation: Levels, Content, and the Expiration Scenario
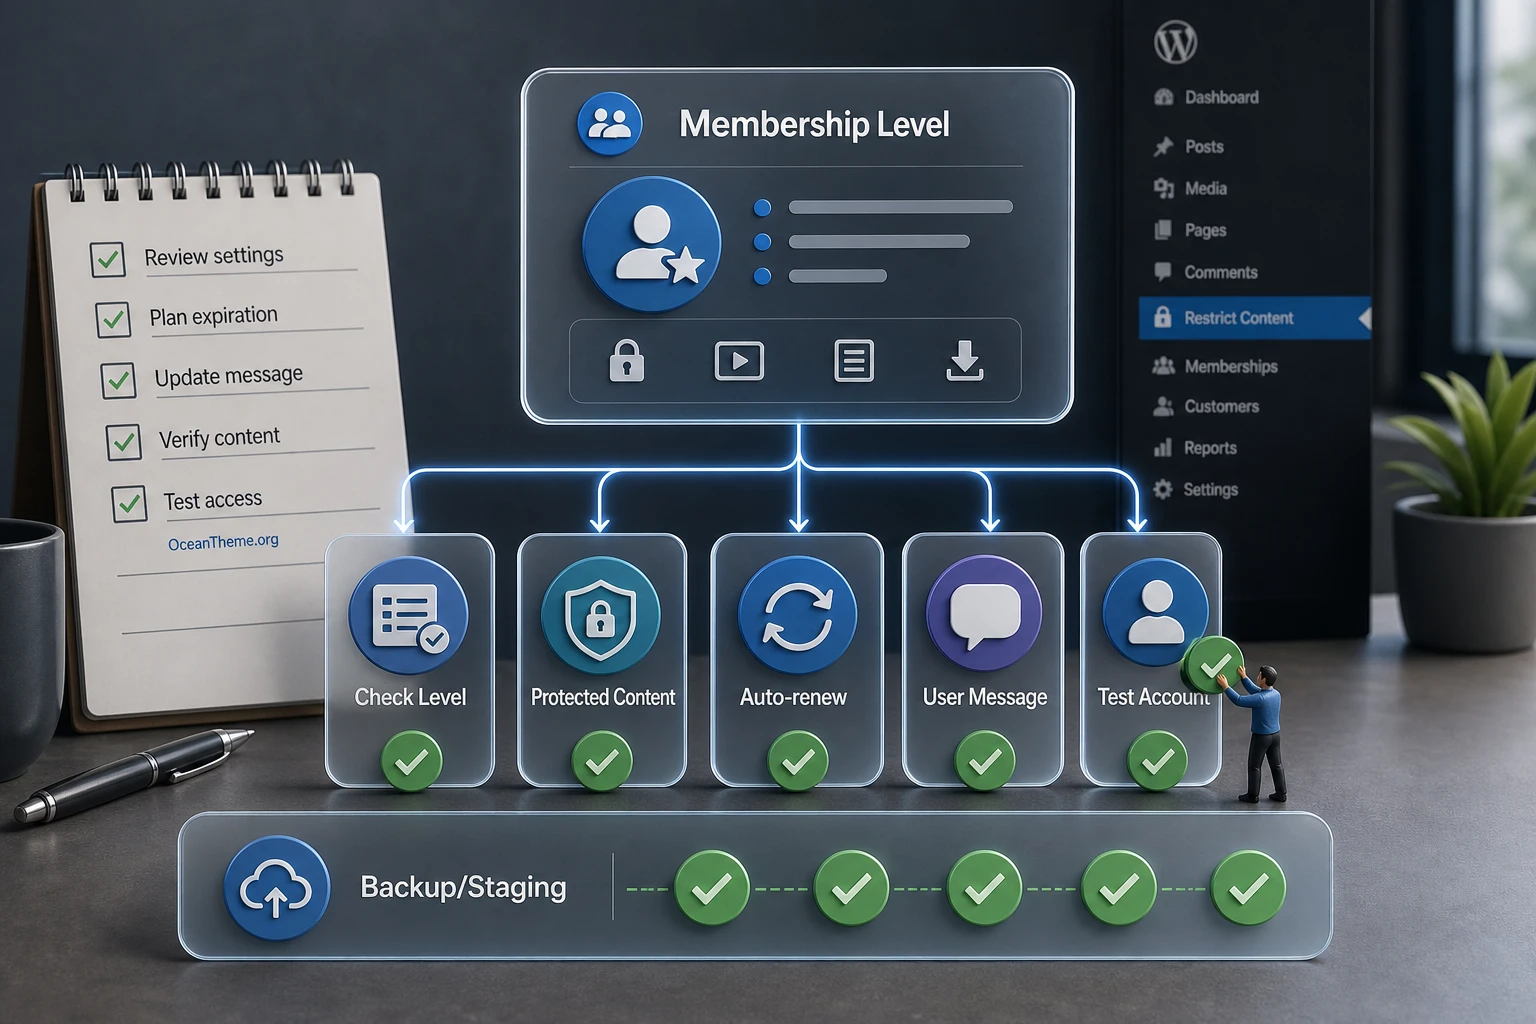
Before installation, do not start with the date field. First, you need to understand which members and which materials are tied to the membership level. Restrict Content Pro can limit access by membership level, access level, user role, paid status, and shortcode. If those options are mixed on the site, one hard expiration date will not explain all access behavior.
Identify the Exact Membership Level
Open the list of levels in the admin panel. In older documentation, the path may be shown as Restrict > Subscription Levels; in newer interfaces, you will more often see Restrict > Membership Levels. The meaning is the same: you are editing the level object, not an individual user.
Write down the level name, its ID, current duration, price, user role, and status. This is not just for formality. If you decide to roll the setting back after testing, you should have a clear record of which parameter was changed and which members were affected.
Check How the Content Is Protected
Go to several key pages in the course, library, or restricted section. In the access restriction block, check whether the page is limited by a specific membership level, paid status, access level, or role. If a page is restricted only by user role, membership expiration may not produce the result you expect, because role and membership are not always used the same way.
If shortcode blocks are used, verify their parameters. For example, content may be restricted like this:
[restrict subscription="123"]Protected content for the selected level.[/restrict]The level ID is more stable than its name: if the level name is renamed later, the ID will stay the same. But do not leave placeholder IDs in live content. Use the actual level number from your site.
Review Payment and Renewal Behavior
Hard-set Expiration Dates affects access, but it should not be treated as a universal payment schedule editor. Restrict Content Pro documentation separately notes that changing the expiration date on a membership with auto-renew may not change the next billing date at the payment provider. That is why levels with recurring payments require a separate check: what is stored in RCP, what is visible in Stripe, PayPal, or another gateway, and what emails the user receives.
Working rule: first configure the fixed date on a site copy or test level, then verify one new member, one existing member, and one restricted page. Only after that should you apply the setting to a live level with real users.
Prepare User-Facing Copy
If a late participant gets less time, that should be visible before registration. Add a short explanation on the form page, in the level description, and in the post-registration email. Do not promise "one month of access" if what you are actually selling is "access until the cohort ends." That difference reduces support requests more effectively than any technical adjustment.
Installing the Add-On and Running an Initial WordPress Check
The installation process is the same as for a typical WordPress plugin: the ZIP archive is uploaded through the plugins section and activated in the admin panel. The official product page says the add-on is available from the Restrict Content Pro member account. This guide does not cover purchasing, license dashboards, or obtaining the paid version, because the practical work begins after the administrator already has a legitimate installable archive.
Minimum Installation Sequence
- Create a site backup or prepare a staging copy.
- Make sure the base Restrict Content Pro plugin or the current product in the Kadence Memberships family is active.
- Open
Plugins, thenAdd New, and upload the ZIP file. - After installation, click
Activate. - Go to the membership levels list and open the add or edit screen for a level.
The key post-activation check is whether the Expiration Date field appears on the add or edit level screen. If the field does not appear, do not continue by guessing. First verify that the add-on is active, that it is compatible with the installed version of the base product, and that you are looking at the correct screen.
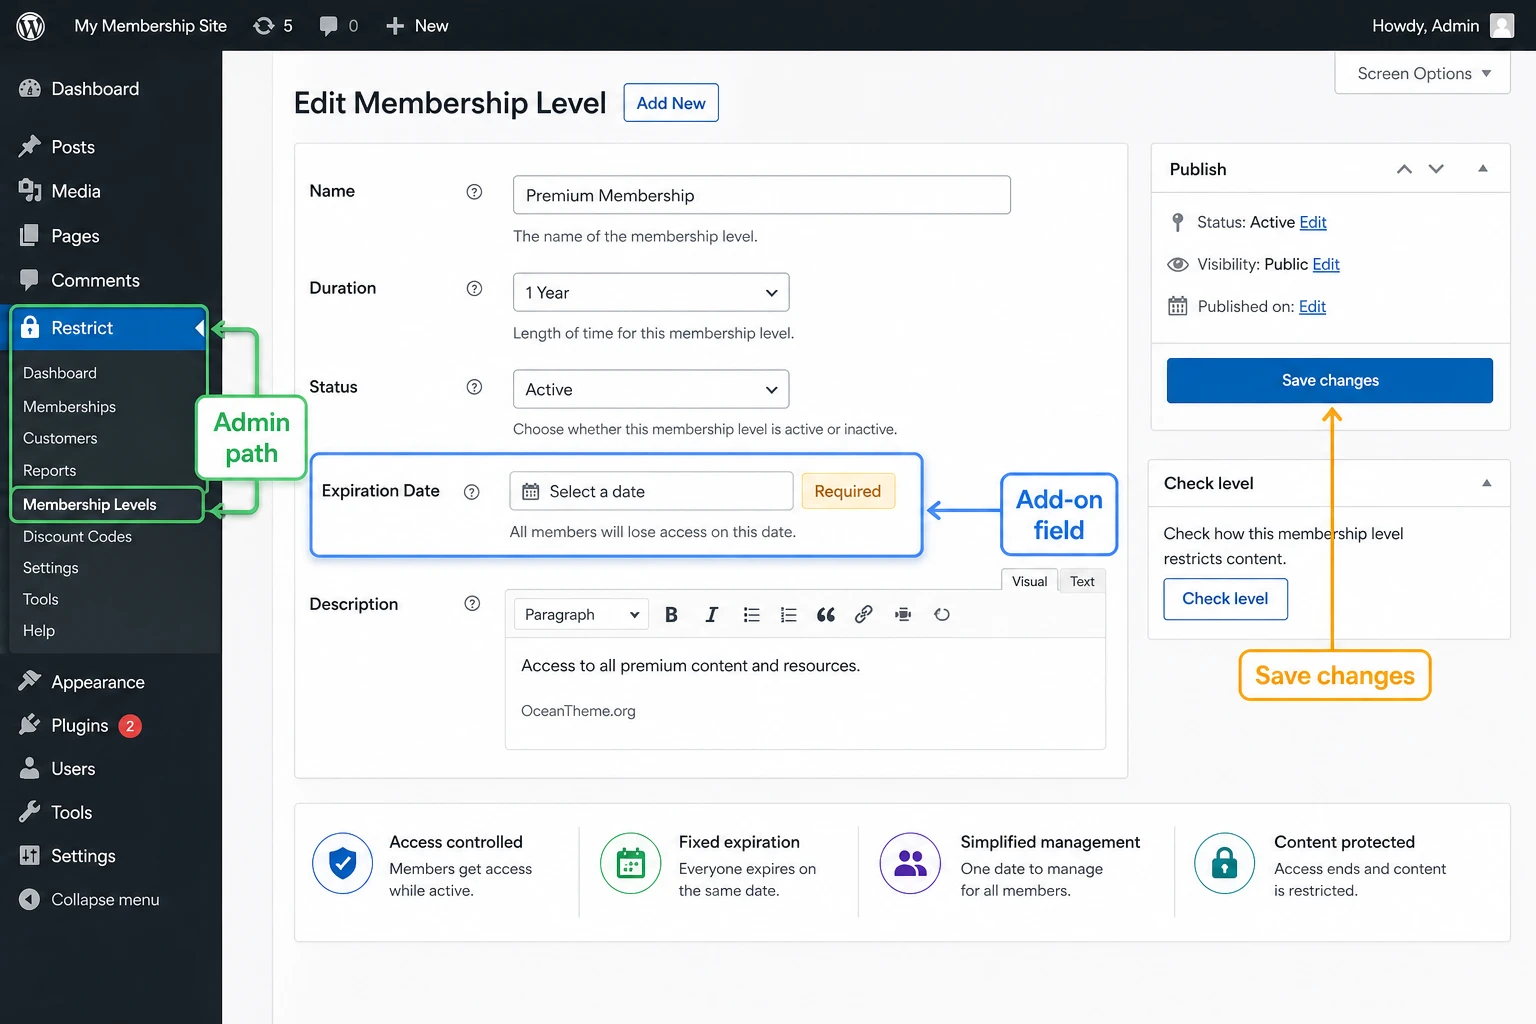
Expiration Date field in the membership level form and which nearby settings are worth double-checking.Why Section Names May Differ
Sources use different names: Restrict Content Pro, Restrict Content, Kadence Memberships, Subscription Levels, and Membership Levels. For an administrator, this means one simple thing: follow the meaning of the screen. You need the section where membership levels are created and edited with price, duration, access level, and user role.
If the site is already using a newer interface version, the menu item may differ from older documentation. Do not try to "fix" that with code, and do not go hunting for hidden database tables. First check the official knowledge base for your version and the list of active plugins.
Initial Testing Without Real Users
Create a temporary level or use a staging copy. Set a fixed date for the level, save the changes, and reopen the edit form. The value should remain saved. Then create a test user and assign that level through a standard registration flow or by manually adding a membership.
At this stage, you do not need to wait for the date to arrive on the live site. What matters is confirming that the field exists, the setting is saved, the member gets the correct level, and the restricted content actually depends on that level.
Configuring the Fixed Date on the Access Level
The main add-on setting is not on a global settings page but on a specific membership level. That makes sense: one group may end at the close of a cohort, another may continue under a standard duration, and a third may be unlimited. Hard-set Expiration Dates lets you define a hard deadline where needed instead of rewriting the entire site model.
A New Level for a Cohort or Season
The safest option is to create a separate level for a specific cohort, season, or event. That way, you do not change the behavior for existing members or mix people with different access terms. In the level form, fill in the name, description, access level, price or free mode, user role, and the other standard fields. Then set the Expiration Date.
Do not make the level name the only place where important information appears. Users may see it on the registration form, but it is better to repeat the expiration condition in the level description, on the program page, and in the post-registration email. It is also useful for the administrator to add an internal note to the site's documentation explaining why the level was created and when it should be closed to new registrations.
An Existing Level With Active Members
If hard expiration is being added to an already active level, the risk is higher. Members may already have individual dates, auto-renew, manual extensions, or different payment terms. Before saving a fixed date, export the list of members on that level or at least record their statuses and expiration dates. That will help you reconstruct what happened if some users contact support.
For an existing level, follow this sequence:
- Make a list of the restricted materials that this level unlocks.
- Check whether the level has recurring payments that are supposed to continue past the shared date.
- Review the registration page copy to make sure it does not promise an individual term.
- Set the
Expiration Dateand save the level. - Check one member from that level both in the admin panel and on the public site.
What to Do With the Standard Duration Field
The standard level duration remains part of the Restrict Content Pro model, but hard expiration changes the final meaning of access expiration for the selected level. Do not rely on guesswork about how your version will combine those fields in every unusual renewal scenario. First test a new signup, a manually added member, and post-expiration behavior on a site copy.
If the level is meant to be strictly seasonal, it is usually better not to sell it as an endlessly renewable subscription. If the level should renew individually, hard expiration is usually unnecessary. One date field should not be used to hide contradictory business logic.
Working With Existing Members and Date Changes
The most sensitive part of implementation is not a new test level but a level that already has active members. Each one may have a different history: some registered through a form, some were added manually, some paid for a recurring subscription, some got access through a promotion, and some may already have had their date edited by an administrator. If you apply hard expiration on top of that history without preparation, the setting may save correctly from a technical standpoint, but support will get questions that are difficult to answer.
First Separate Members by Terms
Before changing an active level, make a simple map: who should lose access with the group, who should keep an individual term, who should be moved to the next cohort, and who should no longer renew at all. You can build this map in a spreadsheet outside the site. What matters is not personal data but access terms: level, status, auto-renew, registration source, and promised term.
If one level contains different commercial promises, do not try to fix that with a single Expiration Date field. Create a separate level for the new rule and move only the users whose terms match the shared date. That makes the outcome easier to explain and easier to roll back if something goes wrong.
How to Change the Date Without Creating Chaos
Sometimes the cohort date shifts. For example, the organizers extend access to the materials or, on the contrary, close enrollment earlier. In that case, more than the technical field changes. You also need to update the level description, registration page, member email, account page, and the administrator's internal note in sync. If you change only the field in the admin panel, the user-facing copy will start contradicting the actual access rules.
A practical order looks like this, especially if the level is already in use on a live site and tied to real payments:
- Take a snapshot of the current state of the level: name, date, status, description, and number of active members.
- Check whether the level has auto-renew or active gateway subscription IDs that require a separate review.
- Change the
Expiration Dateon a staging copy and test it with a sample member. - Update public copy and email templates so they show the same date and the same meaning.
- Apply the change to the live site and immediately verify one active account, one restricted page, and one no-access user message.
Do not change the date several times in a row without keeping records. On a membership site, the administrator's action history matters: it helps explain why one user got a longer access window while another ended up in the next cohort.
What to Do With Members After the Cohort Ends
Once the shared date arrives, the site usually has three options. The first is to leave the expired membership as an archive record and invite the user to join the next cohort. The second is to manually create a new membership for people whose access is extended by agreement. The third is to move part of the audience to another level, such as an archive or free level, if that scenario is built into the site's rules.
The right choice depends on what was promised to the user. If access truly ended, do not quietly reactivate the old level, because later it will be difficult to distinguish exceptions from mistakes. If access was extended for the whole group, it is better to change the level date and update the messaging. If the extension applies to one person only, use manual membership management and record the reason in your notes so you do not break the rules for everyone else.
Rolling Back a Problematic Setting
Rollback should be planned before the change is made. The minimum plan is to restore the previous date or remove hard expiration from the level, clear the cache, verify a test user, review several real memberships, update the public copy, and record why the change was canceled. If the setting also affected payments or member statuses, simply reverting the field may not be enough. In that case, you also need to reconcile RCP, the payment gateway, and the membership history.
For an active membership site, a safe rollback is not a "back" button but a sequence: restore the setting, verify access, explain the change to users, and confirm that payments have not drifted out of sync with memberships.
How the Shared Date Works for Everyone on the Level
The add-on's logic can be described simply: the selected membership level gets a fixed date, and all memberships tied to that level use it as their expiration date. The official documentation specifically emphasizes that once the hard-set expiration date is reached, the membership becomes expired and cannot be renewed like a normal active subscription.

What a Late-Joining Member Sees
A late-joining member gets the same shared deadline as the rest of the group. That is not a bug but the main purpose of the product. If the registration page only says "private club" without explaining the time limit, the user may expect a full individual period. That is why proper configuration includes not only the date field but also user-facing copy: access remains open until the cohort ends, and after that a new enrollment period or separate level is required.
What the Expired Status Means
The expired status affects access to restricted content. If a page is limited to active members of a specific level, a user with an expired membership should not see that material. But if the content is also opened through a WordPress role, another level, or is accidentally left public, the user may still retain access. That is why result verification should always include the page itself, not just the date field in the profile.
Why a Fixed Date Is Not the Same as the Billing Schedule
In membership systems, the access date and billing date often sit side by side, but they are different things. Restrict Content Pro stores the membership and its expiration, while the payment gateway stores its own subscriptions, IDs, and future charges. The membership editing documentation warns that changing the date in RCP may not change the next billing date at the processor.
For one-time seasonal levels, this is usually simpler. Auto-renew scenarios require caution: before enabling the hard date, make sure you are not creating a situation where access has ended but the payment gateway still expects a recurring charge. If there is any doubt, use test mode, consult the gateway documentation, and separately verify the gateway ID in the member profile.
Practical Scenario: A Course With a Shared Access End Date
Let us look at a scenario where Hard-set Expiration Dates really proves its value. There is a WordPress-based learning site, the restricted course lives in standard pages and posts, access is granted through Restrict Content Pro, and all participants in one cohort must lose access at the same time once the program ends. New participants may join during enrollment, but their term is not individual.
Goal
You need to create a separate membership level for the cohort, restrict the course materials to that level only, show the user the end date, and verify that after the program ends the membership no longer grants access to the course pages. At the same time, older levels, lifetime customers, and administrators must remain unaffected.
Preparation
- The base Restrict Content Pro plugin is active, the add-on is installed, and the
Expiration Datefield is visible in the level form. - The course materials are grouped into separate pages, a category, or a defined list of URLs.
- You have a test user without administrator privileges.
- The site has a registration page set up with
[register_form]or another confirmed level registration method. - You have copy prepared that explains the shared access term.

Setup Steps
- Create a new membership level in
Restrict > Membership Levelsor the equivalent section in your version. - Name the level so the administrator can identify the cohort, but do not overload the public name with technical labels.
- Fill in the standard level settings: description, access level, user role, price, or free mode.
- Set the
Expiration Dateto the shared access end date. - Restrict the course pages to members of this level through the access restriction block or shortcode.
- Add the end date to the account page or course page using
[user_expiration]if that shortcode fits your version and page structure. - Create a test registration and confirm that the user can view the restricted content before expiration.
Example of a simple block on the course page:
Access to the materials is available until the date shown in your profile.
Your expiration date: [user_expiration]
For users with expired memberships, you can prepare a separate message:
[is_expired]
Your access to this cohort has ended. Check the next enrollment page or contact support.
[/is_expired]
These shortcodes do not replace the level configuration. They help explain the user's access state. If the content itself is not restricted correctly, the message will not fix the access logic.
Scenario Verification
Log in as the test user and open the course page, the account page, and the registration page. Check three things: the correct level is assigned, the date is displayed as expected, and the restricted material is not available to a user without the required active membership. Then check the same URL in incognito mode and as a standard logged-in user without that level.
Scenario takeaway: hard expiration works as a group rule. The level defines membership, the restricted pages check whether the membership is active, and the user-facing copy explains the shared access term in advance.
Verifying the Result: Admin Panel, Test User, and Public Site
Verification should answer not "was the field saved?" but "what will actually happen to access?" To do that, you need to look at the system from three angles: the administrator sees the membership and date, the test user sees their access, and the public site shows the correct message to people who no longer have access.
What to Check in the Admin Panel
Open the test user's membership profile. Check the level, status, expiration date, auto-renew, gateway customer ID, and gateway subscription ID if this is a paid recurring level. Not every field matters for a free cohort, but for a paid level they help you determine whether Restrict Content Pro and the payment gateway are drifting out of sync.
If the user was added manually, make sure it is an actual membership in the correct level and not just a WordPress role. The documentation for manually adding memberships explains that selecting a level automatically updates the cycle and expiration for that membership. That is one more reason to verify the membership itself, not just the user record.
What to Check on the Public Site
- The restricted content page is available to an active member of the correct level.
- The same page is not available to a user without that level.
- A user with an expired membership sees a clear message if you added a block for the expired state.
- The registration page does not promise an individual term if a shared deadline is in place.
- The cache does not serve restricted content after logout or after switching users.
Verification Checklist Table
| Check | Where to Look | Expected Result |
|---|---|---|
| Level date field | Restrict > Membership Levels |
Expiration Date is saved on the correct level. |
| Member assignment | Restrict > Memberships |
The test user is on the correct level and has the expected status. |
| Restricted page | Public-facing site | The active member sees the material; an unrelated user sees the restriction. |
| User-facing message | Account page or course page | The end date or shared deadline explanation is shown without ambiguity. |
| Payment reconciliation | Membership profile and payment gateway | There is no conflict between access expiration and expected billing. |
Messages for Members Before and After Access Expires
A fixed date can be technically correct and still frustrate users if they did not understand the condition. That is why written messaging is part of the configuration, not decoration. Users should see in advance that they are joining a cohort or season with a shared end date, not buying an individual access period.
Where to Show the End Date
Place the date or an explanation of the access term in three places: the level description on the registration form, the account or dashboard page, and the email sent after membership activation. In Restrict Content Pro Email Settings, template tags including expiration are supported, so for emails it is better to use the verified tags from your version rather than manually typing the date into every template.
On a site page, you can use [user_expiration] if you need to show the current user's date. For a group with hard expiration, this is especially useful: the user sees that the date belongs to their membership, not to some abstract schedule.
What to Say Before Expiration
The wording should be short and honest: access to the cohort materials is available until the shared end date; late registration does not extend access; after the program ends, the next cohort or a separate option will be required. Do not promise "a full month," "one year of access," or "automatic renewal" unless that matches the level configuration.
What to Show After Expiration
For a user with an expired membership, a dedicated block is useful: what happened, where to find the next enrollment period, how to contact support, and what to do if payment went through but access did not open. Do not blame the user and do not expose system details. They need a clear next step.
A simple shortcode version:
[is_expired]
Access to the current cohort has ended. If you believe this is an error, contact support and include your account email.
[/is_expired]
Do not use this block as the only content protection. It displays a message to a specific group of users, but the actual page protection must be configured through Restrict Content Pro rules.
Performance, Caching, and Access Security
Hard-set Expiration Dates should not noticeably burden the public site by itself: its job is tied to the membership date and the level check. But membership sites often use caching, CDNs, page optimization, and security plugins. Those are what can create the impression that the date did not work or that restricted content is visible to the wrong user.
Caching Pages With Restricted Access
Restricted pages, account pages, registration pages, checkout pages, card update pages, and any pages with personal shortcodes are best excluded from full HTML caching. If the cache serves the same version of a page to different visitors, a member may see someone else's state or a guest may see part of restricted content. This is not unique to Hard-set Expiration Dates, but with a shared deadline the problem becomes more visible because many members change access state at the same time.
WP-Cron and Background Checks
WordPress uses the WP-Cron scheduler, which runs when the site receives visits. On low-traffic sites, sites with aggressive caching, or sites where wp-cron.php is blocked, background events may be delayed. If the membership status does not change at the expected moment, check not only the date field but also whether the scheduler is working properly.
A safe approach is to open Site Health, review events with a reliable administrator tool, check hosting settings, and, if needed, set up a server cron job according to WordPress or hosting documentation. Do not add improvised cron snippets for this task: a mistake in that code can create duplicate events.
Permissions and Roles
A membership level and a WordPress role are different mechanisms. The membership levels documentation notes that a level can assign a role to a user, and that role may be removed when the membership expires. But if you manually granted a user a role that independently unlocks content, they may keep access regardless of membership status. During troubleshooting, always check the page rule, the membership, the role, the cache, and the user's actual logged-in state.
Why the Date Did Not Work or Access Is Still Open
It is best to troubleshoot from the symptom. Do not start by reinstalling the add-on, and do not edit the database by hand. On a membership site, the problem is often not a single field but the relationship between the level, membership status, page restriction, cache, and payment gateway.

| Symptom | Possible Cause | What to Check | How to Fix It |
|---|---|---|---|
The Expiration Date field is not visible. |
The add-on is not active, the wrong screen is open, or the interface version uses a different menu name. | The active plugins list, the level screen, and the documentation for the installed version. | Activate the add-on, open the level edit screen, and do not edit the database manually. |
| A late-joining member got only a short term. | This is the expected hard expiration logic for the entire level. | The level description, registration form, level date, and member list. | Explain the shared term, close enrollment earlier, or create a new level for the next cohort. |
| After the date, the user still sees the material. | The content is opened by another rule, a WordPress role, or the cache. | The page rule, shortcode, user role, membership status, and cache behavior on logged-in pages. | Fix the restriction rule, clear the cache, and exclude personal pages from full-page caching. |
| The user paid, but access is closed. | There is a mismatch between RCP and the payment gateway, a webhook was not processed, or the hard date has already passed. | Payment status, gateway ID, webhook logs, membership status, and level date. | Reconcile the payment, manually restore access only after verification, and fix the webhook or next-cohort workflow. |
| Renewal emails are confusing members. | Expiration reminders and renewal reminders are mixed, or the template promises renewal where there is none. |
Restrict > Settings > Emails settings, auto-renew, and email templates. |
Separate messaging for auto-renew and non-auto-renew, and rewrite the copy around the shared deadline. |
| It is unclear whether an expired level can be renewed. | The official Hard-set Expiration Dates logic says that once the date is reached, the membership is expired and cannot be renewed in the standard way. | The level status, current level date, and whether a next cohort or new level exists. | Create a new level or a new membership instead of quietly extending the old cohort. |
When It Is Better to Roll the Setting Back
Rollback is needed if you enabled hard expiration on a level with active recurring payments and discovered a mismatch with the billing schedule, if users received a different term than what was publicly promised, or if restricted pages depend on roles in a way that prevents the membership date from controlling access. In that case, restore the previous level settings, clear the cache, document the changes in your notes, and only then design a new level structure.
FAQ About Restrict Content Pro Hard Expiration Dates
Can I set one expiration date for all members on a level?
Yes. That is the add-on's main purpose: the date is set at the membership level, and members on that level expire on the same shared day regardless of when they registered.
What happens to a user who joins right before the end?
They get the same shared deadline. If that is not what you want, do not use hard expiration for that level. Create a new cohort, close late registration, or keep the standard duration from the join date.
Where is the setting located after installation?
The official documentation says that the Expiration Date field appears on the add and edit screens for levels. Depending on the interface version, the path may be called Restrict > Subscription Levels or Restrict > Membership Levels.
Can the add-on be used with recurring payments?
The exact behavior depends on your configuration, but you need to be especially careful with auto-renew. Restrict Content Pro documentation warns that changing the expiration date does not necessarily change the next billing date at the payment gateway. Always reconcile RCP and the gateway before launch.
How can I show the user their expiration date?
For the current user, you can use the [user_expiration] shortcode if it fits your version and page. In emails, use verified template tags from the email settings, and in the level description write a clear human-readable access condition.
Why can an expired member still see restricted content?
Check whether the content is opened by another rule: access level, WordPress role, paid status, another membership level, or cache. Also make sure the user is actually viewing the page without administrative privileges.
Can I set different dates for different levels?
Yes, the add-on logic is tied to the level. For different cohorts, it is usually better to create separate membership levels so you do not mix members with different terms.
Do I need PHP code to configure this?
Not for a standard scenario. Restrict Content Pro provides code filters for developers, but they should not replace the Expiration Date field. If you need custom logic, build it on a staging copy through a small site-specific plugin or a trusted snippets tool, without editing WordPress core, RCP, or the add-on.
When Restrict Content Pro Hard Expiration Dates Is the Right Choice
This add-on is a strong choice if you already use Restrict Content Pro and need a clear model where "this membership level stays active until one shared deadline." It is especially useful for cohorts, seasonal programs, temporary restricted sections, and event materials. In those scenarios, a shared date makes administration easier and access rules more predictable.
It is not a good fit if you promise every user a full individual term, actively use complex auto-renew scenarios without separately reconciling the payment gateway, or want to manage each member's date manually. In those cases, it is better to keep the duration-based logic, create separate levels, or choose a different membership tool.
Before going live, verify the level, the restricted pages, the test user, the messages for expired members, cache behavior, and any mismatch with payments. Once the scenario has been confirmed on a site copy and you understand which members will fall under the shared deadline, you can go to the Restrict Content Pro Hard Expiration Dates download and test the add-on in your WordPress setup.
The practical conclusion is simple: Hard-set Expiration Dates solves one problem well when that problem is defined honestly. Do not use it as a hidden way to quietly shorten someone's access term. Use it as a transparent tool for cohorts and seasons where a shared end date is part of the offer.

