


Restrict Content Pro BuddyPress - WordPress Plugin
This add-on for Restrict Content Pro creates a seamless connection with your BuddyPress installation. Show user account details in the user’s BuddyPress profile, assign BuddyPress Member Types to individual subscription levels, restrict content by Group membership, and more!
Plugin Features
The integration of BuddyPress with a well-known content restriction plugin provides website administrators with a powerful tool for managing member access to exclusive content. By utilizing this integration, site owners can effectively restrict content, create membership tiers, and enhance the overall user experience. This integration offers a seamless solution for those looking to combine the community-building features of BuddyPress with the content restriction capabilities of the plugin, ultimately fostering a thriving online community with controlled access to different levels of content. Site administrators can easily set up and manage membership levels, restrict access to specific content, and provide a personalized user experience based on each members subscription level.
The seamless integration between BuddyPress and the content restriction plugin empowers site owners to create a dynamic and engaging online community. With this integration, administrators can effortlessly manage user access, protect premium content, and foster a sense of exclusivity among members. By leveraging the robust features of this integrated solution, website owners can build a vibrant community that offers members a range of benefits based on their subscription level. This integration allows for a streamlined user experience, ensuring that members can easily navigate the site, interact with one another, and access relevant content based on their subscription tier.
The plugins BuddyPress integration streamlines the process of managing memberships and content restrictions within a WordPress website. By combining the functionalities of BuddyPress with the content restriction capabilities of Restrict Content Pro BuddyPress, site owners can create a cohesive user experience that encourages user engagement and retention. This integration simplifies the task of setting up membership levels, defining access rules, and customizing the user experience based on individual member preferences. With seamless integration and easy-to-use features, website administrators can efficiently manage their online community, deliver personalized content, and drive member interaction and participation.
The integration of BuddyPress with the content restriction plugin offers a comprehensive solution for managing memberships and controlling access to premium content on WordPress websites. This integrated approach enables site owners to create a membership system that aligns with their community-building goals, providing members with a tailored experience based on their subscription level. By integrating BuddyPress with the content restriction plugin, website administrators can effectively manage user permissions, regulate content access, and tailor the user experience to meet the unique needs of their online community. This integration enhances the overall functionality of the website, fostering user engagement and loyalty among community members.
Specifications:
| Release date: | 11-10-2020 | |
| Last updated: | 11-08-2023 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Access & Security for Restrict Content Pro | |
| Compatibility: | W5.x W6.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | Restrict Content Pro | |
| Rating: | ||
Share with your friends!
A Guide to Setting Up Restrict Content Pro BuddyPress for a Private Community
This Restrict Content Pro BuddyPress guide will help you define access boundaries for your community, prepare the WordPress and BuddyPress integration, configure membership levels and member types, build a testable private-group setup, and diagnose access problems safely. Rather than covering purchase or activation, we’ll focus on how an installed integration works: how a membership becomes a member status, which pages and components actually need protection, and how to confirm that visitors see the experience you intended.
This add-on has a focused but important job: it connects Restrict Content Pro membership rules to the social features in BuddyPress. Standard WordPress post protection may not cover a profile, activity feed, group, or messaging feature because those pages are generated by the community component itself. That’s why the key is not a collection of checkboxes but a sequence: define your audience and access levels, map them to member types, choose what to protect, and then test the rules with different accounts.
This guide takes a cautious approach. The original product page no longer points to the developer’s previous material, so it can’t confirm current support. The practical steps below draw on saved integration documentation and current BuddyBoss/BuddyPress help pages. If you’re using classic BuddyPress rather than BuddyBoss, first check whether the described fields and tabs are available in your installation. If an interface option is missing, stop and verify compatibility instead of trying to replace it with arbitrary code.

What the membership and community integration does
Restrict Content Pro manages membership status and content restriction rules, while BuddyPress adds user profiles, groups, activity feeds, and other social areas. Restrict Content Pro BuddyPress is useful when a private section of your site isn’t enough: you need members at a particular level to enter the community, see the groups they’re allowed to access, receive a clear membership status, and be denied access to other areas even if they follow a direct link.
It helps to think of the integration as a translator between two sets of terms. Restrict Content Pro has membership levels and their statuses. BuddyPress has member types, group membership, and community components. The integration lets you assign a member type to a membership level, update it when the status changes, and use either the member type or group membership as a restriction condition. This gives site editors a clear model: there’s no need to update each new member’s profile by hand when a rule is already tied to a level.
Where it makes a practical difference
One use case is a professional community with several access tiers. For example, visitors might see a public program page, registered members might access the general activity feed, and professional-level members might get a private group for resources and discussions. Another use case is an educational community where a course level maps to the "Student" member type and a mentor level maps to "Instructor." A third is an agency’s client area: employees at a client organization get access to one group, keeping its files, conversations, and activity separate from other projects.
The goal isn’t to lock down everything. A good setup keeps reference material, the login page, and a clear explanation of where users will land after signing in available to the people who need them. Protect the paths where valuable communication actually happens: the member directory, individual profiles, groups, activity, messages, or content inside a particular group. The more precisely you define what needs access control, the easier it is to test the rule and the less likely you are to lock out an editor or administrator by mistake.
Who should use it, and when another approach may be better
This integration is a good fit for a WordPress site that already uses Restrict Content Pro and BuddyPress, or a compatible social platform, and needs membership to change what people can do in the community. It can work well for private clubs, course cohorts, client communities, associations, and internal spaces where profiles and groups matter as much as protected articles.
It may be more than you need if you only want to restrict a few standard WordPress pages to logged-in users. In that case, start with Restrict Content Pro’s built-in tools for membership levels, page or post rules, and restricted-content messages. Don’t add BuddyPress just to get a polished account page. On the other hand, if you need complex access controls based on departments, custom attributes, or external corporate authentication, mapping a membership level to a member type may not be enough. Design roles and user fields separately, and treat the integration as one part of the access model rather than a complete permissions system.
Start with this check: state your access rule in one sentence. For example: "An active Mentor-level member gets the Mentor type, can see the Mentors group, and can use the components allowed there." If you can’t explain the rule clearly, it’s too early to change settings in the interface.
The states that determine a member’s access
Integration problems often start when four distinct concepts get mixed together. A membership level is the condition Restrict Content Pro uses to determine whether a user qualifies for access. Membership status tells you whether that condition is currently active. A member type is a BuddyPress classification that can be assigned automatically. A group is a specific community space that the user belongs to or that’s used as an access condition. These concepts may have similar names, but they’re not interchangeable settings.
The flow works like this: a user gets or changes a membership, the integration maps the level to the selected member type, and then a rule on a page, group, or component checks the current user against the permitted level, type, or group. If the check passes, the user can see the page or perform the action. If the membership is canceled or expires, the type may be removed if that option is enabled in the integration settings. So test both sides of the rule: access to the protected area and what happens when access ends.
A membership level is not a WordPress role
A WordPress role controls basic site-management capabilities, such as editing posts. A Restrict Content Pro membership level controls access based on a membership program. A BuddyPress member type classifies people in the social part of your site. If you need different member types with the same editorial permissions, don’t make WordPress roles the only way to describe your access model. For most communities, it’s safer to give regular members a minimal WordPress role and define access differences through membership levels and member types.
Keep names clear and easy to match
The names don’t have to match exactly, but the connection should be obvious. If a membership level is called "Mentor," the member type could be "Community Mentor" and the private group could be "Mentors." If one setting is called "Premium A," another is "Role 4," and a third is "Private Group 12," no one will be able to update the rules safely a month later. Create a simple mapping in your site’s working documentation and name an owner for each rule.
What you can restrict
The integration help describes restrictions based on member type and group membership, as well as an option to restrict the entire community section and redirect unauthenticated users to a login or membership page. For an individual item, the settings appear in its restriction panel. In practice, this means you can build a rule around a community feature, not just a standard WordPress page. For a public group, you can keep the group itself visible while restricting its contents based on your chosen conditions. For private or hidden groups, account for BuddyPress’s own rules first: users must already join these groups before they can view their contents.
Don’t combine every condition without a reason. Using a membership level, role, member type, and group together makes sense if they each express part of your actual access policy. If the goal is to admit every active mentor, start with one clear condition. Extra conditions make troubleshooting harder: a user may have the right level but still be denied access because they aren’t in the required group.
Plan access before installing or enabling the integration
Before installing, don’t start with "we’ll make the community private." First, list the paths available on the public-facing site: the member directory, profile, group directory, individual group, activity feed, messages, and standard content pages. Then mark each one as open to everyone, available after login, or restricted to a particular membership status. This map helps prevent a common problem: the site appears to work, but a direct link exposes more than you expected.
Your second planning document is a user matrix. Start with three test users: a visitor who isn’t signed in, a signed-in user without an active level, and an active user at the target level. If you have several levels, add one test user for each. Don’t rely on your administrator account as the only test. Administrators can often perform actions that regular users can’t, which can make an incomplete setup look correct.
Check the basic requirements
WordPress, Restrict Content Pro, and the social component supported by your integration build should all be active in the admin area. The saved documentation specifically describes support for BuddyBoss Platform, which has its own development path alongside BuddyPress. That doesn’t mean you should install both social platforms. Choose the community platform you actually use and confirm that the add-on recognizes its interface.
Check a few other basics as well: permalinks should be configured, the login page should open, and your theme should display the standard community pages. If you use a caching plugin, wait to enable full-page caching for authenticated pages until you’ve finished testing access. A cache can show a signed-in member the guest version or, worse, serve one visitor’s personalized content to someone else. That’s a general issue on sites where content depends on whether a user is logged in, not a specific feature of Restrict Content Pro BuddyPress.
Create a recovery point and test site
Required step: change access rules on a staging copy first, or during a short maintenance window with a saved recovery point. Changes to a level, member type, or global restriction can affect every active member. A backup of the database and files doesn’t replace testing, but it gives you a way back to a known state if a rule blocks the account area or an editorial path.
Record the current settings: which community components are open, which pages handle login, and where users without access should be sent. This log is especially useful when several people work on the site. It turns a rollback into a specific set of actions instead of guesswork: remove the last restriction, clear the cache only after restoring the previous settings, and rerun the three-user test matrix.
Choose levels and member types before changing settings
For your first run, keep the setup simple and use one private membership level. For example, "Club Member" could provide access to the general activity feed and one group. Add "Mentor" or "Organizer" only after the initial rule passes testing. Creating five or six levels too early makes it hard to tell which rule caused an access problem.
| Item | Example | Purpose | How to test it |
|---|---|---|---|
| Membership level | Club Member | Defines the access condition in Restrict Content Pro | Check that the test account has active membership status |
| Member type | Member | Classifies the user’s profile and can be used in access rules | Open the profile after assigning the level |
| Group | General Club | Provides a specific space for community interaction | Open the group as each of the three test users |
| Denied-access path | Login page | Gives the user a clear next step instead of a dead end | Open the protected URL in a private browser window |
Once your map is ready, you can install the integration. At this point, you haven’t "set up monetization." You’ve created a clear way to test the rules: which user, with what status, gets which type, and what they can see.
Install and test safely without disrupting active members
Upload the installation archive you already have from the standard WordPress screen at Plugins - Add New - Upload Plugin, then click Install Now and Activate. Don’t change global restrictions as soon as you activate it. First, confirm that the main Restrict Content Pro panel opens and that a BuddyPress-related area appears in the menu. The saved documentation lists the path as Restrict - BuddyPress. The tab or menu item may have a different name in another build, so use the interface that’s actually available in your installation.
If activating the add-on causes a critical error, don’t try to mask it by changing your theme code. Deactivate the latest add-on from the standard plugin list, restore access to the admin area, and compare your version requirements with the vendor’s documentation. This is safer than editing WordPress core or extension files that an update could overwrite.
Enable the settings for the first time
Open the integration area and look for options related to community restrictions, redirects, and removing a member type when a membership is inactive. Don’t turn on every switch. For the first test, choose a clear destination for visitors who aren’t signed in, then confirm that they reach the login form or the page you selected. If the setting offers a pricing or membership page, use a neutral information page on your test site so you don’t confuse access testing with checkout.
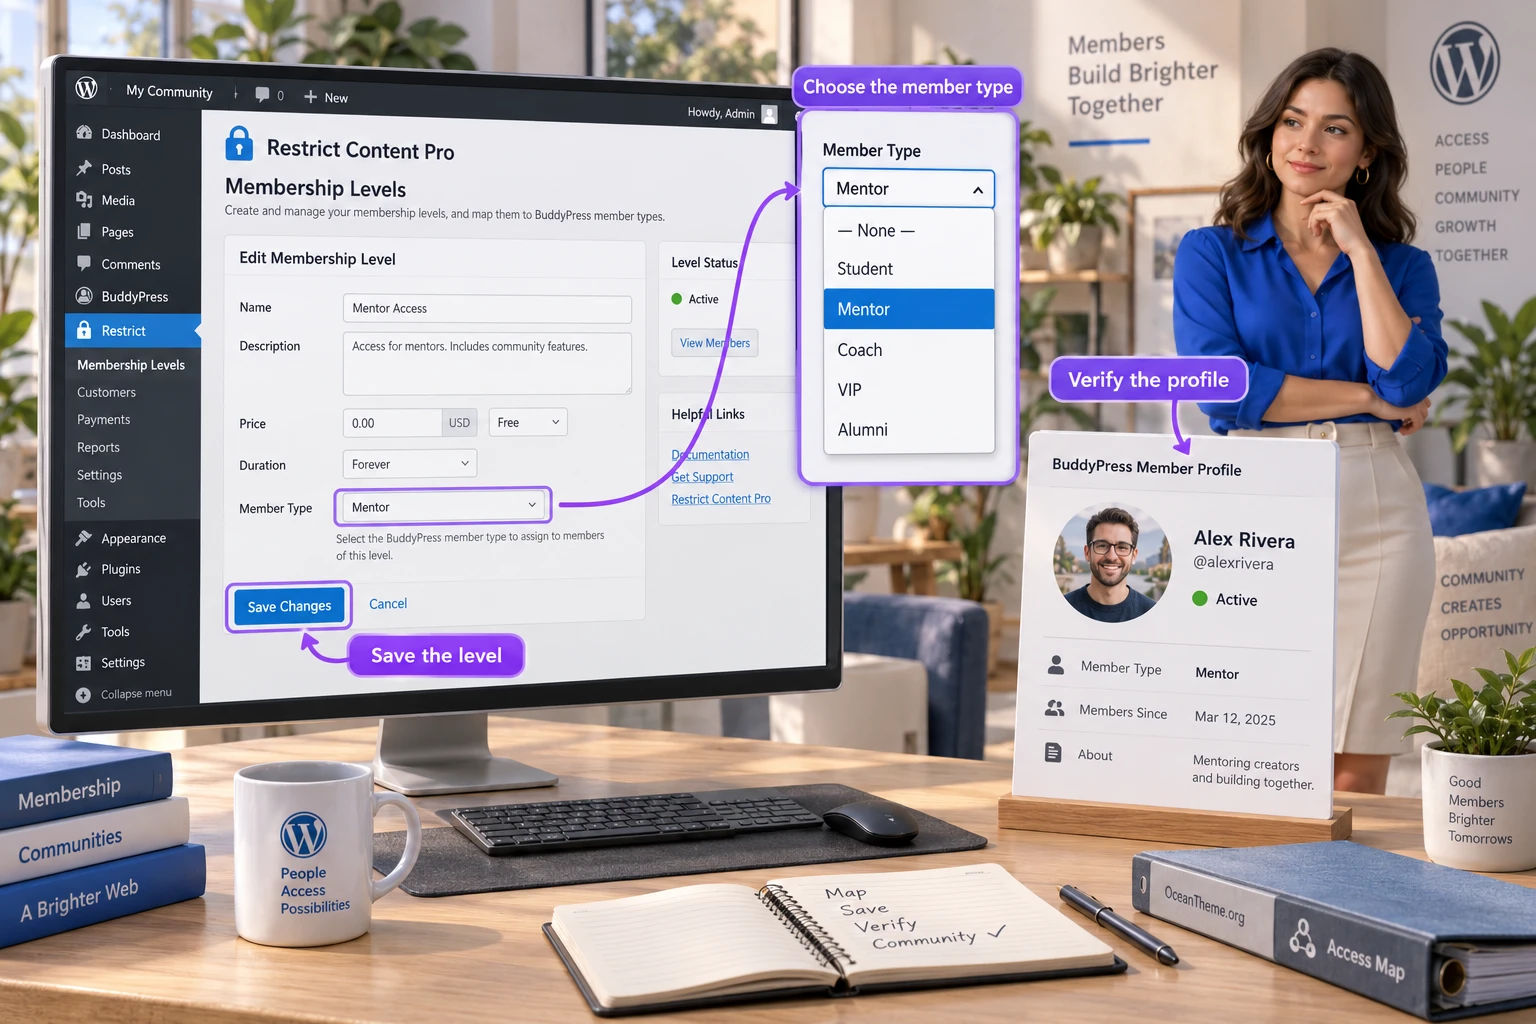
Next, create a test membership level under Restrict - Membership Levels, or open an existing level. If the Member Type field appears after you enable the integration, find it and select the member type you prepared. Save the change with Update Membership Level or the equivalent button. Follow the right order: the member type must exist in the community platform before you can assign it to a level. If the dropdown is empty, don’t substitute a WordPress role for a member type. Go back and configure the types in BuddyPress first.
Test without a payment or unnecessary changes
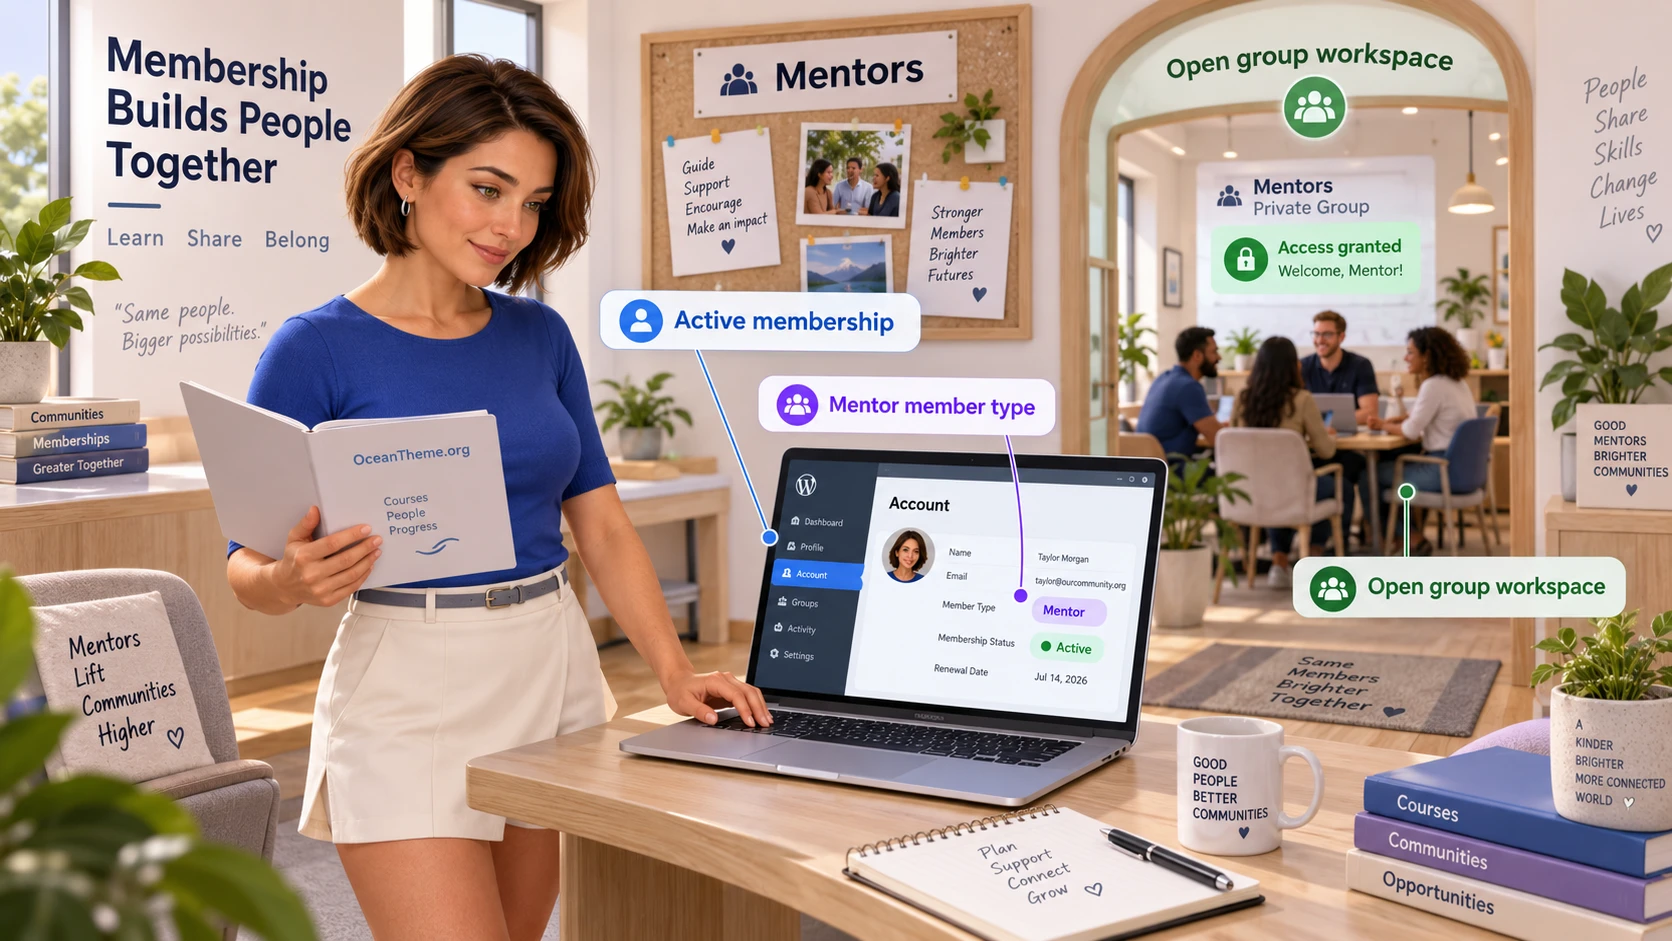
Use an existing test account and change its status using the method provided by your installed version of Restrict Content Pro. Then sign out of the admin area and open the user’s profile in a separate browser. The expected sign is that the corresponding member type appears where your social platform normally displays it. If the integration provides an Account tab, it should show current status details and payment history without any manual setup. You don’t need to create real transactions to run this test.
Installation checkpoint: the add-on is active, one level is mapped to one member type, and the test account shows the expected status. Only then should you restrict your first community item.
Configure Restrict Content Pro BuddyPress, from membership level to access
The most useful setting isn’t the "strictest" one. It’s the one you can explain and reproduce. Start with a rule on a single group or page, then expand from there. In the editor for the item you want to protect, find the restriction panel. For a group, the documentation describes an access-conditions section where you can select permitted membership levels, a role, a member type, or existing group membership. Use only the conditions that match your access map.
If your goal is to admit all active members at a particular level, select that level first. If your policy needs to distinguish mentors from students who have the same level, add a member type. A group-membership condition can help when access depends on belonging to another group, but you’ll need to test how users join. Don’t make membership in the target group and membership in the condition group depend on each other: the user may have no way to join the first group.
Choose an access model, not a random set of checkboxes
There are three reliable models. The first is a fully private community: the entire community section is available only after login or with an active membership. This works for an internal portal, but you’ll need to test the login page and administrator access carefully. The second is a public directory with private participation: everyone can see the group directory or descriptions, but only members can view the contents and take part. This makes the community’s value clearer to visitors, but gives you more access points to test. The third is a set of separate zones: a general group is open to all registered users, a special group is reserved for a particular level, and certain features, such as messaging or group creation, depend on membership level.
Choose one model for the first version. If your site is already live, it’s usually safer to start with the second. That reduces the chance of unexpectedly hiding the entire user journey. After each change, repeat the same test in a private browser window. Don’t evaluate access in the same browser tab where you’ve just been working as an administrator: cookies and the admin bar can change what you see.
Set a global community restriction and define its limits
A global BuddyPress restriction can help with a private club, company space, or course cohort where the existence of members shouldn’t be public. The integration documentation says you can restrict the whole section and send unauthenticated users to a login or membership page. Before you enable this setting, make a list of exceptions: the login page, password recovery, legal pages, and a brief public page about the community if that fits your site strategy.
After saving, don’t stop at the community home page. Check the direct URLs for the member directory, group directory, profiles, activity feed, and a specific group. Some themes also add links to menus and widgets, so look at a sample blog post and the site footer. An access rule is working only if users can’t bypass it with a saved direct link.
Choose what happens when access is denied
Redirecting to the login page works when users need to sign in first. A page with an explanation works when access depends on a higher membership level and visitors need to understand the difference. An inline message is appropriate when someone is already signed in but doesn’t meet the rule. Don’t use the same generic message for every case. Tell the user what to do next: sign in, check their membership status, contact the community owner, or return to a public area. Don’t reveal other members’ names, exact internal names of hidden groups, or other internal information in the denial message.
Map a membership level to a member type
This is what sets the add-on apart from a basic post restriction. Open the level under Restrict - Membership Levels and use the Member Type field if it’s available. The selected type should be assigned when a user gets that level and updated when their status changes, according to your settings. It’s more than a profile label: you can use the type in access rules and community displays if your social platform supports them.
Start by assigning a type to one level. Then change the status of one test account, refresh its profile, and confirm that the type has changed. If access rules already rely on the type but it hasn’t updated, the user may still have access to outdated features. Don’t treat this as a display-only problem. Check that the type exists before mapping it, the level was saved, another add-on isn’t also changing member types, and the user doesn’t have multiple active memberships that create ambiguity.
Support for multiple memberships in a later version of the integration doesn’t mean every combination will produce an obvious result. Define the priority in advance: if a user is linked to two levels at once, which type should appear, and should access be granted when either level qualifies? Add that case to your matrix and test it specifically. A new checkbox won’t resolve an undefined business rule.
Remove a member type when access ends
The documentation describes an option to remove a member type when a membership is canceled or expires. This matters more than it may seem for temporary access. If the type remains, it may continue to affect the profile or a rule based on that type. Enable automatic removal only after you’ve tested the reverse case with a test account: an active level assigns the type, a status change removes it, and the user no longer passes a rule that depends on the type.
However, don’t enable removal automatically if the type is also used for an independent community role. For example, someone might be a "Moderator" regardless of whether their paid or temporary access is active. In that case, don’t link that type to a membership level. Create a separate type that represents membership, or use another condition. This is a case where an accurate data model matters more than convenient automation.
Restrictions for public groups and other group types
BuddyPress has public, private, and hidden groups. Private and hidden groups already have their own membership and visibility rules. The integration is especially useful when you need an extra condition for a public group’s contents. Users can learn that the group exists but see its contents only if they meet the level, member type, or group-membership requirement. This works well for a public-facing club directory, but the page should clearly explain why someone doesn’t meet the rule.
Assign an owner to each group rule. Don’t leave conditions without context: record why the group is private, who can open it, and how to test it. If editors create new groups, give them a process to follow: create the group, set the standard BuddyPress options, check the Restrict Content Pro restriction panel, and only then publish the invitation. Otherwise, a new group may remain open simply because the global access model wasn’t clear.
Group creation limits are a separate rule
The documentation also describes a limit on the number of BuddyPress groups a user can create based on their membership level. This doesn’t restrict viewing, and it doesn’t replace access rules for existing groups. It answers a different question: who can create new spaces and how many they can create. First decide whether you need this quota. It may only add friction for a small club. In a larger community, where new groups affect moderation, a quota can tie membership level to responsibility.
Test the quota with a separate account: create the allowed number of groups, try to create one more, and note the expected message. Don’t set a limit based on the assumption that it protects group content. Existing groups and the ability to view them are controlled by different rules.
Save and test each condition as you add it. If you change five settings screens before testing and then get denied access, it will be difficult to tell which level, type, group, or component caused the problem.
How a membership rule reaches a BuddyPress page
Understanding the flow can save hours of troubleshooting. It starts with a user’s current membership status. Restrict Content Pro determines whether the user meets an active membership condition, and the integration maps that level to a member type if you’ve configured one. The user then opens a BuddyPress path, such as a group page, profile, activity feed, or another component. At the point of the request, the access rule checks the user against the permitted levels, roles, types, or group memberships. The user then gets access to the content, sees a message, or is redirected.
This flow explains why a profile that "looks right" doesn’t prove that access is configured correctly. A visible member type confirms only one part of the process. You still need to test the target path as the right user and as a guest. Conversely, if a user can see a page but has the wrong member type, the rule may be too broad because it allows a level or role that wasn’t intended. The problem may not be type synchronization.
Input, rule, change, outcome, and verification
Describe each requirement in five steps. Input: the user gets the "Club Member" level. Rule: that level assigns the "Member" type, and the "General Club" group allows that type. Change: after signing in, the profile receives the corresponding classification. Outcome: the member can open the group and use its permitted features. Verification: a guest gets the chosen denial path, a user without the level sees a restriction, and the test member can enter without being added manually.
If any step fails, don’t skip straight to the end. For example, if an active member is denied access, first check their membership status, then the mapped type, and then the restriction panel on the specific item. If a guest gets unexpected access, start with the rule’s coverage of the route and the cache rather than changing the member type. This sequence turns site support into a search for evidence instead of a series of random setting changes.
Test community components individually
The documentation mentions restrictions on BuddyPress components based on membership level, as well as control over which components are available to users who aren’t signed in. This is an easy place to make mistakes because a component isn’t necessarily a standard page. The activity feed, messages, and profile sections can have their own paths and actions. Add a separate row to your matrix for each enabled component, then test its view, actions, and direct URL.
For example, it’s not enough to check that a user can’t see the "Messages" link in navigation. Enter the component’s direct URL in a new private browser window. If the platform offers an action through a button, test that too. Hiding a menu item improves the interface but doesn’t replace access control at the request level. At the same time, don’t restrict components that your policy doesn’t cover. Fewer unnecessary barriers make the experience clearer for legitimate members.
What counts as proof that a rule works?
A screenshot of one successful login isn’t proof. At a minimum, test the same URL in three states: a guest gets the expected restriction, a signed-in user without the required status can’t see the content, and an active member can access the expected area and perform the permitted action. If the rule depends on membership ending, add a fourth test: after the status changes, the same user no longer passes the check.
Record the test date, route, type of test account, and expected outcome rather than storing a set of passwords. This makes it easier to repeat the test after updating the theme, social platform, Restrict Content Pro, or caching plugin. It also helps a new administrator understand what "private" means on your site.
Practical example: a mentors’ club with a public directory
Here’s a specific example that doesn’t depend on payment processing. The site has a public page about the club, a general area for registered users, and a private group for mentors. The "Mentor" level should automatically assign the matching member type. Users at that level can see the mentors’ group, while a regular signed-in user gets a clear message and can’t access its resources through a direct link. This is a useful first project because it includes every part of the integration: a level, a type, a group, a denial path, and a reverse-access test.
Define the goal and prepare the setup
The goal is to create a private working area without turning the rest of the site into a maze of inaccessible pages. Before you start, create the "Mentor" member type in your social platform, a test Restrict Content Pro level with the same meaning, and a "Mentors" group. Prepare three test accounts: a guest who isn’t signed in, a regular signed-in user, and a user assigned the test level.
Decide whether the group itself should appear in the directory. If a public listing is acceptable, choose a mode and rule that keep the group visible without exposing its internal resources. If the group is confidential, set its standard visibility options first, then add the integration rule. Don’t assume one restriction automatically covers the other. Group visibility and permission to view its contents are related but separate decisions.
Step 1: Map the level to a member type
- Open
Restrict-Membership Levelsand create or edit the test level. - Find the
Member Typefield and select "Mentor." - Save the level with
Update Membership Levelor the available save button. - Assign the level to the test account using the standard method for your installation.
- Open the test user’s profile in a new window and confirm that the member type changed as expected.
You don’t need to grant additional editorial roles at the same time. If the user needs to moderate the group, configure that separately as a deliberate rule. For this access test, you only need to confirm that the level-to-type mapping works.
Step 2: Configure the group and its restriction
Open group management from the BuddyPress or BuddyBoss menu, select "Mentors," and edit the group. In the group’s restriction panel, select the "Mentor" type or the level you chose as the primary condition. If you’re intentionally using both, confirm that the test user meets each one. Save the group, then sign out of the administrative account right away.
It helps to leave a regular group open to all signed-in users. Use it as a control: if a regular user can’t see that group either, the problem isn’t the private group setting. Comparing two groups reduces guesswork when you troubleshoot.
Step 3: Test the path as three different users
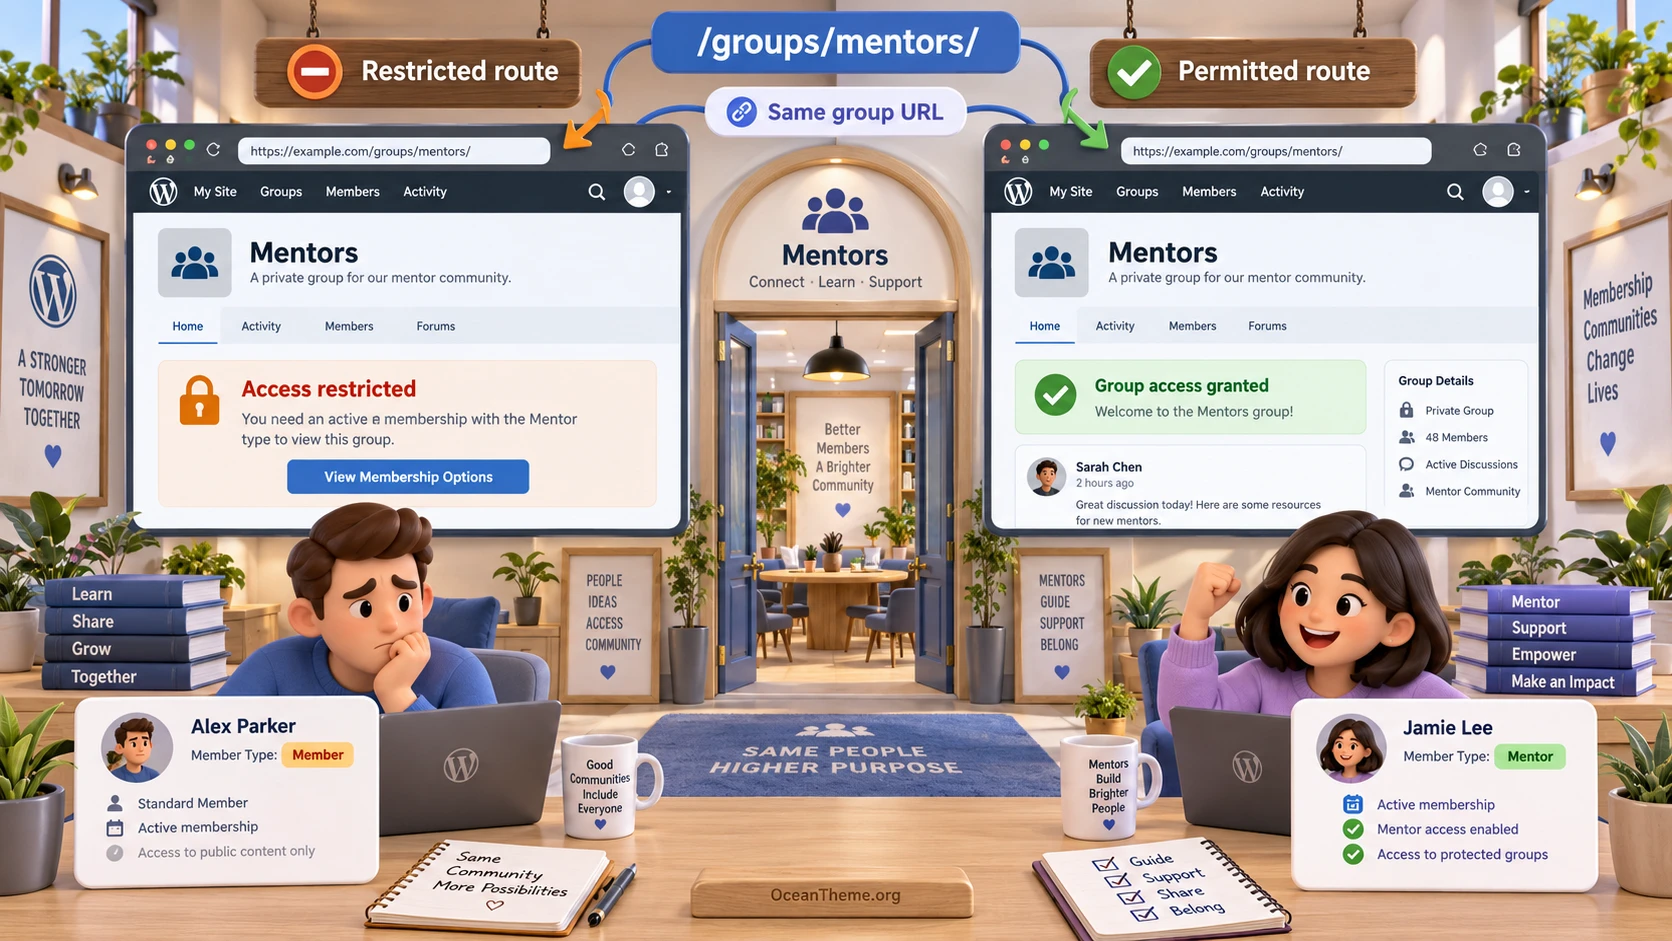
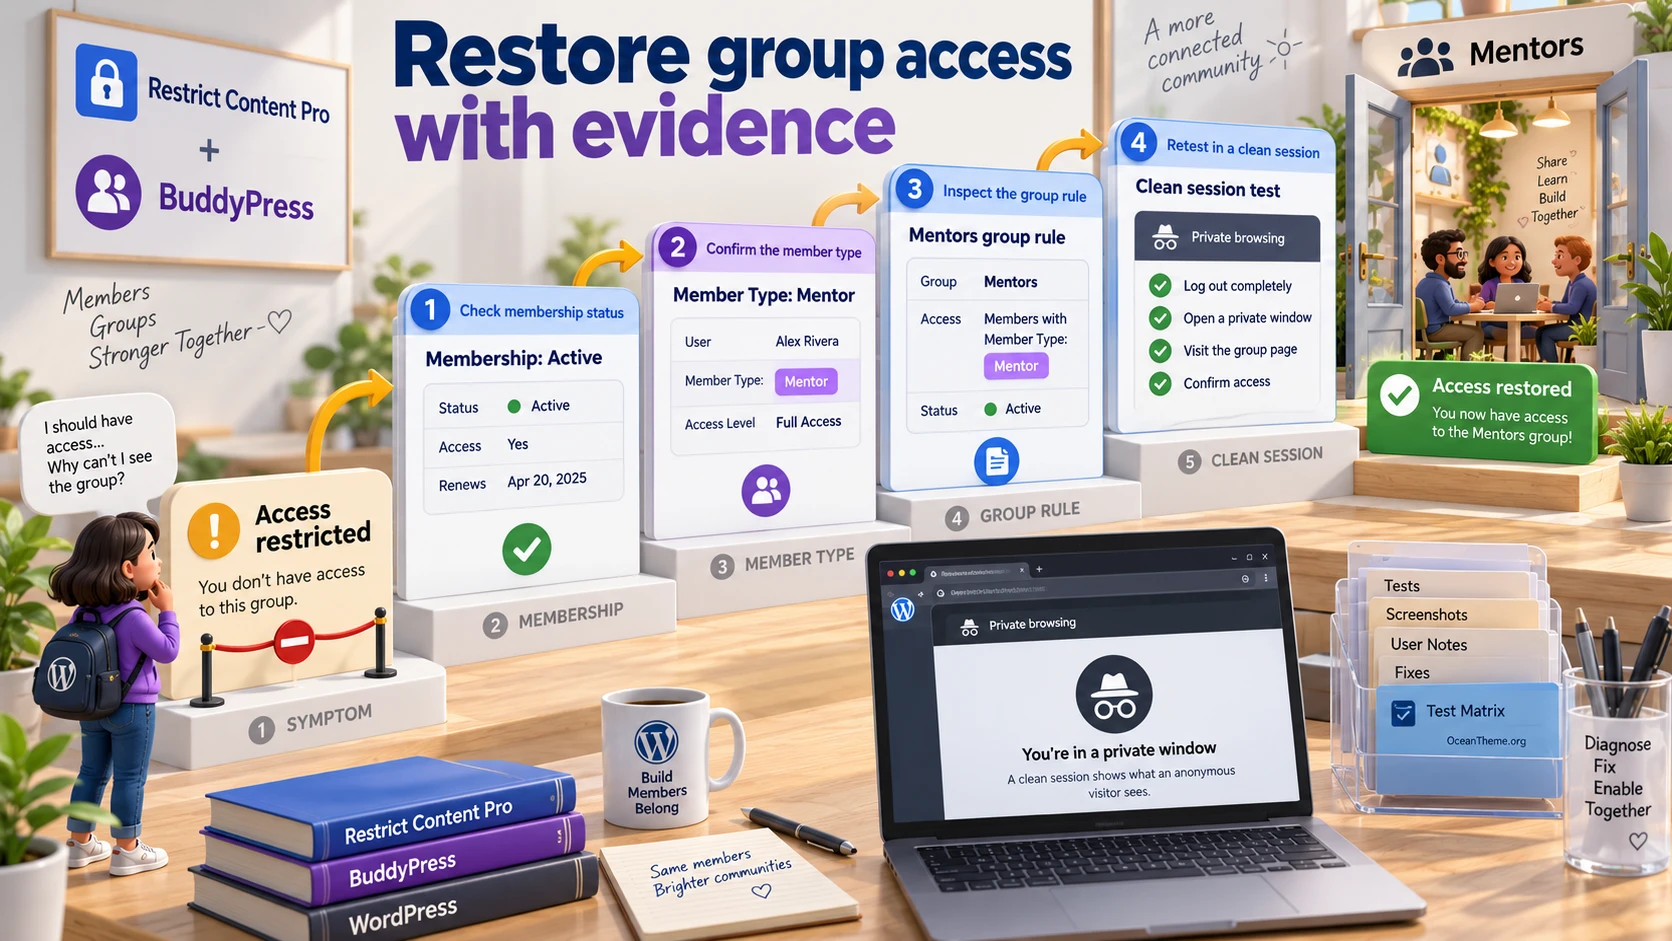
Open the private group’s URL in a private browser window as a guest. Record where the browser takes you and whether that matches the intended behavior. Then sign in with the regular test account and try the same URL. The user should see a message or destination that explains why they don’t have access, without seeing internal content. Finally, sign in as the user with the "Mentor" level. The group, its activity, and its permitted actions should now be available.
After that works, test what happens when access ends. Change the test level’s status to inactive using the method supported by your version, clear only that user’s session, and open the same URL again. If you’ve enabled type removal for inactive memberships, check the profile too. This confirms that the private area won’t remain open because an outdated classification is still in place.
A common pitfall
Don’t treat the group’s name appearing in a menu as proof of access. The theme may cache navigation, and different user levels may see the link. Test the actual page and its contents in a separate session. Also, don’t reuse one test user across several incompatible levels. Its previous states add too many variables. Clean test accounts are more reliable than guesswork.
Example checkpoint: you now have a testable rule, not just an abstract "integration": membership assigns a classification, that classification opens a specific group, and users see the denial before the group’s contents load.
Verify access after changes and updates
After setup, repeat a short regression test whenever you update Restrict Content Pro, the social component, the theme, or your caching solution. You don’t need to review the entire configuration every time. Open the routes you listed earlier in four states: guest, signed-in user without a level, active user at the target level, and user whose target level is now inactive. This gives you a quick way to see whether the access boundary has changed.
Check the user experience too. Active members should have a clear entry point into the community, and users without access should know what to do next. If a user is sent to the home page with no explanation, access may be restricted technically, but you’ll get unnecessary support requests. A clear denial path is part of a reliable setup, not a cosmetic detail.
A checklist for community owners
Test in the right order. First, confirm that the test user is signed in to the correct account. Then check their memberships and current status. Next, inspect the member type in their profile if the rule uses one. After that, test the specific item: a group, page, or component. Only then check menus, cache, and theme styling. This follows the path from data to what the user sees and reduces the chance that you’ll polish the interface while access data is still wrong.
- Test the URL directly. A menu link doesn’t prove that the user can access the item.
- Use a new private window. This reduces the effect of old cookies and an active admin session.
- Write down the expected outcome. Decide in advance whether each route should allow access, show a message, or redirect.
- Change one variable at a time. Change the level or the type, but not both at once when you’re looking for the cause.
- Test the reverse path. Access rules are reliable only if access ends when the condition no longer applies.
If several administrators work on the site, assign one person to own the access model. That person doesn’t have to be a developer. The important thing is to have someone responsible for the level, type, and group mapping, with changes documented before they go live. This way, a new group won’t appear without a decision about who it’s for and how to test it.
Compatibility with themes, caching, and editorial workflows
Restrict Content Pro BuddyPress runs in an environment where several layers contribute to each page: WordPress routes the request, BuddyPress displays the component, Restrict Content Pro and its add-on check the conditions, and the theme displays the navigation and message. So a mismatch in what you see doesn’t always point to an add-on problem. For example, a user may pass the group check but still see an outdated menu link because the theme cached it. Or the restriction may work correctly while the theme’s styling makes the message almost impossible to notice.
Caching: what to check first
Exclude pages that depend on login status and membership from public caching, using the options available in your caching solution. There isn’t one universal setting for every plugin, and the exact rules vary. But the principle is consistent: the same URL shouldn’t show a guest copy to an active member or serve one visitor’s personal response to someone else.
After changing an access rule, clear the relevant cache and repeat the test in a private window. If the outcome changes only after a full cache purge, record that in your working instructions. Don’t disable caching forever because of a single problem. First identify the personalized routes, then configure exclusions for those routes.
Theme and navigation
The theme controls which links are visible, but it shouldn’t be the only barrier. If your tools support visibility conditions, configure the menu so users don’t see sections they can’t access. Then keep the restriction on the route itself. These two layers aren’t redundant: the menu makes navigation clearer, while the rule on the item enforces access when someone uses a direct link.
Check the mobile menu and widgets too. They often contain a separate copy of the navigation that gets missed after the desktop header is checked. Don’t use CSS to "hide access" when there’s no server-side or application-level rule. CSS controls appearance, not permissions. It can be useful for improving the visibility of a standard restriction message.
A safe styling change for restriction messages
If the theme makes the restriction message blend into the background, add a small CSS rule through a child theme or the built-in Additional CSS area, after confirming the element’s actual class in your installation. Message markup varies between themes and versions, so don’t guess at a selector. If you can’t confirm the class, it’s safer to adjust the colors and contrast through the theme’s settings. After the change, check the message as a guest and a regular user. To roll it back, remove only the rule you added in the Additional CSS area.
This cautious approach is safer than trying arbitrary code. It doesn’t change WordPress core, plugin files, or access logic. It only improves the readability of a correct message.
Use it alongside other site features
One practical approach is to use Restrict Content Pro BuddyPress alongside standard Restrict Content Pro pages. You can restrict a club-rules page and course materials by membership level, while the social group uses the same membership concept through the integration. Each product has a clear role: Restrict Content Pro stores access conditions and protects standard content, BuddyPress provides profiles and group conversations, and the add-on connects them. Configure the level first, then a standard restricted page, and then the member type and group. That makes it easier to identify which layer caused a problem.
You can also use bbPress if separate discussions need to be part of the community program. Don’t describe this as an automatic integration without checking your installed version and its documentation. First confirm that the forum has its own access rule, then test it with the same accounts. Access to a group doesn’t automatically grant access to every forum.
Test an integrated setup in order
- Create a level and confirm that it grants access to one standard test page.
- Map the level to a member type and confirm that the type changes in the profile.
- Apply a rule to one group and test access through its direct URL.
- If you use a forum or another component, add it as a separate row in your matrix instead of assuming it works automatically.
- Test a guest, a regular user, an active member, and an inactive member after clearing the user’s session.
Roll back an integrated setup one layer at a time too. First remove the latest rule from the new item. Then temporarily remove the level-to-type mapping if that’s where the problem is. Don’t disable all of Restrict Content Pro because of one group. That would affect standard content and remove useful information for troubleshooting.
Troubleshoot common access problems
Most problems with this integration have an observable symptom. Start there and check the short chain of data instead of changing the level, group, and theme settings all at once. Keeping access under control matters more than getting a random positive result quickly.
An active member is denied access to a private group
Symptom: a test user who should have access based on their level is sent to the login page or sees a restriction message. Possible cause: the level isn’t active, the member type wasn’t assigned, the group has an extra condition, or the user doesn’t belong to a group listed as a requirement. What to check: review the membership record, the member type in the profile, and the restriction panel for the target group, in that order. Compare each setting with your access map.
How to fix it: start by leaving just one primary condition on the item, such as the level or the type. Save and test again. If access works, add a second condition only if you truly need it. When to roll back: if you can’t explain the new combined rule in one sentence, restore the last working model and redesign the conditions on a copy of the site.
The member type doesn’t change when membership status changes
Symptom: the membership status changed, but the profile still shows the previous classification. Possible cause: the type didn’t exist before you mapped it, the level wasn’t saved with the Member Type field, another profile add-on is active, or the user has multiple statuses without a defined priority. What to check: confirm that the type exists and is selected for the level. Review the timing and order of recent changes, and check for other plugins that may change member types.
How to fix it: restore a simple "one test level - one test type" setup, confirm that it works with a new account, and only then apply the rule to active members. When to roll back: if the type serves an independent editorial purpose, don’t link it to membership. Use a separate type for access status.
A guest can still open a restricted route
Symptom: a guest follows a saved link and sees the content or part of a personal area. Possible cause: you checked only the menu link, applied a rule to a different item, are seeing an old cached page, or left a component out of the global setting. What to check: open the direct URL in a clean private window, confirm your login status, and repeat the test after clearing the relevant cache.
How to fix it: return to your route map and add the missing item as a separate restriction point. Configure a cache exclusion for the personalized route using the caching solution’s documentation. When to roll back: if the global restriction accidentally blocks the login page or another essential route, disable only that global setting, restore the route, and apply the rule to a smaller set of components.
Users can no longer create groups after a rule change
Symptom: a user can access the community but can’t create a new group, or sees an unexpected restriction. Possible cause: a group-creation limit is set for the user’s level, the quota has been reached, or the wrong level is being checked. What to check: open the limit setting separately and check how many groups the test account has already created. Don’t combine this test with access to an existing group.
How to fix it: set a reasonable limit for the level or temporarily remove the quota while testing. Then create a new, clean group with the test account and try again. When to roll back: if a group-creation limit doesn’t solve a specific moderation problem, remove it instead of leaving a hidden barrier for members.
The administrator sees everything, but regular users get different outcomes
Symptom: settings appear to work in the admin session, but regular members report problems. Possible cause: you only tested as an administrator, whose capabilities, cookies, and exceptions are different. What to check: use a matrix with several accounts and open a new private window for each user state.
How to fix it: make regular test accounts a permanent part of your change process. When to roll back: if you can’t tell which rules were changed after a broad update, return to the last documented checkpoint, restore one route, and proceed one item at a time.
How you’ll know the fix worked: the problem is gone for regular users as well as the administrator, and every row in the access matrix produces the expected outcome consistently.
Product limitations and decisions a setting can’t replace
Restrict Content Pro BuddyPress helps connect membership to social features, but it doesn’t replace privacy planning. If you need legally significant separation between organizations, fine-grained access to individual files, corporate single sign-on, or custom exceptions for hundreds of profiles, levels and member types alone may not be enough. In those cases, define the data and permissions model first, then decide which parts the integration can automate.
Keep in mind that BuddyPress and BuddyBoss aren’t the same platform. BuddyBoss help describes specific settings for its platform and points to a separate support path. If your site uses classic BuddyPress, don’t assume the menu names and component list are the same. Check the actual items in your admin area and test on a copy of the site. This is more accurate than promising identical compatibility across different social platforms.
When not to use a member type as an access flag
A member type works well when it genuinely describes someone’s place in the community, such as student, mentor, partner, or alumnus. It’s a poor choice as a temporary technical flag if the same type is also used for search, profile design, or an independent role. In that case, a membership change could affect not only access but also how other members see that person. Before using a type as an access condition, ask: "Is it safe for this type to disappear when the membership is no longer active?"
If the answer is no, restrict access by level or create a separate classification that’s used only for access. This adds one more item to the model but avoids overloading the meaning of an existing type. A clear model is easier to maintain through updates and administrator changes.
Why hiding a menu isn’t the same as protecting a page
Hiding a menu item can improve navigation, but it doesn’t control access. Users can still follow a saved address, a link from an email, or a bookmark. Permissions need to be checked on the route or item itself. The theme, menu builder, and CSS work alongside or after the access rules; they don’t replace them. If an item or component is restricted only in appearance, the setup is incomplete.
Search and other public traces
Restricting access to a page doesn’t automatically remove its title, excerpt, menu link, or search-index entry. Check public lists, archives, and widgets separately. Don’t promise users "complete invisibility" just because you restricted a group’s contents. If necessary, create a public information page, then check exactly which details are available to users who aren’t signed in.
This is especially important for internal communities. A clear public page can explain the community and send people to a safe login, while details about members, activity, and files stay in the private area. That’s usually more helpful than an empty error or an unexpected redirect.
Keep the access model clear for editors and support
Once you’ve completed the initial setup, focus on documenting the rules for your team instead of adding ten more restrictions. Create a short record for each private area: its purpose, permitted levels, required type, associated group, public denial message, and test URL. Store these records where editors creating new groups will find them. This isn’t bureaucracy. It helps prevent someone from accidentally publishing an open space.
Plan regular checks of the member lifecycle. A new user gets access, an active member uses the group, the status changes, the type is removed if needed, and access ends. The clearer this path is, the easier it is to answer "Why can’t I see the group?" without granting extra permissions. Don’t assign an administrator role as a quick fix for a complaint. That hides the cause and creates a more serious risk.
A process for adding a membership level
Describe the new level first, then create it as a test, map it to a separate type, and test it with one group before making it available to active members. Don’t copy a level without reviewing all inherited rules. A similar name doesn’t guarantee the same access policy. If you do need to copy it, recheck the member type, group-creation limit, component restrictions, and denial path.
In the end, write messages for people, not just for the system. A denial message should explain the next step without pressuring the user to buy something or making them guess at the cause. For a company space, that could be "Contact your organization’s owner." For a course community, it might be "Check that your membership is active." Clear messages reduce support requests and help members trust the community rules.
A final check before opening the community to members
Before launch, run through the setup from a user’s perspective, not just a technical one. Ask someone who wasn’t involved in the configuration to follow the path of a regular visitor: open the community page, sign in, find their group, try to open an area they can’t access, and make sense of the denial message. Then give an active member the same task. If both people understand what’s happening, the access model is configured and explained clearly.
Check all three layers together. The data layer: is the right level active, and does the profile have the matching type? The rule layer: is the restriction applied to the group, page, or component? The presentation layer: are links, messages, and buttons clear? An issue at one layer can look like a problem at another. An easy-to-miss theme message may look like missing access, while an outdated cache may look like the wrong membership status.
Routes that are easy to overlook
In a new session, open more than the group’s main page. Check an internal tab, activity, a member page, profile settings, and the address from a notification. If you use the messaging component, test both the conversation list and the action for starting a new message. If members can create groups, test that limit separately. On a multilingual site, repeat the critical checks in each language. A translated page shouldn’t become a different item with an empty set of conditions.
If a setting changes how profiles appear, make sure it doesn’t expose an internal type to people who don’t need to see it. A public "Mentor" label may be part of the community experience, but a technical value like "Access-2" shouldn’t become a user-facing label. Separate internal values from human-readable names during planning.
What to record after a successful test
Record the date, owner, routes tested, and outcome for each test account. Add a screenshot for internal support, not publication, showing where the restriction panel is and what a correct outcome looks like. Keep version details as internal records, but don’t include them in user-facing copy. After an update, this information can help you figure out whether a behavior change came from the integration, theme, social component, or cache.
Once every row in the matrix passes, don’t keep changing settings "just to be safe." A documented, simple model is better than a complex one no one can maintain. Add new levels, groups, and components through the same short cycle: map the rule, test one item, check it with three users, test the reverse path, and record the outcome.
A video showing the add-on’s historical interface
For reference, you can watch this video specifically about the Restrict Content Pro - BuddyPress add-on. It provides visual context for the older interface and the general idea of connecting Restrict Content Pro to a social platform. Don’t follow its steps mechanically if the menu names differ in your installation. Check the interface you actually have and use the access matrix described above.
As you watch, focus on the sequence rather than the admin panel’s appearance: activating the add-on reveals integration settings, a membership level can be mapped to a member type, and a rule is checked on the target community item. That sequence remains useful even if the interface changes.
Restrict Content Pro BuddyPress FAQs
Do I need this add-on if I already restrict standard WordPress pages?
You need it when restrictions must cover community-specific items such as profiles, groups, activity, components, or permissions tied to a member type. Restrict Content Pro’s built-in features are usually enough for a couple of standard pages. First decide whether you’re protecting WordPress content or BuddyPress features and spaces.
Can I restrict the entire social section of my site?
The integration documentation describes a mode that restricts the entire community and redirects users who aren’t signed in to a login or membership page. Before enabling it, check that the login page, password recovery, and administrative routes remain accessible. Then test the components’ direct URLs, not just their menu links.
What does the Member Type field on a membership level do?
It maps a Restrict Content Pro level to a member classification in the social platform. When membership changes, the type may be assigned or updated, and can then be used in rules and profile displays. Create and test the type before using it in access restrictions.
Should I use a membership level, WordPress role, member type, and group at the same time?
Only if each condition represents a separate, genuine reason for granting access. For your first setup, choose one primary condition and test it. Combining conditions can make access more precise, but it also makes it harder to find the cause when a user is denied.
Why does an active member still see a restriction message?
The cause is usually somewhere in the chain: the level isn’t active, the type wasn’t assigned, there’s an extra group condition, the user doesn’t belong to another required group, or the page is coming from a cache. Check the path from membership status to the specific route, not just the user’s name in their profile.
Can I prevent users from creating groups but let them view the community?
Yes. These are separate rules. The documentation describes a group-creation limit based on membership level, while different conditions control access to existing groups. Test them separately: a user may be allowed to see a group but not create one.
Does the integration work with BuddyBoss?
BuddyBoss help materials describe the integration for that platform and point to a separate support path. If you use BuddyBoss, check the interface settings against its documentation. If you use classic BuddyPress, don’t assume BuddyBoss’s menu names apply. First confirm that your installation exposes the required features.
How can I test the end of a membership without affecting real members?
Use a separate test account with one test level. Check its access while active, then change only that account’s status using the standard method for your installation. Start a new user session and open the same URL. If the type is removed when the membership is canceled or expires, check the profile as well.
When this integration is a good fit
Use Restrict Content Pro BuddyPress when membership should genuinely change access to an active community, including profiles, groups, activity, or specific features. Its strength isn’t the number of available options. It’s the clear connection between membership level, member type, a rule on the relevant item, and a testable outcome. For a private club, course group, or client space, this model makes access easier to manage and explain.
Start with one test area, one active account, and one clear access condition. Test a guest, a regular user, an active member, and a user after their status changes. Then expand the model to more groups and components without losing track of what each setting does. Once you have a map of routes, levels, and types, you can download Restrict Content Pro BuddyPress and follow the same safe process on a copy of your site.

