


PeepSo File Uploads - WordPress Plugin
The given WordPress plugin is a versatile file upload solution designed specifically for use with the PeepSo social networking platform. This plugin seamlessly integrates with PeepSo to enhance the community experience by allowing users to easily share files with each other. With PeepSo File Uploads, users can upload and share a wide variety of files, including documents, images, videos, and more.
Plugin Features
PeepSo File Uploads provides a user-friendly interface that allows users to upload files directly from their devices or from popular file storage services such as Dropbox or Google Drive. It also offers robust file management features, allowing users to organize their files into folders and easily search for specific files within their uploaded content.
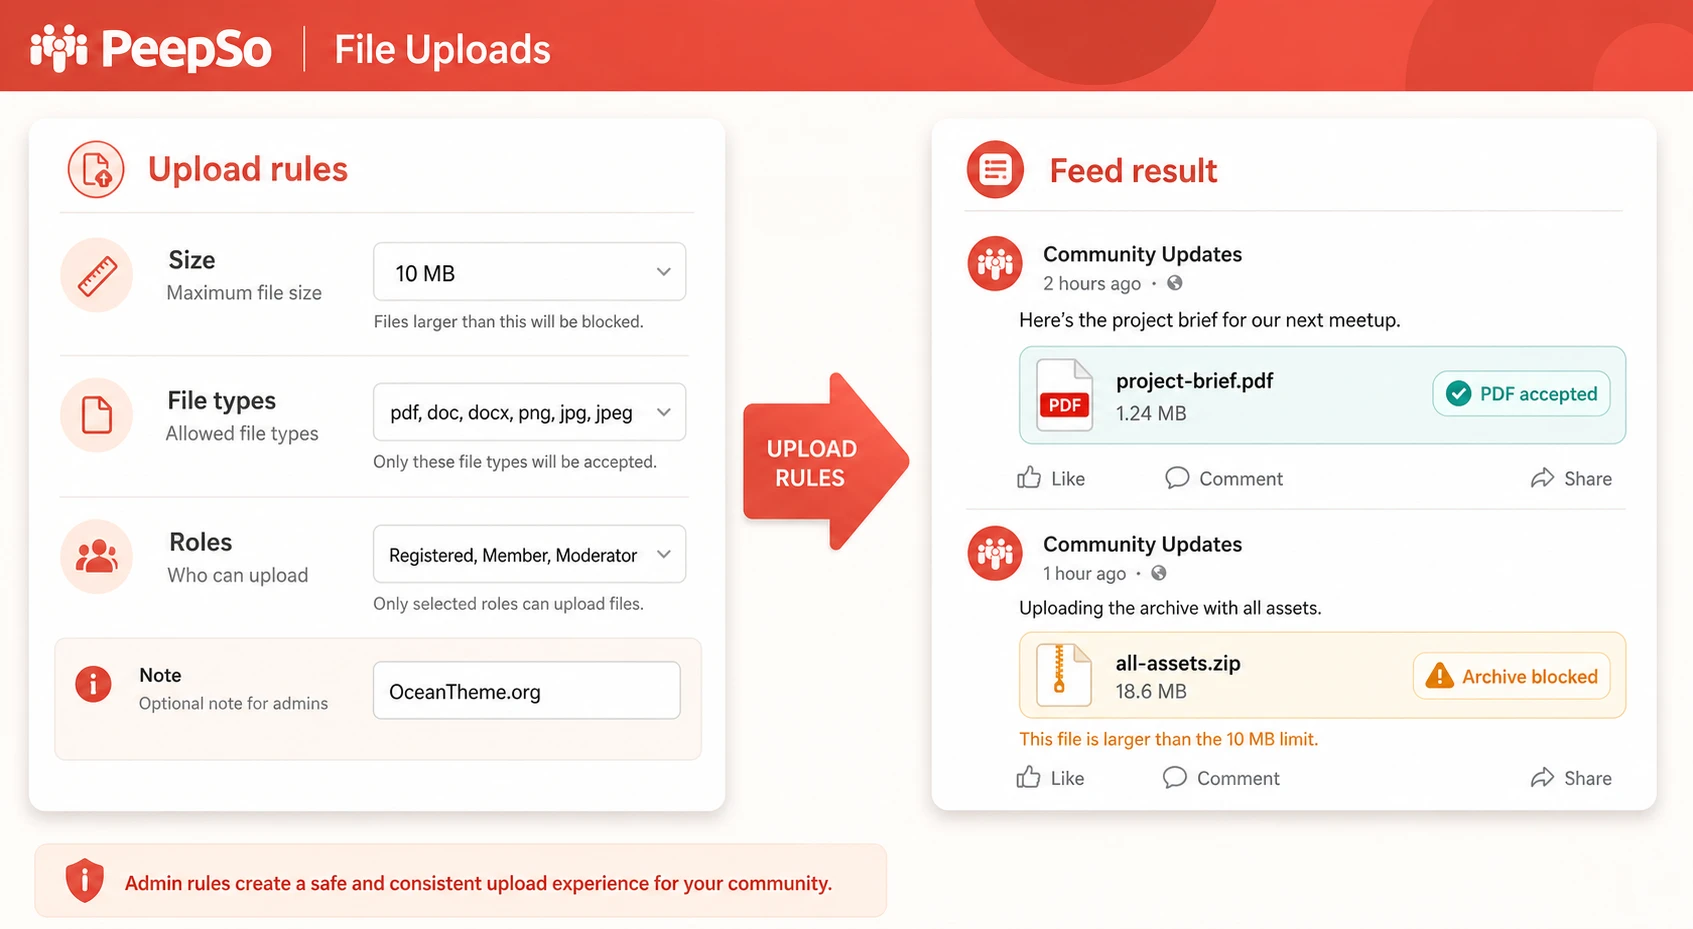
In addition to the file upload functionality, this plugin also provides a range of customization options for site administrators. They can set specific file upload limits, define file types that are allowed or restricted, and even restrict file uploads to certain user roles or membership levels. This gives administrators full control over the file sharing capabilities within their PeepSo community.
From a user perspective, this plugin enhances the overall engagement and interaction within the community. Users can easily share files with their friends, colleagues, or other community members, fostering collaboration and communication. Whether its sharing important documents, showcasing creative work, or simply exchanging multimedia content, this plugin makes file sharing effortless and seamless.
From a technical standpoint, this plugin is built to integrate seamlessly with PeepSo and is optimized for performance and compatibility. It is regularly updated by the developers to ensure compatibility with the latest versions of WordPress and PeepSo, as well as to add new features and address any potential issues or security concerns.
Overall, PeepSo File Uploads is a valuable addition to any PeepSo-powered community, providing a powerful file upload functionality that enhances user engagement and facilitates seamless sharing of files within the community. With its intuitive interface and robust customization options, it offers a comprehensive solution for both site administrators and users alike.

How to Configure PeepSo File Uploads for File Sharing in a WordPress Community
PeepSo File Uploads is not meant for the standard WordPress Media Library. It serves a more practical purpose: letting PeepSo community members attach documents, archives, images, and other allowed files to discussions without forcing the administrator to manually forward materials through email or third-party cloud services. In this guide, we'll look at how to approach installation, which settings to review after enabling it, how to safely restrict file types and sizes, how to test the result from a regular member account, and what to do if uploads do not appear in the activity feed.
This article is written for site owners, WordPress administrators, or community moderators who already understand the basic PeepSo model: the site is built around profiles, the activity feed, groups, and interaction between registered users. File Uploads extends that workflow with file attachments, so the real goal here is not just to "turn on a button," but to set rules that make file sharing convenient for members without turning the site into an uncontrolled storage dump.

This article does not cover purchasing instructions, license bypasses, or plugin code modifications. We are focusing on real-world use of a product you already have: preparing the site, configuring uploads, verifying permissions, testing a realistic workflow, and troubleshooting. Where the exact interface item depends on the PeepSo version or the set of installed add-ons, the wording is intentionally cautious: check the relevant PeepSo settings section, and any uncertain details are moved to notes.
What Problem the PeepSo File Upload Add-On Actually Solves
In a standard WordPress blog, files are usually uploaded by an editor: they open the Media Library, add an image or document, and insert it into a post. In a private or semi-open community, the logic is different. Files appear as part of the conversation: a member attaches a PDF guide to a discussion, an instructor shares an assignment template with a group, a client uploads an error screenshot in a private exchange, or a moderator asks someone to attach a log file or document to a thread. If you rely on external email for each of these cases, the conversation gets scattered across channels, while the community itself is left with only fragments of the context.
PeepSo File Uploads closes that gap. Its purpose is to tie the file to the place where the conversation is happening: a post, a comment, a group discussion, or another PeepSo interface if that workflow is supported by your installed add-ons. The user does not see an abstract file manager. They see a familiar action: "attach a file to this post." The administrator, in turn, has to decide which formats are allowed, what file size is acceptable, who is allowed to upload files, and where the line is between convenience and risk.
When a Community Truly Needs File Attachments
File attachments are useful when the content has practical value, not just an emotional reaction. On an educational site, that might include assignments, presentations, spreadsheets, and review materials. In a member club, it could be routes, diagrams, checklists, or document templates. In a client community, it might be instructions, diagnostic files, screenshots, or exported reports. On an internal company portal, it could be policies, forms, drafts, and working files attached to discussions.
The clearest sign of a good use case is that the file helps continue the conversation inside the community. If attachments are used only as a public document library, a dedicated document plugin or knowledge base is usually a better fit. If files need to stay tied to users, groups, discussions, and moderation, PeepSo File Uploads makes more sense.
How This Differs from the WordPress Media Library
The WordPress Media Library was built as a tool for site authors and editors. It works well for images, documents inside posts, page attachments, and content management in general. But it is not a convenient interface for an ordinary community member: regular users should not need access to the admin dashboard just to upload a file. It also does not explain which discussion an attachment belongs to, who uploaded it, who should be able to see it, or whether moderator intervention is needed.
The PeepSo file add-on works much closer to the social workflow: the user uploads a file in the context of communication, not into an abstract library. That changes the configuration requirements. You have to think not only about file size and extension, but also about visibility, roles, groups, privacy, abuse reports, cleanup of old materials, and moderator response.
Who PeepSo File Uploads Is For and When Another Approach Makes More Sense
This add-on makes sense for a site where PeepSo is already used as the core community layer, or where a new community is being built around profiles and the activity feed. It does not replace PeepSo as a whole, and it does not turn a regular site into a social network by itself. Before installing it, separate real needs from the impulse to "add one more feature." File uploads increase storage load, complicate privacy, and create a new channel for potentially harmful content.
A strong candidate for PeepSo File Uploads is a community where members regularly exchange files and the administrator is prepared to set clear rules. If the site has ten active users and files appear once a month, you can probably start with a simple contact form or a private document page. But if the conversation is active and attachments are needed in almost every thread, manual workarounds quickly become inconvenient.
Good Project Fits
- Learning communities. Members attach homework, study guides, spreadsheets, and other materials to group discussions.
- Private clubs and associations. Files help members share schedules, protocols, diagrams, routes, and working documents.
- Client portals. A user can attach a screenshot, report, or document directly in the problem discussion instead of sending it in a separate email.
- Internal teams. For a small team, PeepSo can serve as a convenient social layer where attachments stay linked to ongoing work discussions.
Cases Where You Should Be More Careful
You should not enable file uploads on an open site without registration unless you have clear moderation rules and restrictions in place. The more unknown users can submit attachments, the higher the risk of junk uploads, spam, excessive disk usage, and complaints about content. For public support scenarios, it is often better to use a ticketing system with well-defined restrictions, because it is usually better tied to statuses, assigned staff, and archival workflows.
You should also be cautious with files that contain personal data, business documents, or medical information. WordPress provides personal data export tools, and plugin developers may integrate with them, but the site administrator is still responsible for defining clear retention, access, and deletion rules. If your site handles sensitive documents, align the process with your security lead or legal advisor first.
A practical rule: if a member can upload a file, the administrator should already know who will be able to see it, who can report it, who can remove it, and how well the site can handle data growth over time.
What to Check Before Installation
File uploads may look like a small feature, but they immediately touch the server, WordPress, PeepSo, the theme, user permissions, and moderation policy. It is worth doing a short preparation pass before installation. This is not a formality: many upload problems are caused not by the add-on itself, but by hosting limits, caching conflicts, or incorrect expectations about user roles.
The Basic WordPress and PeepSo Stack
First, make sure the core PeepSo plugin is installed, activated, and working properly with your current theme. Check profile pages, the activity feed, registration, and login. If the base PeepSo feed is already producing errors, attachments will only add another layer of uncertainty. The logic is simple: File Uploads should extend a stable community layer, not mask core issues.
Next, review how user roles work on the site. WordPress distinguishes between user roles and capabilities, and plugins can add their own access rules. Built-in WordPress capabilities matter as a general principle: a user action should be verified at the permissions level, especially if it sends data to the public-facing part of the site. In practice, that means you should test PeepSo not only as an administrator, but also as a regular member.
Server Limits and Maximum File Size
Even if the plugin allows file attachments, the actual limit is controlled at several levels: PHP settings, the web server, WordPress, and the add-on itself if it provides a separate limit. WordPress calculates the maximum upload size based on PHP settings, including upload_max_filesize and post_max_size. If a user gets an error when uploading a larger file, do not start by reinstalling PeepSo. First, check the upload limit shown in the WordPress Media Library and review your hosting settings.
For a community site, it is usually best to start with a moderate limit. If members only need PDFs, images, and small documents, there is no reason to allow large archives and video files right away. Large files fill disk space quickly, take longer to pass through security checks, and are more likely to fail on slow connections. Video and large media files are usually better handled through separate video hosting or a dedicated service, while PeepSo can store a link or a small supporting file.
Allowed Formats and Security Policy
WordPress checks file types by matching the extension to a MIME type. That does not make uploads completely safe, but it does provide a basic filter: the file must belong to an allowed set, and for images WordPress attempts to detect the real type. Administrators should not expand the list of allowed formats without a clear reason. The broader the allowed set, the harder it becomes to explain the rules to users and the greater the risk of a dangerous attachment.
To start, documents, images, and simple archives are usually enough if archives are genuinely needed. Executable files, scripts, unknown binary formats, and macro-enabled documents are better excluded unless you already have a separate, protected review process. In your community rules, plainly explain which types of materials can be attached and what moderators will remove without debate.
Cache, CDN, and Protection Layers
Caching plugins, CDNs, and security filters can interfere with upload forms. They may delay feed updates, block an AJAX request, strip request parameters, or limit large POST requests. Before installation, document which optimization layers are already active: page cache, JavaScript minification, deferred script loading, host-level web protection, or external anti-attack protection. After enabling File Uploads, test the activity feed page with aggressive optimization disabled for PeepSo pages if you start seeing symptoms.

Installation and the First Low-Risk Validation
Install the add-on the same way you install other WordPress plugins, but first make sure you have a safe rollback point: a backup of files and the database, admin access, and a way to disable the plugin through the hosting panel or file manager. This is especially important on sites with active communities, because any issue in the activity feed becomes immediately visible to users.
If the site already has active members, it is better to test File Uploads on a staging copy or inside a private group first. If that is not possible, choose a low-traffic period, notify moderators, and roll the feature out in stages: first for the administrator, then for a test user, then for a small group.
General Installation Sequence
- Make sure the core PeepSo plugin is active and its pages open without critical errors.
- Upload and activate PeepSo File Uploads in the WordPress admin panel under
Plugins. - Open the PeepSo settings and find the options related to file attachments, uploads, or allowed file types.
- Save the settings without making drastic changes if you are not fully sure what a specific option does.
- Open the PeepSo feed in a private browser window as a test user and check whether the option to attach a file is available.
Do not run your first test as an administrator. Administrators often have more permissions than regular members, so a successful upload from an admin account proves very little. You need a separate user with a typical community role. If PeepSo uses its own access levels or group rules, test the exact level that will be uploading files in real use.
The First Test File
For the first check, do not use a large archive or a file with a complicated name. Use a small PDF or image with a Latin filename, such as test-community-file.pdf. The goal of the first test is to verify that the entire chain works: the user selects a file, submits the post, sees the attachment in the feed, and another user can open or download it with the expected permissions.
Once the basic check succeeds, move on to filenames in Russian, spaces, multiple attachments, the maximum allowed size, and a blocked format. This order saves time: if a simple file does not upload, there is no point arguing with the settings for a more complicated format.
What Counts as a Successful Enablement
Installation is not complete when the plugin is activated. It is complete when the result has been verified in the public-facing part of the site. At minimum, that means the file attachment button or drop zone is visible to the intended role, the file uploads successfully, the attachment is saved next to the post, users without extra privileges only see content they are allowed to see, blocked formats are rejected with a clear message, and the moderator understands how to remove inappropriate material.
Post-Installation Settings: Size, Formats, Access, and Moderation
The settings area is the most important part of PeepSo File Uploads. It is easy to make mistakes in either direction. Rules that are too loose create a storage pool full of unknown files. Rules that are too strict make the feature useless. The right configuration begins with one question: what files do members actually need to exchange inside the community, and in what context?
Limiting File Size
Start with a limit that covers common use cases without encouraging people to upload heavy materials. For documents, spreadsheets, and small images, a moderate value is usually enough. If members will be sharing screenshots of issues, it is better to ask them to compress the image or use lightweight formats. If you truly need video, audio, or large archives, evaluate hosting capacity, backup strategy, and retention rules separately instead of simply raising the limit.
Check three levels: the limit in the plugin settings, if it exists; the WordPress limit shown in the Media Library; and the PHP and web server limits on the host. If the plugin is set higher than the server allows, users will still hit the server-side limit. In that case, changing PeepSo alone will not help.
How to Pick a Starting Value
Gather 5 to 10 real files that members are likely to attach: a study guide, an image, a spreadsheet, a report, an archive with materials. Check their sizes and choose a limit with a small buffer. Do not base the decision on the theoretical maximum allowed by your hosting plan. If the heaviest useful file is only a few megabytes, there is no reason to open the door to tens or hundreds of megabytes for every user.
Allowed File Types
Format restrictions are not cosmetic. They reduce the chance that members will upload executables, unknown archives, or documents with unsafe content. WordPress has a built-in allowed MIME type mechanism, but a community administrator needs to think more broadly: what format is actually needed in the discussion, and how will a moderator know whether the file is safe?
For most community use cases, you can start with images, PDFs, basic office documents, and archives if they are truly needed. If you allow archives, tell members that they must not contain executable files. If the site handles confidential documents, also think about retention periods and access to attachments after a user leaves the group.
Testing a Blocked Format
After configuring the settings, make sure you try uploading a format that should be rejected. Do not use a dangerous file. It is enough to take a normal text file and rename its extension to a format you did not allow, or use a safe test file of an unsupported type. The goal is to confirm that the user gets a rejection and the feed does not publish a broken attachment.
Who Should Be Allowed to Upload Files
Ideally, upload permissions should match the level of trust you place in the user. A registered member with a confirmed email is one level. A brand-new user with no history is another. A moderator or group owner is a third. If PeepSo or your connected membership system lets you segment access, do not open attachments to everyone at once. Start with a trusted user group and expand access after observation.
Check how uploads behave in different areas: personal feed, group, comments, and private messages if those areas are available in your setup. Do not assume the same rule applies everywhere. In community plugins, context often matters more than the generic WordPress role.
Attachment Visibility and Privacy
A file should inherit the expected visibility of the place where it was attached. If a post is published in a private group, the attachment should not become available to a random visitor. If a file is attached in a private conversation, users should not be able to share a direct link that anyone can open. The exact implementation depends on PeepSo and the server, so this must be verified manually.
Open the attachment in another browser while logged out. Then sign in as a user who is not a member of the relevant group. Then test as a group member. If the behavior does not match expectations, do not roll the feature out to the full audience until you understand exactly how the link is generated and which access rules are being applied.
Moderation and Removal
Before launch, decide who removes inappropriate attachments. In a small community, that may be the administrator. In a group with active members, you need moderators. The community rules should clearly state that a moderator may remove a file if it is off-topic, violates rights, includes personal data without consent, or creates a security risk.
Do not postpone moderation planning. Files are harder to review than text comments: part of the content is visible only after download, and the risk may surface later. The clearer the rules are before launch, the fewer conflicts you will have afterward.
Files in the Feed, Groups, and Discussions: Building a Real Workflow
The real strength of file attachments in PeepSo is context. The same document can be useful or unnecessary depending on where it is attached. That is why configuration should be tied to real workflows, not just a settings panel. Picture the member journey: they open a group, write a post, add a file, explain what it is for, get comments, and later a moderator checks whether the file is still relevant.
Activity Feed
The feed works well for materials that many members should see: an announcement, a file attached to a discussion, a general instruction, a sample report, or a template. The description next to the attachment matters a lot here. If a user simply attaches a file without any explanation, other members do not know why they should open it. In your community rules, ask people to include a short context note: what is inside, who needs it, and why the file is attached.
It also makes sense to limit heavy files in the feed and avoid turning it into an archive. If members regularly post large numbers of documents, it is better to create a separate category, group, or document library and leave only discussion links in the feed.
Groups
Groups provide a more precise context. In a study group, files may be part of a lesson. In a client group, they may be part of support. In a club group, they may be part of an event. Check how group access permissions affect attachments. A user who is not part of the group should not see materials from a private discussion. If direct file links bypass the expected privacy rules, that issue must be fixed before launch.
In larger groups, it is useful to appoint moderators who understand the subject matter. The site administrator may not know whether a file is relevant to a specific course or project, but a group moderator can usually tell the difference between a useful attachment and junk much faster.
Comments and Clarifications
If your PeepSo configuration allows files to be attached to comments, use that for clarifications: an error screenshot, a supplementary document, or a corrected version of a file. But do not move the entire discussion structure into a chain of attachments. If too many files accumulate in comments, it becomes hard for users to find the final version. For working materials, it is usually better to pin the final file in a separate post or document the final solution elsewhere.
Private Exchanges
Files in private communication are especially sensitive. They are convenient for support, but they are also more likely to contain personal data, admin panel screenshots, order numbers, or internal documents. If you need this workflow, define the rules in advance: what data should never be sent, what files a moderator will remove, how long materials remain in the system, and how a user can request deletion.

Practical Example: Uploading a Training PDF to a Private Group
Let's walk through a specific example that clearly shows how PeepSo File Uploads works. Assume the site has a private training group. The administrator wants members to be able to attach completed assignments as PDFs, while the instructor and moderator can open the file directly from the discussion. At the same time, a random visitor or a member of another group should not be able to see the attachment.
Goal
Create a working process where a registered group member publishes a post with a PDF attachment, another member of the same group can see the file, the moderator can remove an inappropriate upload, and a user outside the group cannot access the material through the community interface.
Preparation
Before the test, you should already have the core PeepSo plugin, a private group, PeepSo File Uploads, a test member inside the group, a second test user outside the group, and a small PDF file with safe content. If you are testing on a live site, create a file with no personal data so you do not accidentally expose sensitive information if access rules fail.
Steps
- Sign in as an administrator and confirm that PDF is allowed in the file settings and that a reasonable size limit is in place.
- Sign in as the test member who belongs to the private group.
- Open the group page and create a post with a short message: "I'm attaching my completed assignment for review."
- Attach the PDF using the available button or upload area in the PeepSo interface.
- Publish the post and wait until the attachment appears in the group feed.
- Sign in as another member of the same group and verify that the file opens or downloads as expected.
- Sign in as a user outside the group and confirm that the post and attachment are not visible through the group interface.
- Try the direct file link in a private browser window while logged out and compare the result to your privacy policy.
Result Check
A successful result looks like this: the member sees the attachment in their own post, other group members can tell it is a PDF, the moderator can remove the post or attachment, and an outside user cannot see the material in the interface. If the direct URL is accessible to everyone, evaluate that separately. Some sites intentionally store media files publicly, but for private course materials that may be unacceptable.
A Detail People Often Miss
Do not test only the moment of upload. Test the full lifecycle of the file. What happens if the member deletes the post? What does a user see after being removed from the group? Does the file remain accessible through the old link? Does it end up in backups? These questions rarely come up during the first happy-path test, but they are exactly what determines whether the solution is suitable for a serious community.
Quick takeaway: a practical test should include three roles - the file author, an allowed recipient, and a user without access. Otherwise, you are only testing the upload itself, not privacy.
How to Verify the Result After Configuration
After installation and the first practical test, run a more systematic verification pass. A useful way to think about it is as a chain: starting conditions, user action, product logic, visible result, error handling, and rollback. If every stage is clear, the feature is ready for launch. If one stage still feels like "it probably works," test it before announcing the feature to users.
Checking a Normal File
Upload a small allowed file in the feed, a group, and a comment if those contexts matter for your setup. Check how the interface displays the filename, icon, size, or other metadata. Make sure the file can still be opened after a page refresh and after signing in again. If the attachment is visible only before reload, the issue may be related to data persistence, caching, or a JavaScript conflict.
Checking the Size Limit
Prepare one file that is slightly below the limit and one that is slightly above it. The first should upload successfully, and the second should be rejected clearly. If both go through, the rule is not working or is being applied in the wrong place. If both are rejected, the server-side limit may be lower than you think. Compare the result with the WordPress Media Library and your hosting settings.
Checking a Blocked File Type
The user should get a rejection before publication or immediately after the upload attempt. The bad outcome is a post that appears with an empty or broken attachment. In that case, the member does not understand what happened, and the moderator gets junk in the feed. If the error message is too technical, add a plain-language explanation to the community rules or to an onboarding post for members.
Checking Access
Test access in four states: the file author, another allowed member, a logged-in user without access to the group, and a guest who is not signed in. If the site uses page caching or a CDN, run the test in a private browser window and after clearing the cache for the relevant pages. This is especially important for private groups: you cannot rely on simply hiding a button visually, you need to understand what happens with the attachment itself.
Checking the Mobile View
Many members will upload files from a phone. Verify that the attach button is visible, that it is not being covered by the theme, that file selection is usable, and that the upload indicator does not disappear. If the mobile interface breaks, do not rush into random CSS changes. First disable minification, check for a theme conflict, and compare the behavior against a default theme. Only then does it make sense to add a careful visual fix.
Managing Files: Storage, Privacy, and Performance
Once the feature is live, file uploads start to develop their own operational life. Members get used to attaching materials, old files accumulate, backups grow, and moderators take on new tasks. If administration is not planned in advance, the site may run into disk space limits, slow backups, or disputes about old files a few months later.
Where the Line Falls Between Discussion and Archive
The PeepSo feed is convenient for exchanging current materials, but it is not always the right place for a long-term library. If the same document needs to remain discoverable for months, create a separate page, knowledge base entry, or pinned post. File Uploads works best as part of the conversation: the file explains the post, supports a request, confirms a problem, or delivers a working document at the right moment.
Cleanup and Retention
Decide what should happen to old attachments. You may choose not to delete anything if the site is small and the files are harmless. But on an active project, it is better to have a rule: student work is kept until the course ends, temporary diagnostic files are removed after the issue is resolved, outdated document versions are replaced with a link to the final file. The exact mechanism depends on PeepSo settings and site policy, but the principle should be clear to users.
Backups
User files become part of the overall backup strategy. If uploads are frequent, backups become heavier and take longer to restore. Make sure your backups include the necessary directories without creating endless growth because of temporary files. For larger communities, it is worth separately evaluating external storage or stricter attachment size limits.
Personal Data and Export
Files can contain personal data even when the site itself does not explicitly ask users to enter it. A screenshot, PDF, spreadsheet, contract, or request form often includes names, email addresses, phone numbers, and internal details. WordPress has personal data export tools, and plugins may add their own data to that export, but administrators should not treat that as automatic protection. In your community rules, explain what data users must not attach and where they can request removal of uploaded materials.
Speed and User Experience
Files affect speed indirectly. A stored PDF does not slow down a page in the same way as a large hero image, but a feed full of attachments may require more requests, previews, access checks, and browser processing. Watch the pages of active groups closely: if they become too heavy, reduce file size limits, lower the number of attachments allowed per post, or move permanent materials into a separate structure.
Common PeepSo File Uploads Problems and Troubleshooting
File attachment issues often look similar: the user clicks the button and nothing happens; the upload completes and then disappears; the file is visible to the author but not to others; a large file fails with no clear message. To avoid changing settings blindly, move from the symptom to the cause.

The File Attachment Button Is Not Visible
Symptom: there is no upload button in the feed or group even though the add-on is activated. Possible causes: the feature is disabled in settings, the user role does not have access, the selected context does not support attachments, the theme hides the interface element, or JavaScript optimization is causing a conflict.
What to check: sign in as an administrator, open the PeepSo settings, confirm that the add-on is active, open the page as a regular test user, compare the feed and the group, and temporarily disable aggressive minification on PeepSo pages. If the button appears for the administrator but not for a member, the issue is almost certainly related to permissions or access rules.
How to fix it: enable the needed workflow, expand access only for the appropriate user group, exclude PeepSo pages from the problematic optimization layer, or investigate the theme conflict. If the button comes back after disabling optimization, do not leave everything disabled globally. Add targeted exclusions instead.
An Oversized File Will Not Upload
Symptom: the upload indicator fails, a server error appears, or the post is not submitted. Possible causes: the PeepSo limit is higher than the PHP limit, post_max_size is smaller than the request size, the web server blocks large POST requests, or host-level security is blocking the attachment.
What to check: look at the maximum upload size shown in the WordPress Media Library, compare it to the add-on settings, and test a file just below the limit and one just above it. If the smaller file works and the larger one does not, do not reinstall the plugin. First align the limit with your hosting environment.
How to fix it: lower the PeepSo limit to a value the server actually supports, or increase the limit on the host. For a community site, it is often safer to lower user expectations than to allow large files for everyone.
An Allowed File Is Still Rejected
Symptom: the user uploads a PDF, image, or document, but the system treats the format as invalid. Possible causes: the extension is not included in the rules, the file's MIME type does not match the extension, the file is corrupted, the browser submitted an unexpected type, or a security plugin interfered with the request.
What to check: upload a different file of the same format, rename the test file using Latin characters, and test it in the WordPress Media Library. If the Media Library also rejects it, the problem is broader than PeepSo. If the Media Library accepts it but PeepSo does not, look for a restriction in the add-on settings or in the specific context where the upload is happening.
How to fix it: add the format only if it is truly needed, replace the corrupted file, or ask the user to export the document again. Do not expand the list of formats for one questionable edge case.
The Attachment Is Visible to the Author but Not to Other Members
Symptom: the author of the post can see the file, but another member sees an empty area, gets an access denial, or cannot see the post at all. Possible causes: different permissions inside the group, the post is restricted to the author, the cache is showing an outdated version of the feed, the file was not fully saved, or direct file access is controlled differently from post access.
What to check: use two test users with clearly understood roles, refresh the page without cache, verify the visibility of the post itself, and then test file access separately. If the user cannot see the post, the issue is not the file. If the post is visible but the file is not, check the attachment rules and storage path.
How to fix it: bring group permissions and attachment settings into the same logic. If the site requires strict privacy, do not launch file uploads until you have confirmed that private attachments are not exposed accidentally.
The Feed Layout Breaks After Uploading a File
Symptom: the post card stretches, buttons shift out of place, the filename overlaps text, or the mobile view becomes awkward. Possible causes: a theme conflict, excessively long filenames, PeepSo styles being overridden, or CSS minification changing the order in which styles load.
What to check: test both a short and a long filename, compare the mobile and desktop views, temporarily disable CSS combination, and check the behavior with a default theme. If the issue appears only with your theme, fix it carefully through a child theme or custom CSS after verifying the selectors in the browser.
When to roll back: if enabling file uploads makes several key PeepSo pages unstable, disable uploads for members, keep the issue in test mode, and investigate the conflict separately. It is not worth leaving a broken feed on a live community just for the sake of a new feature.
How to Explain Upload Rules to Members
Technical configuration does not solve the behavioral side of the problem. A user is not expected to understand why they should not attach a large archive or a document containing someone else's personal data. If the rules are never explained, the moderator ends up arguing case by case. That is why it helps to prepare a short post or page with upload rules before launch.
What to Include in the Rules
- Which file types may be attached and for what purposes.
- What maximum file size is allowed and what to do if the file is larger.
- Which materials are not allowed: someone else's personal data, executable files, irrelevant archives, or materials without redistribution rights.
- Who can see files in the feed, in groups, or in private conversations.
- How to report an inappropriate attachment or request removal of your own file.
Do not write the rules like a legal document if your audience is unlikely to read one. A simple version works better: "Attach files only when they are relevant to the discussion. Do not upload documents that contain other people's personal data. If a file exceeds the size limit, use the approved external transfer method." A more detailed policy can live behind a separate link.
Launch Message Template
You can use the following text as the basis for an internal announcement and adapt it to your audience:
File uploads are now enabled in community discussions. Please attach materials that help move the conversation forward: documents, images, reports, and learning files. Do not upload other people's personal data, executable files, or materials you do not have the right to share. If an attachment is off-topic or creates a risk, a moderator will remove it.
That kind of message does not replace a privacy policy, but it does reduce accidental mistakes. Users follow rules more consistently when they understand the reason behind the restriction.
Launch Plan for a Live Community
If your site already has active members, turning on file attachments with one big switch is risky. People will immediately start testing the new capability in their own ways: someone will upload a large archive, someone will attach a screenshot containing personal data, someone will try a filename in Russian, someone will post a file in a private group and ask why another user can see it. That is why PeepSo File Uploads is best rolled out as a small project with clear stages.
A good launch plan answers four questions: who is testing, which files are allowed, where exactly the feature is enabled, and how quickly you can roll it back. If you have those answers, even an unexpected error does not turn into chaos. If you do not, moderators will end up figuring out the rules in the public feed, which is bad for both trust and security.
Stage 1: Closed Validation by the Administrator and Moderator
Start by validating the feature without regular users. Create or choose a private group that includes only the administrator, a moderator, and a test member. Check the basic formats, the size limit, attachment removal, visibility after logout, and behavior on a mobile device. At this stage, it does not matter whether the process looks polished. What matters is confirming that the upload chain does not break the feed or expose private materials.
It helps to keep a short test log: which file was uploaded, which user performed the action, what result was expected, and what actually happened. A simple document is enough. Later, that log makes it much easier to explain the issue to your hosting provider or a developer. The phrase "uploads are broken" is useless, while a note like "a 2 MB PDF uploads in the personal feed but fails in a private group for the Subscriber role" immediately points to a concrete check.
Stage 2: Pilot Group
After the closed test, choose a small group of real users who genuinely need file attachments. That might be a course group, a support team, a club committee, or a few regular members. Enable the feature only where it provides real value. Do not ask people to "just try it." Give them a real task: attach homework, upload an issue screenshot, share a template, or send a report.
The pilot phase surfaces questions the administrator would not have predicted. Members may use long filenames, Cyrillic characters, multiple dots in a filename, phone photos, or documents exported from a cloud editor. They may not realize the file has already uploaded if the interface does not show a clear status. They may attach a file without any explanation. None of that is necessarily a plugin bug, but it is a signal that your rules, limits, and guidance may need adjustment.
Stage 3: Rollout to the Right Roles
Once the pilot goes smoothly, expand access based on real need, not on the principle of "all registered users." If files are only needed in course groups, enable them there. If attachments are needed for client support, restrict the workflow to the support area. If the site is not yet able to moderate attachments quickly, do not open the feature in the main public feed.
The safest rollout is the one where the new capability appears exactly where people expect it. Users get a clear tool, moderators understand the context, and the administrator can monitor upload volume and adjust rules in time. A mass rollout without context usually creates extra files and extra questions.
Stage 4: Review After One Week of Active Use
After the first few days of use, return to the settings. See which file types are actually being uploaded, how much space they consume, which errors repeat, whether users complain about limits, and whether moderators can keep up. Do not raise the limit just because one user wants to send a large archive. First ask why that archive needs to live inside the PeepSo feed at all. In many cases, a separate storage method for large materials is the better answer, while the community keeps only the discussion and the link.
If users often attach files without a description, add a rule that any post with a file must include a short explanation. If outdated document versions keep appearing, designate a separate place for final files. If access questions come up often, check whether private groups, the public feed, and private discussions are being mixed together in confusing ways.
Decision Matrix Before Expanding Access
| Question | Good sign | Warning sign |
|---|---|---|
| Size limit | Typical files upload successfully, and heavy files are rejected clearly. | Users see broken uploads or a server error. |
| Formats | Only the necessary working file types are allowed. | The format list has been expanded "just in case." |
| Access | Private attachments are visible only to the expected users. | A direct link exposes the file to the wrong people. |
| Moderation | It is clear who removes a questionable file and under which rule. | No one is responsible for reviewing attachments. |
| Load | Disk usage, backups, and the feed remain manageable. | Upload volume is growing faster than expected. |
Useful Improvements Without Touching Plugin Code
With PeepSo File Uploads, you should not start by editing plugin files, adding hooks, or dropping in custom snippets unless the current documentation clearly confirms the extension point you need. In most cases, organizational improvements and safe technical adjustments are enough: exclude PeepSo pages from problematic caching, prepare usage rules, set up roles, check the mobile view, train moderators, and separate temporary attachments from permanent documents.
Cache and Optimization Exclusions
If the site uses page caching, deferred JavaScript loading, or file combination, review PeepSo pages especially carefully. Dynamic feeds, posting forms, and file attachments usually tolerate aggressive optimization much worse than static pages. The safe improvement is not to disable caching across the whole site, but to add exclusions for profile pages, the feed, groups, and other PeepSo sections where file uploads are used.
After each change, run the same test: open the page as a regular member, attach a small allowed file, refresh the feed, and open the post as another user. If excluding the page from cache makes uploads stable, document that decision in the site's internal notes so another administrator does not re-enable the same optimization later.
User Guidance
Sometimes the problem is not the configuration, but user expectations. A member tries to send a file that is too large, does not understand the allowed formats, or attaches a document without explanation. Instead of a complex interface customization, you can create a pinned post in the group, a short FAQ, or a simple internal guide. Include the allowed formats, size limit, an example of a good file description, and the contact path for questions.
If your theme allows you to add text next to the posting form through built-in PeepSo tools or a widget, use that carefully. The message should be short. Long warnings beside every post annoy users and go unread. Keep detailed rules on a separate page, and leave only one line near the form, such as: "Attach files only when they are relevant to the discussion; the size limit and full rules are listed in the group help page."
Separating Temporary and Permanent Materials
PeepSo File Uploads is convenient for temporary working attachments, but permanent documents need a more stable home. Divide your materials into two categories. The first is discussion-based files: assignments, screenshots, reports, drafts, and attachments tied to a specific question. Those can live in the feed. The second is final documents: policies, finalized templates, instructions, or lesson recordings. Those are better placed in a knowledge base, course page, or document library, while PeepSo carries the discussion and the link.
That approach reduces chaos. Members know where to find the final version, moderators do not have to clean up dozens of outdated attachments, and the feed stays a conversation rather than a file dump. For large communities, that matters more than any cosmetic patch.
Avoiding Unverified Snippets
It is easy to find advice online along the lines of "add this filter and allow any format." For file uploads, that approach is risky. If the PeepSo or WordPress documentation does not confirm a specific hook, do not paste random code into functions.php. In particular, do not change system MIME restrictions just to satisfy one user request. A safer approach is to create a separate process: the user sends the unusual file to a moderator or administrator, that person reviews it, and then uploads it manually to the appropriate place.
Code-level changes are appropriate only when they are minimal, reversible, documented, and fully understood by the responsible administrator. For most sites using PeepSo File Uploads, discipline matters more than a snippet: allowed formats, clear limits, private groups, test users, and regular storage review.
PeepSo File Uploads FAQ
Can PeepSo File Uploads be used without the core PeepSo plugin?
It does not make sense to treat it as a standalone tool. By design, it is an add-on for the PeepSo community workflow, so the core community layer should already be working first: profiles, the feed, groups, or any other sections you need. If all you need is a file uploader without a social feed, choose another type of plugin.
Which file formats should I allow at the beginning?
Start with the formats your users actually need: images, PDFs, and basic office documents. Allow archives only when there is a clear reason. Executable files, scripts, and uncommon binary formats are usually best kept unavailable to regular members.
Why is a file not uploading even though the size seems correct?
The limit may be enforced not only by the PeepSo setting, but also by PHP, the web server, WordPress, a security plugin, or the hosting environment. Check the maximum upload size in the WordPress Media Library, try a smaller file, and compare the result using a regular user account. If a small file works but a larger one fails, the issue is almost always related to limits or protection layers.
Is it safe to allow file uploads for all registered members?
That depends on the quality of your registration process, your moderation capacity, and the type of community. In a private club with known members, the risk is lower. On an open site with quick registration, it is better to start with limited access, verified users, and a strict format list. This feature never provides absolute safety.
Do I need to disable caching on PeepSo pages?
Not necessarily across the board, but pages with a dynamic feed, posting forms, and file uploads often need exclusions from aggressive caching and minification. If the attachment button disappears or posts refresh unpredictably, temporarily disable optimization for PeepSo pages and test the behavior again.
Can File Uploads be used as a document library?
You can store files inside discussions, but it is not the best choice for a permanent library. If a document needs to stay searchable for a long time, carry versions, use categories, and live in a single organized catalog, use a separate knowledge base or document plugin. PeepSo File Uploads works better for attachments tied to active conversation.
What should I do if the direct file URL opens without login?
First determine whether that behavior matches your site's intended logic. In a public feed, it may be acceptable. In a private group, it usually is not. Review PeepSo privacy settings, the file storage method, server rules, and behavior across users with different levels of access. Do not launch private file-sharing workflows until this issue is clearly understood.
When PeepSo File Uploads Is the Right Choice
PeepSo File Uploads is worth using when files are a natural part of communication inside your PeepSo community. Members discuss assignments, projects, support questions, club materials, or internal documents, and the attachment helps keep the conversation inside the feed instead of pushing it out to email or third-party services. In that kind of workflow, the add-on makes the community more practical: materials stay next to the discussion, moderators can see the context, and members can explain a problem or share a result more easily.
You should not enable the feature as decoration. It requires rules, limits, access checks, clear moderation, and attention to storage. If you are ready to go through those steps, start with a test group, allow only the formats you actually need, verify roles, upload several typical files, and make sure private materials are not visible to the wrong users. After that, you can download PeepSo File Uploads and move on to a careful rollout on your site.
The final decision is simple: if your site is built around PeepSo and members need to exchange materials directly inside discussions, File Uploads solves the right problem. If what you need is a document archive, a public knowledge base, or ticket-based support, a specialized tool is the better choice, while PeepSo should remain focused on communication.

