


MainWP Virusdie - WordPress Plugin
MainWP Virusdie is a plugin for WordPress that provides antivirus and threat detection capabilities specifically designed for the MainWP platform. With this plugin, website administrators can easily protect their WordPress sites from malicious attacks, malware infections, and other security threats.
Plugin Features
This plugin integrates seamlessly with the MainWP platform, allowing users to efficiently manage the security of their WordPress websites from a centralized dashboard. By scanning each site in the plugin network, the plugin enables administrators to detect and remove viruses, malware, and other threats that could potentially harm their websites or compromise sensitive data.
The plugin employs advanced scanning algorithms to thoroughly analyze every file and database on the WordPress sites within the MainWP network. It can identify hidden malware, suspicious activity, and potential vulnerabilities, providing administrators with valuable insights into the security status of their websites.
In addition to virus and malware detection, MainWP Virusdie also offers various security features to enhance the overall protection of WordPress sites. It includes a real-time firewall that effectively blocks known malicious IP addresses and prevents unauthorized access attempts. The plugin also provides a detailed security report for each website, allowing administrators to assess the security level and take appropriate actions if necessary.
This plugin is incredibly user-friendly, making it suitable for both WordPress beginners and experienced users. It offers a simple and intuitive interface, allowing administrators to easily navigate through the various security settings and perform necessary actions to ensure the utmost protection of their websites.
By utilizing MainWP Virusdie, website administrators no longer need to manually scan each site individually. They can efficiently manage the security of their entire WordPress network from one centralized location, saving time and effort. This plugin provides a comprehensive security solution, combining antivirus and threat detection capabilities with additional security features, to safeguard WordPress sites against potential risks.
Overall, MainWP Virusdie is an essential plugin for any website administrator using the MainWP platform. Its advanced scanning algorithms, real-time firewall, and user-friendly interface make it an indispensable tool for effectively protecting WordPress sites from viruses, malware, and other security threats.
Specifications:
| Release date: | 11-10-2020 | |
| Last updated: | 17-08-2022 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Access & Security for MainWP | |
| Compatibility: | W5.x W6.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | MainWP | |
| Rating: | ||
Share with your friends!
A Practical Guide to MainWP Virusdie: Managing Scans and Actions Across a WordPress Network
MainWP Virusdie is best understood not as another security plugin installed on every site, but as a link between the central MainWP dashboard and the Virusdie service. With this setup, it matters not only that a scan is reported, but also where the data came from, when it was updated, which features your plan allows, and which actions should wait until you have a backup. This guide follows that workflow from preparing the dashboard to checking the results again.
The focus is on the day-to-day work of an administrator who manages several WordPress sites. Those sites are already connected to MainWP Dashboard, or will be connected before the extension is enabled. We won't treat a scan result as a final diagnosis or recommend risky file changes. Instead, the goal is to learn how to gather data in one place, distinguish fresh results from stale ones, and respond safely to a potential risk.
The steps follow a practical sequence: preparation and backups, installing the extension on the central dashboard, signing in through the supported flow, adding child sites, setting up scheduled and manual scans, reading statuses, checking communication between systems, and troubleshooting. This approach is especially useful for agencies, freelancers, and site owners who need to keep track of unresolved issues across a network.
Interface labels may change slightly as MainWP or Virusdie is updated. So rather than memorizing the location of every button, focus on a workflow you can verify: first check the connection and data freshness, then limit the scope, record the current state, and only then make a fix or enable an automated action.

How the Extension Fits Into Network Security
The main practical benefit of MainWP Virusdie is centralized monitoring. Instead of opening each client site's admin area to check when it was scanned or look for the same kind of message, the administrator can review Virusdie data in MainWP Dashboard and compare it with other operational signals: site availability, updates, backups, and activity logs. This makes it less likely that a site will slip out of the regular maintenance routine.
The extension doesn't replace MainWP Child, your hosting provider, backups, or WordPress itself. MainWP Dashboard is the control point, child sites remain separate installations, and Virusdie provides the scanning service and, depending on the available features, protection or cleanup actions. If any of these layers cannot exchange data, a green status in one interface is not proof that the entire chain is working properly.
It helps to separate three questions that are often conflated. First: can MainWP communicate with the child site? Second: can the extension reach the Virusdie account and retrieve data? Third: what does the scan result mean, and which actions are justified? A problem with the first question usually points to the MainWP connection; the second may involve authentication or the external API; the third calls for a technical review of the specific site. That's why reinstalling the extension is not a universal fix.
This integration is especially useful for networks with several sites that follow a similar workflow, such as client business sites, small stores, education projects, or content sites. It may also help with a single personal site, but a central dashboard offers less of an advantage in that case. Consider whether you need a separate MainWP Dashboard or whether your existing backup, update, and security routines are enough.
It's important to distinguish monitoring from protection. Monitoring tells you what the service reported and when. Protection includes updating vulnerable components, controlling access, maintaining backups, limiting malicious requests, and having an incident response plan. MainWP Virusdie can be an important part of that process, but it doesn't make a site invulnerable. No alert is not proof that there is no risk, especially if the data is stale or a scan has not started.
A simple team agreement helps: every concerning result gets an owner, a time for the next check, and a record of the actions taken. You can track this in a ticketing system, a maintenance log, or an internal spreadsheet. That makes the extension a source of signals for a repeatable workflow, rather than just a screen of colored statuses. A follow-up check should confirm that the site still works after the fix, not just that the alert disappeared.
Who This Setup Suits, and When to Consider Another Approach
MainWP Virusdie is a good fit for an administrator with a central MainWP Dashboard and several child sites connected through the standard MainWP setup. The administrator wants a single overview, scheduled scan results, notifications, and an initial assessment without opening every site. It's sensible to start with a small group of lower-risk sites. That makes it easier to see how synchronization, service file uploads, and data updates work on your hosting setup.
Agencies may find it useful to have one staff member monitor the network while another reviews site content, restores a backup, or communicates with the client. The extension helps centralize the context: the child site's name, scan status, and update time are available in one place. However, access to the dashboard should be role-based, and saved reports and logs should be redacted before sharing. They may contain domain names and technical details about the infrastructure.
The integration may not be a good fit if your organization already relies on another required security management hub and isn't prepared to maintain a second set of statuses. Don't install MainWP Virusdie just to check a box if no one will review or act on its results. Be cautious if the connection between the dashboard and child sites is unstable, too. Resolve basic MainWP issues first; otherwise, ordinary connection failures may be mistaken for Virusdie alerts.
One limitation concerns how the Virusdie account was created. MainWP materials and support discussions mention an important caveat: an existing account created outside the extension's setup flow may lack the API permissions needed to manage connected sites. Being able to sign in to a separate Virusdie dashboard doesn't guarantee compatibility. Before connecting sites in bulk, check the registration and sign-in flow offered by your current version of the extension.
Don't confuse a scheduled scan with an on-demand scan. MainWP discussions clarify that scheduled scans run automatically on some service plans, while Scan Site may not be available without the corresponding plan. If you see Not available for this site, that does not prove the site is damaged or the installed plugin is broken. First check which scan modes are available to that account.
Finally, the extension is not a substitute for an incident response plan. If a site is already redirecting visitors to malicious pages, losing access to its admin area, changing files in bulk, or sending email, prioritize isolation, preserving evidence, restoring from a verified backup, and working with your host or a qualified specialist. The central dashboard can help you inventory the network, but it shouldn't delay initial incident containment.
What to Check Before Installing and Connecting
Preparation starts before you click Install. Make a short list of the child sites for the first rollout. Include each site's address, owner, project type, whether a recent backup is available, the content contact, and the hosting provider's contact information. This isn't bureaucracy. If the service flags a suspicious file or synchronization fails, you need to know whether you can disable a feature, where to find a backup, and whom to notify.
Check that MainWP Dashboard and the child sites are running compatible, stable versions, and that each selected site already communicates with MainWP properly. There's little point in setting up security monitoring on a site that MainWP can't reach: you won't be able to distinguish an extension problem from a general connection issue. Open the child site's entry, run a routine connection check, and make sure you can access its admin area for manual troubleshooting.
Create or verify backups before running cleanup, bulk updates, or security changes. A completed backup job is not enough; you need to be able to restore a specific site. Know where the backup is stored and how long it is retained. If the process is critical, test a restore on a staging copy. Cleanup should not be your first step if you don't have a clear rollback path. Even a correctly identified malicious fragment may be next to site customizations you need to preserve.
Beforehand, rule out obvious server-side blockers. The site should be available over HTTPS, WordPress should be working properly, outbound connections should be allowed, and the service mechanism should have the required write access wherever it needs to place a file. The server should also have enough resources for normal operation. Don't change limits by guesswork. If a specific message appears later, record it and compare it with the MainWP system report instead of weakening the host's security for a single test.
Pay attention to firewalls and access rules. Virusdie's firewall, security plugins, hosting restrictions, or CDN rules may block requests MainWP needs to manage a child site. The answer isn't to leave protection disabled. First record the central dashboard's IP address and the type of request. Then allow only the required connection, using verified details, and test it. Keep the resulting rule as narrow as possible.
Set a notification policy ahead of time. Choose a working email address or a route into your ticketing system, but don't make someone who is going on vacation the only recipient. An alert without an owner is little better than no alert. Also agree on which events need an immediate response, which belong in a daily review, and who is allowed to enable automatic cleanup or change firewall rules.
Prepare a test procedure. For the first group of sites, record the current result date, request a data refresh, compare the site count, and confirm that statuses change as expected. Don't create a malicious file just to test the system. A safer way to verify the connection is to check the scheduled scan's last-run time, the visible connection status, and the logs for errors.
Installing the Extension on the Central Dashboard and Running a Safe First Check
MainWP Virusdie is installed on the WordPress site running MainWP Dashboard, not as the same standalone plugin on every child site. That setup determines the rest of the workflow: the central dashboard stores the extension's settings and requests data, while child sites are added to MainWP's managed network. Installing the extension on the wrong dashboard will scatter your settings and won't give you centralized oversight.
Before activating it, take a screenshot or make a short note of the current state of MainWP Dashboard: the number of connected sites, whether the test group is available, and the backup status. This helps distinguish a problem caused by enabling the extension from one that was already there. After activation, open the extension's page and don't rush into actions across the whole network. First, find the sign-in, registration, or connection section offered by your installed version.
Use only the sign-in flow provided by the extension. Historically, MainWP has simplified working with keys by retrieving the required data through the API during setup, so manually copying arbitrary keys from old instructions may be useless and make troubleshooting more confusing. Don't paste keys into notes, tickets, chats, or public fields. Treat any temporary code or password displayed by the system as a secret, and complete registration in the same secure flow.
After signing in successfully, don't treat a green message as sufficient proof. It may mean that your credentials were saved, but not that a current API exchange succeeded. Next, use the interface's data refresh action, such as Reload Virusdie Data, and compare the result date and status with what you expect from the scheduled scan. If the interface isn't showing fresh data, don't enable additional features at random before checking the log.
Add child sites in stages. For the first batch, choose a few sites with ordinary hosting and an available backup. Confirm that they remain connected to MainWP, appear in Virusdie, and show the expected status. Only then add the other groups. This gives you a clear boundary: if an error appears after the tenth site, you know where to look for the difference instead of having to investigate dozens of simultaneous changes.
During setup, the service may use a unique service sync file to communicate with a site. Don't delete it just because it looks unfamiliar. If the extension says it couldn't upload the file automatically, check filesystem permissions, hosting restrictions, and the instructions for your plan. Uploading it manually is appropriate only through a documented procedure and after verifying that the file belongs to your account. Never substitute a file from another project.
Finish the initial setup with a short acceptance check: the selected sites appear in the list, data loads without errors, the result date isn't obviously stale, notifications have a recipient, and the team has recorded which account was used. A working connection is confirmed by a fresh data exchange, not just by a saved sign-in form. If any item is missing, stop with the test group and troubleshoot before expanding the rollout.
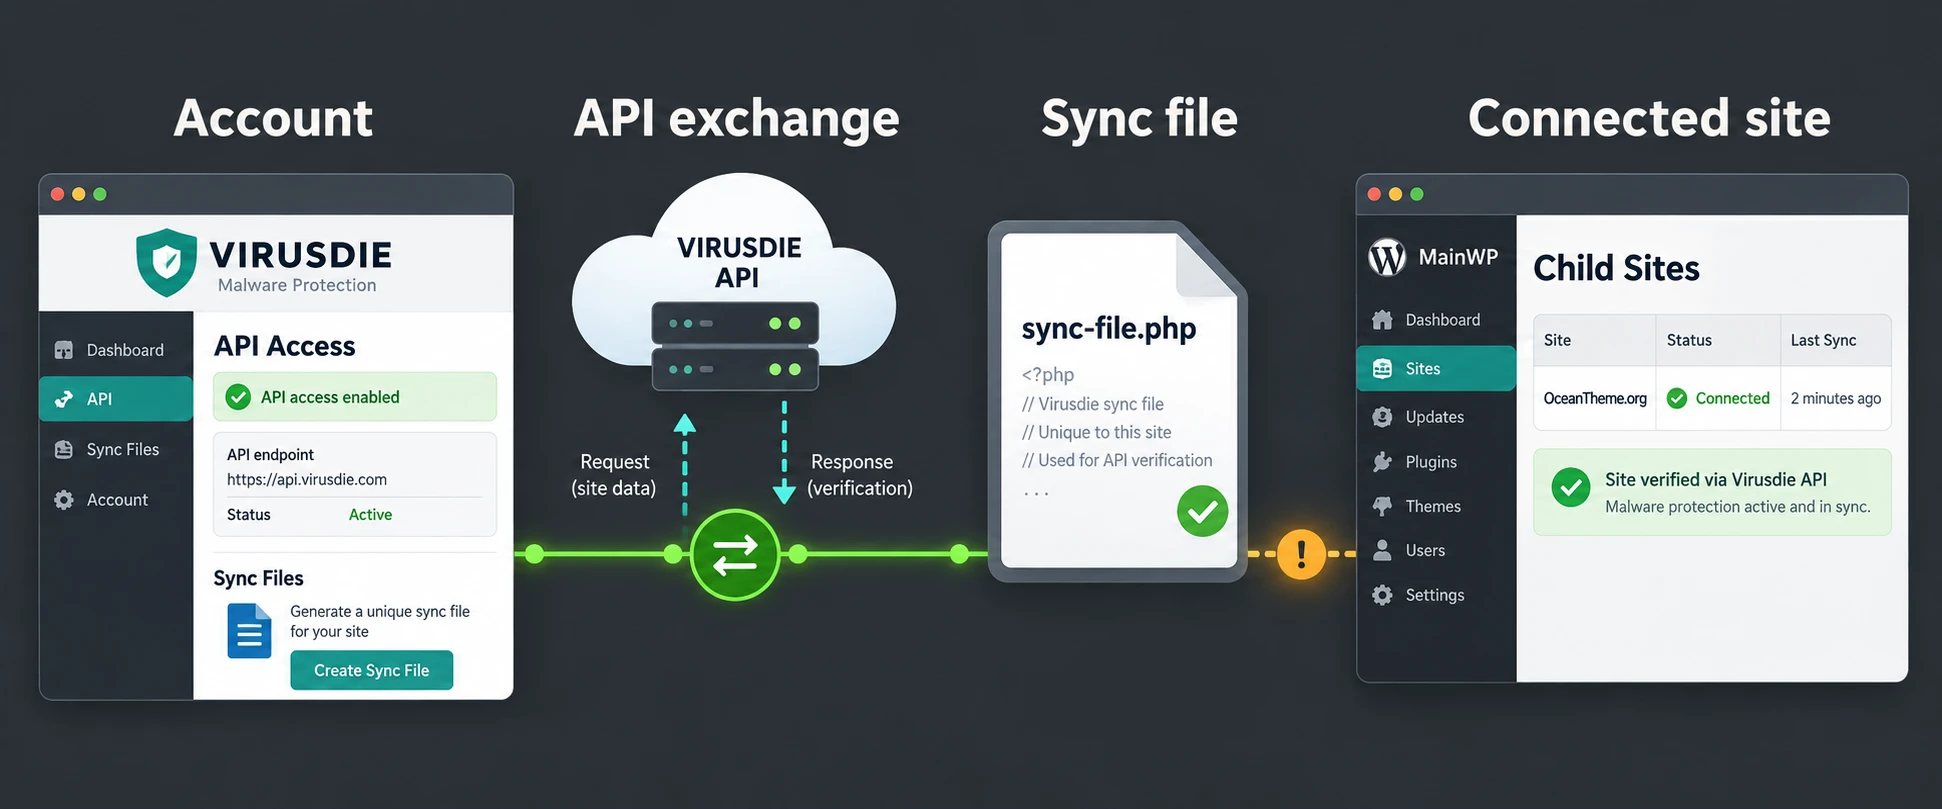
Account, API, and Sync File: Three Common Points of Failure
MainWP Virusdie has three independent states that may all look healthy at a glance: the extension is active, account details are saved, and site data has actually been retrieved. Reliable operation requires all three. If the page shows only saved credentials and the last-scan date isn't changing, treat the integration as unverified until a live request succeeds.
Start with the account. Find out whether it was created through the MainWP Virusdie setup flow or existed beforehand. MainWP Support has received reports of accounts created elsewhere that could sign in but lacked the API permissions needed to manage connected sites through the extension. That doesn't mean you should create several new accounts in a row. First gather the exact error message, the original registration method, and whether the sites are visible in the main account.
Next, distinguish authentication from API availability. If you see a message like Authorization failed - Invalid API key, keep the check focused: did the external service return the error? Does the sign-in flow match what this account supports? Have the permissions or one-time code changed? Don't share a key, a complete log, or client domains in a support request. Give support the time, action, and error code, along with a system report that has been safely prepared if they ask for one.
The third point is the sync file on the child site. Automatic upload saves the administrator manual work, but an upload failure usually points to permissions or server restrictions rather than the scan itself. Check ownership and access to the working directory, hosting restrictions, available disk space, security rules, and whether the site is in maintenance mode. Don't change the ownership of every file or grant broad write access to get past one attempt.
If you need to follow a manual procedure, use only a file obtained from your account for this process. Record which site it was added to, when, and what happened after the next data refresh. Success isn't simply the file being present. It means the exchange is confirmed: the site becomes available in the appropriate list, and its status updates without an upload error. Then make sure the file hasn't ended up in a public repository and that backups aren't exposed to others.
Keep reconnection steps minimal. In one known case, MainWP recommended signing out of the extension's settings and signing in again to get a new one-time code when the old state was interfering with synchronization. This isn't the first response to every failure. It's a careful step to take after recording the error and checking network availability. Before signing out, make sure you know the correct sign-in flow and that someone will still be monitoring the network.
Don't use the extension interface to store secrets. Keys, temporary codes, reports with technical addresses, and diagnostic log screenshots are internal information. Limit access to the central dashboard, secure the MainWP account properly, and follow the principle of least privilege. Security tools often become a source of problems not because of the scanner itself, but because too many people have broad access to a tool that controls multiple sites.
The key takeaway is simple: verify the connection through an observable outcome. After changing the account or sync file, make one controlled request, check the date, site count, and log, then allow time for the scheduled update. Don't repeat the action dozens of times. A series of identical requests clutters the logs and may hide the first useful error.
For each test attempt, record four times: when the request was sent, when the dashboard responded, the timestamp of the last Virusdie result, and when the next scheduled update is expected. This short timeline helps you distinguish processing delays from a real connection failure. For example, if MainWP accepted the action but the log has no record of a request, don't immediately reconnect every child site. Check the central dashboard and account first. If the service responded but only one site's date hasn't changed, look at that site's sync file, permissions, and local security rules.
Keep the record with the incident ticket rather than relying on a staff member's memory. All you need is the site, the action, the time, the visible response, and the next step. If the issue happens again, the record will show whether it followed the same pattern and whether it began after a hosting or security setting changed. It also helps distinguish a normal scheduled scan delay from an API error. For a service that manages a network, this discipline is more useful than pressing the same button repeatedly: the team has a reproducible record of where the exchange stopped.
Setting Up Monitoring: Results, Notifications, and Careful Actions
After connecting the extension, start by choosing a workflow, not by turning on every available toggle. Decide which results you'll review regularly, who receives notifications, and how old the data can be before it needs attention. A small network may need only a daily review and a separate response to concerning alerts. An agency needs a classification system: critical alerts that require an initial response during the same work period, and routine events handled through scheduled maintenance.
When reviewing a result, look beyond the color. Check when the last scan ran, which site the data belongs to, whether it was updated after a manual request, and whether it matches the information in the Virusdie account. If the external service shows a recent scan but MainWP shows an older date, the problem is probably with data transfer, not threat detection. The priority is to restore visibility, not to start a cleanup.
Set up notifications so an email or ticket contains only what someone needs to respond: the site, event type, time, owner, and next step. Don't forward full technical reports to a large group. Prepare a separate, clear message for clients: an alert was detected, the site is being reviewed, a backup is available, and a final decision will follow once the signal is confirmed. This avoids false reassurance and keeps internal details private.
If your Virusdie plan includes firewall management and automatic cleanup, treat them as potentially risky operations. A firewall can block a useful MainWP request, and automatic file changes require a clear rollback path. Enable each feature on a test or well-understood group first. Record the initial status, run one controlled test, and check both the security outcome and the normal operation of the public site.
Automatic cleanup should not replace an investigation. If there are signs of infection, first preserve backups and logs, then determine which files are affected and how critical the site is. If automatic actions are allowed by your organization's policy, check the homepage, admin sign-in, contact form, store checkout, and error log afterward. Any decline in site functionality is a reason to stop further bulk operations and consider rolling back the changes.
Track data freshness separately from alerts. For each site, you need to know not only whether a risk was detected, but also how long ago the system received its last result. A simple rule is to create a task to check the connection if the last-scan date exceeds the agreed limit. This helps avoid treating a calm-looking status from a previous period as evidence of the site's current state.
Don't invent blanket exceptions. If the firewall blocks MainWP, first gather evidence: the central dashboard's IP address, the time, the specific error, the log entry, and a successful retry after a precise allow rule is added. Allowing a broad subnet or leaving protection disabled for convenience creates another risk. After adding a targeted rule, repeat a regular MainWP action and confirm that the block hasn't returned.
It's useful to capture the setup process in a short procedure: check the account, refresh the data, compare its freshness, confirm notification recipients, choose a small test group, enable an additional feature only if needed, and test the public-facing site. The procedure doesn't depend on button locations and helps new staff follow the same careful steps.

How to Read Statuses Without Treating Them as a Final Verdict
A results screen is useful only when the team has agreed on what each status means. Decide in advance how to interpret missing data, an old timestamp, a clean result, a warning, and a connection error. Without a shared understanding, two staff members may respond differently to the same screen: one may assume the site is secure, while another starts an unnecessary cleanup. MainWP Virusdie gives you a reason to investigate; the decision should depend on the site's context and what you've verified.
The first thing to check is the timestamp. The date of the latest available scan answers, "What period does this data cover?" It doesn't answer, "Is the site safe?" If the timestamp is old, even a clean status should be marked as a visibility issue that needs attention. If the data is fresh but a risk has appeared, take the signal seriously, then check which asset is affected and whether the event relates to an action already completed.
The second thing to check is the scope. Find out whether the result applies to one child site, a selected group, or the entire network. The same error across all sites more often points to a central cause: the API, authentication, dashboard settings, or the external service. One site dropping out is more likely to require a closer look at its hosting, permissions, MainWP connection, security settings, and recent changes. This distinction saves time and avoids network-wide actions when one local fix is needed.
The third thing to check is what action should follow. Stale data calls for restoring synchronization. A clear alert calls for preserving a backup, qualifying the finding, and checking its impact. A confirmed authentication error calls for careful access troubleshooting. An unavailable manual scan calls for checking which service mode is available. Add this interpretation to the internal event record so a new staff member can see the next safe step, not just the color.
Don't build reports around the number of green indicators. A more useful measure of maintenance is the share of sites with a current result, the number of open alerts with an assigned owner, and the number of sites where normal operation has been confirmed after an intervention. This reflects the quality of the process, not just how reassuring the dashboard looks. It can also show when the network is growing faster than the team's ability to review incoming signals.
If a result seems contradictory, use cautious wording: "needs review," rather than "the site is infected" or "the site is fully protected." This matters when communicating with a client. A confident claim without an investigation can cause unnecessary alarm or create a false sense of security. MainWP Virusdie helps gather initial context; a final assessment should be based on verified data and a check of the impact on the site.
Coordinating Security Checks With Updates, Backups, and Access Controls
It's best to plan MainWP Virusdie as part of your regular WordPress maintenance cycle. Updates to WordPress core, themes, and plugins reduce risk, but they can also change how a site behaves. Backups give you a way to roll back, but don't explain what caused an incident. Virusdie adds monitoring for the service's results, but it doesn't replace any of these other measures. A strong workflow puts them in the right order instead of running everything at once without keeping a log.
A practical sequence before a significant update is to check that the child site is available in MainWP, confirm that a recent backup exists, save notes on its current state, update a small group first, and then test key user journeys. Virusdie data adds useful context along the way. If the status or connection changes after the update, you know when it happened and can compare the timing with the maintenance log.
Backups serve two different purposes. An operational backup lets you roll back quickly if a change breaks the site. An investigative backup may be needed to preserve the pre-cleanup state and find out what happened. Don't mix them up or replace your only good backup with a new one after an incident. First confirm that the saved restore point is available, has a clear timestamp, and won't be overwritten automatically.
Pay close attention to access. The central MainWP dashboard can affect many sites, so a role that can view scan results may not need permission to change security rules or run cleanup. At a minimum, separate viewing, preparing an action, and approving a risky change. Even a small team can do this operationally: one person records the alert, another confirms the backup, and the person in charge decides whether to intervene.
Don't store one-time codes or technical keys in client tickets, page comments, or shared spreadsheets without access controls. When handing off an incident, include safe context: the site, time, exact error message, action taken, backup status, and a reference to the restricted location where service data is stored. That's enough to continue the work without exposing secrets to everyone in the conversation.
If a site uses a caching plugin, CDN, or server cache, add them to the post-change checklist. Caching doesn't cause a Virusdie API error by itself, but it can make someone see an old public page after files or settings have been restored. Clear only the relevant cache layer, then repeat the affected user journey. Purging every cache across a large network creates load and makes it harder to find the cause.
For stores and sites with forms, define a short test checklist for after any security action: the homepage, sign-in, a safe test form submission, the cart, and checkout without a real payment if applicable. This isn't a claim that Virusdie affects all of these areas. It's a way to catch a different kind of problem: a technical fix may accidentally break an important user journey, and the team should notice before closing the ticket.
Practical Guidelines for Agencies and Multi-Site Owners
One of the most common organizational mistakes in a multi-site network is treating every project the same way. A landing page with infrequent updates, an online store, a site with user accounts, and a staging site each need a different response time. Create or maintain clear priority groups in MainWP. Then when you work with MainWP Virusdie, you see more than a list of domains: you know which sites need an immediate freshness check and which can wait for scheduled maintenance.
Assign an owner and a backup contact to every site. The owner doesn't need to fix every technical issue, but they should receive the alert, confirm that a backup exists, and pass the task to the right specialist. The "owner" field is especially useful when notifications arrive overnight or during a migration. Without it, messages sit in a shared inbox and it's hard to reconstruct the decisions later.
In your weekly routine, separate read-only checks from changes. Read-only work includes refreshing data, comparing timestamps, checking the site list, and reviewing a safely prepared log. Changes include signing in again, placing a service file, changing firewall rules, removing a site from the account, and running automatic cleanup. The first group can be handled regularly. The second should have a reason, a restore point, and a follow-up check.
A small escalation matrix can help. An error affecting one child site goes first to that site's administrator. An authentication or data freshness problem across the network goes to the owner of the central dashboard. A signal that suggests active malicious activity goes to a security specialist and the hosting provider through the incident channel. This doesn't require a complex system; it prevents everyone from waiting for someone else to resolve the issue.
Agree on how to write notes. Instead of "fixed Virusdie," write something like: "Reauthenticated the extension, data refresh succeeded, result timestamp changed, homepage and form checked." Instead of "everything looks fine," say which test passed. Specific notes make the next maintenance cycle easier and help distinguish a recurring failure from a new one. They also make client reports clearer and easier to verify.
Add MainWP Virusdie to the onboarding checklist for new sites only after the basic MainWP connection is working. First, the dashboard should be able to see the site, access should be transferred securely, a backup should be available, and an owner should be recorded. Then connect the Virusdie integration and complete the data refresh check. This sequence doesn't guarantee that a site has no threats, but it prevents a chaotic setup where new sites appear in the network dashboard without a clear security workflow.
Improvements You Can Make Without Code or WordPress Core Changes
MainWP Virusdie doesn't require PHP snippets, WordPress core file changes, or unverified database settings. The most useful improvements here are organizational and reversible: an incident note template, a list of critical user journeys, an assigned notification recipient, and a short data freshness check. These help the team respond to scan results without changing WordPress or creating a new failure point after an extension update.
Create a template in your work tracking system with five fields: site, time and source of the alert, status of the latest backup, safe action taken, and result of the follow-up check. Use it for an API error, a failed sync file upload, or a concerning scan result. It doesn't replace the details of an investigation, but it preserves the minimum information needed to hand the task safely to another staff member.
Another safe improvement is to set up a small test group in MainWP and try new rules there before applying them more broadly. If a new sign-in, firewall rule, or available Virusdie feature changes how the system behaves, you'll have a limited group to monitor. If it fails, you can roll back one clear change across a few sites instead of sorting through dozens of different configurations. This follows the usual practice of introducing changes gradually; it doesn't depend on an invented extension feature.
Rolling back these improvements is straightforward: remove the temporary note, restore the previous narrow access rule, or remove a site from the test group once monitoring is complete. Don't respond to a failure by deleting the extension, disabling all security tools, or editing plugin files directly. First record the symptom and log, then return to the last controlled state. This keeps each change clear, repeatable, and safe through future updates.
Example: Weekly Checks Across a Client Site Network
Consider a realistic workflow for an administrator who maintains twelve client WordPress sites. The goal is to know during each work cycle which sites have a current Virusdie result, which need follow-up, and which changes can be safely closed out. This doesn't assume that every alert means a site has been compromised. It creates a repeatable route from the site list to confirmation that the sites are working normally.
Prepare the Site List and Record the Starting Point
First, the administrator opens MainWP Dashboard and filters the list to show only child sites included in this workflow. For each one, they check the MainWP connection and the latest backup. Then they record the current date of the Virusdie data and flag any sites where the date already looks old. Temporary staging sites and projects handled by another contractor should not be mixed in with this group. A clearly defined scope makes the final report more useful.
Next, they check whether any work before the current review could have affected the connection: a migration, hosting change, DNS update, new firewall, or replacement of a security plugin. If so, the site gets a higher-priority flag. That doesn't mean the site is necessarily unsafe; it means its old sync connection may have stopped working without affecting the rest of the network.
Refresh Data Without Taking Network-Wide Actions
From the central dashboard, the administrator runs the available data refresh once and waits for a response. They don't click the button again until the first request has finished. Then they compare the new timestamps with the ones they recorded earlier. If most sites have updated but one still shows an old date, that's a local issue. If no sites have updated, the account, external API, or central dashboard is the more likely place to look.
For each exception, record four things: the site, the visible symptom, the last known good state, and the next safe step. For example: "Data hasn't changed after refresh; site is available in MainWP; check the Virusdie log and authentication." This is more useful than "doesn't work" because the next person doesn't have to start troubleshooting from scratch. It also avoids including keys, passwords, or unnecessary client details.
Respond to a Detected Risk
Suppose one site gets a concerning scan result. The administrator first confirms that the data is current and that the site is within their area of responsibility. Next, they create a backup or confirm that a recent, verified backup is available, limit content changes if needed to preserve evidence, and notify the owner through the agreed channel. One alert is not a reason to start bulk updates and cleanup across all twelve sites.
The next step is to identify what information the service provides: a general status, a file, an event type, or a request for further review. If automatic cleanup is available and allowed by policy, use it only after creating a restore point and only on that one site. If the feature isn't available or the context is unclear, escalation to a security specialist or hosting provider is safer than guessing. The goal is to avoid erasing evidence or turning a local incident into a network-wide problem.
After taking action, run a functional check. For a typical site, check the homepage, several internal pages, search, a form, and admin sign-in. For a store, add the cart, a test checkout without real payment, email, and the customer account if available. For a site with integrations, test webhooks or connected forms in a test environment. The outcome is acceptable only if the site is technically available and its key user journey works.
Close the Issue and Check Again
After addressing the cause, the administrator refreshes the Virusdie data and records the new timestamp. If the site works for users but MainWP still shows the old data, the ticket shouldn't be closed yet; synchronization may be delayed or the API may have another error. If the data has changed but the site has stopped accepting submissions, that isn't a successful outcome either. You need both kinds of evidence: an updated security status and normal site operation.
At the end of the review, prepare a brief report: how many sites received fresh data, how many needed a connection check, what actions were taken, and what remains open. Give the client a clear status without technical secrets. Keep the detailed internal record, with timestamps, logs, and decisions, in a restricted location. This habit makes MainWP Virusdie part of regular maintenance rather than a dashboard people open only after a serious problem.
It's useful to end the review by checking exceptions, not just counting completed sites. The administrator opens the list of sites whose date hasn't changed, whose MainWP connection is down, or whose result still has no owner, then assigns one next step to each. One site might need a hosting log review, a group may need an authentication check, and a concerning scan result may need a backup confirmed and a specialist notified. Every exception should have a due date and a condition for closure: a new data timestamp, a successful child-site connection, or a verified user journey. That way, an open issue doesn't turn into a permanent spreadsheet note or disappear from the next review just because the other sites look fine.
If authentication changed, a sync file was placed, or a firewall rule was adjusted during the cycle, record a minimal verification sequence after the review. For example: the data refresh ran once, the expected response appeared in the log, the relevant site remained available in MainWP, and the homepage and form loaded. This doesn't duplicate the technical log; it records the evidence behind the decision. If the status goes stale again next week, the team can compare the new failure with the last controlled state instead of changing settings blindly. In the client report, it's enough to say that the connection was checked and list the actions still in progress. Don't publish domains, keys, or internal messages.

How to Confirm the Setup Works, Not Just Looks Complete
Checking MainWP Virusdie's operation should include at least three observations. First, the extension receives current information from Virusdie. Second, the expected child sites are present and remain connected to MainWP. Third, the site's normal admin and public-facing features still work after a security rule change, cleanup, or reauthentication. If even one of these is missing, it's too early to conclude that everything is working properly.
Start with the timestamps. Compare the date or time of the last scan before and after a controlled refresh. Don't expect an immediate change if the service runs on a schedule, but make sure the data isn't staying stale indefinitely. Then compare the number of managed sites with the inventory for your test group. No results, a site that unexpectedly disappeared, or an unavailable status calls for a connection and permissions check, not an assumption that the network is clean.
Next, test the notification route. A harmless organizational check is best: confirm that the assigned recipient receives a normal notification or ticket instead of generating an artificial threat. Document where staff confirm receipt, how they escalate an event, and what to do if the recipient is unavailable. A system that detects events well but silently loses notifications leaves the response process incomplete.
After changing firewall settings, run the MainWP action that was blocked and confirm that the rule allows exactly the required connection. At the same time, check that the public-facing site responds as expected. If the connection works only when protection is completely disabled, the job isn't finished. Replace the temporary broad exception with a targeted rule, document why it's needed, and remove the wider allowance.
When files are changed, don't check only the results page. Review the server and WordPress error logs, test critical forms and user journeys, and clear only the cache layers that might be serving an old page. Don't clear all caches or update every component automatically just because those actions appear on a familiar checklist. Each action should relate to an observed symptom.
A useful final note is specific: "Site data refreshed and timestamp changed; central dashboard can see the site; homepage, sign-in, and form work; no new connection-related log messages." "Everything is green" is not enough. Another staff member should be able to reproduce the check without guessing what the previous person tested.
For larger networks, consider a follow-up check the next day or during the next scheduled cycle. It's not needed for every harmless change, but it can be valuable after restoring authentication, fixing a sync file, or adjusting a firewall exception. If the status goes stale again, you'll have a precise timeline and a clear record to provide to support.

Troubleshooting Common Issues Without Risky Shortcuts
The steps below are a way to isolate problems, not universal fixes. They help distinguish authentication issues from child-site connection problems, scan plan limitations, and firewall behavior. Before making a change, record the symptom, time, affected site, and last successful action. This reduces the risk of removing a useful setting while trying to fix an unrelated problem.
Virusdie Data Doesn't Update After a Refresh
Symptom: the result date stays the same, or a message says the API connection failed. Likely cause: saved credentials don't confirm current access, the external service rejected the key, or the request never reached it. Check: confirm that the main account has the expected results. Then enable the Virusdie log in MainWP through Info and Custom Event Monitor, and capture one data refresh event. Fix: follow the exact error message and use the supported sign-in flow again if there's a clear reason to do so. Rollback: don't delete all settings or change keys manually before saving a safely prepared report.
A Green Message Appears, but the Latest Results Are Old
Symptom: the interface confirms that data was saved, but scans in the main account are newer. Likely cause: the credentials were saved, but the live request or later synchronization failed. Check: compare the timestamps in both places, then run Reload Virusdie Data once. Fix: review the log entry, API status, and exact service response. Rollback: don't enable cleanup or a firewall as a way to "refresh" data; those are separate system layers.
The Unique Sync File Wasn't Uploaded When Adding a Site
Symptom: the extension says it couldn't place the service file automatically. Likely cause: insufficient directory permissions, a hosting restriction, maintenance mode, a conflicting security rule, or a filesystem quirk. Check: confirm that the site is still connected to MainWP and identify the specific server restriction. Fix: restore the minimum required permissions or use the documented manual procedure with a file from your own account. Rollback: after testing, return temporary permissions to the normal policy, and don't leave the directory writable by everyone.
Scan Site Says the Site Is Unavailable for Scanning
Symptom: a manual scan returns Not available for this site, although the site is listed. Likely cause: manual scans may not be included in the current plan, while scheduled scans may run automatically. Check: distinguish the last scheduled result from on-demand scan access, and check which mode is available to the account. Fix: wait for the scheduled update or use the permitted service plan upgrade path through official support. Rollback: don't create new accounts or reinstall the site because of a single plan-related message.
MainWP Can't Manage a Child Site After Protection Is Enabled
Symptom: the child-site connection drops, although the public site may still be available. Likely cause: a firewall is blocking requests from the central dashboard. Check: compare the time of the failure with the firewall log and identify the specific IP address or rule. Fix: add a narrow allow rule for the verified connection and retry one MainWP action. Rollback: remove any temporary broad exception used during troubleshooting; don't leave protection disabled.
A Site Disappears From the List or Doesn't Get the Expected Status
Symptom: a site is visible in MainWP but doesn't appear as expected in Virusdie, or shows an old status. Likely cause: an incompatible account setup, incomplete registration, a missing service file, or a delay in data exchange. Check: start with one site and find the step where the MainWP list, main account, and extension results stop matching. Fix: use the setup flow provided for the account and share only safely redacted information with support. Rollback: don't remove a working child site from MainWP without a separate reason.
If an error affects many sites at once, check the central dashboard, authentication, and API response first. If it affects one site, start with its connection, permissions, and security rules. This distinction saves time and reduces the need for risky network-wide actions.

Common Questions About MainWP Virusdie
Do I need to install the extension on every child site?
No. MainWP Virusdie is designed for the central WordPress installation running MainWP Dashboard. The child sites should already be connected to MainWP. The integration and its service mechanism handle communication with Virusdie. Service-related files may be added on the child sites, but don't distribute the extension's ZIP file across them as if it were a standalone plugin.
Why doesn't saved authentication prove that results are updating?
Saved credentials confirm only one step. A live API request may fail, or scheduled synchronization may stop later. After signing in, check the observable outcome: data refresh, last-scan date, site list, and any log entry if an error occurs. That's why a green indicator with stale data still needs investigation.
Can I scan any site manually at any time?
Not always. MainWP materials distinguish the manual Scan Site action from automatic scheduled scanning, and access may depend on the Virusdie plan. If a manual scan is unavailable, first check which features the account includes. Don't treat that message as automatic proof that the site is infected or broken.
What should I do if an older Virusdie account won't add sites through MainWP?
Check how the account was created. Some accounts created outside the extension have been reported to have API limitations, so signing in may not be enough. Gather the minimum safe details: registration method, exact error message, time, and site status. Then follow the documented support process without sharing keys, one-time codes, or a full system report.
Should I enable automatic cleanup right away?
Only if your plan includes it, your internal policy allows it, and you have a verified backup to restore. Test the process on a controlled site first, record the initial state, and check important user journeys afterward. If the result is unclear, stop and investigate rather than making file changes across the network.
How can I tell whether the firewall is blocking MainWP?
Look for a timing match: the central dashboard stopped connecting to a child site after a rule was enabled, and the firewall log shows a denial for the relevant request. The fix should be targeted: allow the verified IP address or connection and retry one action. Leaving protection disabled or allowing a broad subnet is not a normal long-term setup.
Does MainWP Virusdie replace backups and updates?
No. The integration helps you monitor Virusdie results and take action from the central dashboard, but it doesn't replace backups, WordPress, theme and plugin updates, access controls, or log reviews. A mature workflow combines these measures: a backup gives you a way to roll back, updates reduce known risks, and scan results help you decide where further review is needed.
When MainWP Virusdie Is a Good Fit
Use MainWP Virusdie if you already manage a WordPress network through MainWP and want to include Virusdie data in a clear maintenance workflow: check the connection and data freshness, send a notification, take a safe action, and verify the result. The biggest benefit comes from disciplined use, not from the number of enabled toggles: start with a small test group, verify your backups, assign an owner, and confirm that each site works after a significant change.
Start with a few predictable sites, distinguish authentication from a live data exchange, and troubleshoot alerts based on where the connection failed. To install the extension on your central dashboard and test it, you can download MainWP Virusdie, then complete the acceptance checks on a limited group instead of enabling the extension across the entire network at once.
The most important rule is simple: security depends on verified actions, not the color of a status. When the team knows how to check data freshness, preserve evidence, avoid weakening protection during troubleshooting, and confirm that a site has recovered, the central integration can save time and make it less likely that a problem will be missed.

