


CodeCanyon WordPress GDPR - WordPress Plugin
The plugin is a comprehensive solution for enhancing the security aspects of a WordPress website. With its robust features and functionality, it offers protection and compliance with GDPR regulations, ensuring a safe digital environment for users. Upon installation, admins can configure settings to manage data privacy, cookie consent, data access requests, and more, making it a vital tool for websites that prioritize user data protection.
Plugin Features
Its user-friendly interface simplifies the process of aligning a WordPress site with the necessary security protocols and privacy standards. The plugins customizable options allow administrators to tailor settings to their specific requirements, enabling them to seamlessly integrate security measures without compromising user experience. By streamlining GDPR compliance procedures, it equips website owners with the tools to safeguard sensitive information effectively.
With regular updates and ongoing support, the plugin stays up-to-date with the latest security trends and regulatory changes, ensuring continued protection for WordPress sites. Its compatibility with various WordPress themes and plugins makes it a versatile choice for different website setups, offering flexibility and scalability to adapt to evolving security needs. By addressing critical security concerns proactively, it helps fortify websites against potential vulnerabilities and data breaches, enhancing overall cybersecurity posture.
Furthermore, CodeCanyon WordPress GDPR documentation provides clear guidance on implementation and usage, enabling users to navigate its features with ease. Its intuitive controls and systematic approach to compliance empower website owners to handle data protection responsibilities efficiently, minimizing the risk of non-compliance and associated penalties. By promoting transparency and accountability, it fosters trust between website operators and users, establishing a secure digital ecosystem for all stakeholders involved.
Specifications:
| Release date: | 09-05-2018 | |
| Last updated: | 30-12-2024 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Access & Security | |
| Compatibility: | W5.x W6.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | CodeCanyon | |
| Rating: | ||
Share with your friends!
Guide to Setting Up CodeCanyon WordPress GDPR on a WordPress Site
CodeCanyon WordPress GDPR is a premium WordPress plugin that helps you assemble a workable set of GDPR tools on your site: a cookie consent popup, a Privacy Center, pages and shortcodes for user requests, service management, and basic notices. This guide does not repeat the product listing. Instead, it shows how to approach setup so visitors understand exactly what they are agreeing to, and administrators can verify the result without guesswork.
The legal side of data protection depends on the country, target audience, service stack, and the wording of your privacy policy. Because of that, this plugin should be treated as a technical layer for displaying consents, requests, and data management interfaces, not as an automatic guarantee of legal compliance. No WordPress plugin can replace a cookie audit, service agreements, accurate policy text, and an internal process for handling requests.
Below, we cover pre-installation preparation, initial setup, the core cookie popup and Privacy Center settings, working with GDPR Services, shortcodes, WooCommerce, and forms, a real-world configuration example, result verification, troubleshooting common issues, comparable solutions, and the questions you should settle before publishing the changes.

What Problem the Plugin Solves and Where It Is Actually Useful
This plugin is useful for sites where the administrator wants to give visitors a clear interface for consenting to data processing, viewing policies, requesting access to their data, requesting deletion, and managing cookie-based services. In practice, this matters most for commercial websites, projects with contact forms, blogs using analytics, WooCommerce stores, agency websites, and content-driven sites that rely on third-party scripts.
The main value of CodeCanyon WordPress GDPR is not a single cookie banner, but the combination of several connected elements. The site owner gets a cookie popup, a separate Privacy Center, a set of pages and shortcodes, service settings, the ability to connect plugins and external tools, and checkpoints for handling user requests. If you only use the banner and never configure services, pages, and text, most of the value is lost.
The plugin is a good fit when you need to build a manageable privacy interface in WordPress quickly, without developing a separate solution. It can be especially useful for sites that already have standard policy pages but are missing interactive user requests and structured consent management.
It may not be the right fit if your project needs advanced enterprise-grade consent management with geotargeting, multiple legal regions, a centralized cookie scanner, automatic legal document generation, and a separate audit system. In that case, it makes more sense to evaluate dedicated consent platforms or legal services and use a WordPress plugin only as one layer in the stack.
Practical takeaway: before installation, decide what visitors actually need to see: only a cookie popup, a full Privacy Center, data request forms, service controls, or the complete set. That decision affects your page structure, copy, the modules you enable, and how you test everything afterward.
What to Check Before Installation and Why It Affects the Outcome
Preparing for a GDPR plugin is different from preparing for a typical visual add-on. Mistakes often do not show up right away: the page opens, the popup appears, but some scripts have already loaded before consent, the request form does not send email, the Privacy Center leads to empty pages, or users do not understand what data they are requesting. That is why the first step should be an inventory.
List of Services and Cookies
Make a list of what is actually running on the site: analytics, ad pixels, maps, video, chat, forms, comments, WooCommerce, anti-spam, payment services, and embedded social widgets. For each service, note why it is needed, which cookies or local data it may create, and whether its loading can be delayed until consent is given.
The plugin supports GDPR Services and integration with a cookie whitelist. That is only useful if your service list is prepared in advance. If the administrator enables everything at random, visitors may see a polished interface while the real script-loading logic remains unverified.
Privacy Pages and Policy Text
Check whether the site already has a privacy policy page, a cookie policy page, a contact method for requests, a clear description of the data controller, and information about third-party services. The plugin can help display links and requests, but it should not be expected to invent legal text on behalf of the site owner.
WordPress also includes built-in tools for exporting and erasing personal data. Keep those in mind when planning your process: the plugin can provide a convenient request path for visitors, but the administrator still needs to understand where that request will be processed and how it will be completed.
Theme, Caching, and Script Optimization
The cookie popup and third-party service blocking depend on how your theme and optimization tools output scripts. If the site uses caching, JavaScript bundling, deferred loading, or minification, some scripts may run before the banner appears or stop responding correctly to user choices. Before configuring anything, create a test page and temporarily simplify optimization so you can understand the plugin's baseline behavior without cache-related side effects.
Administrator Permissions and a Rollback Plan
It is best to configure the plugin under an administrator account with access to pages, plugins, theme settings, and caching tools. Before enabling third-party script blocking, create a backup or at least document the original settings. If the popup starts hiding critical elements, you need a fast rollback path: disable the questionable module, clear the cache, and retest the site in a private browsing window.
Installation, Initial Activation, and a Basic Check
Installation works like any standard WordPress plugin: upload the ZIP archive through the Plugins section, then activate it with the Activate button. After activation, do not enable every feature immediately. A better approach is to run a quick baseline test: make sure the admin panel shows no critical errors, the plugin settings are available, and the public-facing site opens without a visual break.
Next, check whether the pages or shortcodes the plugin provides for the Privacy Center, cookie popup, user data, and requests are now available. If your version supports automatic page creation, use that as a starting point, but make sure to rewrite the content to fit your site. If the pages must be created manually, choose clear URLs and page titles ahead of time.
Minimum First-Run Sequence
- Upload the plugin ZIP file through
Pluginsand activate it. - Open the plugin settings and review which modules are enabled by default.
- Create or assign the policy, cookie policy, and Privacy Center pages.
- Enable the cookie popup in a minimal mode without advanced script blocking.
- Open the site in a private browsing window and verify that the banner appears without layout issues.
- Save a visitor choice, refresh the page, and make sure the state does not reset for no reason.
If the basic popup already breaks the layout, do not move on to service configuration yet. First, check for conflicts with the theme, cache, and optimization tools. GDPR settings are best built in layers: first the interface, then the pages, then the services, and only after that the user request checks.
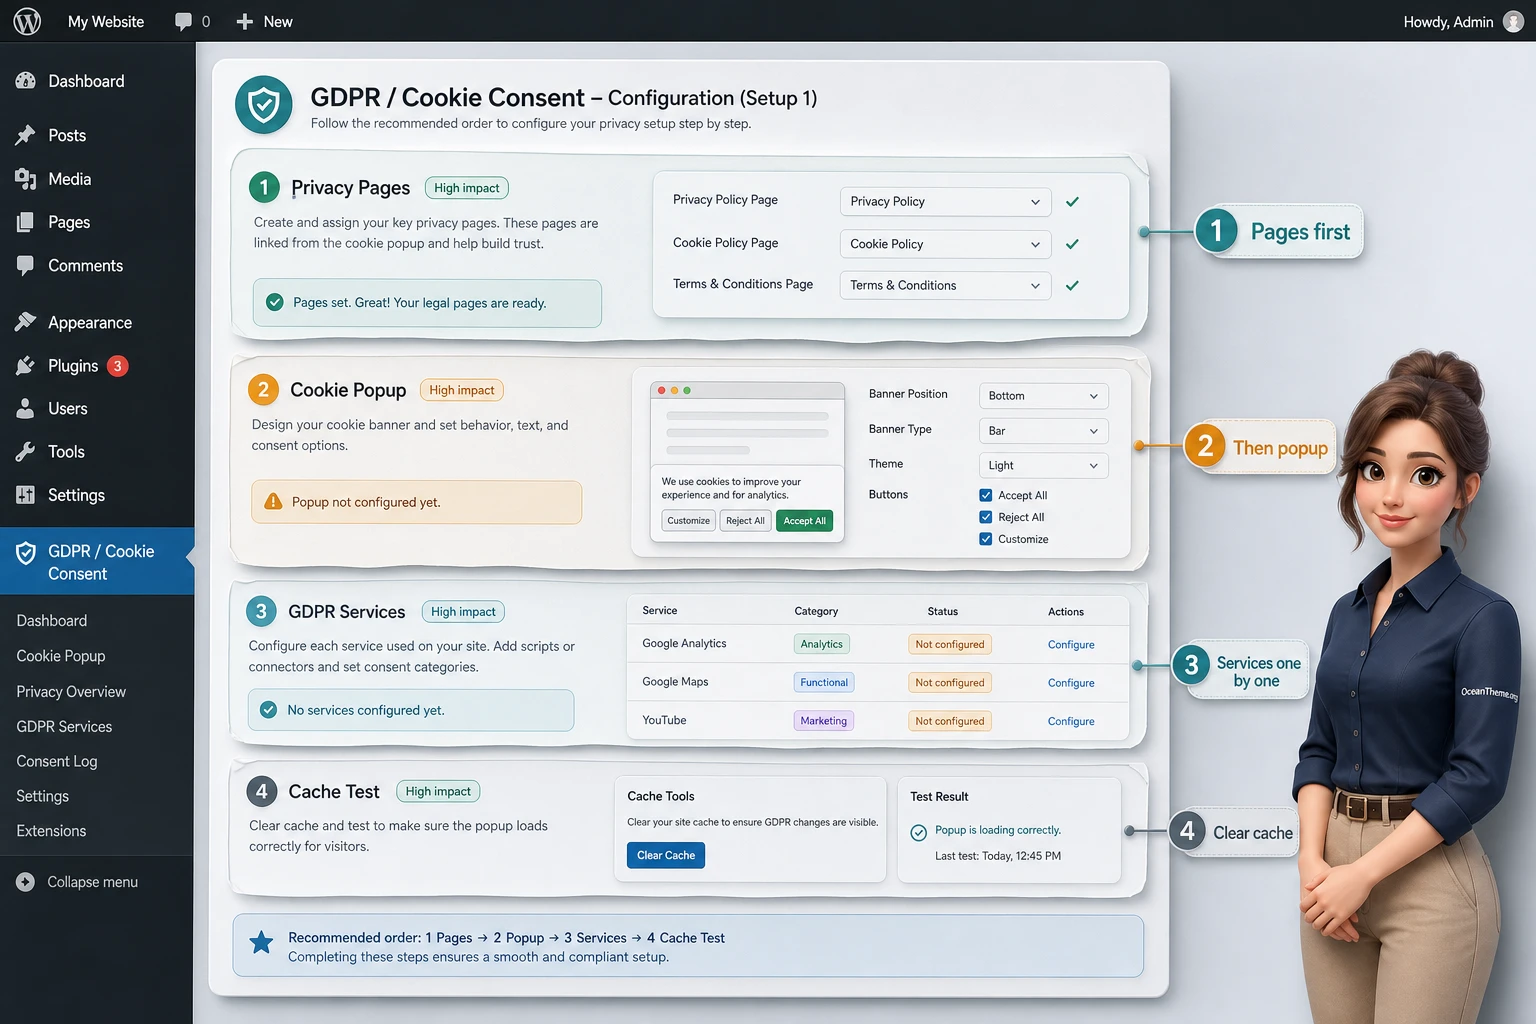
Configuring the Cookie Popup Without Conflicts with the Theme or Cache
The cookie popup is the most visible part of the plugin, but it is also the part most often configured too superficially. Users need a clear choice, and site owners need behavior they can actually verify. What matters here is not just the text and button color, but the relationship between the popup and real services, display timing, reopening settings, and consent storage logic.
Text and Buttons
Start with concise text that explains the purpose of cookies without legal overload. Do not try to fit the entire policy into the banner. A short explanation, a link to a detailed page, and clear action buttons work better. If the plugin supports multiple consent states, button labels should match the action: accept, reject, customize, save choices.
For a Russian-language site, make sure the user-facing text is translated in the settings or through the standard localization workflow. Do not leave half the interface in English if the whole page is meant for a Russian-speaking audience. The only exception is technical admin labels that only the site administrator sees.
Positioning and Visual Compatibility
The popup should not cover the cart, chat button, mobile menu, or WooCommerce system notices. If your theme has a fixed bottom bar, choose a banner position that does not conflict with it. After changing the position, always test the site on the homepage, a product page, a contact form, and an article with embedded video.
It is best to handle visual styling through the plugin's own settings. If those are not enough, you can add a small CSS adjustment through Appearance or a child theme. Do not invent class names unless you have confirmed the plugin's actual CSS structure. The safest option is to use only your theme's general styles for policy containers or add CSS only after checking the real classes in the browser.
When to Enable Service Blocking
Service blocking is useful when external scripts should load only after consent is given. But this setting is sensitive to caching and optimization. Enable it one service at a time: analytics first, then video, then ad pixels, then additional widgets. After each step, clear the cache and retest the site in a fresh private browsing window.
Result check: before consent, the external service should not be actively running; after consent, the page should display the expected element or send the expected event. If nothing changes, the service configuration, cache, or script loading order needs separate diagnosis.
Privacy Center, Request Pages, and Shortcodes
The Privacy Center should be the place where visitors find clear actions: read the policy, request access to data, ask for deletion, update consents, or go to cookie management. A strong Privacy Center does not look like a pile of random links. It explains what will happen after each action and what information the user may need to confirm.
Which Pages to Create
For a typical site, a few pages are enough: a privacy policy, a cookie policy, a Privacy Center, a data request form, and a consent management page. If the plugin uses shortcodes, place them on dedicated pages with clear context before and after the shortcode block. Users should not see only a form with no explanation of why it exists.
Shortcodes are convenient because they let you place a functional block exactly where you need it. But they also come with a risk: if the page is hidden, accidentally deleted, or cached with outdated output, the user journey breaks. After publishing, add links to the Privacy Center in the site footer, on the policy page, and in the account menu if appropriate.
How to Connect the Pages
Create one main path. For example: the cookie popup links to the cookie policy and the Privacy Center; the Privacy Center links to data access requests, deletion requests, and consent management; the privacy policy links back to the Privacy Center. That way, users do not get lost, and administrators know exactly where to test each part.

GDPR Services: How to Describe Third-Party Services Without Losing Control
In this context, it makes sense to treat every external tool that affects visitor privacy as a service: analytics, advertising, maps, video, chat, forms, anti-spam, and embedded widgets. If the plugin lets you define GDPR Services, do not fill them with vague generic language. Users should understand the service category, its purpose, and what their choice changes.
The services section matters most on sites with marketing scripts. Without it, the cookie popup becomes a formality: the visitor clicks a button but never sees which systems are behind that choice. A clear service map helps both the administrator and the site editor understand which scripts are connected and what should be verified after consent is given.
Useful Service Structure
| Parameter | Why It Matters | How to Verify It |
|---|---|---|
| Category | Helps distinguish essential, analytics, marketing, and functional services. | Compare the list against the cookie policy and the page's actual scripts. |
| Description | Explains to the user what the service does and why it asks for consent. | Open the popup as a visitor and check whether the action is clear without admin context. |
| Consent dependency | Shows whether the service should load immediately or only after a choice is made. | Test the page before consent, after consent, and after the choice is withdrawn. |
| Script source | Needed for troubleshooting if a service does not block or does not start correctly. | Review network requests and confirm that the domain matches the service. |
If a specific service is critical to how the site works, do not mark it as optional without testing. For example, form anti-spam, a payment gateway, or a cart system script may break the user journey if it is delayed until consent. For those elements, first clarify the role of the service, then decide how it should be described in the interface.
Integrations with Forms, WooCommerce, and User Accounts
CodeCanyon WordPress GDPR is positioned as a plugin that works with more than just a cookie banner. In a real project, the most important touchpoints are forms, the store, comments, the user account, and email. That is where users actually leave personal data, so the setup needs to be specific and deliberate.
Contact Forms
If the site uses contact forms, add a clear consent field next to submission. Do not pre-check it unless there is a legal reason to do so, and do not hide the policy link. After setup, submit a test inquiry and verify whether the consent appears in the admin email, form entry, or another log if your integration supports that.
What to Check After Submitting a Form
- The form submits without errors after the cookie popup is enabled.
- The consent text is visible near the submit area, and the policy link opens correctly.
- The admin email arrives and still includes all important fields.
- Anti-spam and caching do not block submission after the privacy settings are changed.
WooCommerce and the Customer Account
With WooCommerce, the priority is not breaking the cart, checkout, or account area. The cookie popup should not cover payment buttons, and script blocking should not disable payment elements, shipping fields, or cart updates. If the plugin includes WooCommerce integrations, test them using a test order without real payment.
Check the user account separately as well. If visitors can request their data, delete their account, or change consents, the interface needs to remain available after login and must not conflict with custom account pages. On sites with a modified WooCommerce template, test not only with a default theme but with the actual active theme too.
Comments, Subscriptions, and Embedded Services
If the site collects comments, newsletter signups, or embedded video, do not limit testing to the homepage. GDPR settings need to work where data is actually collected. Check an article with comments, a subscription page, a map page, and a video page. For each element, document whether it should work before consent or only after it.
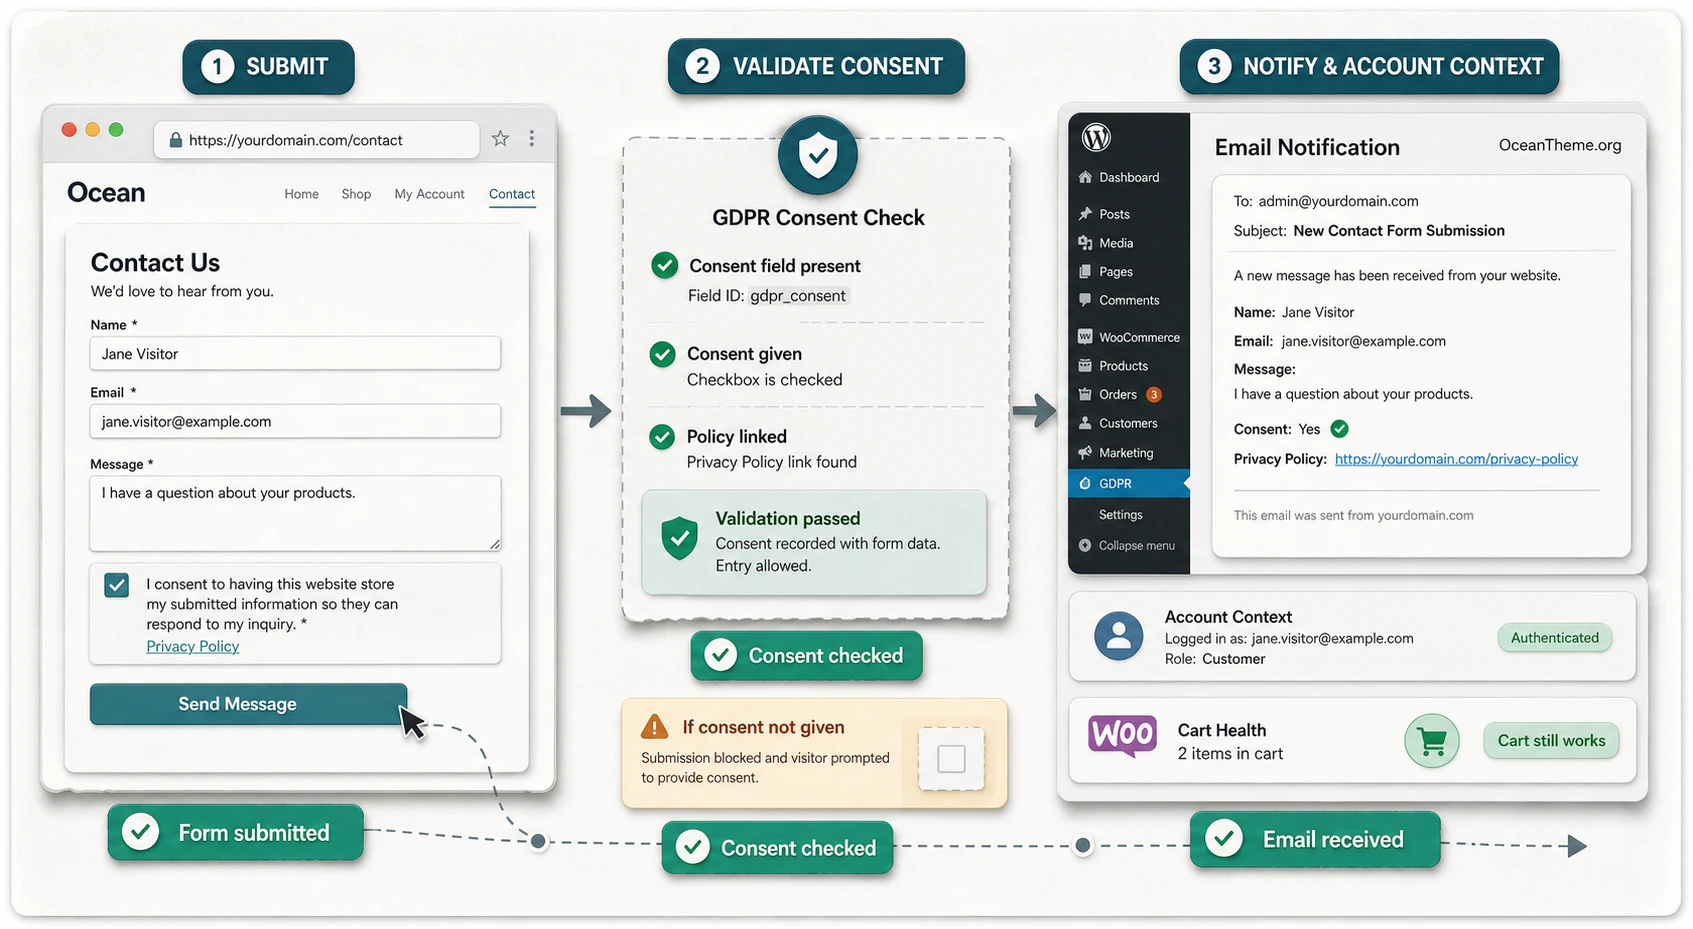
Practical Example: Setting Up an Agency Site with a Lead Form and Analytics
Consider a realistic scenario. You have a WordPress agency site with a homepage, a blog, a lead form, an embedded map, analytics, and an ad pixel. The goal is to show visitors a cookie popup, provide a link to the Privacy Center, keep the marketing pixel from loading before consent, preserve a working lead form, and verify that the user journey remains clear.
Goal
Build a basic GDPR configuration where visitors see a clear banner, can open privacy settings, can submit an inquiry with consent, and the administrator can verify that analytics and marketing elements behave predictably.
Preparation
- The site already has a privacy policy and a contact form.
- The administrator knows which services are connected: analytics, a map, an ad pixel, and anti-spam.
- Caching and script bundling can be temporarily disabled during the initial verification.
- A test email address is available to confirm form delivery.
Setup Steps
- Create a Privacy Center page and insert the shortcodes or blocks the plugin provides for requests and consent management.
- In the cookie popup settings, add concise text, a link to the cookie policy, and a button that opens the settings.
- Create GDPR Services for analytics, the map, and the ad pixel. For each one, describe its purpose in plain language.
- Enable blocking or deferred loading for only one external service first, then test its behavior before and after consent.
- Add a consent field to the lead form if your form and plugin integration supports it. If there is no automatic integration, use the form's native fields and a policy link.
- Open the site in a private browsing window, accept only essential cookies, then repeat the test with full consent.
- Submit a test inquiry and check the admin email, the form entry, and the browser console for errors.
Expected Result
The visitor sees the banner, can open settings, understands what the services do, and can submit the form. The administrator can confirm that services do not run before the selected consent and that the form does not break because of the cookie popup or script optimization.
A Common Complication
If the site uses aggressive JavaScript optimization, an external script may load in a different order or get bundled into a combined file. If that happens, do not try to fix everything at once. Disable script bundling, verify the plugin in a clean state, then turn optimization back on one setting at a time and check the result after each change.
Verifying the Result: How to Tell Whether the Setup Works
GDPR verification should be repeatable. It is not enough to open the homepage and see a banner. You need to test several states: first visit, rejection, partial consent, full consent, return visit, consent withdrawal, data request, and form submission. If even one of those states is undocumented, the administrator will not be able to quickly distinguish normal behavior from an actual issue.
Browser Testing
Use a private browsing window or a separate browser profile. Open the homepage, the form page, the store or product page if WooCommerce is used, and a page with an external service. First accept nothing, then choose minimal consent, then full consent. After each action, refresh the page and check whether the choice is preserved.
Network Request Testing
For analytics and advertising services, it is useful to open developer tools and inspect network requests. Before consent, domains for optional services should not actively fire if you have configured blocking for them. After consent, they should appear without errors. This check is especially important on sites that use caching and script optimization.
Request Page Testing
Open the Privacy Center as a normal visitor. Make sure every link leads to a published page, forms are not empty, requests are understandable, and the expected message appears after submission. If a user request is sent by email, verify delivery. If it appears in the admin panel, confirm where it shows up and who is responsible for processing it.
Safe Improvements Without Editing Plugin Files
For a product like this, the safest improvements usually relate to process, copy, and visual integration rather than programming. Do not edit the plugin files directly: an update can overwrite your changes, and a mistake in consent logic can create a problem that is hard to spot. If you need a visual polish, use theme settings, a child theme, or the Additional CSS field.
Below is an example of a cautious CSS tweak for a Privacy Center page. It does not depend on the plugin's internal classes and works only if you added a custom class to your page through the editor or theme. Add a container class such as privacy-center-guide and apply the CSS through Appearance or a child theme.
.privacy-center-guide a {
  text-decoration-thickness: 2px;
  text-underline-offset: 3px;
}

.privacy-center-guide .wp-block-button__link {
  min-height: 44px;
  display: inline-flex;
  align-items: center;
}
The purpose of this tweak is to make links and buttons on the privacy page easier to read and tap. After adding it, check the page on a mobile device, confirm that the buttons are not crowded together, and make sure the link color still has enough contrast. Rolling it back is simple: remove the CSS and clear the cache.
If you need to change button labels, form messages, or section names, first look for the plugin's built-in settings and WordPress translation mechanisms. Do not use JavaScript to replace text on the fly if the same result can be achieved through settings, translation, or the page editor.
Why WordPress GDPR May Not Work as Expected
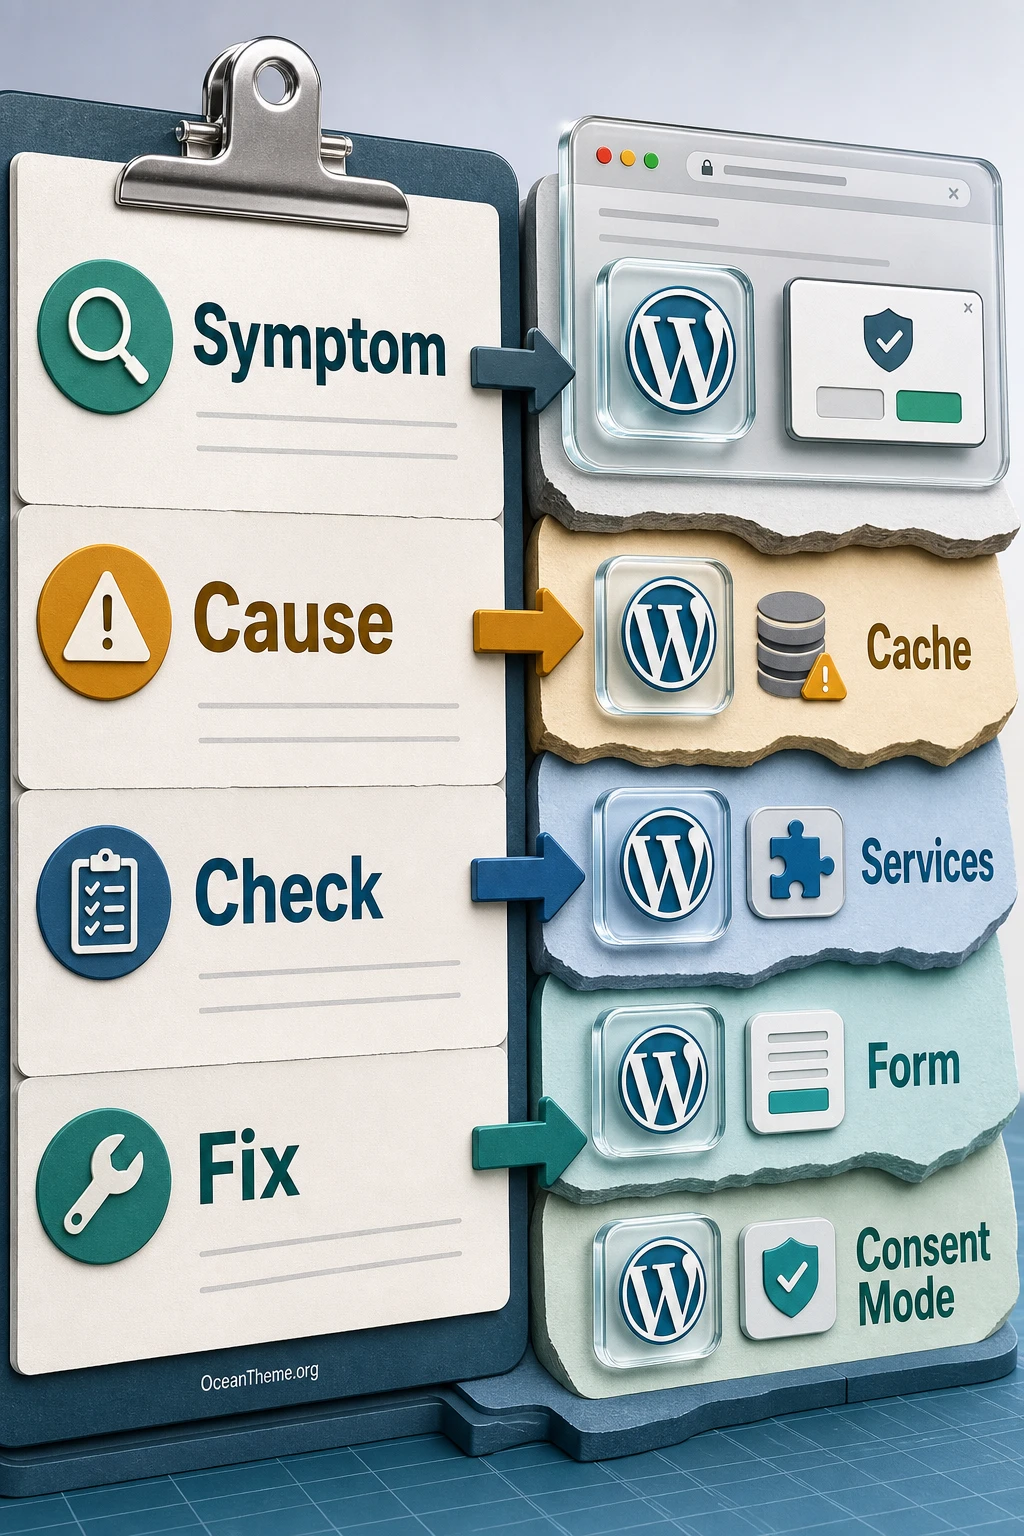
Problems with GDPR plugins rarely look like one obvious failure. More often, the banner is visible but the choice is not saved; services are not blocked; the form stops submitting; the Privacy Center opens but the request never arrives; or settings only take effect after clearing the cache. Below is a troubleshooting map for those situations.
The cookie popup does not appear
Symptom: the popup is enabled in the admin area, but visitors do not see it. Possible causes include the banner already being accepted in the browser, the cache serving an old page, the theme hiding the container, the plugin script not loading, or the popup being disabled on the current page.
What to check
- Open the site in a private browsing window or clear cookies for the domain.
- Clear the WordPress cache, CDN cache, and browser cache.
- Check whether the popup is enabled for the correct page type.
- Temporarily disable JavaScript optimization and run the test again.
If the popup appears after optimization is disabled, do not leave the site without optimization permanently. Create an exclusion for the plugin's scripts or adjust the loading order so the consent logic does not end up inside a conflicting bundled file.
Consent is saved, but the service still loads too early
Symptom: the visitor has not granted consent yet, but analytics, a map, or an ad pixel is already making network requests. The usual reason is that the script is added by the theme, injected by another plugin, served from cache, or not connected to a GDPR Service.
Check where the script comes from. If it is inserted directly in the theme, move it into a managed mechanism or setting where it can be tied to consent. If the script is added by a third-party plugin, review that plugin's documentation and its compatibility with the consent workflow.
The form stops submitting after enabling the cookie popup
Symptom: the submit button can be clicked, but no email arrives or an error appears. Possible causes include an anti-spam conflict, a blocked form script, nonce caching, the banner covering the button, or an error in a required consent field.
Start with the form itself: temporarily disable external service blocking, submit a test inquiry, then restore the settings one by one. If the issue appears only after enabling a specific service, check whether a script needed for form validation or anti-spam was accidentally included in the block list.
The Privacy Center leads to an empty page
Symptom: the link exists, but the page is empty or shows only a heading. That usually means the shortcode was not inserted, was inserted incorrectly, the required module is disabled, or the page is cached in an outdated state.
Open the page in the editor, check the shortcode, save the page, and clear the cache. If the block depends on authentication, test the page as a guest and as a logged-in user. For user requests, the visitor's current state often matters.
Google Consent Mode V2 does not send the expected signals
Symptom: after enabling Consent Mode V2 in the plugin settings, analytics tools do not show the expected consent states. Possible causes include an incorrect integration with Google Tag Manager, early tag loading, caching, another consent system, or incomplete category configuration.
Check the developer's official Consent Mode V2 documentation, then test the tag loading order. Do not enable two independent consent management systems at the same time, because they may send conflicting signals.
When it is better to roll back a setting
Roll back the most recently enabled option if it breaks the form, cart, checkout, user login, or another critical page element. A GDPR interface should not destroy the primary user journey. Restore a working state first, then investigate the exact conflict on a staging copy or during low-traffic hours.
Questions About Setup and Limitations
Can the site be considered fully GDPR-compliant immediately after installing the plugin?
No. The plugin helps display consent interfaces, request flows, and service controls, but compliance depends on your actual data-handling processes, policy text, agreements with services, and which scripts really load on the site. Installation should always be followed by an audit and verification.
Should all modules be enabled at once?
It is better to enable them gradually. Start with the cookie popup and pages, then add services, then form and store integrations, and only after that extra modes such as Consent Mode. That makes it easier to find a conflict and roll back only the most recent setting.
Why is the banner visible to the administrator but not to a regular visitor?
The most common reasons are cache, browser cookies, display conditions, or script optimization. Test in a private browsing window, clear caches, and check whether the plugin script is loading on the public page.
Can the plugin be used together with WooCommerce?
Yes, but the store needs separate testing. Check the cart, checkout, account area, emails, and payment elements. Do not block critical store scripts without running a test order first.
What should I do if an external service is not blocked before consent?
Find out where it is being loaded from: the theme, a separate plugin, code in the header, Tag Manager, or the cache. Then tie it to the correct consent category or move the loading logic into a managed mechanism. If you cannot control the source, document that limitation and do not promise visitors more than the site actually does.
Do I need separate legal text?
Yes. Interface settings do not replace a privacy policy and cookie policy. The plugin can display links, forms, and controls, but the content of those documents still needs to match your site and your jurisdiction.
Will the plugin affect site speed?
Any extra interface and consent logic adds scripts and checks. In most cases, that can be managed with caching and careful configuration, but after enabling service blocking, you should always review performance, the browser error console, and JavaScript loading order.
When CodeCanyon WordPress GDPR Is a Good Choice
This plugin is worth using if you need a manageable set of GDPR interfaces inside WordPress: a cookie popup, a Privacy Center, request pages, a service map, and integrations with common site workflows. It is especially useful when the site owner is ready to do more than simply enable a banner and instead wants to configure the system in layers: copy, pages, services, forms, store, verification, and troubleshooting.
If your entire need is a single "accept cookies" button, the plugin may offer more than necessary. On the other hand, if the site operates across multiple legal regions and requires automatic cookie scanning plus centralized legal support, it is worth comparing specialized platforms. Either way, start with a staging copy or at least enable features gradually.
Once the structure of the pages, services, and testing flow is clear, you can download the ZIP archive, install the plugin on a test site, and run the full verification path: first visit, consent choice, form behavior, external service launch, data request, and rollback of any questionable setting.
The main success criterion is simple: visitors understand what they are choosing, and the administrator can reliably verify that the site behaves exactly as described in the interface and policy.

