


CodeCanyon PrivateContent - WordPress Plugin
The plugin is a comprehensive solution for managing user databases within WordPress, offering multi-level content access control. Its robust features include the ability to create user directories seamlessly. With this plugin, site owners can efficiently manage user permissions and restrict access to specific content based on user roles. It enhances website security by allowing for the creation of private areas accessible to authorized users only.
Plugin Features
This powerful tool enables WordPress site administrators to customize user profiles, offering a personalized experience for each user. Through the plugin, administrators can effortlessly organize users into groups, simplifying the management of content visibility. The seamless integration of this solution ensures a user-friendly experience, enhancing the overall usability of WordPress websites.
The plugin streamlines the process of creating and managing user accounts, providing a user-friendly interface that simplifies complex tasks. It empowers website owners to tailor content accessibility, ensuring that sensitive information remains secure. The intuitive controls offered by CodeCanyon PrivateContent make it easy to configure various levels of access, enhancing the flexibility of content management within WordPress.
With its versatile features, administrators can easily define user roles and permissions, granting or restricting access to specific sections of the website. The plugins functionality extends to customizing login forms and registration processes, offering a seamless experience for site visitors. This streamlined approach to user management enhances the overall efficiency of content delivery on WordPress platforms.
By leveraging the capabilities of the plugin, website owners can establish exclusive member areas, manage subscriptions, and offer premium content securely. The plugins adaptability allows for seamless integration with existing WordPress themes and plugins, ensuring compatibility and a consistent user experience. With its robust features and user-centric design, the plugin provides a comprehensive solution for creating a dynamic and secure user database on WordPress sites.
Specifications:
| Release date: | 01-02-2012 | |
| Last updated: | 23-07-2025 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Clients & Communities | |
| Compatibility: | W6.x W5.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | CodeCanyon | |
| Rating: | ||
Share with your friends!
How to Configure CodeCanyon PrivateContent for Protected WordPress Sections
CodeCanyon PrivateContent is not about making a site look fancier. It is about access control: locking part of your pages, showing content only to a selected user group, giving visitors a login form, and building a simple members-only area without developing a custom portal from scratch. This guide does not repeat the plugin's marketing copy. Instead, it walks through a practical setup: how to prepare WordPress, where to define access levels, how to configure forms, how to verify the result, and what to do if private content is visible to the wrong people.
This article is written for a site owner, webmaster, or editor who already has the plugin ZIP file and wants to understand how to use it safely on a live project. We will carefully separate product-confirmed features from general WordPress best practices: the exact interface items may differ in your build, but the testing logic, usage scenarios, and troubleshooting steps are still useful for most sites with protected content.
The key idea is simple: a private section works well only when user roles, access rules, login behavior, guest messaging, and the verification process are all defined in advance. If you start by installing the plugin and immediately locking pages without an access map, it is easy to run into cache conflicts, user-group confusion, or complaints from people who log in but still cannot see the content they need.

What Problem a Protected Content Plugin Actually Solves
WordPress includes built-in users and roles, but a standard installation is often not enough when you need to quickly create multiple levels of private access on a public website. The typical use case looks like this: some content stays open to everyone, some is available to registered clients, some is visible only to a specific group, and the login form should feel like a normal part of the site rather than a technical WordPress screen.
CodeCanyon PrivateContent belongs to the category of access restriction and private area plugins. Based on the product description, its strong point is a multi-level approach to protected content. That means the site owner is not limited to thinking in terms of just "guest" and "logged-in user." Instead, they can build multiple access groups: clients, partners, course students, staff, members of a private club, or editors of an internal knowledge base.
It is important not to confuse this kind of tool with a full subscription platform. A protected content plugin handles content visibility, login forms, registration, and access management. If your project needs complex pricing tiers, recurring payments, automatic renewals, invoices, coupons, and billing, you will need to check for relevant add-ons or look at dedicated membership solutions. But if the main task is to show the right content to the right user group, PrivateContent addresses exactly that core need.
In that sense, the product is useful as a middle layer between a regular website and a full private platform. Standard WordPress is great for publishing pages and posts, but it does not tell an editor how to assign access by client group. A large membership system can do much more, but it also requires you to plan payments, levels, notifications, renewals, and support. PrivateContent is more direct: it helps you take existing pages and attach visibility rules to them.
This approach is especially valuable on projects where a protected area is added later rather than built into the architecture from day one. For example, an agency may already have a website with services, a blog, and a contact page. Later, it needs to provide clients with instructions and files. Rebuilding the site into a separate portal is expensive, while simply password-protecting a page is awkward. Access groups let you keep a familiar WordPress workflow: the editor creates a page, the administrator assigns access, and the user logs in to see the content intended for them.
Where Private Access Is Especially Useful
In practice, protected content is not just for paid clubs. It is used in business and educational workflows where it is important not to publish everything in the public part of the site.
- An agency client area where each customer can see instructions, files, links, and project status.
- A small training portal with materials for different learner groups.
- An event website where registered participants can access recordings, slide decks, and private announcements.
- A partner area with instructions, pricing files, internal policies, and documents.
- A private knowledge base for staff or volunteers when the project only needs simple access separation.
In all of these cases, the goal is not just to hide a page. You need the user journey to be predictable: registration or manual account creation, login, navigation to the correct section, a clear message when access is missing, a convenient logout flow, and a fast way for the administrator to check which group a person belongs to.
If that path is not defined in advance, the protected area turns into a collection of exceptions. One client gets a link by email, another looks for it in the menu, a third tries to reset a password, and a fourth logs in through an old URL and cannot find the right content. The plugin will not fix that organizational confusion on its own. It gives you the mechanism, but the site owner still needs to define the rules: who gets access, for how long, to which pages, through which login path, and who is responsible for support.
How PrivateContent Differs from a Standard WordPress Role
WordPress roles primarily control permissions in the admin panel: who can publish posts, edit pages, manage settings, and work with users. For front-end visitors, that is too broad a mechanism. Without extra conditions, you cannot conveniently say: this page is available only to students in cohort two, and this block inside the page is visible only to partners.
A plugin like PrivateContent adds a layer on top of the standard user model. In this guide, we will talk about user categories and access rules as a practical map: first define the groups, then connect those groups to content, and only after that add login forms and verify the public-facing result. That sequence reduces the risk of accidentally exposing protected information or, on the other hand, blocking access for everyone.
Another difference is how it works on the public side of the site. WordPress roles almost always sound like administrative permissions: edit, publish, manage. Protected content uses a different logic: see, do not see, log in, receive a message, open the content. That is user logic, not editor logic. A good PrivateContent setup therefore needs to answer not only "who has permission" but also "what will the person actually see on the screen in each situation."
Who PrivateContent Is a Good Fit For, and When Another Approach Makes More Sense
The most common mistake when choosing an access restriction plugin is trying to solve too many different problems with one tool. Protected content, member dashboards, paid subscriptions, training, file management, and client portals may look similar from the outside, but they require different rules, notifications, and validation flows behind the scenes. Before installing anything, it is worth understanding what kind of project you are really building.
It helps to divide projects into three complexity levels. The first is a protected library of materials: users log in, read pages, download files, and maybe submit a form. The second is participants and profiles: each person has their own data, history, custom fields, and possibly a public profile. The third is commercial subscriptions: access depends on payment, expiration, plan level, renewal, and order status. PrivateContent is best evaluated for the first level and part of the second. For the third level, you need to review add-ons and alternatives much more carefully.
Good-Fit Scenarios
PrivateContent makes sense when a site is already running on WordPress and you need a manageable protected layer on top of existing pages. In this scenario, you are not moving the project into a separate system, changing the theme, or building a custom user portal from scratch. You are adding access rules to selected pages, creating user groups, and placing forms where visitors can use them naturally.
A good sign that the project is a match is that you can explain access in one sentence. For example: "All clients can see the shared section, and partners can also see partner-only materials." Or: "Course participants get access to lessons for their cohort, and mentors see additional instructions." If explaining the setup requires a complex diagram of payments, statuses, trial periods, overdue states, and automated emails, the task is already beyond basic content restriction.
- You need to protect articles, instructions, documents, or pages for specific groups.
- The number of users is small to medium, and access can be managed manually or semi-automatically.
- The project needs a simple private area more than a complex payment system.
- Site editors want to manage access without constant developer involvement.
- You need login and registration forms that can be embedded directly into site pages.
When to Be More Careful
If the project is being built from the start as a large membership platform with pricing tiers, coupons, automatic billing, payment logs, newsletter integrations, and subscription reporting, a private access plugin alone may not be enough. In that case, check available add-ons, payment compatibility, and whether the required workflow is actually covered in the documentation. Do not promise your team that access control and subscriptions will automatically become full business logic if the source only confirms content restriction.
You should also be cautious on sites with aggressive caching, a complex multisite network, non-standard user profiles, or a heavy page builder setup. Protected content needs to be validated both on the server side and in the user's browser. If a cache serves a guest a page that was already rendered for a logged-in user, that is not just a visual bug. It is a privacy risk. That is why the sections below include specific guidance on checking cache behavior, permissions, and actual output.
There are organizational limits as well. If administrators do not maintain a record of granted access, do not know who is responsible for removing users after a project ends, and never review old accounts, the protected area will become outdated quickly. A plugin can lock a page, but it does not replace a process: when a user is created, who changes their group, when access is removed, how support requests are tracked, and how disputed cases are reviewed.
For sites that handle personal data, medical materials, legal documents, or internal business files, legal and technical requirements need to be evaluated separately. In those cases, it is not enough to hide content from guests. You also need to think about file storage, access logs, backups, administrator permissions, hosting contracts, and email delivery. This guide does not promise absolute protection: a private area is one part of a system, not the entire security model.
Practical rule of thumb: if you need to quickly protect pages and blocks for user groups, PrivateContent looks like a logical choice. If you need a paid subscription system with billing, renewals, and complex automation, start by reviewing dedicated membership plugins and add-ons.
In this guide, the term membership is used only as the name of a solution category for member sites and subscription workflows. PrivateContent itself is treated here primarily as a private access tool, not as a ready-made payment platform.
What to Check Before Installing on a Live Site
Preparation saves more time than the installation itself. An access plugin affects public page behavior, users, login forms, error messages, and sometimes caching. If you enable it immediately on a live site without a test map, you may get confusing complaints: one user sees the page, another gets a login prompt, a third sees an old cached version, and the editor cannot tell where the rule was actually set.
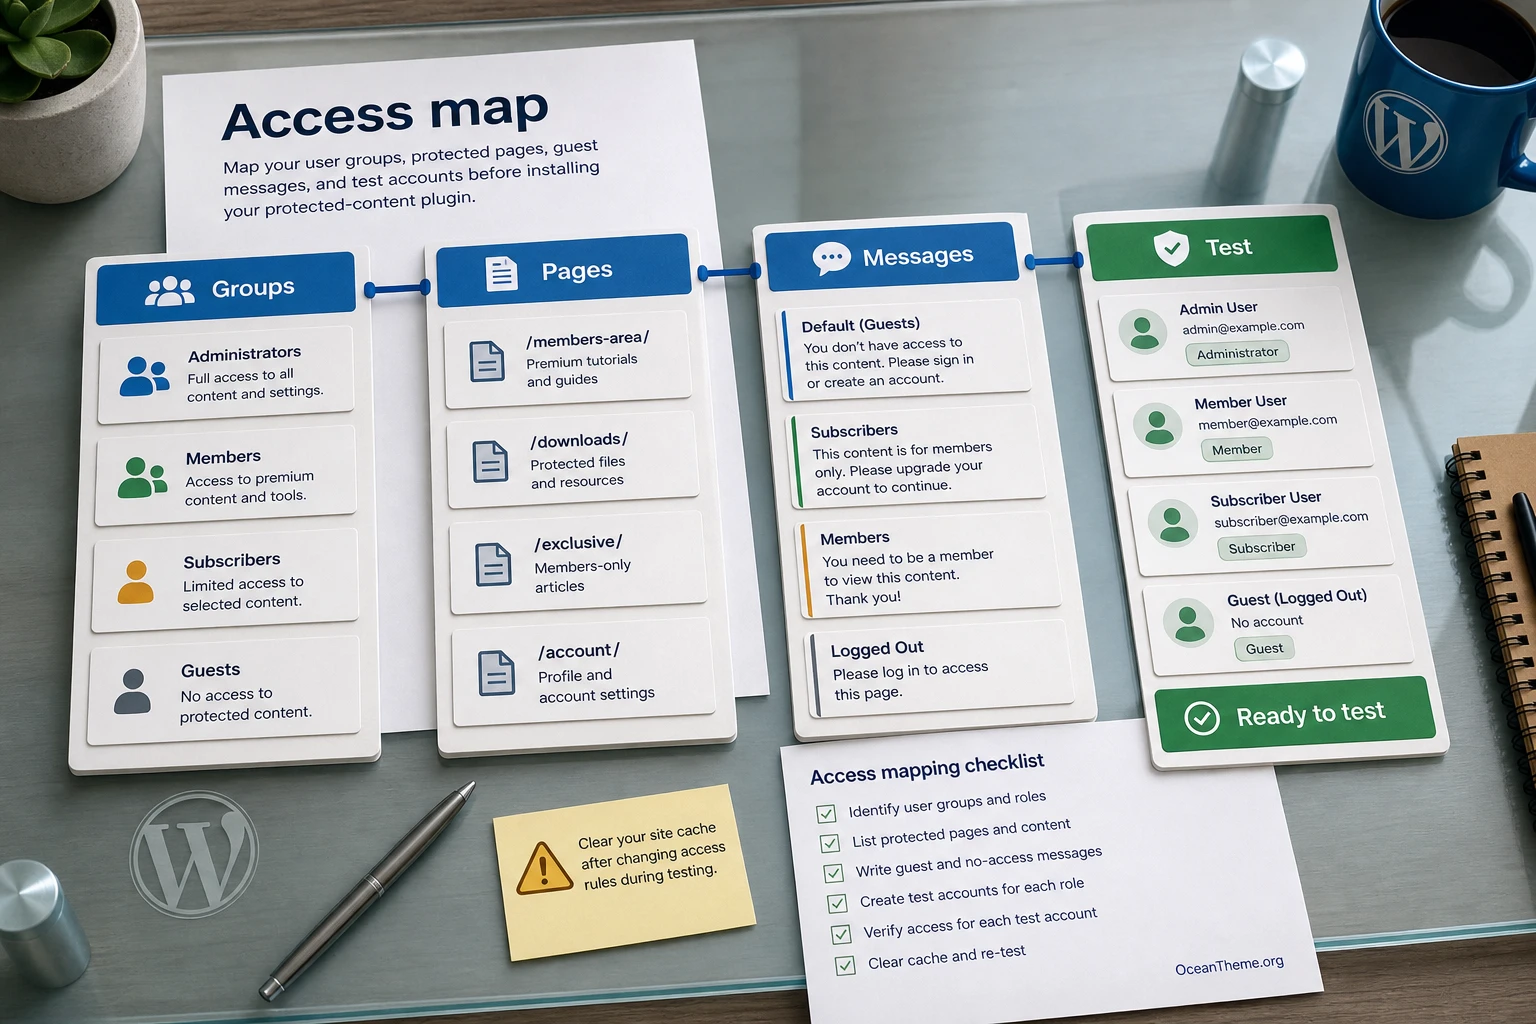
A Mini Access Map Before the First Click
Before installation, write down not the plugin settings but the real groups of people involved. This matters especially for multi-level access. Do not use abstract names like "Level 1" and "Level 2" if the project already has clear roles. Use working labels instead: "Clients," "Partners," "Course Participants," "Staff," "Test Group."
This map can be a simple table in a document. In the first column, list the group; in the second, who belongs to it; in the third, which pages it can access; and in the fourth, who grants that access. Even if you move everything into the admin panel later, this draft map helps you avoid bad configuration decisions. It shows that protected content is not a single checkbox but a connected system.
For each group, it helps to answer five questions right away:
- Which pages or blocks should the user see after logging in?
- What should a guest see instead of the protected material?
- Who adds the user to the group: an administrator, a manager, or the user through registration?
- Does the user need a dedicated destination after login, such as a dashboard page?
- How will the administrator verify that access was assigned correctly?
Technical Environment Check
Because PrivateContent is a commercial WordPress plugin, exact requirements should be verified against the current product page and the developer's documentation. This article intentionally does not lock version numbers into the text, because they go out of date quickly. Instead, use a safe working checklist.
- Make sure the site is running a WordPress and PHP version supported by the plugin.
- Create a backup of both files and database before installing on a live site.
- Prepare a test user without administrator permissions.
- Temporarily disable aggressive optimization on login pages and protected sections if the site uses a caching plugin.
- Check that system emails are not blocked by the host if you plan to use registration and notifications.
- Prepare a separate test page so you do not modify an important section before validation.
Do not start by protecting the home page, cart page, checkout flow, or critical system routes. Even if the plugin can restrict different content types, the first test should be done on a simple standalone page with one paragraph and a clear heading. That makes it easier to understand what the plugin is doing, rather than what the theme, cache, or another module might be doing.
What to Prepare for a Safe Test
A minimal test setup has four elements: a dedicated page, a test group, two users, and a clean browser. The first user belongs to the access group, the second does not. A clean browser or private window simulates a guest. This setup takes only a few minutes, but it immediately shows the three states you will see every day on a real project.
If the site already has active users, do not use their accounts for the first experiments. A real client may have login history, saved cookies, extra roles, or access from other plugins. A test user should be simple and controlled. After validation, you can delete that user or keep it as a permanent control account for future changes.
Which Pages You Should Not Touch on the First Pass
Do not protect the login page, password reset page, privacy policy page, store system pages, contact forms, or other system pages unless you fully understand the consequences. Protected content should help the user reach the right material, not create a trap where they cannot log in, reset a password, or read the explanation of how access works.
If the project uses WooCommerce, a forum, an LMS plugin, or a profile builder, check their own pages first. Each of those solutions may have its own access logic. PrivateContent is best layered onto simple pages first. Complex system routes should only be restricted after separate testing.
Installation and Initial Validation Without Unnecessary Risk
Installing a commercial WordPress plugin usually happens through the admin panel: upload the ZIP archive, activate it, open the settings, and run an initial test. This article does not cover purchasing, entering license details, or obtaining the paid version. The focus is the practical stage after you already have the installation file and the right to use the product on the site.
Basic Installation Order
On a staging site or during a planned maintenance window, follow the standard WordPress sequence. Exact menu names may vary depending on admin panel localization, but the path usually looks like this: Plugins, then Add New, then Upload Plugin, select the ZIP archive, and click Install Now. After the installation completes successfully, click Activate.
After activation, find the new plugin menu item in the admin panel. LCweb products often have their own settings section, but it is best to confirm the exact label in the documentation for your version. At this stage, do not enable every restriction at once. First, identify where the core entities are: users, categories or groups, forms, private access settings, and messages.
Make a note of the path to the main screens. For example: where user categories are created, where the login form is edited, where the message text is configured, and where a rule is applied to a page. That may seem unnecessary until the first support request. When a user says, "I logged in but still see a restriction," the administrator needs to open the right screen quickly rather than search through menus again.
The First Test on a Separate Page
Create a test page, for example "Protected Test Content." Add a short line of text that is easy to recognize instead of mistaking it for a placeholder: "Only the test user should see this paragraph after logging in." Then apply an access rule for one test group. If the interface allows you to protect only part of a page rather than the whole page via shortcode or a special block, start with the simpler option and make it more complex later.
The test should cover three states:
- Open the page as a guest or in a separate browser where nobody is logged in.
- Log in as a test user who has not been assigned access.
- Log in as a test user who belongs to the correct group.
If all three states behave differently in the expected way, the basic installation is working. The guest sees a message or a login form, the user without access does not see the protected content, and the correct user gets the content. If the result is the same for everyone, do not jump into design tweaks. First, check whether the access rule was actually applied, whether the user's group assignment was saved, and whether the page is being served from cache.
After a successful test, keep that page as a control page. Do not delete it right away if you plan to continue configuring forms, redirects, and messages. A control page helps you understand what broke after the next change. If it worked yesterday and today a guest can see the protected text, the cause is almost certainly in new settings, caching, or a conflict with another plugin.
How to Tell an Installation Error from an Access Error
An installation error is blunt: the plugin does not activate, a fatal error appears, the menu item never shows up, or the settings will not save. An access error is subtler: the plugin is installed, the page opens, but different users see the wrong result. For troubleshooting, those two situations need to be separated. If the plugin interface works, do not reinstall the archive at the first sign of an access issue. First, check the group, the rule, the cache, and the login state.
Reinstallation rarely helps when the real cause is a wrongly assigned group. Worse, without a backup and a clear understanding of the current settings, you can lose a working configuration. A safer order is this: take a screenshot or note down the current settings, verify the test users, clear the cache, temporarily simplify the access rule, and only then consider reinstalling or contacting the developer.
Quick takeaway after installation: do not treat plugin activation as a success until you have tested one protected item in guest mode and under two different user accounts.
Access Model: User Categories, Protected Pages, and Protected Fragments
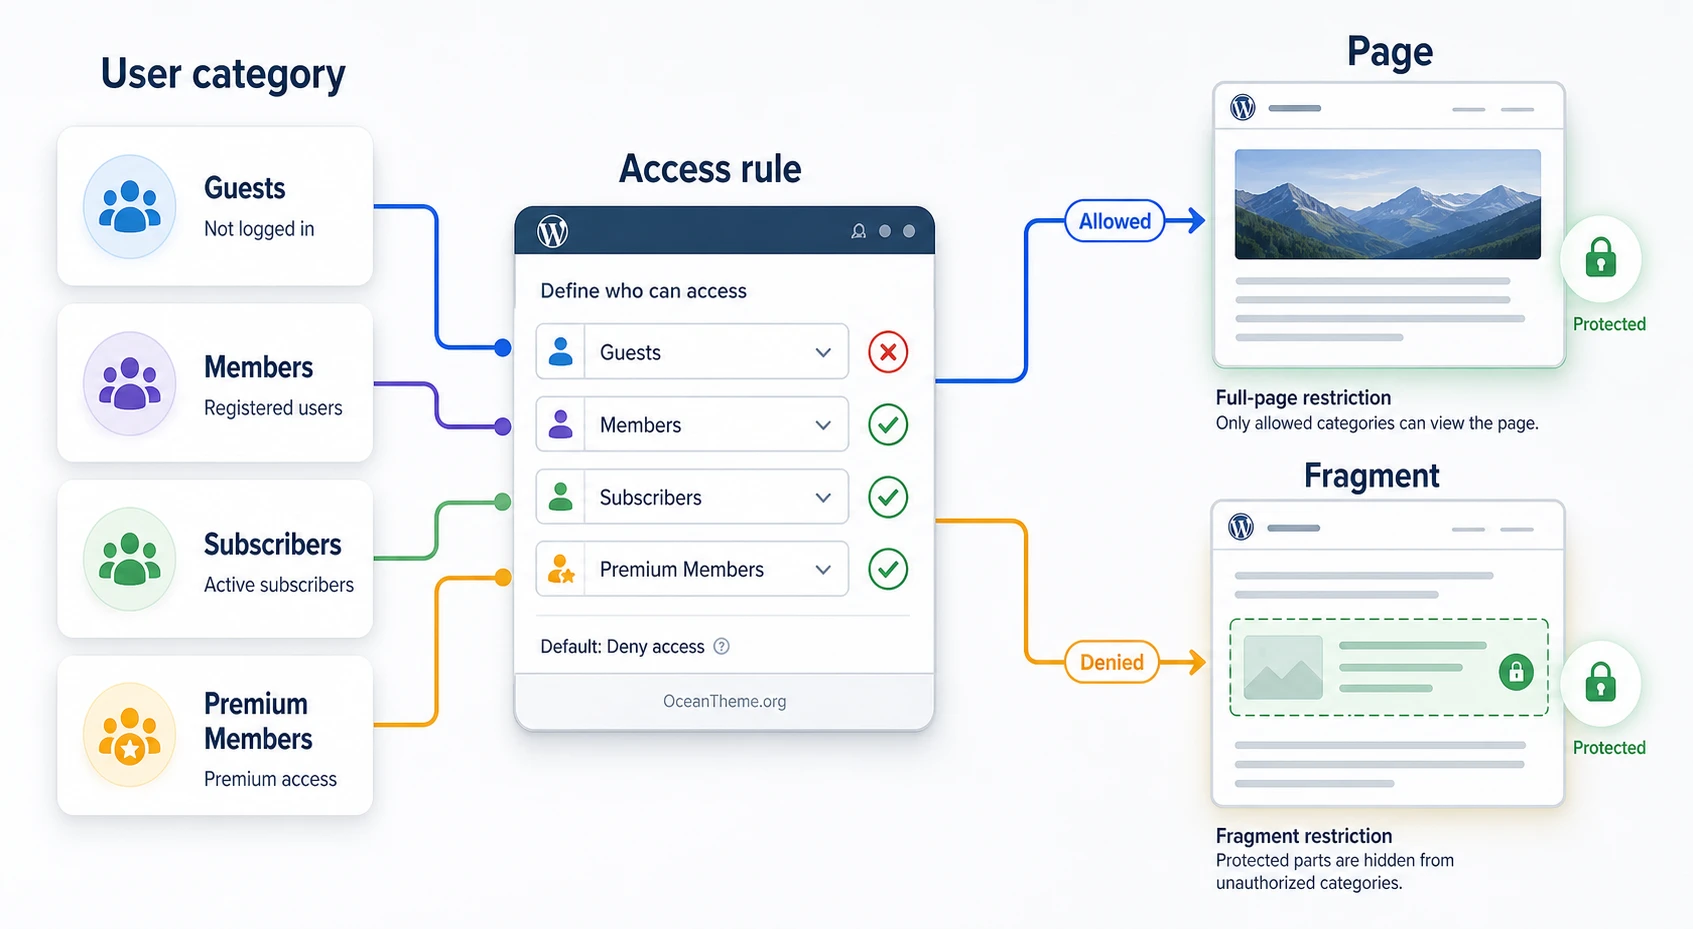
The most important part of setting up CodeCanyon PrivateContent is not the appearance of the form. It is the access logic. Multi-level content is useful only when the levels do not overlap chaotically. If one user accidentally ends up in multiple groups and a page is protected by multiple rules at once, the administrator needs to understand which rule wins and what the user will actually see on the site.
How to Think in Groups Instead of Individual Users
Even if you only have ten users right now, do not assign rules one by one unless you truly need to. Groups or user categories let you manage access as a system. When a new client appears, it is much easier to add them to the "Clients" category than to remember which pages need to be opened individually.
The rule of "group first, user second" is especially important when access is assigned by a manager rather than a technical administrator. It is easier for a manager to choose a clear category than to understand which page has which restriction. The group becomes an internal agreement: a person in this group gets a specific set of materials, and a person outside the group does not.
It is best to keep three layers in your working map:
- People layer: real WordPress users and their profile data.
- Access layer: PrivateContent categories or groups that define permission to view content.
- Content layer: pages, posts, blocks, or shortcode fragments where the restriction is applied.
This approach is especially useful for courses and client portals. For example, a "Course Materials" page might be available to all participants, while an "Extra Files for Mentors" block is visible only to a separate group. If your version of the plugin supports restricting fragments via shortcode, use that carefully: the more nested rules you place on one page, the greater the chance that you will later forget why a specific user sees the wrong block.
If your version uses a shortcode for a private fragment, treat it as a technical access boundary. The protected material lives inside that boundary, and the public page text lives outside it.
For a long-term site, it also helps to maintain a naming policy - a simple naming convention. For example, every course group starts with "Course," every client group starts with "Client," and every internal group starts with "Team." That is not a technical requirement, but it reduces mistakes in the admin panel. Once the group list grows, similar names without a system become a source of incorrect assignments.
Protecting a Full Page vs Protecting a Fragment
The right choice depends on the use case. Protecting the entire page is easier to test and safer for materials that should not appear in public discovery at all. Protecting a fragment is useful when the page itself must stay public, but a specific block should be visible only to logged-in users: a downloadable file, an internal link, an extended instruction, or an application form for participants.
| Scenario | Best Approach | What to Verify |
|---|---|---|
| Client instruction or protected lesson | Protect the entire page for the required group | The guest does not see the text, and the group user sees the page after login |
| Public article with a bonus file | Protect only the fragment or the link | The public part is indexable, and the private link is hidden from guests |
| Partner area with multiple pages | Create a page set and one shared user category | The menu, links, and direct URLs all behave consistently |
| Internal knowledge base | Split materials by access groups | A staff member from one group does not get another group's materials without a valid reason |
If you are unsure, start by fully protecting a standalone page. That is easier to explain to editors and easier to diagnose. Add fragment-level restrictions only when there is a clear reason to leave part of the page public.
How to Work with Nested Materials
Protected sections often include links to related pages: a lesson leads to a file, the file leads to an instruction, the instruction leads to a form. A common mistake is protecting only the first page while leaving the rest of the materials open. A user may not see the link in the menu, but they can still open the direct URL from an email or browser history. That is why it helps to create a list of internal URLs for each protected section and test them separately.
If you have a category archive, post archive, or material listing page, check not only the individual post but also the list page itself. Sometimes an editor protects the post, but the archive still shows the title, excerpt, or image. For a public teaser, that may be fine if it is intentional. For confidential material, it may reveal more than you want. Decide in advance what a guest is allowed to see: only the section title, a brief invitation to log in, or nothing at all.
Detailed Configuration After Activation
Once the first test passes, you can move on to settings that actually affect usability. The best order is logic first, presentation second: groups, rules, and messages first; forms and appearance after that. If you start with the design of the login form but never validate permissions, you may end up with a polished page that sends users to the wrong place or fails to unlock the content they need.
Detailed configuration should be documented. That does not mean writing a large manual for every field. A short internal file is enough: which groups exist, which pages are protected, where the login form lives, where the redirect goes, and which pages are excluded from cache. That document will help when updating the plugin, changing editors, or investigating disputed access cases.
User Groups and Categories
Create the minimum number of groups needed. Do not build too many levels in advance. A good starting model for most projects is one test group, one main group for clients or participants, and one internal group for staff or editors. Once the workflow becomes stable, you can add finer segmentation.
How to Name Groups
A group name should help the administrator, not look attractive in a storefront. Use clear internal labels: "Clients," "Partners," "Course - Basic Access," "Course - Mentors," "Staff." If the group belongs to a temporary program, add a short cohort marker, but do not turn the name into a long description. The key is that another editor should understand a month later who belongs there.
How to Avoid Confusion with Overlaps
If a user can belong to several groups, decide in advance what that means. For example, "Clients" may grant access to general instructions, while "Partners" grants access to a separate section. Overlap is fine if the user truly should see both sets of materials. But if the groups are mutually exclusive, such as different course tiers, it is better not to add a person to multiple levels without a clear reason.
When overlaps are unavoidable, use test users for each typical profile. One test account is only a client, the second is a client and a partner, the third is a staff member, and the fourth has no access. After every major change, open the same page under those accounts. That makes it much easier to spot exactly what changed.
Message for Guests and for Logged-In Users Without Access
The access restriction message is not a minor detail. The user should understand what happened: they are not logged in, their account is not part of the required group, or the material is no longer available. If everyone sees the same generic phrase, the administrator will get unnecessary support requests.
For a guest, a message inviting them to log in or register is usually enough if registration is open. For a logged-in user without access, it is better to show a neutral explanation: the material is available to a different group, contact the administrator, or make sure you are logged in under the correct account. Do not expose unnecessary details of the protected area in a public-facing message. A guest should not see a list of hidden materials just because they opened the URL.
The message should be short and useful. A poor placeholder says only "Access denied" and leaves the person stuck. A good placeholder explains the next step: log in, use the email address you registered with, or contact your account manager. For a user without access, avoid sounding accusatory. They may have been added to the wrong group or logged in through a different address. The tone of the message affects support load.
Login and Registration Forms
If PrivateContent provides login and registration forms, treat them as part of the user journey. Do not send people to the default wp-login.php screen if the project is meant to feel like a client portal or an educational site. The login form should appear alongside a short explanation: who can log in, what to do if there is a problem, and where the user will land after a successful login.
In the form settings, check which fields are actually necessary. The more fields you request during registration, the higher the chance of mistakes, invalid data, and incomplete submissions. For a protected section, a name, email address, password, and possibly one field that helps the administrator identify the user's group are often enough. If you need extra data, verify where it is stored and who can access it.
What to Check After Saving the Form
- The login form appears on the correct page and does not break the theme layout.
- Password errors and empty-field errors are shown clearly.
- After login, the user lands on the expected page rather than in the WordPress admin panel.
- After logout, the protected content becomes inaccessible again.
- If registration is enabled, it does not place the user into a privileged group without review.
Redirects After Login and Logout
A redirect is the user's path after an action. For a protected area, it matters almost as much as the access rule itself. If a user logs in on a course page, it makes sense to send them back to the course materials. If they log in from a general access page, it makes sense to send them to a member area or a page with available materials.
Do not set the redirect target to a page that is itself restricted by another group. That creates the impression that something is broken: the person entered correct credentials but still sees a restriction. First confirm that the destination page is available to all users in the required group. Then test the direct URL in a separate browser.
Emails and Notifications
If your version includes notifications for registration, password changes, or user actions, configure them from a support perspective. The email should clearly show who the sender is, what happened, and where the user should go next. Do not include confidential data in the message, and do not send passwords in plain text. WordPress sites with unreliable email delivery typically use a separate SMTP plugin, but that is part of the mail infrastructure rather than PrivateContent itself.
Emails should be checked not only for delivery but also for meaning. The user should understand why they received the message and which button leads to the protected area. If an email is sent after a user is added manually, add a separate validation step: make sure the user is already in the correct group before the email goes out. Otherwise, the person receives an invitation, logs in, and sees a denial. Technically the email was sent, but the user flow is broken.
Registration: Open, Manual, or Hybrid
There are three registration models for a protected area. Open registration lets people create their own accounts, but it requires spam protection and a clear rule for which group they are assigned to. Manual registration is safer for client and partner areas: the administrator creates the user and assigns access directly. A hybrid model accepts a request through a form, but access is granted only after review.
Do not automatically assign new users to a private group unless you are fully confident in the workflow. On a public site, that can expose materials to anyone who signs up. If screening is required, use manual approval or a separate intermediate group where the user sees only a message such as "Your request has been received."
Importing and Bulk-Adding Users
If the product or supporting tools allow user import, test it first with a small CSV file containing two or three rows. The risk in bulk import is not only technical failure but also incorrect column mapping: the email ends up in the wrong field, the name becomes the group, the group is not recognized, or some users receive extra access by mistake. Before importing, create a backup and prepare a rollback plan.
After import, check several random accounts from different groups. Do not stop at the message that says "import completed." What matters in a protected area is the actual result: the user logs in and sees only their materials. If the import process creates passwords or sends emails, verify that the message does not expose unnecessary information and does not link to the wrong page.
Styling the Form and Access Page
Verify functionality first, then visual styling. The login form should look normal on mobile screens, should not be covered by a fixed menu, should not lose field labels, and should not blend into the background. If the plugin offers built-in design settings, start there. If they are not enough, use a careful CSS adjustment in the theme or in the Additional CSS area, but do not edit plugin files.
A safe option is to wrap the login page in your own container and style only that container. This keeps you from depending on internal plugin classes that may change after an update.
.pc-client-zone {
  max-width: 760px;
  margin: 0 auto;
  padding: 32px 24px;
  border: 1px solid #d7dde8;
  border-radius: 8px;
  background: #ffffff;
}

.pc-client-zone input[type="text"],
.pc-client-zone input[type="email"],
.pc-client-zone input[type="password"] {
  width: 100%;
  min-height: 44px;
}

.pc-client-zone .access-note {
  margin-top: 16px;
  font-size: 0.95rem;
  color: #4b5563;
}
This snippet does not try to guess PrivateContent's internal classes. It works around your own wrapper, which you can add to the login page or an editor block. Validation is straightforward: the form stays readable, the fields do not overflow the width, and rollback is as simple as removing that CSS or the wrapper.
If the form stops submitting after a CSS change, revert the styling and check whether the container is covering the button, whether focus states were disabled, or whether error messages were hidden. Clean visuals should never come at the cost of accessibility: the field label should be clear, the error should be readable, and the button should remain visible on mobile.

Practical Example: A Protected Client Area for an Agency
Now let us build a scenario that is easy to adapt for a course, a partner section, or an internal knowledge base. Imagine an agency wants to provide clients with a page containing instructions, files, and links to reports. The material should not be visible to guests or random WordPress users. At the same time, the editor should be able to add new clients without involving a developer.
This example is useful because it includes all the key PrivateContent elements: a user group, a protected page, a login form, a guest message, a message for a logged-in user without access, a direct URL check, and cache compatibility. If you can set up this scenario confidently, more advanced versions will differ mostly in the number of groups and pages, not in the core logic.
Goal
Create a protected page called "Client Hub" that is visible only to users in the "Clients" group. A guest should see either a login form or a clear message. A user without access should see a separate explanation so they do not assume the site is broken.
Preparation
Before configuring anything, create a test user with regular permissions, a separate "Clients" group, and a simple page with several content blocks. Inside the page, you can place an introduction, a list of links, a downloadable file, and support contact details. If the site uses caching, exclude the test page from full-page caching until validation is complete.
For this example, also create an open page called "Client Login." It can include a short explanation and the login form. Do not mix it with the protected page itself while you are testing. A separate login page makes it easier to understand where to send users from an email, a menu item, or an access restriction message.
Configuration Steps
- Create or open the "Clients" access group in the PrivateContent interface.
- Add the test user to that group and save the profile.
- Create a "Client Hub" page in WordPress and add the content that should be protected.
- Apply the page access rule for the "Clients" group.
- Configure the guest message: invite the person to log in and explain that access is granted to agency clients.
- Configure the message for a logged-in user without access: suggest contacting their account manager.
- Place the login form on the access page or next to the message if that flow is supported in your version.
- Save the settings and clear the page cache if caching is enabled.
Validating the Result
Open the page in a private browser window. You should not see the client hub content. Instead, you should see either a message or a login form. Then log in as a test user who is not part of the "Clients" group: the material should still stay protected. After that, log in as a user in the "Clients" group and make sure all page blocks are visible, all links open correctly, and files do not require extra permissions.
Then test the return path. Log out, refresh the page, and confirm that the protected material is hidden again. Next, open the direct file URL if the file is stored in the Media Library. If the file is supposed to be private but the direct URL is still available to guests, change the storage approach or use protected file delivery if your plugin stack supports it.
Control sign: the direct URL of a protected page should not bypass the access rule. Always test the direct URL, not just navigation from the menu.
A Detail About Menus and Links
Even if the page is protected, the menu link to it may still remain visible. That is not always a mistake. Sometimes it is useful to show guests a "Client Hub" menu item so they can reach the login form. But if the very existence of the section should not be public, the menu needs separate configuration. PrivateContent controls access to the material itself, while menu item visibility may depend on the theme, the menu editor, or other plugins.
For a client portal, a common compromise is this: the login entry point is visible to everyone, but internal links inside the protected section appear only after authentication. That way the user does not lose the path to log in, while private pages are not exposed in navigation before they should be.
How to Hand the Workflow Off to an Editor
After setup, create a short instruction for the editor: how to add a page to the client section, which group to choose, where to review the guest message, how to add a user to the group, and which test account to use to verify the result. You do not need to document the entire admin panel. Five or six steps tailored to the actual site are enough. That reduces the chance that someone creates a new private page a month later but forgets to assign access.
If multiple editors work on the team, agree on who is allowed to change access groups. A content editor may write the material, but they should not always manage users. The fewer people who can grant private access, the easier it is to investigate mistakes and keep the system organized.

Validation, Security, and Cache Compatibility
After configuring a protected area, do not stop with a visual check in one browser. Access depends on the user account, session, cookies, cache, direct URLs, and sometimes files stored in the Media Library. If you test only under an administrator account, you can miss a serious problem: administrators can usually see almost everything, so their session is a poor way to validate real user restrictions.
Validation in Four Modes
Use a simple matrix. It helps you quickly understand where the failure is: in the access rule, the user's group, the login form, or the cache.
| Mode | Expected Result | If the Result Is Different |
|---|---|---|
| Guest without login | Sees a message or login form, does not see the protected block | Check whether the rule is applied to the page and whether the cache was cleared |
| User without group | Sees a denial or an instruction to contact the administrator | Check group overlap and the user's WordPress role |
| User in the required group | Sees the protected material and can follow internal links | Check the group assignment and the post-login redirect |
| Administrator | Used only for setup, not for final access testing | Do not draw conclusions from the admin account |
Cache and Optimization
Caching plugins make a site faster, but protected content requires careful exclusions. The main risk appears when a page rendered for one user state is served to another state. For example, a guest may receive content that was cached for a logged-in user, or an authenticated client may see the guest placeholder instead.
For login-related pages, cookies matter especially because browser state is what allows the site to distinguish a guest from an authenticated user. If the cache ignores that state, the protected area starts behaving unpredictably.
For login, registration, member area, and fragment-protected pages, it is usually best to disable full-page caching. If the caching plugin lets you exclude URLs, cookies, or parameters, use those built-in settings. Do not try to fix this kind of issue just by clearing the cache: that may help temporarily, but it does not correct the caching rule.
Check caching not only after enabling PrivateContent, but also after updating the caching plugin, changing CDN settings, or enabling new host-level optimization. Sometimes the problem does not appear on the day you configure the protected area, but later when the site is being optimized. Keep a separate list of exclusions for private pages and store it alongside your internal access documentation.
Files in the Media Library
Check files separately if the protected page contains PDFs, ZIP archives, or images. Restricting the page does not always mean protecting the direct file URL in the Media Library. If a file should not be accessible via direct URL, verify whether your version of the product or a related solution offers protected file delivery. If not, do not store critical documents as regular public WordPress attachments.
SEO and Indexing of Protected Pages
Protected materials should not accidentally become a source of SEO spam or empty pages in the index. If a page is fully private, consider whether search engines should see it at all. In some cases, site owners keep a short public login page with a normal description and render the private material inside it only after authentication. In other cases, private URLs are better excluded from the sitemap through an SEO plugin if that fits the site structure.
Do not assume that protected content is automatically safe from search visibility. Check the page source in guest mode: private text should not appear in the HTML if it is meant only for users after login. If the text is merely hidden with CSS, that is a poor model for confidential material.
Validation After Updates
Updates to WordPress, the theme, caching plugins, and PrivateContent itself can change the behavior of forms, scripts, styles, and redirects. You do not need to manually retest the entire site after every update, but you should have a control workflow. Open the login page, the protected test page, the direct URL of protected content, and the page shown to a user without access. If those four checks pass, the chance of a hidden break is much lower.
Before a major update on a live site, it helps to have a staging copy. That is especially important if the protected area is tied to clients, courses, or partners. On staging, you can catch a conflict before users start contacting support. If no staging copy exists, at least choose a lower-traffic time window and keep a backup ready.
Practical Ways to Use It Without Overcomplicating the Project
Once the basic protected area is working, it is tempting to start locking everything. A better approach is to expand gradually: every new scenario should have a clear group, a clear piece of content, a clear message, and a clear validation step. Below are several use cases that fit a multi-level access plugin well without turning the site into a complicated platform.
The expansion principle is simple: one new scenario, one testable hypothesis. For example, first you protect a client page. Then you add a partner section. Then you introduce an extra block for mentors only. After each step, test the guest view, the user without access, and the user with the required group. If you add ten rules at once, it becomes difficult to tell which one caused the problem.
Mini-Course with Different Participant Groups
For a mini-course, create a separate group for each cohort or level. Public pages can explain the program, while lesson materials are visible only to participants. If some materials are available to mentors, create a separate group and do not mix it with baseline access. Test not only lessons, but also menus, file links, comments, and feedback forms.
Knowledge Base for Clients
A client knowledge base works best when the user has one clear starting page. Do not make clients memorize dozens of private URLs. Create a page called "Client Materials," grant access to the client group, and organize topic sections inside it. If some clients should see different documents, use extra groups only for those blocks rather than for every small link.
Partner Area
A partner area usually contains documents, instructions, banners, internal policies, and contact channels. It is important to configure a useful message for users without access: a partner may log in with an old email address or lose group assignment after a manual edit. If the message is clear, support can more quickly determine whether access needs to be restored or whether the person ended up in the wrong place.
Internal Team Materials
For an internal team, a protected area can replace scattered documents, but it should not store critical secrets without additional protection. PrivateContent helps limit the visibility of pages, but responsibility for passwords, email, administrator roles, backups, and hosting access still belongs to the site owner. Use this scenario for instructions, internal procedures, and training materials, not for storing sensitive keys or personal data without a legal review.
Protected Bonuses Inside Public Articles
If the site publishes blog posts or tutorial articles, you can keep the public part open while showing bonus material only to members. That bonus might be a checklist, an additional example, a recording link, or a downloadable file. This scenario works well when the public article should stay indexable and attract traffic, while the protected block encourages people to log in.
But fragment-level restriction requires discipline. In the editor, it should be obvious where the private block starts and where it ends. Do not place important protected text too close to public content without checking the guest HTML. If the editor is not comfortable with shortcode or restriction blocks, create a ready-made page template first so they change content rather than the access structure itself.
Different Instructions for Different Client Types
Agencies, service companies, and consultants often work with multiple client types. Some need instructions for handing off assets, others need report access, and others need training recordings. Instead of one large protected page, create several sections and connect them to separate groups. That is better than giving every client the same access to the entire archive.
The key is not to split groups to the point of absurdity. If every client ends up with their own category, the administrator quickly loses visibility. Individual groups make sense when the materials are truly unique or confidential. For standard instructions, a shared group with separate topic pages is usually the better choice.
Why Protected Content Can Behave Incorrectly
Problems with private access often look similar: the user cannot see the material, the guest sees too much, the login form does not return to the right page, or the error message is unclear. But the causes are different. Below is a diagnostic map that helps you avoid changing every setting at once.
The main rule of troubleshooting is not to test everything under an administrator account. Admin access often hides the problem. If a regular user complains about access, create or use the same type of account and repeat the path: open the page, log in, follow the redirect, refresh the page, log out, and open the direct link.

A Guest Can See Content That Should Be Protected
Symptom
You open a private page in a new browser without logging in and see the full text, file, or link that should be available only to a user group.
Possible Causes
- The access rule was applied to the wrong page or was not saved.
- Only a specific fragment is restricted, while important content sits outside it.
- The cache is serving an older open version of the page.
- The direct link points to a Media Library file rather than to a protected page.
What to Do
First, check the access rule in the admin panel and save the page again. Then clear the cache only for that page and open it in a private window. If the problem involves a file, test the file's direct URL. If the file opens without login, do not assume it is protected just because the link is hidden on a protected page.
The User Logged In but Still Cannot See the Section
The most common reason is that the user is not in the correct group or is in a different group with a similar name. Open the user's profile in the admin panel and review the access assignment. Then make sure the page rule is linked to that exact group. If you have many groups, temporarily create a test page for only one group and validate it separately.
If the assignment is correct, check the post-login redirect. The user may authenticate successfully but land on a page where access has not been granted. In that case, it looks like a denial even though login itself worked.
Another common cause is that the person logged in under a different email address. On client sites, one person may have an old address, a company address, and a personal address. In support, it helps to ask not only for the name but for the exact account email used to log in. That is often faster than searching for a configuration problem when access was granted to a different account.
The Login Form Looks Broken or Does Not Fit the Layout
The cause is usually theme CSS, a page builder layout, or a conflict with form styles. First test the form on a simple page without complex columns or popups. If everything works there, the issue is in the layout of the specific page. Use built-in design settings if they exist, or wrap the form in your own container and style that container as shown in the configuration section.
After Login, the User Lands in the Wrong Place
Check the redirect settings. If the plugin allows you to define a post-login URL, it should lead to an accessible page. Do not send users to a page restricted by another group, and avoid external redirects unless there is a clear reason. If the user logs in from a specific content page, verify whether the current configuration can return them to the original URL or always sends them to a general dashboard.
If the redirect creates a loop, the user sees the login form over and over again. That may mean the destination page is itself restricted for that group, cookies are not being saved, the cache is serving an old form, or another plugin is intercepting authentication. Break the chain down step by step: did login succeed or not, was the user session created or not, and is the target URL accessible or not.
The Protected Page Works Sometimes but Then Reverts to an Older State
This usually points to a cache conflict. Exclude login pages, registration pages, and protected materials from full-page caching. If server-level cache or a CDN is involved, a setting in the WordPress plugin alone may not be enough. Test the result after clearing every cache layer and in a browser without a saved session.
Registration or Password Reset Emails Are Not Arriving
This is not always a PrivateContent problem. WordPress sends mail through the server's mail function, and the host may restrict delivery. Check the mail log, configure SMTP through a separate trusted plugin, and make sure the messages are not landing in spam. Do not change access settings until you have separated the email issue from the authentication issue.
To test email, create a separate test address on an external email service and run the full workflow: registration, confirmation, password reset, and admin notification. If email arrives for one domain but not another, the cause may be DNS, SPF, DKIM, or the receiving provider's policy. That will not be fixed by changing access groups.
The Protected Block Is Visible in the Editor but Not on the Site
The WordPress editor and the public-facing site may display content differently. In the editor, the author sees the page content because they are editing the material. On the front end, that same block is processed through access rules. If an editor says the block "disappeared," clarify where they are looking: in the admin panel, in preview mode, under an admin account, or as a regular user.
Test the published page in a separate browser. Preview mode may use the admin session and does not always reflect the state of a normal visitor. For access control, the real public URL matters more than preview.
The User Can See the Menu but Not the Page
That is not necessarily an error. Menu visibility and page access can be controlled by different mechanisms. If the menu item is visible to everyone, a guest can click it and see the login form. If that is intentional, it is fine. If the menu item should disappear for guests, configure the menu separately or use a solution that manages navigation visibility by role and login state.
Do not try to hide the problem just by removing the menu item. The direct URL still needs to be protected. The menu affects usability, while the access rule protects the content itself.
When It Is Better to Roll Back a Change
Roll back the most recent change if it made protected material visible to guests, caused a user to lose access to a working section, or turned the redirect into a login loop. Do not try to fix everything at once. Return to the last known working configuration, clear the cache, and repeat the change on a test page.
A good habit is to change one thing at a time. First the group, then the message, then the redirect, then the design. If you change the group, cache, form, and CSS all at once, troubleshooting turns into guesswork. With protected content, that is risky because the mistake may not just be inconvenient - it may expose the material itself.
Questions About Setting Up PrivateContent on WordPress
Can I use the plugin for just one protected page?
Yes. That is a perfectly valid setup. Create one group, one test user, and one protected page. In fact, it is the best first step: you can validate the login form, guest message, caching, and access assignment without risking the rest of the site.
Should all private pages be blocked from indexing?
If a page is entirely made up of protected material, it is usually better to remove it from public search logic through your SEO plugin settings and sitemap. If the page acts as a login entry point and contains a public explanation, you can leave that public part accessible, but the private text should not appear in the guest HTML.
Can I protect files just by hiding their links inside a protected page?
A hidden link is not the same as a protected file. Test the direct attachment URL. If the file opens without login, you need a dedicated file protection method or a different storage approach. Do not rely only on a hidden content link for sensitive documents.
Why should I avoid testing access under an administrator account?
Administrators often have elevated permissions and can see more than regular users. For testing, create separate accounts: one without the required group and one with it. That reveals access rule mistakes much faster.
What should I do if users start seeing the wrong page version after caching is enabled?
Exclude login pages, registration pages, and protected materials from full-page caching. If a CDN or server-side cache is involved, review those settings separately. Clearing the cache without adding a permanent exclusion fixes the problem only temporarily.
Is PrivateContent suitable for a full paid subscription system?
The plugin belongs to the category of private and multi-level access solutions. A full subscription model requires payments, membership levels, renewals, notifications, and reporting. If those are critical, review the available add-ons and compare the product against specialized membership plugins.
Can I let an editor manage users without giving full administrator access?
That depends on your site's permission model and the capabilities of the specific product version. Do not assign the administrator role just to let someone add users to a group. First check whether permissions can be limited using standard WordPress tools, plugin settings, or a separate role-management solution.
When CodeCanyon PrivateContent Is a Strong Choice
PrivateContent is worth testing if you need a protected layer on an existing WordPress site: user groups, protected pages or fragments, login forms, and a clear path to materials after authentication. It is a good fit for client areas, training materials, partner documents, and internal instructions where the main priority is manageable content visibility rather than a complex payment platform.
Before launching on a live site, verify three things: the group map matches real users, guest mode does not expose private text, and cache does not serve the wrong page version. After that, you can carefully move the setup from a test page to production sections. If you are ready to evaluate the product on your own site, you can download CodeCanyon PrivateContent near the download block and start with a separate test page rather than fully locking an important section.
Do not treat a protected area as a one-time configuration. After adding new pages, groups, users, caching rules, or updates, run the control scenario again. The most reliable approach is to keep a test user, a test page, and a short internal instruction for the team. That way, PrivateContent remains a manageable tool rather than a hidden set of rules nobody remembers.
During preparation, no exact YouTube video was confirmed that clearly demonstrates this specific product rather than just showing a generic marketplace walkthrough. For that reason, no video block was added to the guide. It is better to leave the page without an iframe than to embed an irrelevant video and create the false impression of an official tutorial.

