


CodeCanyon Lighthouse - WordPress Plugin
Lighthouse is a performance tuning plugin, removing lots of default WordPress behaviour, such as filters, actions, injected code, native code and third-party actions.
Plugin Features
CodeCanyon Lighthouse is a performance optimization plugin for WordPress that significantly enhances website efficiency. Focused on improving speed and overall functionality, this tool is essential for WordPress users aiming to boost their sites performance. It offers a comprehensive set of features that streamline and optimize various aspects of a WordPress website.
The functionality of this tool extends to caching mechanisms, image optimization, and code minification, all designed to reduce loading times and enhance site speed. By optimizing critical elements like CSS, JavaScript, and HTML, the plugin ensures fast and efficient website loading. Additionally, advanced techniques are employed to prioritize content delivery and improve user experience.
An outstanding feature of this plugin is its ability to provide detailed performance reports and analytics. Users gain access to valuable insights on their sites speed, performance scores, and specific optimization areas. This data-driven approach enables website owners to make informed decisions and implement targeted enhancements.
Moreover, seamless integration with existing WordPress themes and plugins makes CodeCanyon Lighthouse a hassle-free optimization solution. Its user-friendly interface allows for easy configuration and customization, catering to both novice and experienced WordPress users. With regular updates and continuous support, the plugin stays current with the latest optimization methods and best practices.
Website owners can rely on CodeCanyon Lighthouse to significantly impact their sites SEO rankings and user engagement. By emphasizing performance optimization, the plugin helps sites achieve higher rankings in search engine results and offers visitors a smooth browsing experience. Whether for personal blogs, business websites, or e-commerce platforms, this versatile tool addresses the core needs of WordPress users seeking to enhance their online presence.
In conclusion, CodeCanyon Lighthouse is a dependable and effective performance optimization plugin for WordPress. With its robust feature set, seamless integration, and data-driven approach, it serves as a valuable asset for website owners looking to enhance their sites performance. By leveraging the capabilities of this plugin, users can unlock their WordPress websites full potential, achieving optimal speed, efficiency, and user satisfaction.
Specifications:
| Release date: | 11-10-2020 | |
| Last updated: | 05-09-2025 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Core Enhancements | |
| Compatibility: | W5.x W6.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | CodeCanyon | |
| Rating: | ||
Share with your friends!
A Guide to Configuring and Safely Using CodeCanyon Lighthouse
CodeCanyon Lighthouse is not a typical cache plugin that promises to speed up your site with a single click. In this guide, we will look at how to use it as a toolkit for performance control, cleaning up unnecessary WordPress output, checking server response times, adding basic login protection, and tuning a site carefully without modifying core files.
This guide is written for the situation where the plugin is already available to the site administrator and the goal is to understand what to enable first, which settings require caution, how to verify the outcome, and how to roll back a change if it affects the theme, page builder, form plugin, WooCommerce, or another critical module. It does not cover purchasing, payment, or license activation - only practical work with an installed product.
The core idea behind CodeCanyon Lighthouse is to give a WordPress site owner more control over what the site sends to the browser and which background processes put load on the server. That is why this guide is built around practical workflows rather than a marketing list of features: what gets enabled, which unnecessary output disappears, where the change should show up, how to spot the difference, and what warning sign tells you the setting should be turned off.

What Lighthouse Actually Solves on a WordPress Site
Lighthouse is most useful when a site is already live, but the administrator is dealing with a familiar WordPress problem: too many unnecessary requests, meta tags, built-in scripts, background server calls, and features that not every project needs. Page caching can hide some of that load, but it does not explain why the site gets heavier after adding a new plugin, why the admin area responds slowly, or why the latest round of tuning made a test score worse.
The developer positions Lighthouse as a performance and security tool that removes some default WordPress behavior, helps with caching, provides data for informed decisions, and adds modules such as SpeedFactor, persistent SQLite3 object cache, Cloudflare Turnstile for login protection, registration filters, and Volt for managing multiple sites. It is important to understand this from the start: the plugin does not work like a magic speed-up button - it acts more like a control panel for several layers of the site.
In a typical WordPress request, the request passes through the theme, plugins, the database, a set of default actions and filters, and then the browser receives HTML, styles, scripts, images, and external resources. Lighthouse steps into specific parts of that chain: it disables unnecessary elements, changes how some headers and browser hints behave, helps reduce extra requests, and in newer versions adds a separate persistent object cache layer. Instead of one master switch, the user gets a collection of decisions, each of which has to be matched to the site in front of them.
When the impact shows up fastest
The most visible gains usually appear on sites where many default WordPress features are enabled even though some of them are not being used. For example, a company site with comments turned off, a blog that does not embed third-party posts, a catalog with no public registration, an agency site without WooCommerce, a landing page built with a heavy page builder, or a client project where the admin area is crowded with unnecessary blocks. In those cases, cleaning up output and disabling background processes often produces a clearer improvement than piling one more cache layer on top of what is already there.
There is a tradeoff, though. If the site actively uses comments, oEmbed, the REST API, XML-RPC, Jetpack, WooCommerce, public registration, a mobile app, external integrations, or a complex page builder, you cannot turn on everything blindly. The goal is not to choose the "strictest" settings, but the ones that do not break how people actually use the site.
How it differs from a typical cache plugin
A standard cache plugin usually creates static copies of pages and manages minification, lazy loading, and cache headers. Lighthouse takes a broader view: it helps disable parts of WordPress, measure response time, remove unnecessary output from <head>, control browser hints, reduce Heartbeat overhead, check specific metrics, and close off several common abuse vectors. That makes it useful alongside a cache plugin, but it should not be treated as a full replacement for every optimization tool.
Practical rule: start with settings that you can verify quickly by eye or with a metric, then move on to options that change WordPress behavior more deeply. If you cannot quickly tell what changed after enabling a feature, it is better to test it on a staging copy of the site.
Who This Product Fits and Where It May Be Unnecessary
Lighthouse works best in the hands of an administrator, developer, technical SEO specialist, or multi-site owner who is willing to verify the outcome after each change. The plugin offers many toggles and status markers, and that is exactly what makes it both powerful and demanding.
It is not right for every site. On a small blog with solid hosting, a modern theme, and a single cache plugin, some of its features may simply be more than you need. On a larger project with WooCommerce, account areas, forms, membership logic, and external integrations, Lighthouse should be introduced gradually, because even a well-intentioned optimization can affect a critical user flow.
Good use cases
- A WordPress site loads reasonably well, but you want to remove unnecessary output, scripts, meta tags, and background overhead without editing the theme by hand.
- The administrator wants to see more than a one-time test result and track response time changes after updates, plugin installs, or a hosting move.
- The site does not need XML-RPC, public author archives, some comment features, extra editor blocks, or default widgets to stay enabled.
- The team manages several WordPress projects and wants a single admin dashboard for updates, core health indicators, and site status.
- User registration is open, but the administrator is dealing with spam accounts and wants filters in place before the user database becomes polluted.
When a different approach is better
If the site's main problem is oversized images, weak hosting, heavy third-party widgets, a poorly written theme, or dozens of unused plugins, Lighthouse can help reveal and partially soften the issue, but it will not replace a proper technical cleanup. The developer explicitly notes that good results still depend on image optimization, removing unused styles and scripts, working on fonts, and making basic server-side improvements.
You should not enable Lighthouse as a strict "speed mode" on a live store without testing. WooCommerce, the cart, checkout, payment forms, customer accounts, and subscriptions often depend on scripts, cookies, the REST API, AJAX, and dynamic caching. What you need here is a plan: a site copy, a list of critical pages, specific checks, and a fast way to disable any questionable setting.
What to Check Before Installation and First Run
Before installing a performance plugin, prepare the site first. This is not just a formality. Lighthouse can change what WordPress outputs on the front end, how the admin area handles background requests, which headers browsers receive, and which entry points are closed to outside access. So the first step is to document the current state.
Create a baseline for comparison
Before installation, collect a minimal set of reference data: response time for the home page, one typical internal page, a page with a form, a product page or cart page if there is a store, and one admin login flow. Do not chase the perfect stack of testing services. What matters more is that you compare the same thing before and after: the same URL, the same page type, similar cache conditions, and the same workflow.
Record TTFB, the number of requests, page size, main menu behavior, form behavior, image loading, user login, and checkout if the site has one. After each major change, these checkpoints will help you see exactly what moved. Without a baseline, optimization turns into guesswork.
Check site dependencies
Make a short list of features that cannot break. On a standard site, that usually means the menu, contact form, search, comments, map, analytics widget, subscription flow, login page, and content editor. For a store, add the cart, checkout, quantity changes, coupons, customer account, emails, and payment methods. For a community-driven site, verify registration, password reset, profiles, and notifications.
It also helps to flag plugins that may depend on XML-RPC, the REST API, Heartbeat, cookies, comments, or their own scripts loading on every page. That does not mean Lighthouse cannot be used. It means those features should be enabled carefully and only after verification.
Set up a fallback path
For most settings, it is enough to have admin access so you can uncheck a box. But some features, such as object cache via object-cache.php or changes to wp-config.php, sit closer to the infrastructure layer. Before touching those, make sure you have access to the hosting file manager or SFTP, a fresh backup, and a clear understanding of where wp-content, wp-config.php, and the plugin directory live.
Safe order of operations: first create a backup, then enable one settings group, then test the front end, the admin area, and critical forms. Only after that should you move on to the next group.
Installation and the First Post-Activation Check
Installing CodeCanyon Lighthouse follows the normal process for a WordPress ZIP plugin. In the admin area, open Plugins, go to Add New, choose Upload Plugin, upload the ZIP archive, and click Install Now. After installation, use Activate Plugin. If the site refuses the ZIP because of an upload size limit, use manual installation only through secure file access and only if you understand the structure of wp-content/plugins.
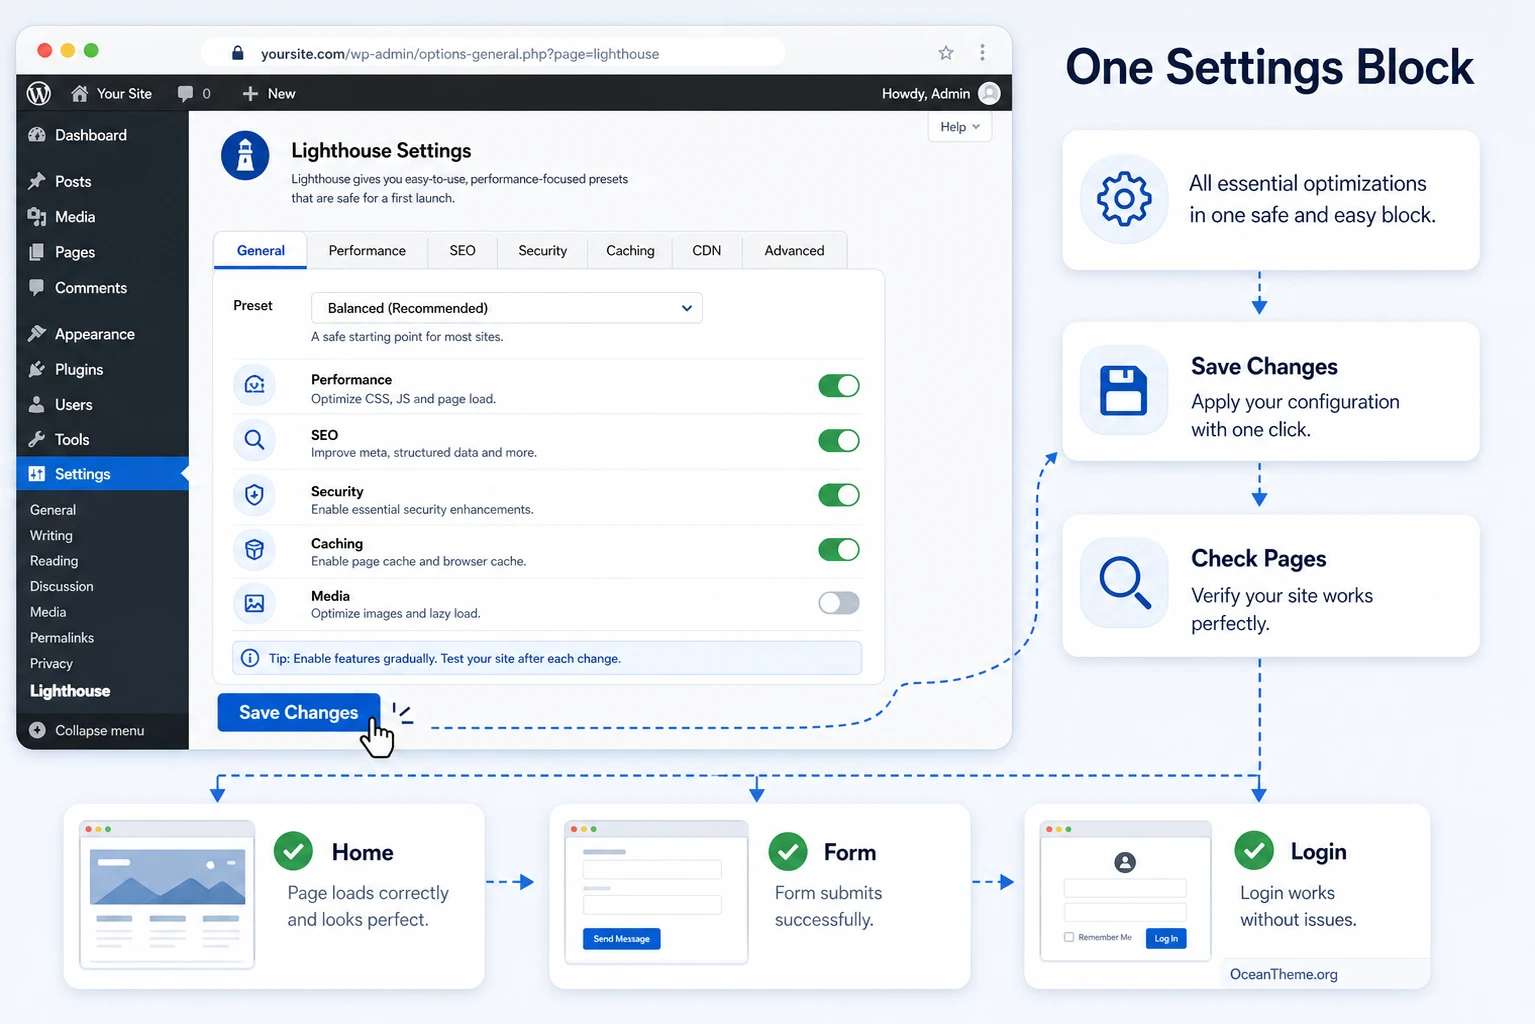
After activation, the Lighthouse documentation expects a settings section under Settings -> Lighthouse. On the opening screen, the user sees a summary of settings, system details, and a set of recommended configuration options. That is the right place to start: do not jump straight into deeper tabs until you understand which modules are active and what the plugin itself is recommending.
First check without aggressive settings
- Open the public site in a private browser window and make sure the home page loads without visible errors.
- Check admin login, because some security features affect authentication directly.
- Open a page with a form or a cart, if those flows exist, and perform a test action without making a real payment.
- Go back to
Settings->Lighthouseand review which tabs are available in your version:Dashboard,Performance,Cache,Security,SpeedFactor,Media & Storage,Tips & Tricks, or similarly named sections. - Do not enable settings marked
use with cautionyet unless you understand exactly which WordPress feature they disable.
At this stage, the goal is not to speed up the site immediately. The goal is to confirm that the plugin is installed correctly, the admin area still opens, there are no conflicts with an empty configuration, and the required tabs are available. If a problem appears right after activation with no settings enabled, start by checking WordPress version compatibility, PHP version, hosting cache, and any other performance plugins already in use.
Post-Install Configuration: From Presets to Manual Decisions
The Lighthouse documentation advises newer users to start with a preset, while more experienced administrators are encouraged to enable options gradually and verify the outcome. That is strong advice, because the plugin includes many settings with different levels of risk. One checkbox may remove an innocuous extra tag, while another may disable a mechanism the theme or an integration depends on.
It is easier to work in layers. Start with the summary and presets, then move to safe front-end cleanup, then server-load settings, then browser resource hints, then media and storage, and finally security. That order lowers the chance of ending up with twenty enabled settings and no clear way to tell which one broke the menu or the form.
Summary, recommendations, and status labels
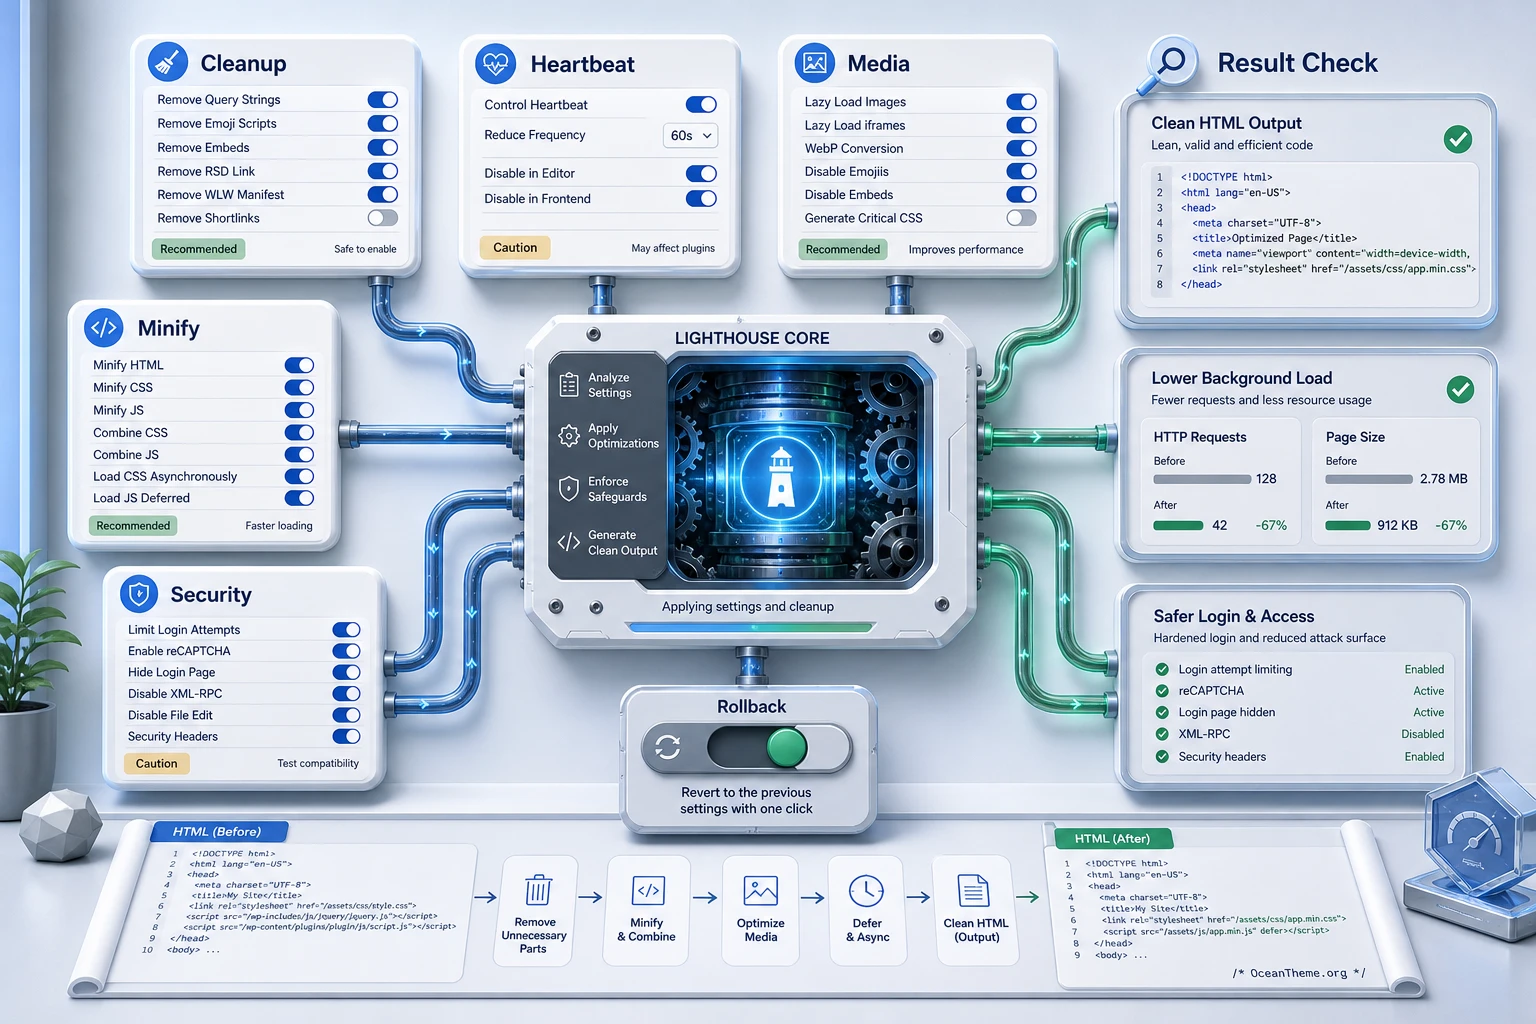
In the Lighthouse interface, individual settings may be labeled recommended, not recommended, use with caution, or use if needed. Treat those as a priority system. Start with the recommended options that actually fit your site. Leave the "if needed" settings for cases where you have a specific problem to solve. Test caution-level settings one at a time.
For example, disabling emojis and extra links in <head> is usually easier to verify: check the page source, request count, and visual appearance of the content. Disabling XML-RPC, the REST API, oEmbed, comments, or Heartbeat requires testing the related workflows. If the site uses the WordPress mobile app, remote publishing, Jetpack, or an external system, XML-RPC may still be needed. If a form or builder depends on the REST API, overly strict restrictions can break saving or data submission.
Optimizing the front end
In performance and theme cleanup sections, Lighthouse can remove version parameters from styles and scripts, disable emojis and smileys, remove some links from <head>, disable WordPress embeds, strip out unnecessary widgets, and reduce the load caused by elements the site does not use. The practical goal is to produce cleaner HTML and fewer requests without changing the design.
For a standard brochure-style site, a gentle starting set might look like this:
- Disable emojis and smileys if editors do not use them as part of the content.
- Clean up
<head>by removing internal links that are not needed by search engines, users, or integrations. - Disable WordPress embeds if your posts do not need to be embedded on other sites and you do not use that mechanism inside your own content.
- Slow down Heartbeat if the admin area creates noticeable background load, but editors are not working simultaneously on a large volume of content.
- Remove Dashicons on the front end for logged-out users if the theme does not depend on that icon font.
After applying that set, open the home page, an article page, a page with a form, and the mobile menu. Check not only speed, but behavior as well: do the menu items expand, does the form submit, did any icons disappear, did fonts change, and are there any browser console errors.
Settings you should never enable mechanically
Some options look attractive but require context. Disabling native lazy loading for images only makes sense if another plugin or the theme is already handling it better and without conflicts. Removing mediaelement.js is safe only if the site has no audio, video, or player that depends on the standard WordPress library. Disabling author archives helps on projects with no public author pages, but it can be the wrong move for an editorial site with author profiles.
The same caution applies to canonical redirect and REST request settings. If the site's SEO structure, page builder, form plugin, store, or integration expects standard WordPress behavior, overly aggressive cleanup may create a hidden conflict rather than a speed improvement. A good Lighthouse configuration is not the most aggressive one - it is the one you have actually verified.
| Settings group | When to enable it | What to verify after saving |
|---|---|---|
<head> cleanup |
When the site does not depend on WordPress service links, RSD, WLW, or shortlinks. | Page source, SEO plugins, canonical URLs, and the absence of markup errors. |
| Disable emojis and embeds | When the content does not rely on standard WordPress embeds as a key feature. | Posts with media, the editor, text appearance, request count, and the browser console. |
| Heartbeat and server load | When the admin area frequently generates background AJAX requests or the site runs on limited hosting. | Post autosave, collaborative editing, WooCommerce notifications, and admin area stability. |
| Media and storage | When the site stores many images and does not need every intermediate size. | New uploads in the media library, responsive images, galleries, and main image quality. |
| Security and registration | When the site is dealing with login attempts, spam registrations, or unnecessary XML-RPC access. | Login, password reset, registration, external apps, and block logs. |
The table does not replace testing. It helps you decide the order: the more deeply a setting changes WordPress behavior, the fewer changes you should make in a single pass.
SQLite3 Object Cache: When to Enable It and How to Test It
One of the stronger features in newer Lighthouse versions is persistent object caching on SQLite3. In standard WordPress, object cache lives only for the duration of a single request unless a separate persistent cache is installed. That means frequently reused data often gets read from the database again. Persistent cache stores some of that data between requests and can reduce MySQL load, especially on sites with frequent access to options, user metadata, and transient data.
The developer highlights one important distinction: this mode does not require a separate Redis or Memcached server, and the object-cache.php drop-in can be installed and removed from Settings -> Lighthouse -> Cache. That makes the feature attractive on standard hosting where you cannot ask the server administrator to provision Redis. But convenience does not remove the need for caution: object cache is an infrastructure-level layer and should be tested separately from routine HTML cleanup.
Prerequisites
Before enabling it, check whether the SQLite3 PHP extension is available on your hosting. If the host has it disabled, the feature will not work correctly. Also make sure there is no other active object-cache.php drop-in in wp-content from Redis, Memcached, or another cache plugin. Running two persistent object caches at the same time is a bad idea: WordPress uses a single drop-in, and a conflict can lead to unpredictable troubleshooting.
If the site already uses Redis Object Cache or a similar tool and it is working reliably, do not replace it without a reason. Lighthouse's SQLite3 layer is most useful where there is no separate server-side service and you want to cut down database queries. On a high-traffic clustered project with multiple web servers, a file-based SQLite cache may not fit the architecture at all.
Safe activation order
- Create a backup of both files and database, especially if the site is live and receiving leads or orders.
- Confirm that no other
object-cache.phpis present, or document which cache layer is currently in use. - In the admin area, open
Settings->Lighthouse->Cacheand install the drop-in using the built-in button if your version provides it. - Immediately confirm that the site still opens, the admin area does not throw an error, and the Lighthouse panel shows cache status.
- Clear page cache if you use it, then run several identical requests against the home page and an internal page.
- Review hit/miss stats, cache database size, and the behavior of dynamic pages.
Do not judge object cache by a single cold page load. First the cache has to warm up, then it starts serving repeated data. If hit/miss values do not change after multiple requests and the site behaves the same or worse, check the drop-in status and PHP errors.
What can go wrong
A common conflict symptom is that the site still works, but some dynamic data updates with a delay, the admin area shows odd status messages, or another cache plugin says its drop-in is inactive. If that happens, do not start changing ten settings at once. First disable Lighthouse object cache using the built-in drop-in removal button, clear all caches, and test again.
If the problem disappears, the cause was a cache conflict or a hosting incompatibility. If it does not, keep going: PHP errors, file permissions, disk space, a corrupted drop-in, server-side caching. The key point is not to delete plugin files manually on a live site until you have used the normal rollback path and still have backup access.
SpeedFactor and Monitoring: How to Tell Whether the Site Actually Got Faster
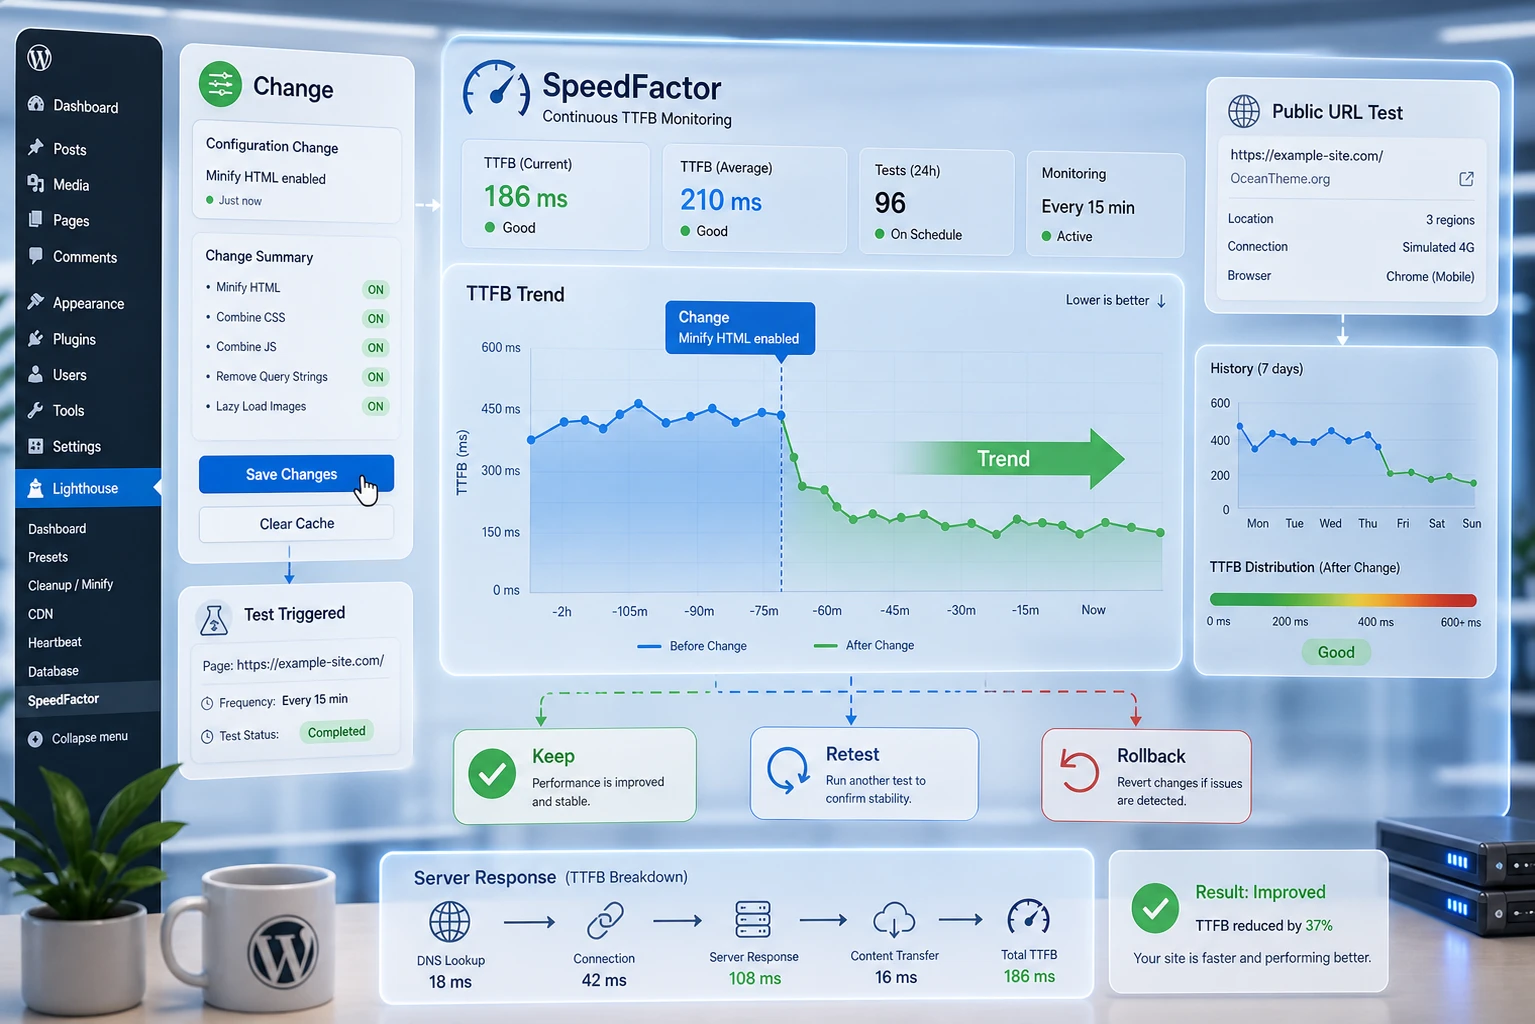
SpeedFactor is Lighthouse's module for recurring speed and response-time checks. Its value is that it helps you look beyond a one-time test and focus on trends. If yesterday you enabled <head> cleanup, today you updated the theme, and tomorrow you added a new builder block, the chart can show where the slowdown began. That is especially useful on sites that are constantly changing.
According to the developer description, SpeedFactor measures raw page-loading data such as connection time, redirects, time to first byte, and total document response. It is not a full browser-based lab test that accounts for every image and third-party script. It is a separate monitoring layer focused on server and document response timing. So it should not be expected to answer every Core Web Vitals question. Its role is to show how baseline response speed changes and whether the site has regressed after admin actions.
Setting the check frequency
The documentation mentions frequency options such as hourly, twicedaily, daily, and weekly, along with a selectable time range for charts. For most sites, daily or weekly checks are enough. Hourly checks can be useful during active experimentation, but on weaker hosting or across many sites they may add unnecessary background traffic.
A strong default for a smaller site is a daily measurement with trend review after each major change. For an agency serving clients, it can make sense to use more frequent checks on troubled projects and less frequent checks on stable ones.
How to interpret the chart
Do not expect every enabled setting to produce a beautiful drop on the chart. Sometimes HTML cleanup reduces the number of requests but barely changes TTFB. Sometimes object cache lowers database load, but the real bottleneck still lives in an external script that SpeedFactor does not measure as a full browser experience. So read it as a combination: SpeedFactor, browser testing, network waterfall, real pages, and error logs.
If the chart gets worse after a specific change, approach it like an engineer:
- Roll back the most recent setting, not the entire set of parameters.
- Clear page cache, object cache, and CDN cache if those exist.
- Repeat the test on the same URLs.
- Compare the admin area and the public site, because the problem may live in only one layer.
- If the cause is still not confirmed, leave the setting disabled until you can test it on a site copy.
Security, Login, and Registration Without Overpromising
Lighthouse includes several features that are not about speed at all, but about basic WordPress protection: disabling XML-RPC, brute-force protection, user enumeration prevention, registration spam filtering, a CAPTCHA module, and Cloudflare Turnstile integration. These features are useful, but they should not be described as absolute protection. They close off common abuse patterns and reduce noise, but they do not replace updates, strong passwords, backups, access controls, or monitoring.
XML-RPC and user enumeration
XML-RPC was historically used for remote access to WordPress, but many modern sites no longer need it. If the site does not use the WordPress mobile app, Jetpack, older remote publishing tools, or integrations that explicitly require XML-RPC, you can disable it through Lighthouse and check whether anything breaks. If an integration stops working, turn the setting back on and look for a different protective measure.
Blocking user enumeration helps when an attacker tries to discover usernames through URLs such as ?author= or exposed REST API user responses. The expected outcome is simple: a public visitor should not be able to retrieve a convenient list of real accounts. But if the site includes public author profiles, account pages, or community features, make sure the restriction does not interfere with legitimate profile display.
Brute-force protection and CAPTCHA
Brute-force protection matters on sites that see a noticeable number of login attempts. After enabling it, test normal admin login, password reset, editor login, and the behavior of an incorrect password. If you enable CAPTCHA for login, registration, password reset, or comments, test each selected screen separately. Do not turn on CAPTCHA where it is not needed, especially if it makes the user journey worse.
Cloudflare Turnstile works as a softer alternative to traditional CAPTCHA. The external service performs a browser-side check and returns a token that must then be verified by the server. If your Lighthouse version supports Turnstile, store the keys carefully, do not expose secrets in public code, and verify that the protection appears only on the forms where it is intended. If Turnstile becomes temporarily unavailable or conflicts with caching, you need a fallback login path for the administrator.
Registration spam filtering
If the site allows public registration, Lighthouse can check domains, keywords, suspicious address patterns, and external lists. The documentation also describes a filter named lighthouse_spam_check_result, which lets you react to the registration check outcome. That is already developer territory: you can send a notification, write to a log, or connect an internal review system, but only if you understand which data you are processing and where it will be stored.
For most sites, the built-in settings are enough. Start with a clear error message, a careful list of blocked domains, and verification against real registrations. If false positives are frequent, loosen the rules. If spam still gets through, enable additional layers one by one and review the data.
Resource Hints, Media, and Storage
The tabs related to speed and media do more than remove unnecessary items - they also help guide the browser. Lighthouse includes settings for DNS Prefetch and Preconnect, as well as media and storage controls such as native lazy loading, srcset behavior, disabling oversized image generation, and removing extra image sizes. These options may look technical, but in practice they answer a simple question: which resources should the browser prepare in advance, and which files should WordPress stop generating unnecessarily.
DNS Prefetch and Preconnect
dns-prefetch tells the browser to resolve DNS for an external domain ahead of time. It is a lightweight hint that can help with fonts, analytics, a CDN, or other third-party resources. preconnect goes further: the browser establishes the connection early, so it consumes more resources. Lighthouse documentation warns that preconnect should be used carefully, or you may spend bandwidth on resources the user never requests.
A safe approach is to add only domains that really load on most important pages. For example, a static-file CDN, the main font domain, or an analytics domain if it is needed immediately. Do not add dozens of rarely used external services. After saving, review the page source and the browser's network waterfall. If the hint is present but the actual resource is hardly ever used, remove it.
Media and image sizes
Media settings should be touched only after checking the theme. WordPress may generate several image sizes, and the theme and plugins may rely on specific variants. If you disable too many sizes, older images will not disappear automatically, but new uploads may receive a different file set. That is good for saving space, but risky for a theme, a gallery, an online store, or a responsive layout.
Native lazy loading is useful in most cases, but if the site already uses a separate advanced lazy-loading mechanism, conflicts are possible. In that case, do not run both layers at once. Choose one approach, then test the primary image above the fold, the gallery, images inside posts, and any iframe. Pay special attention to LCP: if the main image loads too late, the optimization has become harmful.
Minification and code cleanup
CodeCanyon screenshots show a Minify tab with options for HTML minification, inline JavaScript minification, and comment cleanup. Minification can reduce response size, but its value depends on the theme, the cache layer, and any tools already in place. If the site already uses a separate cache plugin with minification, do not enable overlapping minification without testing. Two tools modifying the same HTML or JavaScript at the same time increase the risk of subtle errors.
For the first pass, it is better to enable cleanup that does not alter executable behavior and postpone script minification until a separate review. If the menu, carousel, form, or map stops working after minification is enabled, disable minification and check the browser console. In most cases, that kind of failure is easier to fix with an exclusion inside the cache plugin or by consolidating minification into a single tool than by forcing several optimizers to coexist.
Practical Example: Speeding Up a Brochure Site Without Breaking the Form
Let us walk through a concrete example. Imagine a WordPress agency site with a home page, a few service pages, a blog, a lead form built with Contact Form 7 or a similar plugin, analytics installed, and a CDN in front. There is no WooCommerce, no public registration, and comments are closed on the blog. The goal is to reduce unnecessary output, cut background load, and start tracking response time without breaking the form or analytics.
Goal
Get a cleaner front end and a reliable verification process. After configuration, the administrator should be able to see that unnecessary WordPress elements are disabled, the form still sends a test submission, the menu still works, SpeedFactor metrics are being collected, and each change can be rolled back individually.
Preparation
- Create a backup of the site or use a staging copy.
- Record baseline metrics for the home page, a service page, and the contact page.
- Check which external domains are actually used: analytics, CDN, fonts, map services.
- Make sure the administrator has fallback file access in case a conflict appears.
Configuration steps
- Open
Settings->Lighthouseand choose a gentle preset or enable only recommended options that do not affect the form. - In the cleanup section, enable emoji removal,
<head>cleanup, and embed disabling if the site's posts do not rely on embedding. - Disable comment cookies and comment scripts if comments are closed and the theme does not reuse that code for some other behavior.
- Slow down Heartbeat, then test the post editor and autosave afterward.
- In resource hints, add only domains that are genuinely used on key pages, such as the CDN or font domain.
- Enable SpeedFactor with a daily schedule and choose a chart range that makes comparison meaningful after changes.
- Open the contact page and submit a test request. If the form uses AJAX, verify not just the on-page confirmation message but also the email or entry created by the form.
- Clear page cache and CDN cache, then repeat the check in a private browser window.
Expected outcome and verification
After configuration, you should see less internal output in the page source, fewer unnecessary requests, stable form behavior, and the first SpeedFactor data once the checks start running. If the contact page stops submitting without a full reload, disable the most recent change related to scripts, minification, or REST/AJAX behavior. If icons disappear from the visual layout, check the Dashicons removal setting or related font handling.
Short takeaway: in this setup, Lighthouse does not "speed up everything." It helps remove specific unnecessary layers. Each setting ties back to an observable outcome: cleaner HTML, fewer background requests, a working form, and a SpeedFactor chart that shows what happens next.

How to Verify the Outcome After Each Settings Group
Outcome verification should be just as systematic as the configuration itself. One common admin mistake is to look only at a single overall score in a speed-testing service. Lighthouse changes several layers of the site, so the checks should also cover several layers: HTML, network requests, interface behavior, server timing, dynamic workflows, and error logs.
The public-facing site
Check the home page, one post, a page with a form, the search page, an archive page, and an important landing page. If the site includes a store, add a product page, cart, and checkout. Do not look only at load speed - look for failure signs too: the menu no longer expands, the form does not submit, the map is blank, icons are missing, the gallery does not open, editor block styles have changed, or the page redirects in an unexpected way.
Quick source-code check
Open the page source and look for the elements the setting was supposed to remove: emoji traces, RSD/WLW links, the generator tag, shortlinks, extra rel tags, embeds, or version parameters. If nothing changed, the enabled setting may not apply to that page, the result may be hidden by caching, or another plugin may be adding the same element back.
Network waterfall check
In developer tools, inspect the network tab. For resource-hint settings, confirm the presence of dns-prefetch or preconnect. For script cleanup, check whether the right files disappeared and whether any JavaScript errors appeared. For minification, make sure the files still load, do not return errors, and do not break execution order.
The admin area and editor
After changing Heartbeat, Zen mode, metaboxes, or editor blocks, always verify the admin area. Create a draft, wait for autosave, open the posts list, upload an image, and save a page. If the editor hangs, fails to save changes, or shows a warning about a newer post revision, roll back the settings related to Heartbeat and metaboxes.
Dynamic pages
Dynamic behavior matters more than a single score. The cart, account area, forms, search, filters, registration, and password reset should not be cached or cleaned up like a normal static page. If Lighthouse is used together with a cache plugin, exclusions for those pages are usually handled in the cache plugin, while Lighthouse settings should be checked for anything that may disable required scripts or API access.
| What to check | Normal outcome | Problem signal |
|---|---|---|
| Page source | Unnecessary internal elements are gone, but SEO markup and canonical links remain in place. | Important meta tags, canonical, or structured data from the SEO plugin are missing. |
| Forms | The message is submitted, the user sees confirmation, and an email or log entry is created. | The button does not respond, the AJAX request fails, or CAPTCHA validation does not pass. |
| Editor | The post saves correctly, and autosave works with acceptable delay. | REST errors appear, saving hangs, or blocks fail to refresh. |
| SpeedFactor | A trend appears, and data updates at the selected frequency. | No measurements appear, the chart is empty, or CRON is not running. |
| Object cache | The drop-in is active, the site opens normally, and statistics change over time. | White screen, PHP errors, or a conflict with another object-cache drop-in. |
Compatibility With Cache Plugins, CDNs, WooCommerce, and Page Builders
On most production sites, Lighthouse does not exist in isolation. It may sit alongside a page cache plugin, a CDN, Cloudflare, WooCommerce, Elementor, WPBakery, Contact Form 7, WPForms, Gravity Forms, Jetpack, or another important plugin. The CodeCanyon page claims compatibility with a broad set of popular tools, but practical verification is still necessary because a specific site may use a custom theme, nonstandard server-side caching, or extra scripts.
Working alongside a cache plugin
The best way to combine Lighthouse with a cache plugin is to split responsibilities. Let the cache plugin handle static page copies, exclusions, cache purging, script delay, and CDN integration if it supports those. Let Lighthouse handle cleanup of default WordPress behavior, object cache, measurements, selected headers, resource hints, and security features. Do not enable the same minification in both places.
If the cache plugin already minifies JavaScript and CSS, leave Lighthouse minification turned off until you run a separate test. If Lighthouse adds browser cache headers while the cache layer or CDN already sets headers, inspect the final server response. Duplicate or conflicting cache headers can be worse than leaving one optimization unused.
WooCommerce and dynamic sections
With WooCommerce, the main risk is optimizing pages that need to stay dynamic. The cart, checkout, customer account, cart fragments, and some AJAX requests all require caution. Even if Lighthouse is compatible with WooCommerce, a specific theme or payment module may still depend on scripts and REST/AJAX responses.
Test the store with its own workflow: add a product, change quantity, apply a coupon, go to checkout, select shipping, use a test payment method without a real transaction, verify the order email, and check the account area. If enabling cleanup or minification breaks one of those steps, roll back the most recent setting instead of disabling the entire plugin.
Page builders and visual blocks
Page builders often load styles, scripts, icon sets, media libraries, and AJAX-based editors. That is why settings such as removing mediaelement.js, Dashicons, block styles, embeds, lazy loading, or Heartbeat should be tested both in the editor and on the front end. Pay extra attention to pages with sliders, popups, tabs, forms, and animation.
If the problem appears only for a logged-in editor while the public site still works, look for a conflict in the admin area, Heartbeat, the REST API, or builder modes. If every visitor sees the issue, inspect minification, script cleanup, block styles, and caching.
Specialized Modes Worth Learning Separately
Lighthouse includes several areas that are easy to underestimate if you think of the product only as a bundle of performance checkboxes. They are not required on every site, but they are exactly what make the plugin more distinctive: recommendation labels next to settings, Query Tracker, Tips & Tricks, registration filtering, wp-config.php controls, and Volt for multi-site oversight. These modes should not be enabled just to say they are enabled. They are better treated as separate working tools for specific situations.
Query Tracker as a way to see the source of load
Product screenshots show a dedicated Query Tracker tab. That kind of section is useful not for visitors, but for an administrator or developer trying to understand which queries and actions are weighing down a page. If a site slowed down after installing a new plugin, switching themes, or adding a complex block, a single overall speed score is not enough. You need to see whether database activity changed and which queries are repeating more often than expected.
A practical approach is this: first identify the problematic page, then open it several times under the same conditions, then look not for one suspicious query but for a repeating pattern. If one plugin generates many similar queries, that does not automatically mean it has to be removed. Sometimes it is enough to disable a specific widget, remove a block from the page, change an output setting, or enable object cache. If the queries are tied to WooCommerce, account pages, or catalog filters, do not draw conclusions until dynamic pages have been tested.
Tips & Tricks as a reference, not a mandatory command list
The Lighthouse documentation mentions a Tips & Tricks tab with technical recommendations, including static robots.txt and favicon.ico files, server software checks, database encoding, WordPress memory, and other measures. This is an important section, but it should not be treated as a universal "turn everything on and rewrite everything" plan. Some advice belongs to hosting, some to site structure, and some to WordPress settings that are best changed only after a backup is in place.
For example, a static robots.txt can reduce unnecessary WordPress initialization on bot requests, but if an SEO plugin manages a virtual robots.txt and the site regularly changes its indexing rules, you first need to understand which system should own that file. The same applies to favicon.ico: if browsers keep requesting a file that does not exist, adding a real static file helps. But that is not a feature to hunt for in Lighthouse as if it were a magic speed boost. It is a small technical cleanup task that the plugin helps bring to your attention.
wp-config.php changes and where responsibility shifts
The developer changelog mentions features for managing specific wp-config.php constants, including CRON lock, alternate CRON, file editor control, and skipping bundled themes. These settings are closer to WordPress administration than ordinary interface-level configuration. They can be useful, but they require a clear understanding of their consequences.
Disabling the file editor in the admin area, for example, is often seen as a sensible safeguard against accidental changes and some abuse paths. But if an administrator is used to editing files through the built-in editor, they will see that familiar menu item disappear after enabling it. That is not a bug - it is the expected outcome. The team should understand in advance that file changes are now supposed to happen through a repository, a child theme, SFTP, or another controlled path.
CRON requires even more caution. If the site's standard WordPress CRON is disabled and replaced with a server-side scheduler, Lighthouse and any other plugin expecting background tasks still need to receive scheduled execution. Otherwise, SpeedFactor, cache cleanup, reports, emails, and scheduled actions may stop updating. So verify any CRON-related setting by behavior rather than by checkbox: did the task run, did the data update, and does the log stay clean?
Volt for multiple sites
In the Lighthouse description, Volt is presented as a multi-site management module. It is most relevant for agencies and administrators responsible for several WordPress projects. The practical value of a module like this is not in replacing a full DevOps system, but in making it easier to see site status, updates, errors, and signals from outside services such as Cloudflare.
If you manage only one site, Volt may be unnecessary. If you manage several, use it only after the core Lighthouse configuration has been stabilized. First tune one reference site: cleanup, security, SpeedFactor, object cache, and verification. Then connect the others and compare them not just by overall status, but by project type. A store, a blog, and a brochure site should not receive the same configuration even if they belong to the same administrator.
Main takeaway on advanced modes: Query Tracker helps identify the source of load, Tips & Tricks points to technical improvements,
wp-config.phpchanges require backup access, and Volt is useful only when you are truly managing multiple sites.
How to Build Your Own Lighthouse Settings Profile
There is no universal profile that fits every site. But you can build your own profile in a way that is easy for the team to understand and easy to verify after updates. That profile has four parts: site type, enabled Lighthouse groups, a list of exclusions, and verification checks. If you document it in the project itself, the next administrator will not have to guess why one setting is enabled and another is turned off.
Profile for a brochure site
For a brochure site, the usual priorities are a fast home page, clean HTML, a reliable lead form, and a stable editor. In that context, you can be more comfortable disabling comments, embeds, extra <head> elements, author archives, Dashicons for guests, and some background processes. But even on a simple project, the form remains critical. If it depends on AJAX, CAPTCHA, or the REST API, it should get a dedicated test after every change.
In the profile, document not only which settings are enabled but why. For example: "comment cleanup is enabled because comments are closed on all post types"; "Dashicons are removed for guests because the theme does not use them on the front end"; "Heartbeat is reduced because editors work one at a time." Notes like that prevent pointless arguments months later when the site has evolved.
Profile for a blog or media site
A blog comes with different risks. It may rely on author archives, comments, embedded content, RSS, and active editorial work. So disabling author archives, RSS links, comment cookies, or embeds should happen only after you understand the editorial model. If author pages bring in search traffic or serve as expert profile pages, disabling them may damage the site structure. If comments are active, overly aggressive cleanup can make the user experience worse.
For that kind of site, it is more sensible to start with emoji cleanup, internal tag cleanup, Heartbeat control, and SpeedFactor. Then review media separately, because images in articles often affect speed more than many smaller HTML optimizations. If the editorial team updates content frequently, overly aggressive background-process throttling in the admin area can interfere with autosave.
Profile for WooCommerce
For a store, the profile should be the most conservative. Every optimization should be judged against the customer journey. Enable cleanup - then test the product page. Change minification - then test variations, the cart, and checkout. Enable CAPTCHA or login protection - then test the customer account and password reset. Turn on object cache - then test inventory updates, the cart, and user data refresh.
Some Lighthouse features are very helpful in a store: SpeedFactor helps surface regressions, object cache can reduce repeated queries, security modules protect login, and cleanup removes unnecessary WordPress output where it is not needed. But a store almost always needs exclusions. Do not optimize checkout like a static page, and do not disable WooCommerce scripts if the cart depends on them.
Profile for an agency
An agency usually needs several profiles rather than one. For example: "brochure site," "blog," "store," "registration-based site," and "page-builder site." Each profile should include baseline Lighthouse settings, a list of options that should be enabled only after testing, and a set of checkpoint pages. Volt and SpeedFactor help provide visibility across a portfolio of sites, but the decision to enable features still has to be made based on project type.
This approach lowers the risk of mechanical configuration. A client site does not receive the "fastest" profile if it breaks the lead form. A store does not get blog settings. A registration-based site does not get a filter that blocks legitimate users. Lighthouse becomes part of the maintenance process rather than a one-time experiment.
Safe Enhancements and Practical Techniques
Lighthouse includes its own settings and a documented filter for the outcome of registration spam checks. That means safe customization should be done through standard WordPress mechanisms rather than by editing plugin files: a child theme, a small standalone plugin, or Code Snippets. If the exact hook is not confirmed by the documentation, it should not be invented. In this guide, we use only one example based on the published lighthouse_spam_check_result filter.
A lightweight log for registration-check outcomes
The goal is simple: when Lighthouse evaluates a registration attempt as suspicious or clean, write a short line to the WordPress debug log. This is useful on a staging copy of the site when you want to understand which filtering layer is firing, without sending unnecessary emails to the administrator or exposing data to the visitor. Before using it, enable debug logging on a test site and verify your personal data handling policy.
add_filter( 'lighthouse_spam_check_result', 'site_log_lighthouse_registration_check', 10, 4 );

function site_log_lighthouse_registration_check( $is_spam, $username, $email, $method ) {
    if ( defined( 'WP_DEBUG_LOG' ) && WP_DEBUG_LOG ) {
        $status = $is_spam ? 'spam' : 'clean';
        error_log(
            sprintf(
                'Lighthouse registration check: status=%s method=%s user=%s email_domain=%s',
                $status,
                sanitize_key( $method ),
                sanitize_user( $username, true ),
                substr( strrchr( sanitize_email( $email ), '@' ), 1 )
            )
        );
    }

    return $is_spam;
}
The code does not change Lighthouse's decision. It only writes a diagnostic line if WP_DEBUG_LOG is enabled. Put it in Code Snippets or a small site-specific plugin, not in Lighthouse files and not in WordPress core. Once testing is complete, remove or disable the snippet so the log does not grow unnecessarily.
A practical setup with cache and CDN
If the site uses a CDN, divide responsibilities clearly: the CDN serves static files closer to the user, the cache plugin manages pages and dynamic exclusions, Lighthouse removes unnecessary WordPress output, configures browser hints, and collects its own metrics. A sensible setup order is this: first page cache and dynamic exclusions, then Lighthouse cleanup, then resource hints, then CDN headers, then SpeedFactor verification and a browser-based test.
If a conflict appears, roll back in reverse order: first resource hints and minification, then questionable cleanup settings, then the cache layer, then the CDN. That sequence helps preserve a working configuration instead of losing it because of one aggressive setting.
Troubleshooting Common Problems
Problems after performance tuning almost always look the same: "something got faster, but one important part of the site broke." The difference is where you look for the cause. Lighthouse changes several layers, so troubleshooting has to be based on symptoms, not on the assumption that the entire plugin is to blame.
The page loads visually, but the menu, form, or slider no longer works
Symptom: the HTML and styles are there, but an interactive element does not respond. A likely cause is minification, removal of a required script, a conflict with lazy loading, or a cache plugin. Check the browser console, disable the latest minification or script-cleanup setting, then clear cache and test again.
If the issue disappears, do not enable that option globally. Look for a targeted exclusion in the cache plugin, or keep minification in a single tool. If the issue remains, check the theme and any third-party plugin, because the failure may simply have coincided with an update.
The form does not submit or CAPTCHA validation fails
Symptom: the user clicks the button, but no submission is created, a validation error appears, or the request hangs. The cause may involve REST/AJAX behavior, caching on the form page, Turnstile, another CAPTCHA plugin, or a JavaScript conflict. Start by excluding the form page from page cache, then make sure two CAPTCHA mechanisms are not enabled at the same time.
If Turnstile is in use, confirm that the keys belong to the correct domain, the form is not being served from stale cache, and the server-side token validation succeeds. If password reset or admin login is blocked, use fallback access and temporarily disable the CAPTCHA module.
An external integration stops working after XML-RPC is disabled
Symptom: the mobile app, Jetpack, remote publishing, or an older external service can no longer connect. The likely reason is that the integration genuinely depends on XML-RPC. Turn the setting back on and check whether the service offers a modern REST-based connection method. If there is no alternative, leave XML-RPC enabled and strengthen login protection in other ways.
SpeedFactor is not showing new data
Symptom: the monitoring tab is empty, the chart does not refresh, or the data is stale. Check whether the module itself is enabled, whether a schedule frequency is selected, whether WordPress CRON is running, whether the server allows outgoing requests, and whether the required background tasks are active. If CRON is disabled on the site and handled by a server-side scheduler, make sure that scheduler is actually firing.
Object cache causes errors or stale-looking data
Symptom: some data stops updating, another cache layer reports a conflict, the site throws an error, or the admin area becomes unstable. Check whether another object-cache.php exists, whether SQLite3 is available, and whether there is enough write permission and disk space. Remove the drop-in normally through the Cache tab, clear all caches, and test again.
Icons disappear or the front end looks different
Symptom: the text and layout are intact, but icons turn into squares, buttons change appearance, or the media player stops rendering. The cause is often tied to removing Dashicons, mediaelement.js, block styles, or theme styles. Disable the most recent option from the Theme Tweaks or Media & Storage group and check the page again in a private window after clearing cache.
The admin area becomes worse at saving posts
Symptom: the editor takes a long time to save a post, autosave behaves unpredictably, or a post revision conflict appears. Check Heartbeat settings and REST API restrictions. If several editors work on the site, do not make Heartbeat too infrequent. For an editorial team, stable saving matters more than a small reduction in background load.
Questions About Setup and Limitations
Can I enable all recommended settings at once?
On a staging copy, you can try that if you are prepared to roll changes back quickly. On a live site, it is better to enable settings in groups. Even a recommended option may not fit a particular theme, form, or integration.
Does Lighthouse replace a standard cache plugin?
Not always. Lighthouse includes cache-related features and object cache, but page caching, dynamic URL exclusions, CDN integration, and advanced file optimization are often easier to manage in a dedicated cache plugin. The best setup depends on the site and on which functions are already in place.
Do I need Redis or Memcached for Lighthouse object cache?
For the SQLite3 object cache described by the developer, a separate Redis or Memcached server is not required. But on sites that already use Redis successfully, there is no reason to change a working architecture without a clear need and proper testing.
Why did the overall PageSpeed score not improve after optimization?
Lighthouse can reduce unnecessary output and overhead, but the overall score also depends on images, fonts, JavaScript, server response, main content, third-party scripts, and theme behavior. If the main bottleneck is a heavy hero image, WordPress cleanup alone will not solve the issue completely.
Can I use the plugin with WooCommerce?
The product page claims WooCommerce compatibility, but a store still requires its own test cycle. Check the cart, checkout, account area, emails, and payment workflow. Do not apply aggressive minification or API disabling without verification.
What should I do if login protection blocks the administrator?
Use fallback file or hosting access, temporarily disable the problematic module, and then reconfigure the protection more gently. Before enabling CAPTCHA or brute-force protection, always test login in a separate browser while the current admin session is still open.
Is Lighthouse suitable for beginners?
Yes, if they start with presets and do not enable everything at once. But the most benefit comes to a user who is willing to verify outcomes and understand which WordPress feature is being disabled. For a completely non-technical site owner, it is better to work together with an administrator or developer.
When CodeCanyon Lighthouse Is a Strong Choice
Lighthouse is worth using if you need more than caching - if you want a controlled technical cleanup of WordPress: removing unnecessary output, managing background load, checking response time, using object cache without a separate Redis server, adding basic login hardening, and protecting registration. It is especially well suited to sites where the administrator wants to see the consequences of each action instead of just clicking a generic "speed up" button.
If the site is complex, start with a copy, a gentle preset, and one settings group at a time. If the site is simple, do not enable features that do not solve your problem. If you already have a strong cache plugin, split responsibilities and avoid duplication. If public registration is active, watch for false positives. If you enable object cache, prepare the rollback path in advance.
Once the configuration is in place, critical pages have been tested, and the limits are understood, you can download the CodeCanyon Lighthouse archive and move on to testing it on your own site. The key is to treat it as a technical tool rather than a marketing speed button - that is how it delivers more value and fewer unexpected conflicts.

