


CodeCanyon File Manager - WordPress Plugin
The file manager plugin for WordPress is a vital tool that simplifies the management of files and folders within a WordPress site efficiently. With streamlined file organization and intuitive features, it enhances the user experience for website administrators. This plugin allows for seamless file uploading, downloading, editing, and deleting directly from the WordPress admin dashboard, offering convenience and practicality for users. Its user-friendly interface and robust functionality make file management a breeze, saving time and effort when handling various files on a website.
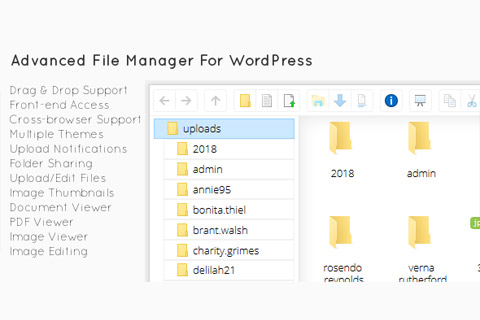
Plugin Features
Enhancing the websites workflow, the plugin streamlines the process of file handling by providing a centralized location for all files, ensuring easy access and efficient management. From images to documents, this plugin supports a wide range of file types, catering to diverse content needs on WordPress websites. Its versatile capabilities empower users to organize files systematically, fostering a structured and methodical approach to content management. By enabling quick search and retrieval options, it boosts productivity and enhances the overall efficiency of handling files within a WordPress environment.
Furthermore, the plugin offers advanced file security features that safeguard sensitive data and prevent unauthorized access, ensuring the protection of valuable content. With customizable permissions and access controls, users can regulate who can view, edit, and download files, enhancing the security posture of the website. Additionally, CodeCanyon File Manager backup and restore functionalities provide peace of mind by offering solutions for file recovery in case of accidental deletion or data loss. This adds an extra layer of protection and reliability to the file management process, contributing to a robust and secure content management system.
Moreover, the file manager plugin integrates seamlessly with various third-party applications and services, expanding its functionality and compatibility with external tools. This interoperability allows for easy file sharing, collaboration, and integration with other platforms, enhancing the plugins versatility and utility. Whether its linking cloud storage services or syncing files with external databases, the plugin facilitates a connected ecosystem for efficient file management and content distribution. Its extensibility and integration capabilities make it a valuable asset for WordPress users looking to optimize their file handling workflows effectively.
In conclusion, the file manager plugin for WordPress elevates the file management experience by providing a comprehensive set of tools and features to streamline the handling of files within a WordPress site. From enhanced organization and security to seamless integration and accessibility, the plugin offers a robust solution for managing files efficiently and effectively. With its user-friendly interface, advanced functionalities, and versatility, this plugin is a valuable addition to any WordPress website, empowering users to optimize their file management processes and enhance overall productivity.
Specifications:
| Release date: | 13-07-2012 | |
| Last updated: | 20-10-2021 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Administration | |
| Compatibility: | W5.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | CodeCanyon | |
| Rating: | ||
Share with your friends!
A Practical Guide to CodeCanyon File Manager for WordPress
This guide to CodeCanyon File Manager will help you understand file access boundaries, prepare a safer environment, configure user permissions, and test a public-facing workflow without taking unnecessary risks. It walks through the process from installation and initial checks to granting limited access, working with user folders, validating the outcome, and diagnosing issues that are especially important for a tool that can read, upload, and modify site files.
This plugin has an unusual role. It is not simply a tool for organizing the WordPress Media Library, nor is it a standard document-upload block. According to its product page, CodeCanyon File Manager provides an Explorer-style file interface for browsing, creating, and editing WordPress files and folders. It supports context menus, drag and drop, archives, a text editor, previews for different file types, and displaying the file manager on the public-facing part of a site for authorized users. That means a sound setup does not begin with the Upload button. It begins with a more important question: who needs access, which area should they access, and which operations do they actually need?
That distinction shapes the entire approach. A content manager who needs to send a PDF to a client usually does not need to see the theme structure, plugin folders, or configuration files. A developer may need to quickly inspect a text file, but that does not make public access safe for every registered visitor. A site owner may need to create a private document exchange area for several employees, while an agency may want to assign each client a separate uploads folder. Each case carries a different level of risk and requires its own permission model.
The product page classifies the product as a WordPress extension and describes it as an extension built on the open-source elFinder file manager with additional WordPress capabilities. It also lists user roles, read and write permissions, folder assignments, automatic folder creation for users, folder uploads, archive creation, image and file editing, and public display through a shortcode. These features are useful, but they do not mean every option should be enabled at once. This guide follows the principle of least-privilege access: start with a separate test account and one folder, allow only the necessary operation, and expand the workflow only after it has been verified.

Define the boundaries first: what should the file manager actually accomplish?
Before installing anything, define the expected outcome rather than a feature name. Saying "give users access to files" is too vague. A better statement would be: "the project manager uploads layouts to a separate folder; project members can see only that folder's contents and download PDFs, but cannot rename or delete documents." That wording immediately tells you that you need a separate area, a limited role, an operation checklist, and testing from a member account.
A second common use case is administrative work in the WordPress dashboard, where someone needs a convenient way to browse the uploads folder, create a ZIP archive, or replace an image. In that case, public display may not be needed at all. A third use case is personal folders: after registration, each user receives their own folder and exchanges files with the site within it. The product page mentions automatic folder creation for all users and configurable user folders. That can be a useful starting point for a private exchange area, but the folder boundary and the actual access checks should be confirmed on a site copy, not assumed from the name of a setting.
Three access models you should not mix together
The administrative model is appropriate for the site owner, a technical specialist, or a small number of trusted staff members. The tool remains in the dashboard, no public-facing access is published, and all file operations are treated as technical work: create a backup first, perform the action, then check the site. This is the most predictable option when the task is simply to replace an asset, find a log, or package a set of files.
The private user model is intended for member areas, courses, contractor collaboration, or document exchange. The user does not see the server as a whole, but only the area assigned to them. If the plugin interface provides rules for roles, folders, and permissions, build them around one user group and one test directory. Do not immediately move existing subscribers or customers into an access-enabled group. WordPress separates roles and capabilities, and the default Subscriber role has minimal permissions. That is a useful baseline: file access should be an explicit decision, not an accidental side effect of registration.
A public document library can resemble a file manager, but it often requires a different tool. If visitors only need to see a list of guides and download publicly available files, it is usually better to publish selected files through the Media Library, a downloads catalog, or a page of links. A full Explorer-style interface with the ability to create, edit, copy, and delete files is excessive for that purpose. CodeCanyon File Manager makes sense on the public side of a site only when you can clearly name the authenticated group, its folder, and the list of allowed operations.
A question to answer before proceeding: if a user gains access to the wrong folder, what exactly could they see, download, change, or delete? Until you can answer that in one sentence, your access rules are not ready to publish.
Who the plugin suits, and when a different approach is better
The plugin is appropriate for a WordPress administrator who needs a file interface without constantly switching to an SFTP client; for a team that needs files organized into personal or project folders; and for a private portal where a simple upload form is not enough. It can be convenient when users need to work with images, text files, archives, or previews of supported materials in one place. Context menus, list and icon views, drag and drop, and archiving can reduce routine work, but they do not replace access control.
It is less suitable for an open file catalog without accounts, for storing genuinely sensitive data, for collaborative document editing with version history, or for teams that require strict enterprise audit logs, external storage, and formal change approval. It should not be used as a way to edit WordPress core files, themes, or plugins on a live site either: any PHP change made through a web interface is harder to validate, roll back, and hand off to another specialist. For that kind of work, the normal workflow remains a local copy, version control, and a secured deployment channel.
There is also an important caveat about currency. The available CodeCanyon product page lists compatibility through the WordPress 6.0.x branch and indicates that the product was last updated some time ago. That does not prove the plugin will fail on a newer site, but it is not a basis for promising current compatibility either. Before deploying it on a live site, check the age of the archive and the author's recent responses, make a backup, create a site clone, and run a dedicated test on your own combination of WordPress, PHP, theme, and plugins.
Prepare the site: backup, roles, and a test entry point
A file manager should be installed with the same caution as any extension capable of changing site content. The most unpleasant failure with tools in this category is not a nicely formatted error message. It is an unnoticed extra permission: a user can see someone else's folder, upload an inappropriate file type, or gain the ability to delete material they should never have seen. Prepare the environment and document the starting state before unpacking the archive.
Begin with a backup that can restore both files and the database. Files matter because the manager works with them directly; the database matters because WordPress and plugins store settings, roles, pages, and media relationships there. The backup should not simply be something your hosting provider created at some point in the past. It must be available for restoration. On a site copy, test at least one small restore or ask the provider for the exact procedure. Do not treat a ZIP archive on the live server as your only fallback: if server access has already been compromised, that archive may not help.
Next, make a small map of which file categories are involved in the workflow and who needs them. For example, wp-content/uploads/client-files/ may be the working area for client documents; public blog images remain in the standard Media Library; plugin and theme directories are not part of the user workflow at all. You do not have to create physical folders in advance if the selected plugin mode creates them automatically. What matters is deciding ahead of time which area is considered the working area, so you do not grant access to the site root merely because it makes every file easier to see.
Check the WordPress and hosting environment
On the test copy, sign in as an administrator and record the active plugins, PHP version, theme, caching setup, and the method WordPress uses to write files. This is not bureaucracy. WordPress can access the filesystem through different methods, and on some hosts the web server owns files differently from the SFTP user. The official WordPress documentation describes the Filesystem API as a mechanism designed to account for these differences. If installation or dashboard uploads request server credentials, do not try to solve the problem by randomly changing file permissions. First ask your host how file ownership and writing to wp-content are configured.
It helps to separate two things that are often confused. A WordPress user's permissions determine whether they can open a page or perform an action in the interface. Filesystem permissions determine whether the server is allowed to create, modify, or delete a particular file. A problem in one layer is not fixed by carelessly weakening the other. If a user sees an Upload button but the file is not created, first check the server log, path, file size, and file type, then inspect directory access rules. If the file is created but visible to the wrong user, that is a plugin configuration and role issue, not a reason to make the directory more accessible to the web server.
In a standard secure WordPress setup, core directories including wp-admin and wp-includes should not be working areas for routine changes. WordPress security guidance recommends limiting write access as much as possible and allowing it only where genuinely needed, such as within wp-content. For file-exchange work, this is a useful guideline: create a separate data area instead of allowing changes to every folder the web-server process can see.
Prepare roles before configuring the plugin
Do not tie access to convenient role names without verifying them. In WordPress, a role is a set of capabilities, not a guarantee that a particular third-party extension interprets it in exactly the same way. In a single-site installation, an administrator usually has broad permissions; Editor, Author, and Subscriber roles are significantly more limited. For a private file workflow, it is often better to create a dedicated role with a trusted role-management tool or assign pre-approved rules to a small group directly within File Manager than to use the familiar Editor role simply because it already exists.
A minimal test set consists of three accounts:
- Administrator, who configures the plugin and can see administrative sections.
- Test participant, who is permitted to perform only the required action, such as uploading to and viewing their own folder.
- Control user, who is outside the group and must be denied access.
Do not use your main account for these checks: an administrator browser session can easily create the false impression that a public page is available to everyone. After each change, clear the session, open an incognito window, or sign in with the test account. Then repeat the check using the control account. The third account is what shows whether the restriction actually works, rather than merely proving that the interface exists.
Operations checklist for the first launch
During the first pass, allow no more than one or two operations. For document exchange, viewing and uploading are usually enough, and downloading may be needed as well. Add folder creation, renaming, deletion, archive extraction, text editing, and image editing later and one at a time. Even if the product page lists archive creation, copying, pasting, and editing as available features, that does not make them necessary for every workflow. The shorter the action list for a test user, the easier it is to spot an imprecise rule.
Define the allowed file types and size limits separately. If employees exchange PDFs, images, and office documents, there is no reason to allow uploads of everything the server accepts. WordPress may impose one set of limits, hosting may impose another, and the file manager may impose a third. Write down the expected behavior: an allowed file uploads and is visible only in the assigned area; a prohibited file receives a clear rejection; a large file does not leave behind a partially created object. This turns installation into a testable workflow rather than a collection of switches.
Required step: before enabling public display, verify that a standard user cannot open the manager page through a direct URL after signing out. A hidden menu or an unpublished link is not a substitute for permission checks.
Install the archive and run the first safe check
Once the test environment is ready, use the standard WordPress path: in the dashboard, open Plugins > Add New, select Upload Plugin, choose the ZIP archive you received, complete the installation, and click Activate Plugin. This sequence follows the official WordPress instructions for installing plugins from ZIP archives. Do not manually unpack the archive over an active directory unless there is a specific technical reason to do so: if something goes wrong, it is easier to identify what was installed and disable the extension through the standard plugins list.
Immediately after activation, do not publish the shortcode or move real users into the new rules. First locate the File Manager item in the dashboard, open it as an administrator, and perform a harmless check: navigate to the preselected test directory, create a small text file inside it with a neutral name, view it, and then delete it. If that does not work, do not weaken permissions across the entire site. Check the path, directory ownership, hosting restrictions, and log messages.
If the basic check succeeds, try uploading one safe file of a known size, then download it again and compare the size and contents. For an image, also test the preview; for a text file, open it without saving. The product page lists file-type icons, image thumbnails, and previews for a range of formats, but actual support depends on the environment and version. Do not promise your team that every office document will open in the browser: test the exact set of formats you need first.
After the first test, make a brief record: which path worked, which account was used, what is permitted, and what remains disabled. This log will be useful during updates and will help distinguish a plugin problem from a later server-side change. You can now move from safe installation to configuring folder and role boundaries.
Configure folders and roles: turn a general file browser into a limited working area
The most useful part of CodeCanyon File Manager is not its list of buttons, but its ability to connect a user, a role, and a folder. The product page lists read and write permissions for different users, folder-level access assignments, denial of access to selected users, custom roles, and automatic folder creation. These features can support several ways of working, but only if they are configured in the right order: first the path, then the access rule, then the allowed operations, and finally testing under every role.
Open the plugin settings screen and do not enable every available toggle. The interface and exact tab names may vary between archives, so look for conceptual groups instead: general access, user or role rules, default directory, folder depth, read/write permissions, toolbar items, and context-menu items. If an option has a different name, match it to your workflow rather than to an expected label from an old review. Be especially careful with settings that define the visible root, allow recursive browsing, or create folders automatically.

Start with a separate directory, not the WordPress root
Technically, a file manager is valuable because it can work with the WordPress folder tree. In practical terms, that also makes it easy to grant access that is too broad. A good starting path is inside a prepared content area, not at the level of /, wp-admin, wp-includes, the active theme directory, or installed plugin directories. For file exchange, it is usually more reasonable to choose a child directory within wp-content/uploads, such as wp-content/uploads/client-files or wp-content/uploads/private-work, if that structure fits your site's policies and hosting setup.
Choosing a separate area provides four advantages. First, it is easier for users to understand where they are, and they are less likely to accidentally affect administrative files. Second, auditing becomes more manageable: you inspect one branch of the tree rather than the entire server. Third, backups and cleanup of the working area do not become mixed with theme code. Fourth, site migrations are easier to control because the source of user files is clear. However, a path inside uploads does not make files private automatically. URL access, web-server rules, and plugin checks may behave differently, so do not store data requiring strict protection in such a folder until you have tested the actual behavior in a browser and without authentication.
One folder, one workflow owner
For the first working launch, avoid a complex hierarchy. Create one directory, such as project-alpha, and one test group. Put two objects inside it: a document the user is allowed to see and a test file that can later be deleted. Do not immediately create folders for dozens of existing users. Automatic folder creation, listed among the product features, becomes useful only after you have proven that folder names are generated as expected, users do not land in someone else's area, and revoking access does not leave a visible link to old content.
The product author has a separate FAQ about changing the location of the folder created for each user. It suggests editing a plugin file. That is a historical indication that the folder path could be changed, but it is poor practice for an active site: an edit to the extension file will be overwritten during an update, complicate troubleshooting, and may not match your archive. If the current settings screen does not provide the folder structure you need, it is safer to keep the workflow in a separate prepared folder, use another tool for isolation, or ask the author for a current supported method. Do not change plugin source code merely for cosmetic folder placement.
Separate visibility, reading, and modification
Permissions are often incorrectly reduced to two states: "has access" and "does not have access." That is not enough for a file workflow. A user may be able to see a file name, open content, download a file, upload a new file, create a folder, rename an object, replace an existing item, delete material, extract an archive, or edit text. The File Manager product page separately mentions read/upload access, toolbar and context-menu configuration, archives, and text editing. Treat each action as an independent permission whenever your version allows you to restrict it.
For most working portals, a good initial set of permissions is: see the assigned directory, view the list, upload approved documents, and download them again. Leave text-file editing, archive creation, and deletion to administrators. This policy does not prevent users from completing their tasks, but it preserves more control over mistakes. If someone genuinely needs to replace a document, use a clear naming rule instead, such as uploading a new version with a date in the name, while an administrator removes the previous version after review.
| Operation | Test participant | Administrator | Why |
|---|---|---|---|
| View assigned folder | Allow | Allow | The workflow cannot begin without this. |
| Upload approved file types | Allow after testing | Allow | Needed for exchange, but requires format and size limits. |
| Download | Allow when needed | Allow | Confirm that the file opens only according to the workflow rules. |
| Create and rename folders | Do not enable during the first launch | Allow when required | Can easily disrupt a previously understandable structure. |
| Delete, archive, edit text | Do not enable | Only when required | These actions carry a high risk of accidental loss or modification. |
The table does not replace plugin settings, but it helps prevent a common mistake: granting write permissions and discovering that unnecessary menu items became available along with them. After saving the rules, sign in again with the test account and literally walk through every operation. If a button is visible but the action is denied, that is better than silent access, but it still requires a clear explanation for the user. If a deletion control is visible and works, return to the menu or role-permission configuration rather than hoping the user will "just not click it."
How to test automatic user folders
If your product instance offers to automatically create a directory for each user, test it first with a new account. Record the username, create the account, open File Manager as that user, and check whether the expected folder appears, whether it is empty, which path is displayed, and whether the user can navigate up a level or open a neighboring user's address. Then create a second test user and repeat the test in reverse order. It is important to verify not only that "each user sees their own folder," but also that "the first user cannot see the second one after it is created."
Do not treat the visual absence of a folder in the tree as the only form of isolation. Try manually changing the page address, opening a previously copied link, and requesting a file in a separate unauthenticated session. If the link remains accessible, the workflow cannot be called private. In that case, remove the public page, limit the work to the dashboard, or choose a specialized solution that documents how it protects file delivery. Display configuration and file protection are different tasks.
Configuration checkpoint: at this stage, you should have one clearly defined working folder, one test user with minimal operations, and one control user without access. Only after this three-account test succeeds should you expand roles or enable automatic folder creation.
The public-facing site: when a shortcode is justified and how to avoid exposing too much
The CodeCanyon page states that an administrator can display the file manager on the public-facing part of a site using a shortcode and that the interface is visible only to users with permission. This capability can be useful for a private portal, but it also requires the most rigorous testing. In the dashboard, the user has already passed WordPress authentication and expects a technical interface. A standard site page exists in a different context: it may be opened by guests, search crawlers, caching systems, users with stale sessions, and people who saved a direct link.
For that reason, do not search online for a shortcode and paste one in at random. Open the documentation included with your archive or the official documentation section, identify the exact shortcode format for your version, and first place it on an unpublished draft page. Do not add the page to a menu, link it from a profile, or place it in a page builder until testing is complete. The exact name, parameters, and available attributes may depend on the product version, and an invented shortcode may simply fail or conceal the real cause of an issue.
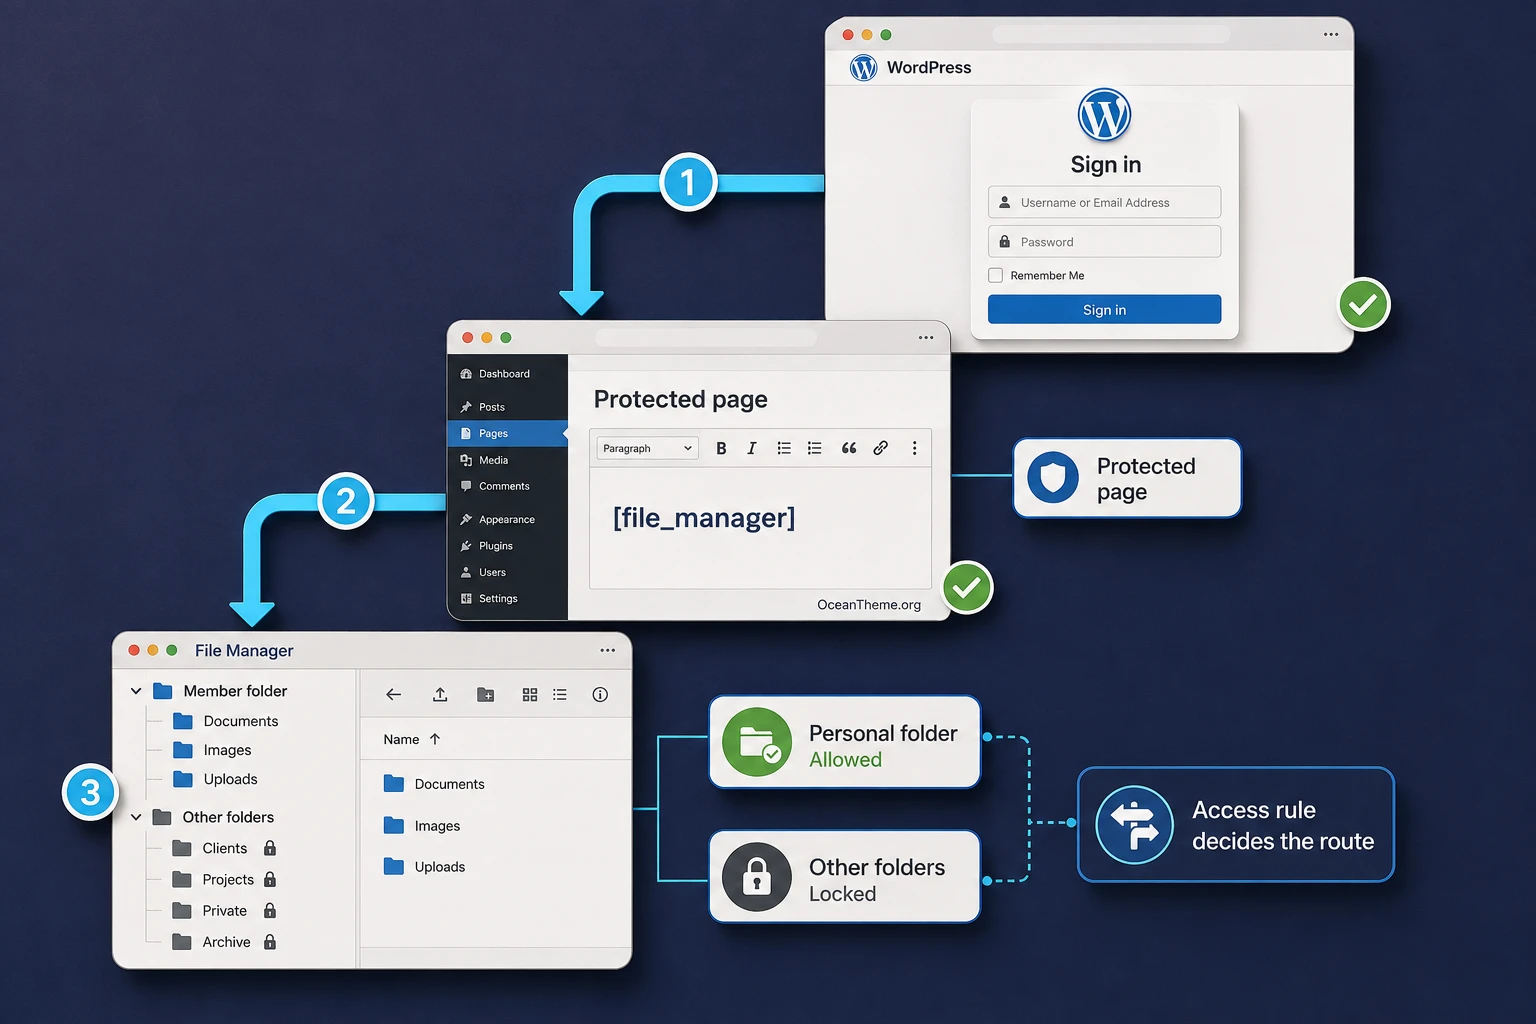
Build the page as a private working screen
A page containing the manager should have a clear purpose. A title such as "Project Files" tells the user where they are; a short note below the heading explains which materials can be uploaded, which formats are allowed, and whom to contact if a document does not appear. If the site uses a member-area system, add a link to this screen only within authenticated-user navigation. If it does not, do not hide the problem behind a direct URL: first establish a standard login requirement and role validation.
Let the page show only the interface and a brief action guide. Do not place contact forms, marketing blocks, or large banners next to it, as they make testing more difficult. A working screen is best experienced as a separate workspace: the user sees the assigned folder, permitted operations, and upload outcome. If file support is needed only after an order or project assignment, use the site's existing access mechanism as the primary barrier, with File Manager settings acting as a second boundary inside the file area.
Test four sessions
After inserting the exact shortcode, perform four checks rather than one. First, sign in as an administrator and confirm that the page renders without errors. Second, sign in as the test participant and confirm that they see exactly the required folder. Third, sign in as the control user who was not granted permission and confirm that the manager does not show a tree or provide access through a button or direct URL. Fourth, sign out of WordPress, clear the site's cookies, or use a private window. A guest must not receive the file interface, object list, or working links to private materials.
Record the outcome of every test. For example: "the participant sees project-alpha and can upload a PDF; the control user receives a denial; the guest is redirected to sign in." This is more useful than the abstract statement "access is configured," because it lets you repeat the check after a plugin update, caching change, or role change. If even one test produces an unexpected outcome, keep the page as a draft or temporarily remove the shortcode and return to the access rules.
Caching, indexing, and direct file links
A member-area page should generally not receive shared caching intended for anonymous visitors. If page caching is enabled on the site, find its exclusion rule for the private member-area URL or disable caching for this page using the normal method provided by your solution. After making the change, run all four checks again: caching can show an authenticated user an old page or, more dangerously, return a cached version to the next visitor. You do not need to disable caching throughout the site; the goal is to exclude one protected route and verify its behavior.
Do not treat the file screen as a standard indexable landing page. Do not link to it from an open menu, sitemap, or public article. Depending on the theme, SEO settings, and login system you use, you may be able to prevent indexing through the standard configuration for that page, but that is only an additional measure. Being absent from search results is not access control: actual protection must remain at the authentication and file-manager-rule levels.
A separate check is needed for the direct URL of an uploaded file. Sign in as a participant, find a way to open or download the file, copy its address, and try opening it as a guest. Then test the address under the control account. The behavior depends on the storage location, server configuration, and the extension's own mechanics, so there is no universal promise to make here. If the file still opens freely through a direct link, do not place contracts, personal information, backups, or other confidential materials there. Limit the workflow to non-sensitive documents or use a specialized protected-delivery system.
What to enable in the interface and what to leave disabled
The product features include a context menu, toolbar, drag and drop, file and folder creation, copying, pasting, archiving, image editing, and text editing. A convenient interface does not need to be the same for every role. For an employee who only adds work output, the primary actions are selecting a folder, uploading, and confirming the file name. A technical administrator may benefit from search, preview, ZIP archive creation, and an editor. If the settings screen allows individual toolbar or context-menu items to be disabled, use that not as decoration but as an implementation of the access matrix.
The recommended order is:
- Keep only the actions for the initial workflow visible - for example, viewing, uploading, and downloading.
- Save the rules and open the page as the test participant in a new session.
- Check the button, right-click menu, and keyboard shortcuts, if they work in your interface: hiding a button should not leave an alternative route to the operation.
- Add one operation at a time, only when you can name its owner, purpose, validation method, and reversible rollback method.
Do not treat image editing as a replacement for a full image editor or the text editor as a replacement for development work. The product page lists image cropping, rotation, and resizing, as well as text-file editing. Those capabilities can help with a simple asset adjustment, but every file change on a live site should be reproducible: retain the original, record who changed it, and check the public-facing outcome. For PHP, configuration files, and theme files, it is safer not to enable editing in the user workflow at all.
Do you need a separate page for every project?
If you have several independent clients, you do not necessarily need many shortcodes. The main principle is independence of folders and rules, not the number of pages. One private page can be convenient if, after signing in, every user sees only their own area. Several pages are justified when projects have different operations, retention periods, responsible people, or document requirements. In every case, create a named check: "client A cannot see client B," "the participant cannot delete," "the administrator can see the log and reverse an error." This matters more than the menu's visual layout.
Practical guideline: enable public display last. If the same workflow can be completed in the dashboard by a small number of trusted staff members, do not move the file manager onto a site page merely for navigation convenience.
Practical example: a private folder for project materials
Let us examine a working use case where CodeCanyon File Manager is genuinely more useful than a simple file link. A small agency sends clients layouts, PDF reports, and source images. The client needs to download completed documents and, when necessary, upload comments or new materials. They must not see folders belonging to other clients, the theme structure, backups, plugins, or administrative files. The site administrator reviews uploads, can create an archive for delivery, and deletes outdated versions only after confirmation.
The goal is not to give someone "access to a file manager." The goal is to create a predictable private folder where the user performs two actions: upload an approved file and download the required output. This distinction matters because settings should be chosen for the intended outcome, not merely because they are available in the interface.
Step 1. Prepare the data and naming rules
On the test copy, create a separate project directory within the pre-approved working area. The path may look like wp-content/uploads/client-files/project-alpha, but confirm the specific location against hosting rules and your site configuration. Do not name the folder after a client's personal details if URLs or file names could potentially appear in logs, caches, or backups. A neutral project identifier is better, while a meaningful description can remain in the dashboard or project documentation.
Agree on file names from the start. For example: brief-v01.pdf, logo-comment.png, report-final.pdf. Names such as "final-final2" do not create a security problem, but they turn review and rollback into an argument. The rule is simple: the name should show the material type and revision number; a changed file should not silently replace the previous version until an administrator has confirmed that it is correct. If a user needs to edit an image, keep the original beside the derivative version rather than cropping the only copy directly in the browser.
For testing, prepare three files: a small PDF, an image, and an intentionally unsuitable file or one that exceeds the agreed size limit. This set tests a successful upload, preview, and rejection. Do not use real passports, contracts, database exports, or configuration files in testing. Neutral samples marked test are enough.
Step 2. Assign a limited participant and folder
Create a test client account or assign it the role prepared earlier. In the File Manager rules, select that role or specific user, assign the working folder, and enable only viewing, uploading, and downloading if those actions are needed. The product page states that the plugin can assign read and write access to different users, define folder permissions, and deny access to selected users. Use those capabilities as three independent checks: the user is recognized, the folder is assigned, and the operation is permitted.
Do not enable archive creation, the text editor, dragging files through the folder tree, deletion, copying between directories, or image modification for this account. Sometimes the interface describes permissions compactly while individual operations are hidden in the context menu. After saving, test the rule not only through visible buttons but also by right-clicking a file, a folder, and an empty area. The test participant's task is not to test every plugin feature, but to prove that the selected unnecessary capabilities are absent.

Step 3. Create a private page and add the exact shortcode
Create a draft page titled "Project Materials." At the top, add a short rule for the client: "Upload PDFs and PNGs with clear names; do not delete files; contact the administrator if an error occurs." Then insert the shortcode from the included instructions for your exact plugin version. Do not add parameters found on a random forum or belonging to another file-sharing plugin. Publish the page only after confirming that it can be opened exclusively by authenticated members of the required group.
Connect the page to the member area if the site already supports restricting pages by role or order. If no such connection exists, do not imitate protection with a hidden URL. One practical option is to keep File Manager in the dashboard until the login system is ready. That is more honest than publishing a tool with unknown guest behavior. Combining it with the WordPress login mechanism is a standard division of responsibility: WordPress handles authentication, your member area handles the user's route, and File Manager handles allowed operations in the assigned area. This is not a claim of an official developer integration.
Step 4. Run an end-to-end user test
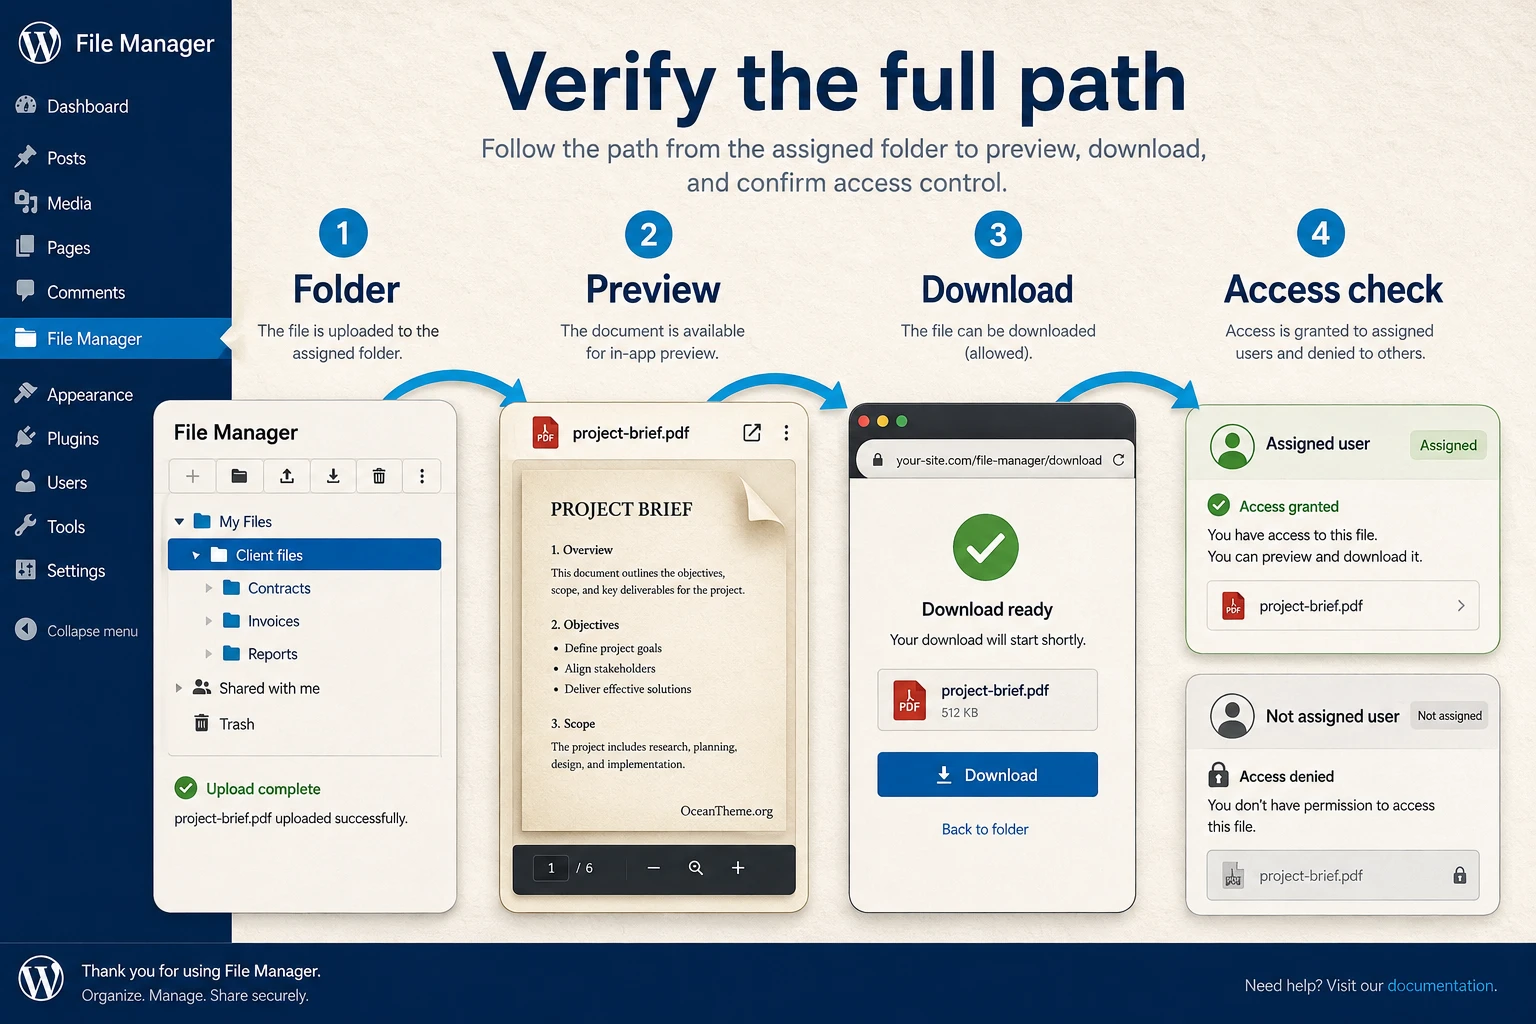
Sign out of the administrator account. As the test user, open the project page and complete the actions in their normal order. First confirm that the tree begins in the correct folder and does not show a path above it. Then upload an allowed PDF. Wait for a clear interface response, refresh the page, and make sure the file has not disappeared. Open the preview if the format and your environment support it, then download the file and compare its size with the original. Finally, confirm that the Delete button is absent or that the action is rejected.
Then open the page under the control account. It should not see the project folder. Next, try the direct URL of the uploaded file without signing in. If the file is non-sensitive and public availability is acceptable for the workflow, document this as a limitation: File Manager separates the interface, but the file link may not be protected. If direct access is unacceptable, stop the workflow and configure another protected-delivery method before working with real materials.
Administrator review
Return to the dashboard. Confirm that the new upload appears in the assigned area, its name follows the rule, its extension is expected, and its size does not look unusual. Do not open an unknown file in the editor or extract a received archive directly on the live site. If a client needs to send an archive, it is more sensible to download it first, scan it with antivirus software, and extract it in a local test environment. For an already reviewed group of files, an administrator may create an archive if their plugin version supports it, but the originals should remain separate until delivery is confirmed.
In this workflow, preview is useful as a quick review aid, not as an integrity guarantee. An image can look correct when reduced but have the wrong dimensions; a PDF can open but contain the wrong revision. For important files, check the name, size, upload date, and, when necessary, the contents at full scale. After successful review, mark the document as accepted or delivered in your internal system. There is no need to turn the file manager into an approval system if the product does not claim to provide that feature.
Common issues that usually appear only in real use
The first issue is user names. If automatic folders are used, they may depend on the login name. Profile renames, site migrations, or similar duplicate logins should be tested with test accounts. The second is deletion. Even if the interface provides a trash feature or deletion, do not treat it as full versioning. Plan for restoration through backups rather than hoping the action can be undone. The third is volume. Many large files may hit PHP limits, execution-time limits, available disk space, and hosting proxy restrictions. Test a large file separately instead of relying only on a tiny PDF.
The fourth issue is notifications. The product feature list mentions emails to administrators and users after uploads. If your version includes such a setting, enable it only after testing delivery to working addresses and agreeing on who should receive notifications. An upload email is convenient as a signal, but it does not replace file review. If emails do not arrive, troubleshoot WordPress mail configuration separately and do not expand user permissions in an attempt to "fix" notifications.
Expected outcome for this example: the client can sign in, see only the project folder, upload an approved sample, and download the completed file. The control user and guest receive neither the interface nor the directory. Any deviation from this outcome means the workflow is still in testing.
Work with files without creating chaos: uploads, previews, archives, and editing
Once the access boundary has been verified, CodeCanyon File Manager becomes a practical working tool. The product page lists drag and drop, file and folder uploads, file creation, copying and pasting, icon and list views, context menus, archive creation, multimedia and document previews, and text and image editing. The important part is to use these capabilities not as a collection of conveniences, but as clear stages: accept a file, verify it, place it in the correct location, deliver the output, and preserve the ability to roll back.
Begin every work session in the required directory rather than with a global search. If the user workflow is tied to a project, the manager should open directly in the project area; if the work is administrative, choose the exact administrative branch first. List view is useful when you need to compare names, dates, and sizes, while icon view helps quickly distinguish images. Change the view only to understand the contents, not because one looks better: decisions to move or delete a file should be based on the exact name and path.
Safe uploads: verify the file before treating it as complete
Drag and drop reduces clicks, but it does not remove the need for control. Before uploading, the user should know which file types are allowed, how to name the material, and which folder to use. After upload, check four indicators: the object appears in the expected folder, its name and size resemble the original, the file opens or downloads without corruption, and another user cannot see it outside their area. For large files, add one more indicator: after refreshing the page, the object remains present and has not become a zero-byte file.
Do not confuse an interface response with final storage. A green notification or a newly displayed row may mean the browser transferred the file, but it does not guarantee that hosting saved it without a size or execution-time limit. For important materials, do not test only one small sample. Take a file close to the real expected size, check it after signing in again, download it, and compare the checksum or at least the size. If uploads sometimes stall, do not conclude that the user needs access to broader folders. Check PHP limits, free disk space, error logs, and connection stability.
If the plugin can upload an entire folder, treat that as a separate mode. It is useful for a collection of images or documents, but it also accelerates mistakes: the wrong directory can create hundreds of objects. Enable folder uploads only for a group that understands the prepared structure, and first run a trial import of five files in a test area. After import, verify that hidden system files, duplicates, and unexpected nesting did not appear.
Preview is useful, but it has limits
The product page lists image thumbnails, audio and video previews, and previews of supported PDF and office documents through Google Docs using the preview action. This leads to a useful practical conclusion: preview is good for quick orientation, but it depends on the format, browser, external mechanism, and environment settings. Do not build a business workflow around the assumption that every document will open in the manager window.
For images, check not only that a thumbnail appears, but also that the file has the expected width, height, and orientation. For a PDF, open the first and last pages if the document is short, or at least confirm that the correct revision was uploaded. For video and audio, record the formats you have actually tested. If preview does not work, that does not automatically mean the file is corrupted. Download it and open it locally, then compare its name, size, and type. This separates a browser-preview issue from an upload issue.
When archives are useful and when they create a problem
The product features list ZIP, TAR, BZIP, and GZIP creation. An archive is useful when you need to deliver a reviewed collection of many files while preserving its structure. It is unnecessary for a single PDF that can be downloaded directly. Before creating an archive, make sure the folder does not contain temporary copies, personal data from another project, administrative files, or old drafts. Give the archive a clear name and do not delete the originals until the recipient confirms successful receipt and extraction.
Extracting an uploaded archive requires more attention than creating one. An archive may contain unexpected nesting, many files, or materials that should not be placed in a public file area. Do not allow ordinary users to extract archives during the first launch. If the workflow genuinely requires accepting an archive from a client, it is safer to download it, inspect it away from the live site, extract it in a local copy, and only then upload selected files. An archive is not safe merely because it passed through an authenticated page.
Text and image editing: the boundary between convenience and code changes
File Manager lists text-file editing and basic image processing, including cropping, rotation, and resizing. For a banner that needs a quick rotation or size reduction, that may be enough. Before the first save, download the original or copy it to an archive folder if the structure and access rules allow it. Then make one change, inspect the outcome in the interface and on the site page, and clear cache only for the relevant route. If the page looks worse, restore the original rather than trying to fix it through a series of additional saves.
The rule is stricter for text files. HTML, CSS, JavaScript, PHP, configuration files, and templates can affect the whole site. The presence of a built-in editor does not make a web interface an appropriate development environment. Do not use CodeCanyon File Manager to edit wp-config.php, WordPress core, the active theme, or plugin files on a live site. WordPress security guidance specifically recommends restricting the ability to edit files from the dashboard. For team development, prepare a copy, edit the file locally, test the changes, and apply them through a controlled deployment process.
A small reversible improvement without editing the plugin
If work takes place on a private page, it is more useful to improve the instructions around File Manager than to change its source code. For example, place a standard note above the shortcode with naming rules and allowed formats, plus a link to an internal help page. This requires no PHP snippets, will not be lost during an update, and reduces the number of incorrect uploads. The page template can use ordinary text: "Upload only PDF, PNG, or approved formats. Do not delete the previous version until its replacement is confirmed." Validation is simple: the test user sees the rule before the panel, and rollback consists of removing that block from the page.
If you need to change the location of user folders or modify plugin behavior more deeply, do not edit its files based on old FAQ examples. The author's official FAQ shows that historical type of edit by default, but an update may overwrite it. Without a confirmed current hook or setting, it is safer not to add code at all. Document the requirement, ask the author whether a supported method exists, or choose a tool with documented extensibility. This is not caution for its own sake; it protects future maintenance.
Deletion and recovery procedures
Deletion is the most dangerous button in any file interface. Even if an administrator needs it, establish a rule: first identify the file owner and the reason for deletion, then download or archive any important object, then delete it, and finally check links on the site. If a file is used in a post, gallery, or email, its disappearance may not be apparent immediately. Before cleaning up old materials, confirm that site content does not link to them and that they are not needed for regulatory or contractual retention.
Recovery testing should be part of the configuration. On a test copy, delete one neutral sample and restore it from a prepared backup. If the procedure is unclear, do not grant users deletion permissions. In a working process, it is easier to limit a permission than later explain why restoring a hosting backup reverted an old database or affected neighboring changes.
Practical takeaway: File Manager is useful when the user journey is short and verifiable: upload, see, download. The closer an action is to code modification, bulk extraction, or deletion, the more reason there is to leave it to a technical administrator and perform it with a backup available.
Validate the outcome and maintain the setup after launch
Configuring File Manager does not end when a user can see a file. A working outcome consists of several independent indicators: the right role opens exactly its own area, an allowed file appears in the correct directory, a prohibited action is absent or denied, the control role receives no access, and a guest cannot see the private screen. If you verify only the first indicator, you have proven interface convenience, not the correctness of access separation.
Build a short set of checks that can be repeated after a WordPress update, theme change, caching activation, hosting migration, or update of the extension itself. Since the available CodeCanyon page indicates an older last update and an older stated WordPress branch, this retesting is especially important. You do not need to run full regression testing every day, but before moving to a live site and after a significant environment change, repeat the key operations with test accounts.
A six-step validation path
- Sign in as an administrator and make sure the tool opens and the role and folder settings have not been reset.
- Sign in as the test participant and confirm that the entry point leads to the assigned directory without access to the level above it.
- Upload a permitted small file, refresh the page, and open or download it again.
- Check a restriction - try one action prohibited for the role, such as deleting a file or creating a folder.
- Sign in as the control user and confirm that the page, tree, and direct link are unavailable within your workflow.
- Sign out of WordPress and open the page and copied file address in a clean session.
Do not try to hide negative outcomes. If a control user suddenly sees a folder list after an update, that is not a minor interface quirk. It is a reason to immediately disable public display, record version details, and contact the developer or a WordPress specialist. For temporary stabilization, you can remove the shortcode from the page, close the member-area route, or disable the plugin through the Plugins list. Do not blindly delete files on the server until you have documented exactly what changed.

Keep a change log instead of relying on memory
For file access, a simple log is enough: the date of change, who changed the rule, what changed, which test account was used, which operations were checked, and where the backup is stored. Keep this log in internal project documentation rather than on a public page. For multiple clients, add the project identifier and folder owner. This helps not only during an incident. After several months, an administrator may forget why a role cannot create folders or why one page is excluded from caching. A single sentence next to the change can save hours of troubleshooting.
Keep a separate list of people with administrative access. A tool that can manage files makes compromise of an administrator account especially serious. Official WordPress security materials recommend keeping WordPress, themes, and plugins updated, using strong unique passwords, limiting administrative access, and thoughtfully configuring filesystem permissions. In this workflow, that is not generic advice; it is part of the functionality. The fewer trusted administrators there are, the easier it is to determine who could have changed a rule or uploaded a file.
Update without surprises
Before updating the product, first determine whether the author provides a current archive and changelog. Do not update the product on the live site immediately after receiving a file. Copy the site into a test environment, create a backup, update there, and run the six-step validation path. Confirm that visible menu items, the user-folder path, available operations, shortcode handling, direct-link behavior, and the page's fit within the theme have not changed.
Pay special attention to older custom modifications. The author's FAQ about moving the automatically created folder suggests changing lines in an extension file. If a similar customization already exists in your installation, an update will almost certainly be a risk point: the change may disappear, conflict with a new structure, or conceal an access issue. Before updating, list such changes, save a copy, evaluate whether supported settings exist, and do not reapply the edit automatically. The safest outcome may be abandoning an unsupported modification and rebuilding the workflow around a separate directory.
Compatibility with the theme, editor, and cache
A public-facing file interface lives inside the page template. The theme can affect container width, responsiveness, button styles, and scrolling. The product page mentions a file-manager window-height setting among its updates, but do not rely on that detail without checking your archive. Open the private page in a standard desktop browser and in a narrow window, then confirm that the folder tree, action toolbar, and list area remain usable. If the panel extends beyond the container, first try the plugin's standard sizing setting or the page template rather than adding untested CSS to the extension files.
The public page can also conflict with JavaScript optimization tools. Symptoms vary: buttons do not respond, the context menu does not open, the list does not refresh after an upload, or a browser-console error appears. Isolate the issue methodically: open the page in a clean browser, temporarily exclude the route from caching and script combining through the optimizer, and test in a staging environment for a conflict with a recently enabled plugin. Do not disable every plugin on a live site without a plan. If isolation helps, keep the narrowest possible exclusion for the private page and repeat the role tests.
A safe combination with the standard Media Library
Sometimes a team needs both the Media Library and a file manager. A practical approach is to separate responsibilities: editors add public images to the standard WordPress Media Library, while File Manager is used by a limited group for project documents in a separate area. Do not call this an official integration; it is an organizational arrangement. Its advantage is that public materials remain in the familiar editorial workflow while technical or client files do not become mixed with post images.
The rollout order for this arrangement is simple: use the regular Media Library for editorial materials, define a directory for project exchange, grant File Manager only to the necessary role, verify both workflows with different users, and record who is responsible for cleanup. A possible conflict is duplication of the same image in two locations. Prevent it with a rule: an image becomes public only after it is explicitly transferred or uploaded to the Media Library, while the working copy remains in the project folder until the task is complete. Rollback is clear as well: disable access to the project page without touching the Media Library or published posts.
Check performance without making unsupported promises
You cannot promise that a file manager will speed up a site or have no impact at all. On a private page, the main load depends on the number of files, thumbnail sizes, previews, server requests, and browser behavior. Test a practical case: how quickly a folder with a normal number of objects opens, what happens with one hundred images, how search behaves, and whether the list stalls when changing views. If the interface becomes heavy, do not begin with global WordPress optimization. First split an oversized folder into project subfolders, remove unnecessary test copies, and reduce the number of files the user must see at once.
Outcome validation is successful only when both convenience and restriction are confirmed. The user must be able to complete their task, while a user without permission must receive neither the interface, another user's area, nor an unaccounted-for direct route to data.
Troubleshooting: from an empty folder to excessive access
The same symptom can have several causes in a file manager. An empty list may indicate an incorrect path, or it may indicate that a role restriction is working correctly. An upload error can originate from a PHP limit, directory permissions, file type, disk space, or a browser extension. For that reason, troubleshooting should not begin by broadly enabling permissions. Start with a reproducible test: who signed in, which folder they opened, which action they performed, which file they used, and what they saw in a new session.
A user cannot see their folder or sees a blank screen
First check which account is currently signed in. Then, as an administrator, compare that account with the role rule and assigned folder. Open the same route in a private window after signing in as the user. If the folder exists for the administrator but not for the participant, do not assume a path problem: it is more likely that the role is not assigned, the rule was not saved, or the access filter is stricter than expected. If nobody can see the folder, check the actual server directory and the path in the plugin settings.
The safe fix is to return to one test directory and one test user. Remove complex nested rules, save the minimal model, and sign in again. Do not begin by granting access to the WordPress root. If simplifying the setup resolves the issue, add subfolders and operations one at a time. If it does not, record browser and server messages, compare the behavior on a site copy, and contact the documentation or author with an exact description of the archive version and reproduction steps.
An upload fails or a file disappears after refresh
The symptom usually appears with large documents before it appears with small ones. Check the test file size, permitted type, available hosting space, PHP upload and execution-time limits, and ownership of the working folder. Then upload a small neutral sample to the same directory. If the small file succeeds but the large one does not, the cause is more likely to be environmental limits than the role. If the interface reports success but the file disappears after refresh, check the error log and actual path before repeating the upload many times.
The fix should not be weakening permissions for all of wp-content, much less the entire site. Ask your host a specific question: can the WordPress process write to the selected working folder, and which upload limits apply? After correction, repeat the test with the same file in the test environment. If the issue occurs only on the private page, check its cache and script-optimization exclusions.
A user sees operations they do not need
If a participant can create an archive, delete a document, or open the editor even though the workflow does not require it, first check the role rule and the list of available toolbar or context-menu items. The presence of a button does not always mean the operation will succeed, but leaving it visible in the hope that it will fail is not a sound practice either. Perform the action with a test file. If it succeeds, the restriction is not ready. Remove the extra operation, sign out and back in as the user, then repeat the test through both the button and context menu.
When a user should see nothing beyond uploading and downloading, it is better not to use a broad role they already held for other purposes. Create a dedicated group or apply a precise user rule if your File Manager version supports it. Rollback is simple: return the test account to its previous role and remove page access until the details are understood.
The file screen stops working after enabling caching or optimization
Typical signs include unresponsive buttons, a list that does not refresh, drag and drop that does not start an upload, or one user seeing outdated content. First compare the page in a clean browser and a private window. Then, on a site copy, temporarily exclude only the member-area route from page caching and JavaScript optimization. If the issue disappears, keep the narrowest exclusion and repeat the role tests. Do not immediately disable all site caching or modify plugin files: the goal is to identify the specific conflicting layer.
A direct file link opens for a guest
This is one of the most important symptoms. It may mean that File Manager restricts the interface but not the actual delivery of a file by URL. Do not delete the file or conclude that the site was hacked right away. Check the exact address, storage location, and expected project policy in a new unauthenticated session. If the material is sensitive, stop using that folder for such data immediately, remove the link from the private page, and choose a solution with documented protected delivery. If the file is intended for unrestricted download, simply record that the manager is being used to organize the work, not to protect the content.
Folders or rules disappear after an update
First restore understanding of the state rather than plugin code: compare current settings with the change log, check the test directory and test users, and see whether an old manual modification has disappeared. If the public-facing screen behaves differently after an update, temporarily remove the shortcode, return to a backup only through a prepared plan, and collect information for support. Do not copy old extension files over new ones without verification: that can leave an incompatible mix of code and conceal the source of the error.
When to roll back: immediately, if an unauthorized role can see another user's area, if a guest gains access to the private interface, or if a change breaks the public-facing part of the site. First disable the specific access route, then restore a verified configuration on a site copy.
Questions to resolve before granting access
Can CodeCanyon File Manager replace SFTP?
For simple browsing, uploading, or work within a limited folder, it can reduce the number of context switches. However, it does not replace a safe technical process for code changes, bulk deployment, or site recovery. For those tasks, keep a backup, work on a site copy, and use a managed file-transfer channel.
Can I open the manager to every registered user?
Public display is listed as a technical capability, but the decision should depend on the folder and allowed operations. You should not open the manager to all members without a limited working area and permission checks. If people only need to receive materials, consider a normal downloads page instead of a full file browser.
How do I configure a personal folder for a client?
Check the user, role, and automatically created directory settings in your version. First create one new test user, assign one folder to that user, and confirm that a second test user cannot see it. Do not edit plugin files based on an old FAQ example until the author confirms a current supported method.
Why should I not grant write permissions immediately?
Write access can include much more than uploading: folder creation, replacement, renaming, deletion, or file editing. Begin with the smallest set of actions, check the menu and actual execution, then expand the rules only for a confirmed task.
Is the plugin suitable for documents containing personal data?
Do not reach that conclusion merely because roles and hidden folders exist. Test direct URLs, guest behavior, the file-delivery mechanism, and your organization's requirements separately. If a document must not open through a copied link, use a solution that documents protection of content access, not merely protection of the interface.
What should I do if the shortcode stops working after an update?
Temporarily remove the public entry point, repeat the test on a site copy, compare the settings with the change log, and check for caching or script-optimization conflicts. Do not replace plugin files manually or carry over old modifications without verification.
Should I disable WordPress's standard file editing?
If there is no justified reason to edit code through the dashboard, official WordPress security guidance recommends limiting that capability. This decision applies to the site's overall administration policy and should be tested on a site copy: File Manager should not be used to bypass that policy.
When CodeCanyon File Manager is a good choice
CodeCanyon File Manager is justified when you need a limited file interface in WordPress: either for a technical administrator performing controlled file work or for a small trusted group exchanging materials in a separate area. Its strength is the combination of a file tree, user rules, read and write operations, folder handling, previews, and public display where permission exists. Its weakness appears when convenience replaces control: broad access to the site root, publishing a shortcode without testing guest behavior, manually editing plugin files, or treating a simple URL as though it were protected storage.
If your task can be described as "one role, one folder, several permitted actions, repeatable validation," begin on a site copy and run the test workflow described above. Once every check has passed, you can get the WordPress version, install the archive through the standard WordPress process, and gradually move the rules into the live environment. If you instead need a public catalog, strict protection for confidential files, version history, or code development, choose a more specialized solution rather than forcing a file manager to perform a role it was not designed for.

