


CodeCanyon Content Protector - WordPress Plugin
Protect your online content from copying. Just install a small extension on your site Content Protector for WordPress to protect web content from plagiarism. The extension completely blocks all methods of copying content: selection, hot keys, developer tools and the context menu.
Plugin Features
Content Protector for WordPress prevents content theft by 95% of typical users. And flexible options allow you to configure each parameter. Extensions are quiet and invisible to ordinary users, but fast and reliable for those who are trying to steal your content.
By default, any ability to copy content is disabled. However, depending on your needs, you can enable or disable some of the options:
- Disable the selection of all: keyboard shortcuts: Ctrl+A (Windows and Linux), ⌘+A (macOS). Protect your text from copying by selecting all the keyboard shortcuts.
- Disable copying: keyboard shortcuts: Ctrl+C (Windows and Linux), ⌘+C (macOS). Protect your text from copying using the Copy hotkeys.
- Disable cutting: keyboard shortcuts: Ctrl+X (Windows and Linux), ⌘+X (macOS). Protect your text from copying with Cut HotKeys.
- Disable insertion: keyboard shortcuts: Ctrl+V (Windows and Linux), ⌘+V (macOS). Disable the insertion of hotkeys.
- Disable saving: keyboard shortcuts: Ctrl+S (Windows and Linux), ⌘+S (macOS). Protect your text from being saved by using the Save keyboard shortcuts.
- Disable the viewing source: keyboard shortcuts: Ctrl+U (Windows and Linux), ⌘+U (macOS). Disable viewing the source code of the page using hotkeys.
- Disable the print page: keyboard shortcuts: Ctrl+P (Windows and Linux), ⌘+P (macOS). Protect your page from printing with hot keys.
- Disable the developer tool: keyboard shortcuts: Ctrl+Shift+I (Windows and Linux), ⌘++I (macOS). Disable viewing the source code of the page using the developer tools.
- Disable Safari reading mode: Safari reading mode: ⌘+Shift+R (macOS). Protect text and images from copying in Safari Reader mode.
- Disable right-click: Protect your content from copying using the context menu.
- Disable text selection: Disable text selection (text selection) with the mouse.
- Disable dragging the image with the mouse.
- JavaScript required: Protect the content if JavaScript is disabled.
Specifications:
| Release date: | 08-06-2021 | |
| Last updated: | 28-12-2023 | |
| Type: | Paid | |
| License: | GPL | |
| Subject: | Authoring & Content | |
| Compatibility: | W5.x W6.x | |
| Includes: | Plugin | |
| Language packs: |

|
|
| Developer: | CodeCanyon | |
| Rating: | ||
Share with your friends!
A Practical Guide to Configuring CodeCanyon Content Protector
CodeCanyon Content Protector is best viewed not as a "lock" for an already published page, but as a manageable barrier against the simplest ways of taking text and images. This guide explains how to install the plugin, choose a sensible set of restrictions, avoid breaking forms and editors, test the outcome in a clean browser session, and understand the line between discouraging casual copying and truly restricting access.
The approach here is deliberately cautious. When visitors read a long article, look for a passage, copy an order number, quote a source, or fill out a form, aggressively disabling every key can get in the way of the very people the site is meant to serve. Start by defining the protection goal, enable rules in small groups, and check the public-facing site after every change.
We will also cover the modes that matter most for this product: blocking text selection and image dragging, copy and source-view keyboard shortcuts, the context menu, RSS, view-source: detection, a JavaScript requirement, the copyright notification dialog, custom styles, and scope control through assignments. By the end, you will have a repeatable workflow for an editorial site, a troubleshooting map, a comparison with related solutions, and answers to the questions that usually come up after the first setup.

Where Copy Protection Reaches Its Limit
On a published web page, the browser has already received the content it needs to display to the visitor. JavaScript restrictions can therefore intercept familiar actions such as mouse selection, opening the context menu, dragging an image, certain keyboard shortcuts, and some ways of opening browser tools. This is useful as a deterrent: someone who intended to select a paragraph and press Ctrl+C encounters an obstacle or a notice and will often stop there.
That same architecture also creates an honest limit. If the material has been delivered to the browser, an experienced user can retrieve the data by other means, and an image can be reproduced with a screenshot. The developer explicitly states that the product does not provide one hundred percent protection. For that reason, it should not be described as cryptographic encryption, server-side authorization, or legal proof of infringement. CodeCanyon Content Protector makes unauthorized copying less convenient, but it does not make published material secret.
This distinction helps you make the right decision before installation. For an original article, a portfolio, a recipe collection, a small publicly available course, or images without source files, the barrier is often justified. For an account area, paid download, private lesson, contract, medical data, internal instruction, or any material that must not be shown to an unauthorized person, you need a different class of solution: server-side user and permission checks, protected file links, role separation, or an access-control plugin. A right-click restriction cannot replace those measures.
Actions the Product Can Discourage
The product page and official overview list individual toggles. They can disable text selection, selecting all content, copying, cutting, pasting, saving the page, printing, viewing source with a keyboard shortcut, opening developer tools, Safari Reader Mode, the context menu, image dragging, and RSS. Updates also mention detection of view-source: addresses and the Eruda console in mobile browsers. These features should not be enabled all at once: every restriction carries its own risk for a normal visitor workflow.
Blocking Ctrl+C and text selection can make sense on pages where the text itself is the primary asset. Disabling image dragging is usually more relevant for illustrations, portfolios, and cards containing original photography. Disabling the context menu removes the most obvious path to browser commands, but it also takes away familiar visitor actions: opening a link in a new tab, saving an image URL, checking spelling in a field, or using an accessibility extension. The context menu is therefore not a default setting but a deliberate tradeoff.
Save, print, view-source, and developer-tool restrictions belong to a more aggressive group. Test them on one page rather than across the whole site. For example, disabling printing may be reasonable for an image showcase, but it is a poor fit for an instruction page, ticket, recipe, course material, or address page. Blocking paste is particularly risky: it can prevent a customer from pasting a promo code, tracking number, address, support request, or password into a form. In most projects, it is better left disabled.
What a Good Outcome Looks Like
A good outcome does not look like a page where a visitor can barely do anything. It means the chosen actions are discouraged on protected material while the user's essential tasks remain possible. Visitors can still read, follow links, use buttons, complete forms, add products to the cart, choose an option, open menus, and receive a clear explanation when an action is restricted.
Define the goal in measurable terms. For example: "Visitors cannot select text or drag original images on articles in the Research section, but text selection, copying, and the context menu remain available on support pages." Or: "Our public portfolio shows a notice when someone attempts to copy content without blocking links, the contact form, or printing." Wording the goal this way immediately clarifies which toggles are needed and which would be unnecessary.
Who This Approach Is For, and When to Choose Something Else
The plugin is especially reasonable for a public WordPress site where you want to make bulk, thoughtless copying less convenient without having to identify the visitor before displaying the page. For an editorial team, this may be a series of original analyses; for a photographer, sample images; for an instructor, introductory materials; for an agency, a portfolio; or for a store, its own descriptions and product photography. In all of these cases, the page must remain accessible to search and ordinary visitors, while the goal is simply to discourage easy actions in the interface.
The approach is also useful when you want to gently remind visitors about rights to the material. The copyright notification dialog mentioned in the changelog confirms that the product has evolved beyond a simple collection of restrictions. A notice can explain that text and images are protected by copyright and link to quotation terms or a licensing page. That is much better than silent failure, where readers do not understand why a familiar action did not work.
Do not start with Content Protector on a site where the main value is ease of working with text. Knowledge bases, documentation, reference sites, support websites, study notes, and blogs that benefit from natural quotations often gain more from allowing readers to select and copy a short passage with attribution. In those cases, it is better to provide clear quotation rules, a visible author credit, a link to the original source, and monitoring for unauthorized copies than to disable ordinary browser features.
When You Need Access Control Instead of a Client-Side Barrier
If a visitor must not see a file or text at all until a condition is met, choose an access-control solution. This includes subscriber-only material, client documents, private videos, archives, price lists, post-payment files, and internal team pages. Tools in this category check a login, role, password, link expiration, or another rule before delivering the content. Content Protector can then be used only as an additional reminder, not as the primary protection.
Protecting Media Library files and preventing direct links to images, PDFs, or videos is a separate task. It requires file-level access rules and, where needed, hotlink protection. Simply disabling right-click does not hide the URL of an image that has already been delivered. Solutions that restrict direct access to files are much better suited to that task than tools that only alter page behavior in the browser.
Finally, plagiarism prevention is not limited to interface restrictions. Preserve original publications, publication dates, and editorial source files; provide clear author information; use canonical URLs where appropriate; monitor suspicious copies by searching unique phrases; and prepare a process for contacting an infringer. The plugin can reduce casual copying, while organizational and legal measures help you respond to real cases.
Preparation: Map Pages, Roles, and Your Rollback Path
Before installation, make a list of specific site areas rather than treating "the whole site" as one unit. Divide pages into at least three groups: material you want to protect; pages where normal browser features matter more than protection; and administrative or dynamic screens. The first group may include long-form original articles and portfolio pages. The second may include contact forms, help sections, search, account pages, checkout, coupon-code pages, return pages, and contacts. The third may include editors, previews, admin screens, external embeds, and pages that load complex widgets.
Check which elements must not be disrupted. If the site accepts inquiries, list every field where a user may paste text. If there is a store, include the cart, coupons, address fields, and product search. If there is a forum, comments, or a content editor, include publishing fields, attachment uploads, and formatting buttons. If you use a page builder, make sure testing happens on the public-facing site, not inside the editor. The developer's changelog specifically notes an exception for the Elementor editor in the admin area, but that does not replace testing your own site configuration.
Create a rollback point. It is enough to record the current active plugins, clear any pending cache changes, and know who has access to the Plugins section. There is no need to edit WordPress core, modify product files, or add third-party JavaScript snippets. A safe rollback is straightforward for this task: disable the risky toggle, restore default settings if necessary, or temporarily deactivate the plugin from the regular plugin list.
A Minimal Test Matrix
A small matrix with a page, action, and expected outcome in each row is useful during preparation. It protects you from a situation where the plugin blocks copying perfectly on an article but accidentally prevents someone from writing a message in a form. Maintain it before and after configuration changes, preferably in a private browser window.
| Area | Action to test | Desired state |
|---|---|---|
| Original article | Select a paragraph and copy it | The action is restricted or a copyright notice is shown |
| Portfolio gallery | Drag an image into a new tab | Dragging is restricted, while normal image viewing still works |
| Contact form | Paste long text into a field | Pasting works without interruption |
| Search and navigation | Open a link in a new tab | The context menu or the standard method remains available when the workflow requires it |
| Print page or instruction | Open the system print dialog | Printing is not blocked if users would reasonably expect to use it |
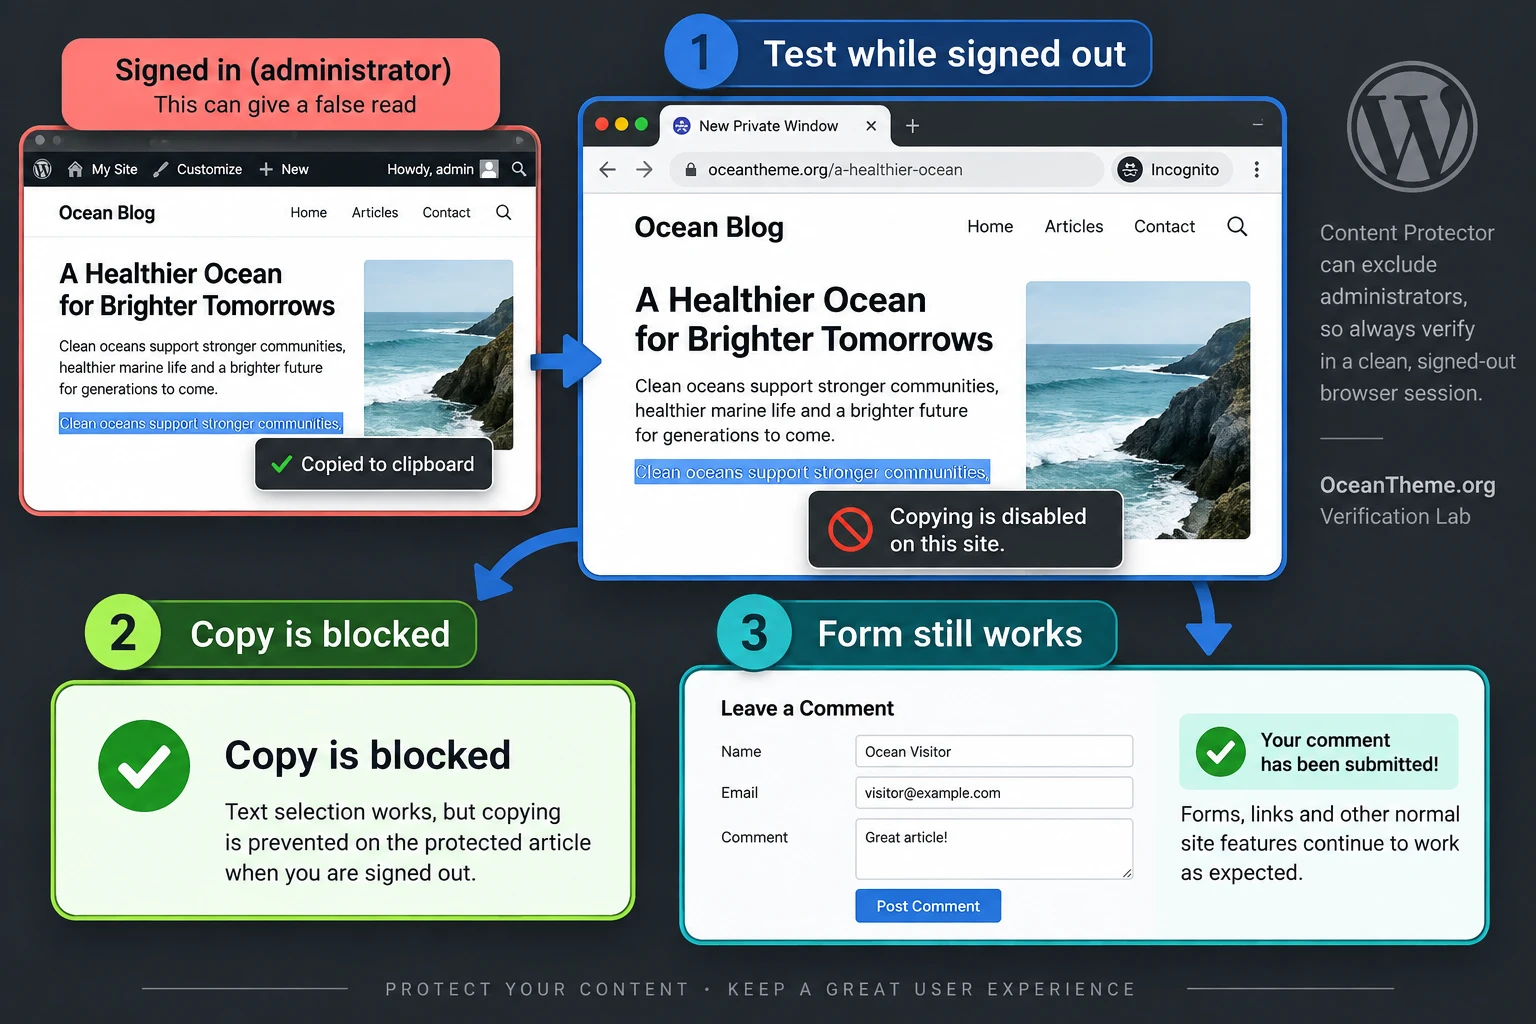
Do not test only while logged in as an administrator. Many restrictions may intentionally exclude administrators, creating the false impression that a rule does not work. Open a logged-out window, and for a key workflow, ask a colleague to repeat it in another browser. This checks role exclusions, caching, and differences in event handling at the same time.
Compatibility and Caching
The product listing claims compatibility with common WordPress editors and solutions, including the block editor, Elementor, WPBakery, form plugins, WooCommerce, WPML, and other components. This is a useful reference point, not a guarantee for every combination of theme, optimization settings, and custom code. Pay particular attention to caching plugins and deferred JavaScript loading: after changing settings, clear the site and browser caches, otherwise you may see an old behavior and mistakenly change the rule a second time.
If the site uses a minifier, do not disable it permanently for a single test. First reproduce the issue in a private window after clearing caches. Then, if it can be done safely, temporarily disable only JavaScript optimization for a brief test. If the conflict disappears, document the exact version combination and exclusion setting in the site documentation. If it does not disappear, restore optimization and identify which action breaks the interface: selecting text, clicking, pasting, form loading, or the editor.
Install Without Unnecessary Changes to WordPress
The official 42Theme instructions describe a standard installation through the WordPress admin panel. From the supplied archive, select the plugin file, then open Plugins - Add New, choose Upload Plugin, select the product ZIP file, click Install Now, and then Activate. If the extracted archive contains documentation and other supporting files, do not upload the entire extracted package: the standard WordPress form needs the plugin package identified in the supplier's instructions.
After activation, do not blindly enable every protection option. First find the settings page through the plugin row link or the menu item added by the product in the admin panel. Its exact location can vary between releases, so this guide uses rule names from the official description rather than promising a fixed menu path. Before saving for the first time, take a screenshot of the current values or write them down in a working note.
The product is described as a native JavaScript solution with no jQuery dependency. That does not mean it should be excluded from the normal update cycle or that conflicts are impossible. Update WordPress, your theme, and plugins as part of the usual maintenance process, then repeat the short matrix from the preparation section. The changelog includes fixes for multiple 42Theme plugins running together, AJAX requests, the Elementor editor, Safari, and iframe behavior. Those entries are a reason to test specific user workflows after updates, not a reason to assume the issues are closed forever.
First Check Immediately After Activation
Open one test article in a private window and try only two actions: select a short sentence and open the context menu. If you already see blocking, do not immediately change the entire rule set. First make sure forms, search, and links on the same page still work. If the product displays a copyright notification dialog, assess its wording from the visitor's perspective: it should explain the rule rather than sound like a technical error.
Then open the login page, one form, a page with regular links, and a page containing an image. If everything remains usable, move on to configuration. If not, temporarily return to the minimal mode and isolate the conflict one rule at a time. Do not troubleshoot a site by changing five toggles at once. Otherwise, it is impossible to know which one intercepted the action you need.
Settings Map: Enable Rules by Behavior, Not by Name
Detailed CodeCanyon Content Protector configuration begins by choosing the most appropriate mode, not the strictest one. The product offers separate controls for the keyboard, mouse, images, source viewing, and feeds. Divide them into three layers: discouraging obvious copying, additional restrictions for sensitive material, and high-risk modes for visitor usability. This division gives you predictable behavior and lets you quickly roll back a questionable choice.
First Layer: Text, Selection, and Image Dragging
For most public articles, start with actions directly related to simple content extraction. These include Disable Copy, Disable Select All, Disable Text Selection, and disabling image dragging. You do not have to enable all four. If you want readers to retain the ability to select a term or name but make routine keyboard copying harder, test only copy blocking. If you publish valuable original text and quotation is not a goal of the page, you can add a selection restriction.
Disable Text Selection has an easy-to-understand side effect: it can make it harder for visitors to work with text on the page. Someone may not be able to easily select a phone number, address, order number, definition, or model name. For posts containing information that visitors reasonably expect to transfer to another application, try a lighter mode without disabling selection. If you still choose a strict mode, provide copyable buttons or separate links where they genuinely matter.
Disabling image dragging is useful for portfolios and pages with photography, illustrations, and design mockups. However, it does not replace a watermark, a licensing notice, or server-side protection of the original file. A good practice is to publish a reasonably sized image publicly, store the source file separately, and add a clear usage-terms section. The plugin then discourages the easiest action while organizational protections remain in place.
What to Do About Paste and Cut Shortcuts
The official list includes Disable Cut and Disable Paste. On a public article, disabling cut adds almost nothing because a visitor normally does not edit the page text. Disabling paste is much more noticeable and more likely to cause harm, because browser paste is used in forms, search, comments, shipping fields, and editors. Leave Disable Paste turned off unless you have a narrow, tested reason to enable it in a specific area.
If your goal is to prevent visitors from pasting a particular template into a field, solve that within the form itself through validation, guidance, format restrictions, or server-side checks. Content Protector is not designed for that purpose. Its keyboard handling occurs before meaningful data validation and may affect legitimate users.
Second Layer: Context Menu and System Commands
Disable Right Click prevents the mouse from opening the context menu. It is the most visible sign that the product is active and therefore the most controversial setting. On an image showcase, it may reduce attempts to save a picture through the obvious menu. On a normal informational page, it is often frustrating: people use the context menu to open links in another tab, translate a passage, check spelling, access extension features, and use accessibility tools.
Before enabling the restriction, look at the page through the eyes of someone who knows nothing about your site. Are there links that are convenient to open separately? Is there an image whose address a user may need to view or share? Is there text that may need translation? If the answer to even one question is yes, first try leaving the menu available and strengthening only copy or drag protection. When the context menu truly needs to be disabled, provide alternative interface paths: clear buttons, visible links, and a short rights notice.
System commands include Disable Save and Disable Print Page. They discourage familiar keyboard shortcuts, but they do not remove other browser and operating-system functions. These rules are generally unsuitable for material that visitors would reasonably want to print or save for personal use. First determine whether you need to protect the text itself rather than prevent people from working with the page.
Third Layer: Viewing Source, Browser Tools, and Safari Reader
Disable View Source, Disable Developer Tool, and Disable Safari Reader Mode only make sense after you accept the limits of this type of barrier. They can intercept the best-known ways of opening page source, developer tools, or reading mode. The official overview lists them as product features, while the changelog refers to improved tool detection and special work for iOS and Eruda.
Do not treat a triggered restriction as proof of absolute protection. Browsers, extensions, and nonstandard workflows vary. More importantly, aggressive interference with developer tools can hinder developers, support staff, accessibility tools, and your own site troubleshooting. Begin with one noncritical test page and check several browsers. If you see a false positive, stop at this layer and return to lighter mouse and keyboard rules.
Safari Reader Mode deserves particular care. It helps some users read long material without unnecessary styling. Disabling it can make reading worse for people who need concentration or a simplified text presentation. If the only reason is preserving the page layout, consider whether a properly responsive page, clear authorship, and protection of original images would be a better priority.

RSS, JavaScript, and view-source: Addresses
The version reflected in the changelog introduced RSS blocking and view-source: detection. RSS is not merely a technical leftover. It may be used by readers, aggregators, applications, and content-distribution workflows. Before enabling Disable RSS Feeds, check whether the site has feed subscribers, whether content is sent to other services, whether the feed supports internal automation, and whether it is part of an agreement with your audience.
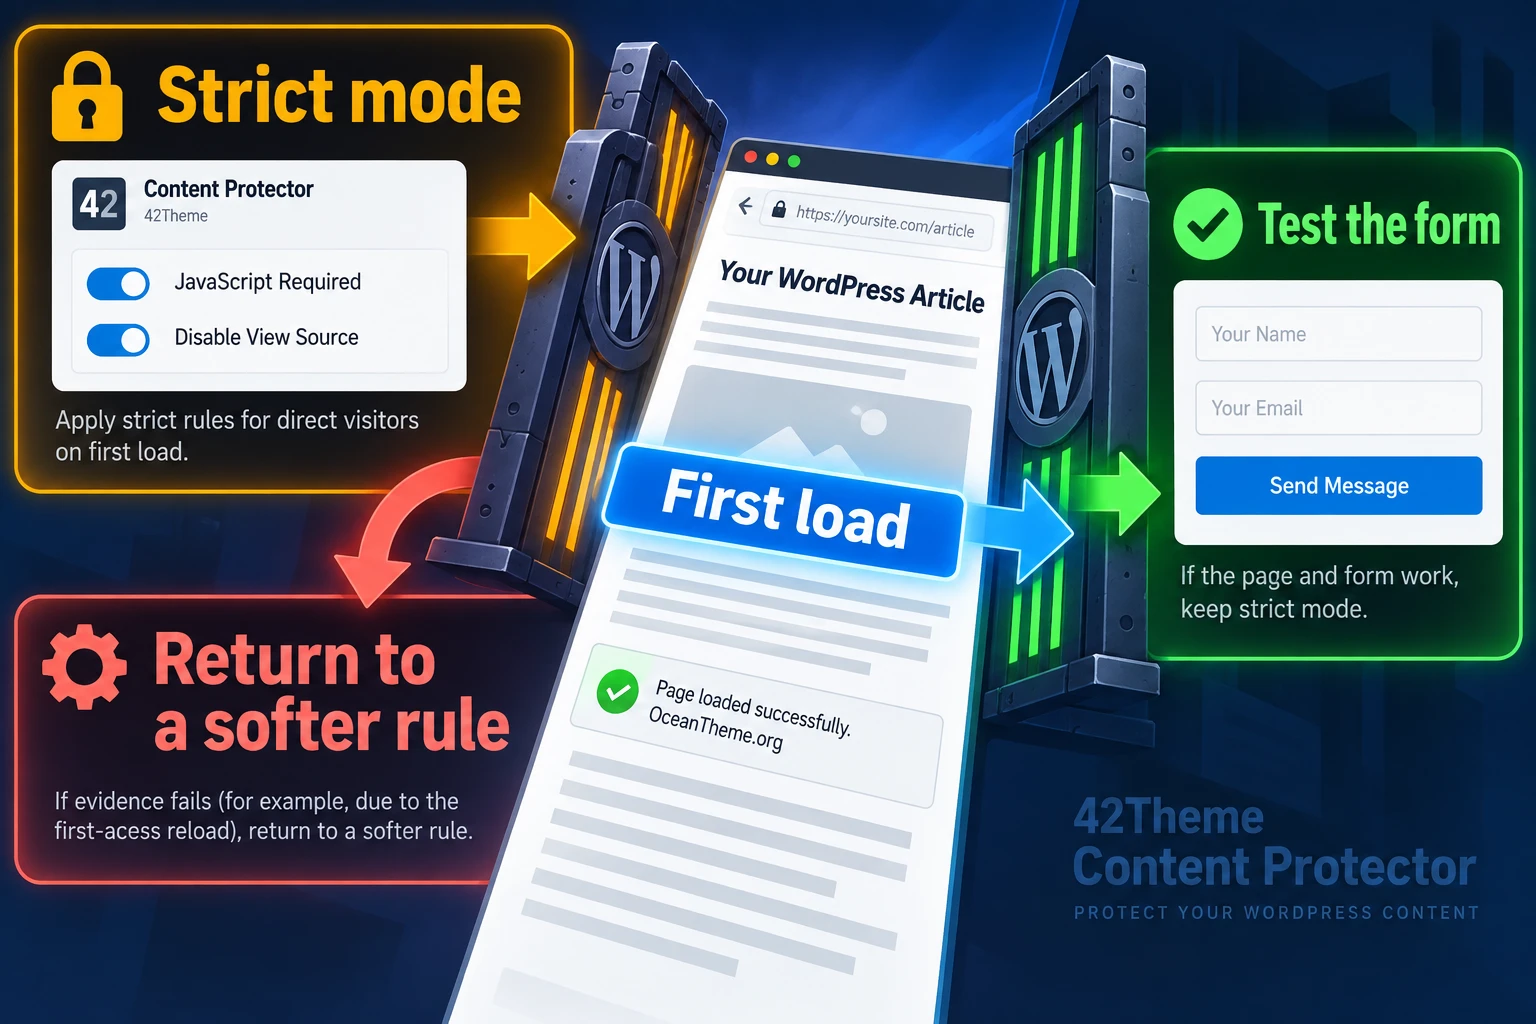
JavaScript Required is stricter still. The official overview warns that it blocks clients without JavaScript along with the protection. This means you are deliberately denying access to some visitors and tools. It should not be treated as a neutral "strengthen protection" toggle. For a public article, help page, documentation, or a page needed for a customer inquiry, this mode is usually unjustified. Use it only when you understand the consequences, have limited its scope, and have tested the indexable public-facing site.
According to the developer, the feature related to view-source: may trigger two initial reloads for a direct visitor. That is a critical testing signal. If you enable this mode, test the first load on a clean device, a direct link from search results, analytics, forms, and cache behavior. If you see flickering, a repeated load, lost URL parameters, or a failure in a dynamic interface, disable the rule and retain a lighter set of measures.
Assignments, Exclusions, and Activation Order
The changelog mentions an assignments tab, and the documentation includes a separate article about limiting the plugin's scope. This matters more than most individual keyboard shortcuts. If your installation offers page, content-type, area, or exclusion selection, start there. The goal is not to make the entire site equally unfriendly, but to apply the barrier to publications where it is justified.
A practical order is as follows: first enable the plugin on a single test article, then on a small section with a similar layout, then test forms and theme elements, and only then expand coverage. If the product lets you exclude administrators or logged-in editors, use that to keep the team working normally, but do not mistake an administrator exclusion for a public-facing test. Always keep one logged-out browser window for verification.
Do not try to bypass plugin restrictions by editing its files. Those changes will disappear during updates, and the source of a problem will become unclear. If you need to change the appearance of the official notice, first investigate the built-in custom-style section added to the product according to the changelog. If exact selectors are unavailable in the current documentation, do not add CSS by guesswork. It is safer to begin with notification text and assignment rules, then make appearance changes only after reviewing the supplier's available documentation.
Copyright Notification Dialog and Custom Styling
The product history notes Copyright Dialog and a Custom CSS tab. The dialog is useful when its message relates to a real visitor action. Instead of a threatening statement, briefly explain that the material is copyright-protected, short quotations with an active link are allowed, and there is a contact method for licensing or republication. This preserves a human tone and gives people who genuinely want to use the material correctly a legitimate path.
Test the dialog on both large and small screens, on a page with video, on a page with a form, and with browser zoom enabled. The text must be readable, closable in an obvious way, and must not permanently cover a button, field, or navigation. If users cannot close the notice or return to reading, it becomes an interface failure. In that case, first look for a built-in behavior setting, and if no documented option exists, roll back the rule.
Custom styles should be the last step, not the first. They make sense if the notice clashes with the theme and you can confirm which selectors the current version supports. Apply any change first to a site copy or test environment, then check it on the front end and keep the original snippet separately for rollback. Do not place CSS in WordPress core, theme files without a child theme, or Content Protector files.
High-Risk Modes: Avoid Cutting Visitors Off From the Site
The most troublesome failures happen not because a rule "doesn't work," but because it works too broadly. The plugin catches an event that looks like a copying attempt to you but is an ordinary task for a visitor. Before enabling aggressive settings, walk through this sequence: original action - intercepted rule - interface change - expected benefit - potential harm - test and rollback.
Forms, Search, and Editing Fields
A contact form is the best place to test. Paste several lines with line breaks into a field, select one word, correct it with the context menu, try browser autofill, and send a test message. Then repeat this in search, comments, registration, newsletter signup, and, if applicable, checkout. If enabling a rule breaks even one expected input method, do not explain it to the user as a "protection feature." Disable the risky setting or exclude that area from the product's scope.
Check fields embedded by a third-party service through an iframe separately. The changelog includes a fix for behavior inside iframes, but the existence of a past improvement does not replace testing your own form. Open the page on a desktop device and a touch device, make sure the cursor appears, text can be entered, the submit button can be pressed, and no false dialog appears after submission.
If you notice a problem only for some visitors, ask about their browser, extensions, and exact page rather than immediately rewriting site settings. A simple table of "browser - page - action - outcome" leads to the cause faster. Temporarily narrow the scope to material for which protection is critical so forms continue working.
Links, Images, and Theme Elements
Disabling right-click can interfere with links, while blocking selection can affect text buttons and interface fragments that the theme styles in nonstandard ways. Walk through the header, footer, drop-down menu, breadcrumbs, social buttons, lightbox gallery, and embedded map. At each element, ask: can it be clicked, can a separate link be opened, can a window be closed, can an image be enlarged, and can the visitor return?
If the main reason for installation is image protection, do not automatically enable the same rules for text. Choose image-drag restrictions and assess the context menu only in the gallery. The user-experience difference is significant: a person can still copy an address and quote text on the page, while losing the most direct way to drag a sample image. This configuration is often more useful than a blanket restriction.
Keep accessibility in mind. Visitors may use keyboard navigation, screen magnification, voice input, translation tools, the context menu, or browser assistive features. Do not treat their attempts as malicious. If the site contains required information, contacts, legal terms, or instructions, preserve normal reading and copying of critical information. It is better to isolate protected content by page or section than to turn the entire site into a restricted zone.
Cache, Optimization, and Misleading Tests
After saving settings, clear the cache that actually serves the public-facing page: plugin cache, hosting cache, content delivery network if used, and browser cache. Then use a private window. If you test only an already open tab, you may see old JavaScript or an already saved state and mistakenly blame Content Protector for inconsistent behavior.
Do not confuse a blocked action with a loading error. If a form or gallery does not work on a page, check whether the issue disappears after disabling only one rule. If it does, you have a reproducible connection. If not, investigate cache and third-party plugins. The changelog mentions fixes for conflicts with other 42Theme products, AJAX, and Page Builder, so post-update testing should be part of normal operation, not a one-time installation procedure.
Practical Workflow: Protecting a Series of Original Research Articles
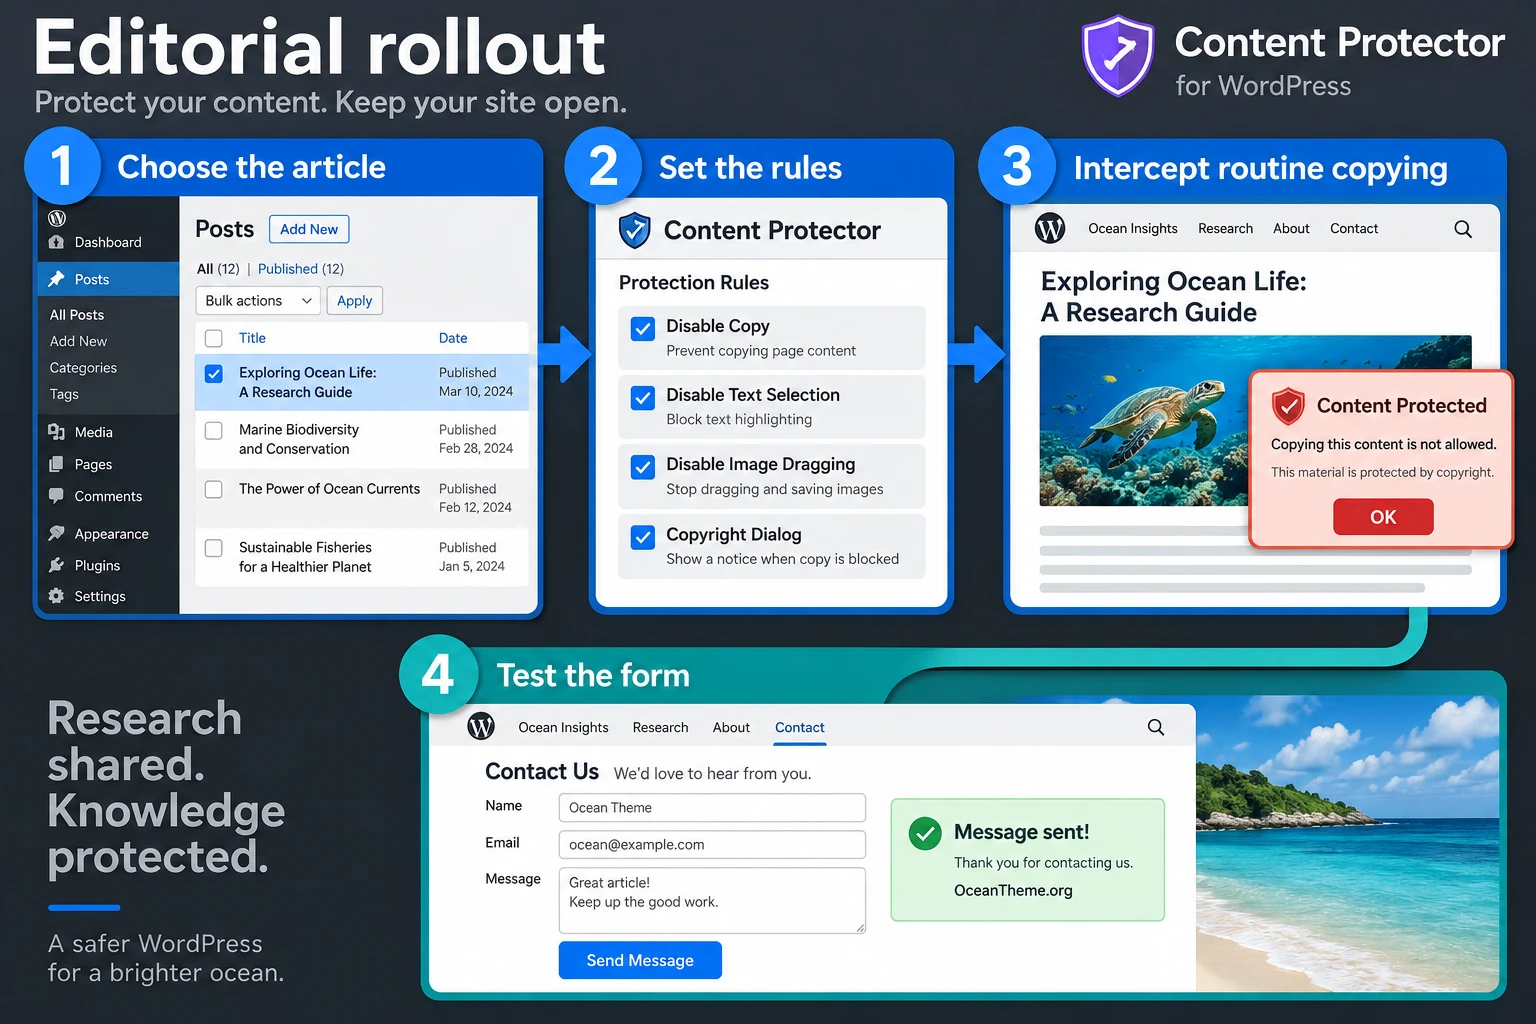
Consider a realistic task. An editorial site has a section of long research articles where the value lies in original text, infographics, and commissioned illustrations. The site also has a "Contact Us" page, a topic-submission form, a newsletter signup, search, and a regular news section. The goal is not to hide the research from readers, but to make mechanical copying less convenient without breaking the rest of the site.
Goal and Workflow Preparation
Define the desired outcome: on research pages, visitors cannot simply select the entire text, copy it with the usual shortcut, or drag an illustration; when they attempt to copy, they see a clear copyright notice. Text selection, pasting, the context menu, and printing remain available on contacts, search, forms, subscription pages, and regular news articles. Do not enable RSS blocking, paste blocking, print blocking, source-view blocking, developer-tool blocking, or mandatory JavaScript during the first pass.
Create one test post with several paragraphs, a link, an image, a blockquote, and a "Contact the Editorial Team" button. Add a standard form to it or link to an existing form. This setup lets you observe not only text protection but also how the rules interact with links, images, and user actions.
Configuration Steps
- Open Content Protector settings and identify the assignment mechanism offered by your installation. Select only the test post or test section, not every page type on the site.
- Enable copy blocking and disable select-all if that matches your goal. Save the changes with the interface's standard button.
- Enable image-drag restrictions. Leave the context menu enabled for the first test so visitors retain normal link-navigation options.
- Configure the copyright notification if it is available in your version. State a clear policy: brief quotations with a link are allowed, while republication requires contacting the editorial team.
- Clear caches and open the test post in a new private window while logged out of WordPress.
The point of this sequence is that every change has its own observable effect. After the second step, you learn whether the rule affects text. After the third, whether it affects images. After the fourth, whether the response is clear to the visitor. If you enable everything at once, it becomes impossible to identify which setting made the page inconvenient.
Verify the Public-Facing Outcome
On the test post, try selecting one paragraph with the mouse, using Ctrl+A, using Ctrl+C, dragging an image, opening a link with a normal click, and filling in the form field. The expected outcome is that the actions you chose to discourage are restricted or trigger a notice; the link opens; the form accepts input; and the submit button works. If you cannot paste text into the form, a restriction that is too broad may have been enabled accidentally, or the assignment may have affected the form component.
Next, visit the contact page and perform the opposite test. Here, selecting a phone number or address, pasting into the message field, and using the context menu should work if you chose to retain it. This pair of tests proves not merely that the plugin works, but that its scope is correct.
Expand the Workflow Without Losing Control
Only after success on one post should you add two or three more pages from the same section. Check pages with different layouts: one with a large image, one with many links, and one with embedded content. If the behavior is stable, expand the assignment to a category or content type when that option is genuinely supported by the current product version. Repeat the short private-window test after every expansion.
Do not automatically apply this mode to archives, search, tags, author pages, or the homepage. In those areas, users often want to open posts in separate tabs and work with navigation elements. Observe actual audience behavior first. If complaints arise around a specific action, narrow the rules instead of adding further restrictions.
How to Verify That Rules Actually Work
Testing should not be limited to one right-click. You are checking the relationship between "rule - event - visible outcome - preserved usefulness of the page." It is easiest to do this with a short workflow and record not only success but also side effects. This log is especially valuable after updating the theme, caching plugin, or Content Protector itself.
Basic Test in a Clean Session
Open a private browser window. Do not log in to WordPress. Go to the protected page using its direct URL, not only from an already open tab. Check loading, scrolling, links, images, selection, copying, and the keyboard shortcuts you selected. Then open a page with a form and try entering and pasting text. If your audience uses several important browsers, repeat the test in at least two of them.
Touch devices require a separate workflow. On a phone or tablet, try a long press on text, zooming, following links, opening an image, and using the form. Do not draw conclusions from desktop-browser behavior alone. The changelog specifically mentions the Eruda mobile console and the removal of developer-tool detection for iOS, which itself shows that interface restrictions behave differently across platforms.
Check Search Accessibility Without Making Grand Claims
The developer states that the product does not negatively affect indexing, and the update history notes unrestricted access for Google PageSpeed Insights. This is useful information, but it does not remove the site owner's responsibility to test the exact configuration in use. Do not claim that every restriction is guaranteed to be neutral for search. Treat JavaScript Required, RSS, and the mode related to view-source: with particular caution.
The practical minimum is simple: open the page while logged out, make sure the main text truly loads, check that no reload loop occurs, and do not block ordinary access to the site merely to enforce a protection interpretation. Then use your existing indexing and performance monitoring tools if they are already connected to the project. If metrics or crawling behavior become suspicious after enabling a strict rule, the strict mode should be the first rollback candidate, not an arbitrary theme change.
Verification criterion: a logged-out visitor can see and read the selected material, simple copying is discouraged, forms and links continue to work, and the first load does not look like an error or endless redirect.
Test After Updates
The official changelog records compatibility improvements for AJAX, page builders, Safari, and iframes. Therefore, after updating Content Protector, WordPress, the theme, or a significant optimization stack, repeat the test matrix. You do not need to retest the entire internet, but spend five minutes on critical paths: the protected article, form, search, image, page with an embed, and the first logged-out page load.
If an update causes a problem, first record the plugin version, exact page, browser, and action. Then temporarily disable only Content Protector or only the recently added rule to establish the connection. Do not simultaneously update, change themes, reset all settings, and add custom code. When several changes happen together, you cannot reconstruct the source of the problem.
Compatibility, Accessibility, and Editorial Workflows
Strong protection settings account not only for external traffic but also for the work of your team. An author may need to select their own text on the public-facing site, an editor may need to open an image, a support specialist may need to reproduce an issue, and a developer may need to inspect the console. If the product offers exclusions for these roles, apply them only within the normal WordPress permissions model. However, perform primary testing while logged out, otherwise exclusions will hide the behavior seen by ordinary visitors.
Do not confuse editorial permissions with copy protection. WordPress roles govern who can modify posts in the admin panel. Content Protector governs browser events on public pages. If an editor cannot edit material, that is not this plugin's task. If a client cannot see a protected contract, that is not this plugin's task either. Keeping those responsibilities separate prevents unsuccessful attempts to solve accessibility, authorization, and interface behavior with one toggle.
Why Accessibility Matters More Than Maximum Strictness
Blocking selection and the context menu changes more than an abuser's path. It also affects people who find it easier to use text enlargement, translation, reading assistance, or voice input. On a site with instructions, services, legal terms, and contacts, this can become a real obstacle. Before expanding rules, evaluate whether you can limit them to a topical section while leaving key service pages normal.
Add a clear authorship statement and permission-request method to the protected page. This helps more than an opaque collection of blocks. If a visitor needs to quote several lines for a review or study, they understand whom to contact. If they need a number or link, they are not trapped because text selection was disabled by accident. Users should retain the ability to complete a reasonable task.
Pages With WooCommerce, Builders, and Widgets
The product listing names compatibility with WooCommerce, builders, forms, and other common solutions. Treat this as a starting point for testing, not as permission to enable every restriction on a checkout page. In WooCommerce, paste and context-menu restrictions are especially risky: a visitor may need to paste an address, coupon, payment details, or order number. You can lightly protect original product images, but it is wiser to exclude the cart and checkout.
In page builders and complex widgets, the front end may use mouse handlers, dragging, iframes, and AJAX. If only one block breaks after activation, do not disable the entire site. Check whether the block belongs to the protected material. If it does not, exclude the page or area. If it does, choose the smallest rule that produces the needed effect, such as disabling image dragging instead of disabling the context menu globally.
A multilingual site needs separate checks for every language. The plugin claims RTL support and WPML compatibility, but a long notice or narrow button can look different on a translated page. Check dialog text length, interface direction, links, and the form. Do not treat the Russian or English outcome as proof for all other languages.
Safe Editorial Practice Instead of Unverified Code
The product mentions a custom CSS settings section, but the available official page with exact selectors could not be opened during research. That is why this guide does not include a random CSS snippet. This is intentional: do not add styles based on assumptions about internal markup. A safe sequence is to use the built-in dialog text, check the documentation for your current package, test the change on a site copy, and preserve a simple rollback method.
If serious customization of behavior is required, consult the supplier's documentation or a specialist who can review the specific package version. Do not edit plugin files directly. For most sites, the best improvement is already available without code: narrower assignments, lighter rules for text, image-drag protection, and a clear copyright notice.
Troubleshooting: Symptoms, Causes, and Safe Rollback
The checks below are not abstract suggestions but diagnostic chains for typical issues in a plugin that intercepts browser actions. Begin by reproducing the problem in a private window and change only one setting at a time. If rolling back one setting resolves the issue, record it as the cause rather than compensating for a new failure with additional code.
A Visitor Cannot Paste Text Into a Form
Symptom: the cursor is in the field, but Ctrl+V, the context-menu paste command, or autofill behaves strangely. Likely cause: paste blocking is active, or protection has been assigned too broadly and intercepts the form event. Check: open the page while logged out, paste multiline text into every critical field, and compare the behavior with the rule temporarily disabled.
Fix: disable Disable Paste or exclude the form page from the plugin's scope. If the goal was improving inquiry quality, address it in the form itself with required-field validation, guidance, or server-side validation. When to roll back: immediately if registration, contact requests, search, payments, or login are affected.
A Link Does Not Open in the Expected Way
Symptom: a normal click works, but visitors cannot open a link in a new tab, view its address, or use translation. Likely cause: the context menu has been disabled. Check: test internal, external, and telephone links on the protected page. Do not limit testing to one text link: the theme menu and widget buttons may also depend on familiar mouse behavior.
Fix: leave Disable Right Click turned off or narrow the assignment to a gallery if the current version and site layout allow it. Add visible buttons for actions previously performed through the menu. When to roll back: if the restriction interferes with navigation, support, or access to important information.
The Page Reloads After Enabling a Strict Mode
Symptom: on the first direct visit, the page flickers, reloads, or some dynamic elements appear late. Likely cause: the feature related to view-source: detection is enabled; the official description warns of two initial reloads during a direct visit. Conflicting JavaScript optimization is also possible.
Check: clear caches, open the exact URL in a private window, and repeat the visit from a search or external source. Then temporarily disable only this strict mode and compare. Fix: retain lighter copy, selection, and image-drag rules if they meet the primary goal. When to roll back: if repeated loads occur, URL parameters disappear, a form breaks, or visitors see an unstable page.
Protection Appears Not to Work for an Administrator
Symptom: after saving settings, an administrator can still select and copy text. Likely cause: the product or assignment excludes the administrative role, or the browser is showing an old cached page. The update history specifically mentions excluded administrators.
Check: log out of WordPress and open the page in a private window. Clear the site and browser caches. Review assignment and role-exclusion settings. Fix: do not remove an exclusion solely for testing if it is useful to the team. Set up a normal public-facing test instead. When to roll back: no rollback is needed as long as the restriction works correctly for logged-out visitors and does not disrupt the page.
A Builder, iframe, or AJAX Form Behaves Unreliably
Symptom: a block does not open fully, a form does not submit, or an editor or embedded component stops responding. Likely cause: event interception overlaps with a builder script, iframe, or AJAX behavior. The changelog contains fixes for iframe, Elementor, and AJAX conflicts, but the exact third-party component stack on your site may be different.
Check: disable only Content Protector for a short test or remove the specific rule. Then disable caching in a test environment and compare. Record the browser, URL, and action. Fix: exclude the affected page, reduce the number of active restrictions, or update components in a controlled order. When to roll back: immediately if form submission, editing, the cart, or the primary interactive workflow is disrupted.
An Image Can Still Be Retrieved
Symptom: image dragging or right-click is blocked, but a user can still find the file in cache, take a screenshot, or discover a direct address another way. Cause: Content Protector operates on a page already displayed in the browser and is not server-side file protection. Check: do not turn this observation into an endless race with the browser. Ask whether the file should actually be publicly available.
Fix: for a public portfolio, use a reasonable image size, attribution, and usage terms. For a private file, use a solution that controls file access. When to roll back: roll back the unrealistic expectation, not the light protection itself. The plugin may remain useful as a barrier against ordinary dragging, but it should not be treated as a safe.
RSS or Reader Mode Is No Longer Useful to the Audience
Symptom: readers complain that they no longer receive posts in their usual reading method or cannot open a simplified mode. Likely cause: Disable RSS Feeds or Disable Safari Reader Mode is enabled. Check: determine whether the audience uses feeds, aggregators, and reading mode, then compare behavior before and after disabling one rule.
Fix: disable the relevant restriction or limit it to a narrow set of materials if assignment settings allow that safely. When to roll back: as soon as the rule worsens access to material that should naturally remain easy to read.

Questions That Come Up After Initial Setup
Can CodeCanyon Content Protector Be Considered Full Protection Against Theft?
No. It discourages familiar browser-based copying methods: selection, some keyboard shortcuts, the context menu, dragging, and certain other actions. The developer explicitly states that there is no one hundred percent protection. Use the product as an additional barrier and a clear copyright notice, while access to nonpublic data should rely on server-side rules and authorization.
Should I Enable Every Toggle at Once?
No. Start with one page and a minimal set, such as copy blocking and image-drag restrictions. Then test links, the form, and normal reading. Add restrictions for pasting, printing, RSS, reading mode, source viewing, developer tools, and mandatory JavaScript only after you understand their side effects and need.
Why Can't I Test the Plugin Only as an Administrator?
Administrative-role exclusions may apply, and the browser may retain an old version of the page. Test in a private window while logged out. This is the test that shows normal visitor behavior and also helps reveal caching issues.
Will Disabling Text Selection Harm SEO?
The developer states that the product should not negatively affect indexing, and the update history mentions access for PageSpeed Insights. However, no absolute promise can be made for a specific site. Check JavaScript Required, RSS, and view-source: modes especially carefully. After making changes, make sure the logged-out page loads and displays its main text without an abnormal reload.
Can I Protect Only Images Without Making Text Harder to Copy?
Yes, and this is often a sensible option. Focus on disabling image dragging and assess the context menu carefully only where it genuinely creates a problem. Let readers select an address, name, code, or quotation. Remember that a published image does not become a private file: strict protection requires control over direct access to the Media Library.
What Should I Do If a Form Stops Working After Activation?
First check Disable Paste and the assignment scope. Open the form in a private window, paste multiline text, and temporarily disable one risky rule. If the issue disappears, leave the restriction disabled on the form or exclude the page. Do not compensate for the problem by changing WordPress or plugin files.
Do I Need to Block RSS?
Only if you deliberately want to disable that distribution channel and have confirmed that readers, aggregators, and internal workflows do not need it. For a blog or news site, RSS is often part of normal content consumption. Blocking it is justified less often than basic copy deterrence on an individual page.
Is the Product Suitable for a Paid Course or Private Document?
Not as the only solution. If material is available only to a buyer, client, or employee, use a login system, roles, page restrictions, expiring links, or file protection. Content Protector can remain an additional layer on an already available page, but it should not be responsible for authorization.
When This Plugin Is a Good Choice
CodeCanyon Content Protector is a good choice if you publish material publicly, understand the unavoidable limits of browser-based protection, and want to remove the simplest methods of bulk copying without rewriting your theme. The most dependable strategy is not maximum strictness but precise assignment: protect original research or a gallery, keep forms, help, search, and critical pages convenient, and regularly repeat a short verification after updates.
If testing shows that the visitor workflow remains clear and the selected actions are genuinely discouraged, the configuration is correct. If the site loses the ability to support normal reading, form completion, document printing, or link use, take one step back. A lighter rule applied correctly is more useful than dramatic protection that creates a new problem for the audience.
Once you have a rollback point, a test matrix, and a clear scope, you can download the ZIP archive and begin with one test post. This makes installation a controlled experiment rather than an irreversible change to the entire site.
CodeCanyon Content Protector Setup Video
This video complements the guide: a product video. Open it after the basic setup to compare the interface and sequence of actions.

