


Advanced Scripts - WordPress Plugin
Advanced Scripts is a versatile and powerful plugin designed specifically for WordPress users. This plugin serves as a script manager, allowing users to effortlessly manage and execute various scripts on their WordPress websites. With an intuitive user interface and extensive features, Advanced Scripts provides a seamless experience for users looking to enhance the functionality of their websites through the implementation of custom scripts.
Plugin Features
This plugin empowers website owners and developers by providing a centralized platform to execute scripts without the need for manual implementation. With Advanced Scripts, users can easily add, edit, and customize scripts directly within the WordPress dashboard. This streamlines the process of script management and eliminates the need for manual coding or editing of website files.
One of the standout features of this plugin is its ability to prioritize scripts based on specific conditions or criteria. Users can prioritize scripts based on URL parameters, browser types, user roles, or any other custom conditions to ensure scripts are executed accurately and efficiently. This level of customization allows website owners to tailor their scripts to specific scenarios and maximize their effectiveness.
Additionally, this plugin offers a comprehensive library of pre-built script examples to help users get started. These examples cover a wide range of functionality, including analytics tracking, conversion tracking, A/B testing, and more. With this library, users can quickly implement common script functionalities without the need for extensive coding knowledge.
Furthermore, Advanced Scripts provides advanced debugging tools to assist in identifying and resolving any script-related issues. Users can easily track script execution, view error logs, and monitor script performance to ensure optimal functionality of their website. This plugin also offers comprehensive documentation and support resources to help users troubleshoot and get the most out of their scripts.
Overall, the Advanced Scripts plugin for WordPress is a valuable tool for website owners and developers looking to enhance their websites with custom scripts. This plugin simplifies the process of script management, offering a user-friendly interface, customization options, pre-built examples, and effective debugging tools. By leveraging the potential of this plugin, users can unlock a wide range of possibilities to enhance the functionality and performance of their WordPress websites.

A Practical Guide to Advanced Scripts: Code, Resource Loading, and Safe Testing in WordPress
Advanced Scripts becomes useful not when you simply need to paste one snippet somewhere on a site, but when custom code starts taking on a life of its own: one style is needed only on a landing page, a JavaScript library only on a gallery page, an analytics tag in a specific template location, and a PHP change must run at exactly the right point in the WordPress lifecycle. In that situation, the real task is not to "add code," but to maintain a clear relationship between the goal, code type, execution location, condition, and verification method.
This guide does not repeat the plugin's short product description. Instead, it walks through a practical workflow: how to prepare a test, install and enable Advanced Scripts, fill out each script card, understand why wp_head and wp_footer are not interchangeable, load CSS or JavaScript from a URL, decide when SCSS/LESS makes sense, check storage status, and recover if a PHP snippet disrupts the WordPress admin area.
Throughout this guide, the word "script" means a managed item inside Advanced Scripts, not necessarily JavaScript. The plugin supports PHP, CSS, JavaScript, HTML, SCSS, and LESS, along with custom hooks. A single site may therefore contain a design adjustment, a small server-side function, and an HTML ownership-verification tag, but their risks and verification methods are different.
The best way to get predictable outcomes is to treat every item as a small change with its own record: a clear name, one type, one purpose, an expected execution location, a limited scope, and an obvious way to disable it. That turns Advanced Scripts from a storage area for random inserts into an orderly manager for WordPress technical enhancements.

Not a collection of snippets, but a code manager for your site
WordPress sites often do not face one large development task, but a series of small ones. You may need to adjust a form's styling, add a client-side library to one page, output an HTML fragment in a template, apply a PHP function to a known WordPress hook, or temporarily test an idea. If all of these changes go into a theme file, they become mixed into the template code and may disappear after a theme update. If you install a separate extension for every task, the number of admin panels, update points, and places to investigate when something breaks keeps growing.
Advanced Scripts brings these types of work together in one interface. According to its official description, the plugin is designed for PHP, CSS, JavaScript, HTML, SCSS, and LESS, and can work with custom hooks, external resources, and HTML tracking snippets. That does not mean it should replace a full plugin for complex business logic. Its strength is in transparent, local, maintainable changes where it matters that you can quickly see where something is enabled and disable it without editing theme files.
What changes after you add an item
Every item follows the same conceptual path. First, there is an input: code text, the URL of an external file, or a ready-made HTML fragment. Advanced Scripts then handles it according to the selected type. The location setting determines whether the output applies to the public site, the admin area, or a specific hook. Finally, an active item produces an observable effect: it changes markup, loads a style, runs server-side code, or adds a resource to the document.
The order matters. You should not activate a snippet first and only then try to determine when it needs to run. For example, CSS rules for a public page and PHP for handling a WordPress action may have similar names, but they are different classes of change. With CSS, you would normally inspect the page source, cascade, and visible styling. With PHP, you check for errors, the intended hook, access permissions, logs, and behavior across several use cases. The sooner that difference is documented in the item card, the less expensive it is to correct a problem.
When Advanced Scripts is especially useful
The plugin works well on sites where technical adjustments are made regularly but do not amount to a standalone product. That might be an agency site with several service pages, a company site with analytics integrations, a project built with a visual builder, a store with one localized interface adjustment, or an editorial site where some enhancements are made by a developer while others simply need to be enabled or disabled without searching through files.
A practical sign that a task is a good fit sounds like this: "I can describe the change, its scope, and its expected effect in one sentence." For example: "Load gallery styles only on the portfolio page" or "Output a verification tag in the document." If the task instead sounds like "Build a complex integration with an external system, store data, provide a settings screen for several roles, and cover it with tests," it is better to consider a custom plugin or a dedicated development project.
What the plugin does not replace
A snippet manager does not replace backups, a staging environment, access control, or sound update practices. It also does not make arbitrary PHP automatically safe. Safe Mode can help restore access in a particular situation, but it does not prove that business logic is correct or replace testing the public site. Likewise, the ability to load a file from a CDN does not answer questions about privacy, licensing, service availability, dependencies, or performance.
It is helpful to think of Advanced Scripts as an execution and record-keeping layer. Responsibility for what the code does remains with the author of the change. Before saving, you should know what every line does, where the snippet came from, which pages it should run on, and how to remove it without side effects. This is especially important for code found in discussions, because the context of another site's setup almost never matches yours exactly.
Who this approach is for, and where to stop
For the owner of a small WordPress site, Advanced Scripts is convenient when several tested changes need to be kept in one place without editing the active theme file. For a front-end developer, it can serve as a workspace for CSS, SCSS, or LESS that needs to be enabled for a specific task. For a developer, its value is usually in precise hook targeting, priority control, and avoiding the need to scatter small enhancements across a child theme, separate header/footer plugins, and random files.
The plugin is useful to a team only when there are clear rules. Decide in advance who is allowed to create PHP snippets, who may only enable pre-approved items, where the source for complex changes is stored, and who is responsible for post-update checks. If every administrator can paste unknown PHP directly into a live site, the problem is not the manager interface, but the access process.
Well suited to localized functionality
Here, "localized" does not necessarily mean one page. It means a change with a limited purpose: styling for a component, loading a verified library, a small HTML fragment for a service, a server-side function on a documented hook, or a supporting admin customization. You can name it, test it, and disable it with one action if necessary. This format works particularly well for work that should survive a theme change but does not require its own user interface.
For example, a photographer's site can load external gallery CSS and JavaScript only on static portfolio pages. A service site can add HTML provided by an analytics service, but only after its source has been verified. A project using Oxygen can use SCSS/LESS and builder-related global colors where the specific configuration supports them. In all three cases, the outcome is immediately visible and separate from the rest of the site.
Not suitable for unclear or third-party code
Do not use the editor as a place to experiment with a large snippet whose purpose you do not understand. Phrases such as "paste this into functions.php" do not explain the level of risk, required dependencies, or execution scope. Moving that code into Advanced Scripts does not make it more understandable. First find the original source, check which WordPress and extension versions it was written for, identify the required hook, and test it on a copy of the site.
Take extra care with snippets that affect authentication, payments, checkout, personal data, email delivery, user permissions, or security headers. If changes affect these areas, prepare a backup access route and a complete rollback plan. Do not enable that kind of PHP on a live site at the same time as updating a theme, builder, or several other plugins. Otherwise, the symptoms will not reveal which change caused the issue.
Decide before installation: one role, one tool
Before installing the plugin, perform a short inventory. List the places where custom code is already stored: a child theme, an additional CSS field, header/footer inserts, a separate snippet plugin, builder settings, and server files. Do not move everything mechanically. For each item, ask: Is it still needed? Does it have an owner? Can it be removed without an effect? Does it need a new home in Advanced Scripts?
This step prevents one of the most common sources of confusion: after migration, CSS starts loading twice, while JavaScript is loaded both through the theme and through the new manager. The site may appear to work, but duplicate click handlers, repeated requests, and harder-to-debug style conflicts begin to appear. During migration, keep only one source for each specific change enabled. Disable the old source after verifying the new one, not before.
Preparation: a testing route, backup access, and a dependency map
Before opening the page to create your first script, prepare the conditions for a safe experiment rather than the code itself. The most sensible option is a separate staging copy of the site with the same theme and key extensions. There, you can enable PHP, change resource order, test the admin area, and see error messages without putting visitors at risk. Official WordPress documentation explicitly recommends using debugging tools in a local or staging environment rather than on a live site.
If you do not have a full copy of the site, at least choose a short maintenance window, create a backup, keep a second administrator login available, and prepare a list of what you will test. Do not run the first test from a mobile browser, where it is harder to open the console, page source, and developer tools. You need a standard desktop browser, an administrator account, and the ability to open a public page in a private window while signed out.
Minimum map before enabling anything
- Change goal. One specific sentence describing what should change and for whom.
- Type. PHP, CSS, JavaScript, HTML, SCSS/LESS, or an external file.
- Scope. Public site, admin area, one page, a group of pages, or a specific hook.
- Dependencies. Theme, builder, library, analytics service, other code, or load order.
- Verification. What will be visible in the browser, page source, console, Site Health, or log.
- Rollback. How to disable this exact item and what does not need to be touched during rollback.
The purpose of the map is not bureaucracy. It helps you spot incompatibilities before activation. If you cannot identify the scope, condition, and verification method, you are not yet ready to enable the script. For example, "speed up the site" is too vague. In contrast, "load a library only on one page after the required markup already exists" contains a testable hypothesis and implies measurement before and after the change.
Check the site's baseline state
Open a key public page before making changes, both normally and in a private window. Check whether the console already contains errors, whether forms are working, whether images load, and whether the menu functions correctly. Then take a screenshot or save a short note about the baseline behavior. This is not a formality: if an error appears after activation, you will compare against a known state instead of relying on memory.
For PHP, it is useful to open the Site Health section in advance and know where your environment exposes its error log. WordPress describes WP_DEBUG, WP_DEBUG_LOG, and WP_DEBUG_DISPLAY as tools for development and diagnostics. Do not display errors to visitors on a live site. If diagnostic mode is required, use a staging environment or logging without rendering messages in the public page markup.
Separate code by risk level
The safest place to start is usually CSS that affects one visible block and can easily be disabled. Next come external CSS/JS files, provided you know their source and dependencies. HTML for tags and verification requires checking its document location and privacy policy implications. PHP carries greater risk because it runs on the server and can affect login, the admin area, or an entire request. SCSS/LESS also requires understanding the compiled output.
Do not combine different risk levels in one card. If CSS, JavaScript, and PHP are saved together, you cannot quickly disable only the cause of an error. One item, one reason for enabling it, one expected outcome.
Installation and an initial check without unnecessary changes
Advanced Scripts is distributed outside the official WordPress directory, so it is commonly installed from a ZIP archive obtained legitimately from the developer or your account. The standard WordPress path for this archive is Plugins > Add New, then Upload Plugin, select the ZIP file, install it, and choose Activate. Do not unpack the archive manually if standard installation is available: it makes it easier to see an error message, a directory-name conflict, or a file-permission requirement.
After activation, do not begin with PHP. First locate the plugin's menu item and open the scripts list. Confirm that the interface is available to your account, that you can create a test item, and that the site has not encountered an unexpected failure. If the panel does not open or errors appear immediately after activation, stop. Do not try to "fix" the installation with another code snippet.
Your first test should be reversible
Create a very small CSS item for an unimportant test page rather than for the homepage. For example, add a thin outline to a prepared block with the as-check class. The goal is not to create a polished design, but to verify the entire chain: saving, activation, clearing cache if needed, opening the page in a private window, and returning to the previous appearance after deactivation.
.as-check {
  outline: 2px solid #3b6f75;
  outline-offset: 4px;
}
This snippet does not depend on theme internals, alter a checkout form, or involve PHP. If nothing changes on the page, that is still a useful discovery: you can check the insertion location, cache, and presence of the class before adding more complex code. After the test, disable or remove the item if it is no longer needed. A test is successful only when you have observed both activation and reversible deactivation.
Set naming rules immediately
A name should explain the task and scope, not the syntax. Good examples: Portfolio - GLightbox CSS - public pages, Analytics verification - HTML - head, Oxygen editor colors - SCSS hook. Poor examples: new code, test 2, fix. With the first approach, six months later you can understand what is happening and where to look for the effect. With the second, you must open every item and read its code.
If a description field is available, record the source, dependency, and verification method there. For example: "Source: library documentation. Works only after the gallery HTML markup is present. Test: open the portfolio page, click an image, and confirm there are no console errors. Rollback: disable both CSS/JS items." This is more useful than a long comment inside the code because the information is visible before opening the editor.
The script card: type, location, hook, priority, and condition
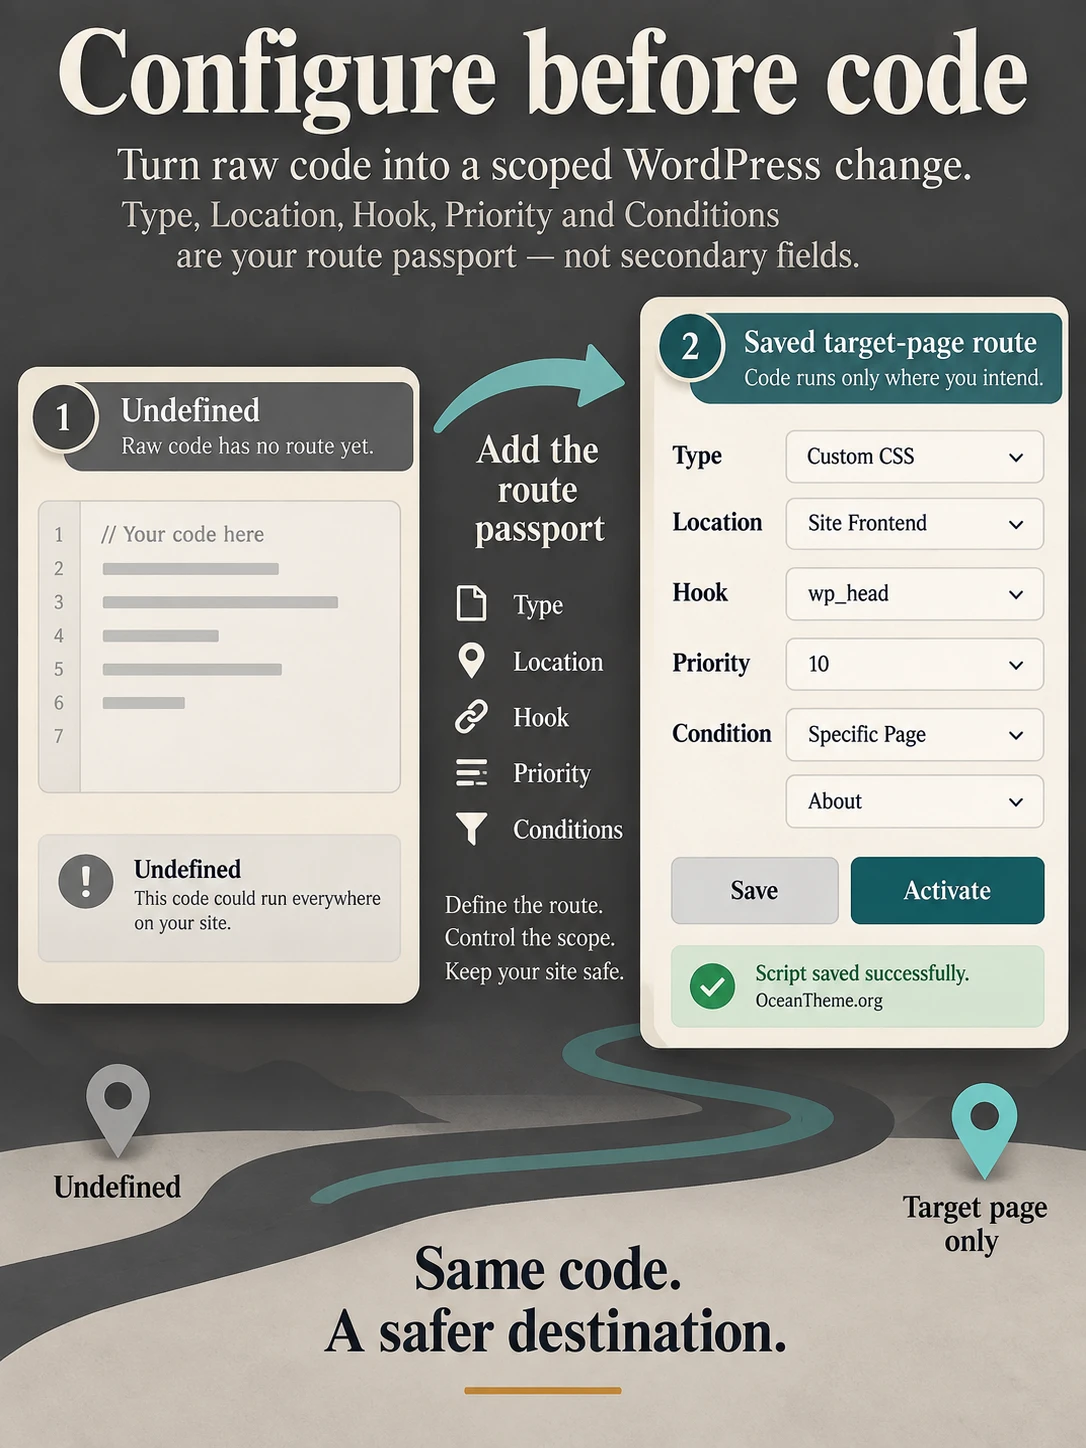
The most valuable part of configuring Advanced Scripts is not the editor field, but the settings around it. They answer questions that code alone cannot answer: where it should appear, when it should run, what should happen before it, whether it belongs on the public site or in the admin area, and whether it should avoid running on other pages. In one detailed third-party example for the plugin, item creation starts under Tools > Advanced Scripts, followed by selecting the type, Location, hook, priority, and condition. Labels may differ slightly in your version, so focus primarily on what each field means.
Before writing the content, fill out the item's record. Start with the name. Then select the type. Then define the scope. Only after that should you choose the hook and condition. This order reduces the risk of putting correct code in the wrong part of the document. For an external file, decide in advance whether it must be available before dependent code runs; for PHP, determine which exact WordPress stage it requires.
Type is a contract, not a label
The type tells the plugin how to handle the content. PHP runs on the server and is usually attached to the WordPress lifecycle. CSS affects presentation. JavaScript runs in the browser and depends on load order and the presence of DOM elements. HTML adds markup or code provided by an external service. SCSS and LESS must be transformed into CSS. External resources do not copy code into the editor; they load a file through a URL or a Media Library item, as described on the plugin's official page.
Do not try to fix an error by randomly switching types. JavaScript inserted as HTML may appear in the document in the wrong form. CSS treated as PHP will not follow the normal output path. SCSS should not be treated as ordinary CSS if you expect variables and nesting to work. First make sure the source material truly belongs to the selected type, then test its smallest version on a separate page.
Location answers the question "where?"
The key decision is whether the code belongs on the public site or in the admin area. Code that changes a visitor-facing page usually does not need to run in the administrative interface. Conversely, an editor adjustment should not accidentally reach site visitors. A practical Advanced Scripts guide uses Location: Front-end for CSS and JavaScript loaded on a public page. Another CSS tutorial specifies Location: WP header. The point is the same: before activation, choose the context where the output is actually needed.
If the product offers a broader option such as "everywhere," do not select it out of habit. It is the broadest scope, not the best default. The wider the scope, the more likely a library will load where it does nothing or collide with builder markup, the login screen, or an admin page. Start with the smallest working scope and expand it only after verification.
A hook sets the timing
A hook is needed when order matters. WordPress describes wp_head as an action that outputs data and resources inside the public theme's head. wp_footer runs before the closing body tag. An external Advanced Scripts tutorial pairs CSS with wp_head and JavaScript with wp_footer. This is a useful starting pattern, but not a rule: a particular library may need a different order, and the theme must actually call the relevant hook.
It is especially important to remember the dependency on the theme. Official WordPress documentation notes that wp_footer is theme-dependent: it is available when the theme author included the call. If a script attached to this hook does not appear on the page, do not immediately rewrite the JavaScript. Check the page's HTML source, the theme's hook support, the active scope, and the condition. With a custom theme or builder, this may be the main explanation for the symptom.
Priority is needed only for a known dependency
Priority changes the order of callbacks on the same hook. It is justified when you know exactly that your function must run before or after another known callback. Do not raise or lower a number in the hope of making the site "faster." Priority is not an optimization by itself. It is an ordering tool, and it is useful to record the reason in the description: "after resource registration," "before this block is rendered," or "default priority retained because there is no dependency."
For CSS and JavaScript, users are more likely to encounter item order than numeric priority. The GLightbox tutorial includes an important point: when several JS files depend on one another, their order can be adjusted by dragging items in the list. This is a reminder that "enabled" does not necessarily mean "ready": the main file must appear before the code that refers to it.
A condition limits the cost of a change
A condition is useful not only for precise behavior, but also for maintainability. The practical CSS/JS example uses the is_page() expression, which applies the library to static pages. This is not a universal pattern for every site. One project may require a specific template, another a single page, and a third all posts of a certain type. The principle remains constant: the rule should be as narrow as possible without losing the purpose of the change.
Do not write a complex condition without testing it. First enable the item for one known URL and confirm that it appears exactly there. Then open a similar page where it should not appear. If the plugin allows conditions to be selected through the interface, describe in plain language which set of pages is covered. If the condition is entered as a PHP expression, test it separately and do not add several independent branches before verifying the first one.
Routing code: how not to confuse the public site, head, and footer
Placement is a causal part of the configuration. The same CSS file may be valid but load too late for an important hero section. The same JavaScript may work correctly but fail to find DOM elements if it runs before they exist. The same PHP code may be syntactically valid but run on a hook where the required data is not yet available. Before creating each item, it is useful to state the chain clearly: "What already exists at the time this runs, and what should appear after it?"
CSS and resources in wp_head
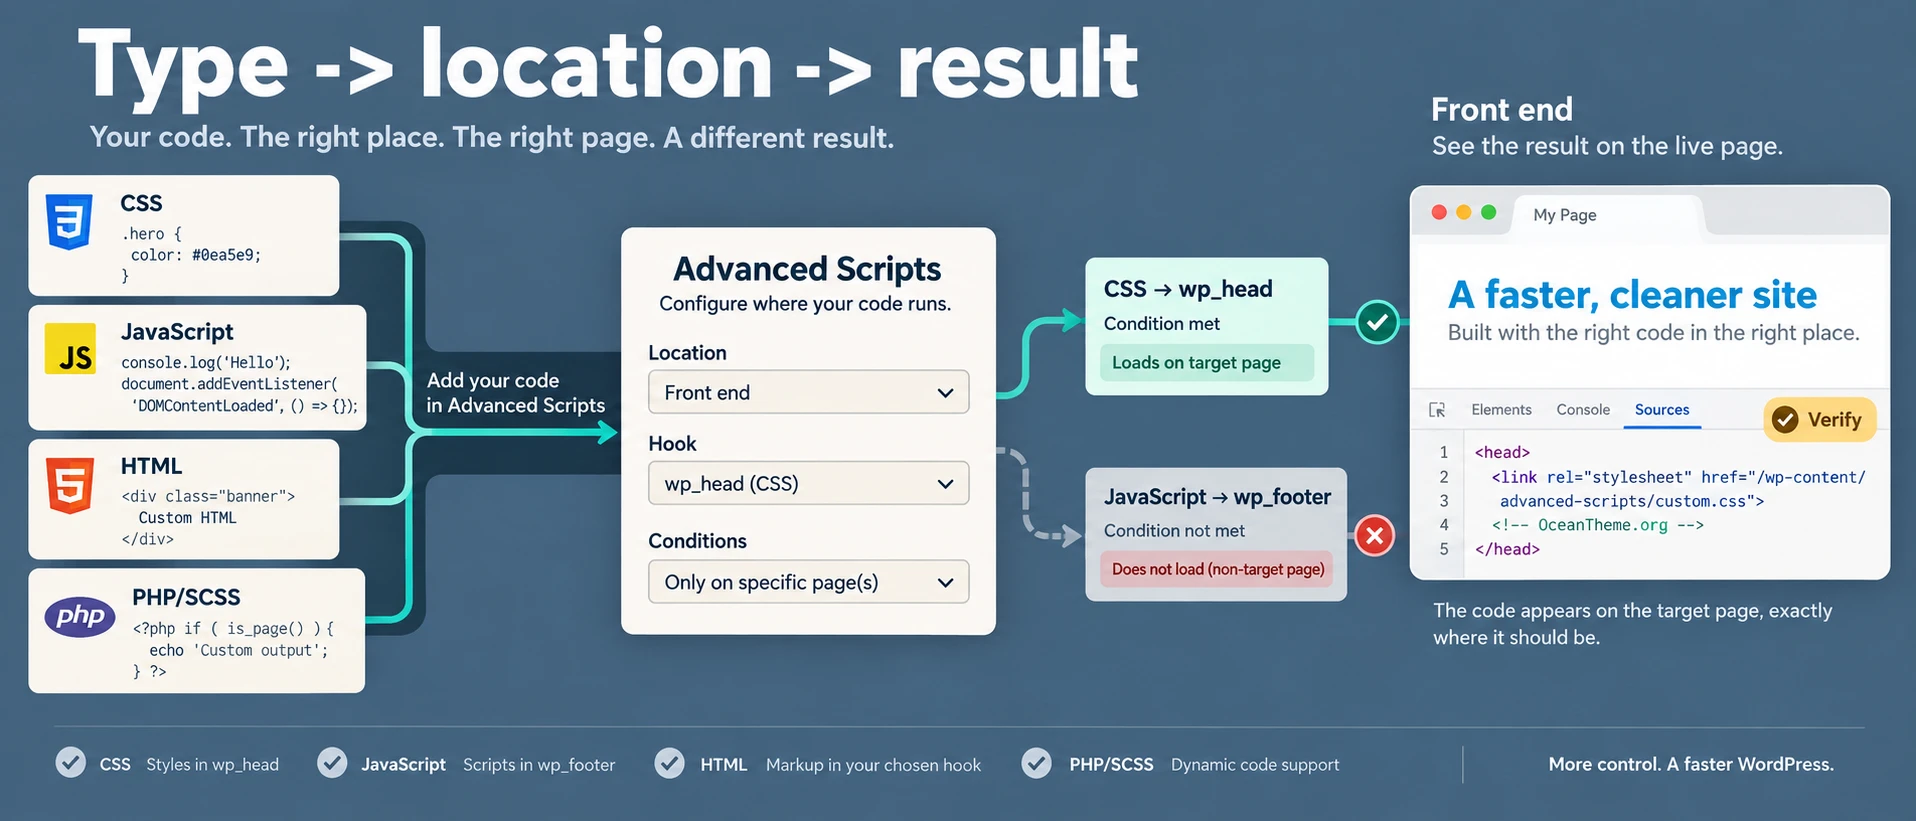
CSS is usually placed in the head when rules should apply before the page first renders. Official WordPress documentation confirms that wp_head prints scripts or data in the public site's head. A practical Advanced Scripts resource-loading article shows the combination CSS: Load from URL, Location: Front-end, Hooks: wp_head, and the is_page() condition. This is a useful example for an external stylesheet, but the URL itself must be trustworthy and the scope must be justified.
Check such an item in the browser's Network panel and in the HTML source. The file should load without an error, return the expected content type, and appear only once. Then make sure the rule is actually used. If DevTools shows that your CSS loses to a more specific theme rule, do not immediately add !important throughout the file. First identify the selector and cascade order that are needed, or narrow the scope of the specific adjustment.
JavaScript near wp_footer
JavaScript that works with page elements often makes sense in the footer because the markup is closer to complete by that point. The official description of wp_footer states that the action runs before the closing body tag, while a specialized tutorial associates it with JavaScript: Load from URL. Do not confuse loading a file with DOM readiness. If a library requires initialization, the following code must wait until the required elements actually exist.
Verification has at least three parts. The file itself appears in Network. The Console contains no errors such as a missing variable. The page performs the expected action. If the library loads but clicking does not work, the issue is usually in one of four places: the selector does not match the markup, the code runs too early, a dependency has not loaded in time, or the condition does not cover the required URL. This diagnostic pattern is more useful than changing hooks at random.
PHP on custom hooks
The official Advanced Scripts page highlights custom hooks, dynamic callback functions, and execution priority as capabilities for more advanced PHP work. This is where the plugin is both most powerful and most demanding of discipline. PHP should not output random markup or run queries everywhere without understanding the context. First find a documented hook from WordPress, the theme, or a particular extension, then confirm which arguments it passes and when it is called.
If the exact hook is not confirmed by a primary source, do not paste PHP "just to try it" on a live site. This is especially important for internal hooks in third-party themes and builders. An external Oxygen example uses oxygen_enqueue_ui_scripts to customize the editor, but that applies to the specific Oxygen ecosystem, not a standard public WordPress page. There are always two conditions for correctness: the hook exists in your environment, and your code is designed for that exact moment.
An HTML fragment is not a place for an unknown tracker
Advanced Scripts can place HTML tracking snippets, including analytics-service code and a meta tag for site verification. This is convenient because you do not need to search through theme files for that material. But convenience does not remove the need for verification. Use only code issued by your service or its official documentation, save a link to the source in the item description, and decide in advance where in the document it belongs.
After enabling it, open the HTML source and find the tag's unique identifier. Then confirm that it appears once rather than being duplicated by the old theme, another header/footer tool, or a container. For analytics, also make sure the selected method aligns with your privacy policy, consent mechanism, and jurisdictional requirements. The plugin inserts a snippet technically, but the site owner determines the legal basis and data accuracy.
Styles as a system: SCSS, LESS, partials, and Oxygen Global Colors
Regular CSS is convenient while there are only a few rules. As repeated colors, dimensions, button states, and related components appear, the risk of copying the same values grows. Advanced Scripts states that it supports SCSS and LESS, transforming code into standard CSS that is added to the page output. This makes it possible to organize styles as a small collection of source files rather than one long, unstructured block.
Compilation does not make a complex style system mandatory. For two rules on one page, regular CSS is usually simpler and safer. SCSS/LESS is justified when there are repeated values, understandable modules, and someone who can maintain the code later. Otherwise, nesting and variables only make the task more complicated. Start small: one basic partial for colors and one main item that imports it.
How to think about partials
A published Advanced Scripts update overview describes SCSS partials: styles can be split into small reusable components, and the import rule is shown under the item type. Nested use of partials is also supported. File names are generated from an item's title, so partials with the same name require unique prefixes. This is an important organizational detail: colors on one site is easier to understand than ten items vaguely named main.
/* Partial: brand-tokens */
$brand-accent: #3b6f75;
$brand-surface: #eef4f3;

/* Main SCSS item */
@import 'brand-tokens';

.as-note {
  border-left: 4px solid $brand-accent;
  background: $brand-surface;
  padding: 1rem;
}
The example demonstrates a structure, not a mandatory naming convention. First save the partial containing tokens, then the main item with the import. In a particular interface, the exact import rule may be shown by the plugin, so do not replace it with a guess. After activation, always inspect the final CSS: variables and nested syntax should be gone, while the browser should receive ordinary rules. If compilation fails, disable the item, fix the smallest error, and enable it again.
Do not move all old CSS into SCSS
A bulk migration solely for the sake of the format rarely provides value. It can disrupt cascade order, make the sources of older rules unclear, and create many new failure points at once. A more sensible path is to use SCSS for new, consistent components. Leave old rules alone until a separate refactoring effort has a measurable goal: remove duplicates, extract shared tokens, narrow scope, or reduce conflicts.
A useful discipline is one partial for base values, one item for a specific component, and one test URL. Then, when an accent color changes, it is clear what needs to be checked. If a shared partial contains styles for the menu, form, cards, modal, and checkout page, every change becomes a risky release. Modularity is helpful only when boundaries reflect the site's actual structure.
Working with Oxygen Global Colors
For Oxygen sites, the official Advanced Scripts page states that the Oxygen global color palette is available within CSS, SCSS, and LESS. The practical benefit of this integration is consistency: if a color changes in the builder palette, related custom styles can remain aligned with the overall design system. This is especially valuable when an enhancement should not become a separate palette disconnected from the site's components.
However, do not make assumptions about color names or syntax. First create one test component using a known global color, save it on a test page, change the color in Oxygen, and confirm that the rendered appearance truly updates. If the site does not use Oxygen, this section simply does not apply. Do not add related mechanisms in the hope that they will improve a standard WordPress theme.
Practical use case: load CSS and JavaScript only where a gallery is needed
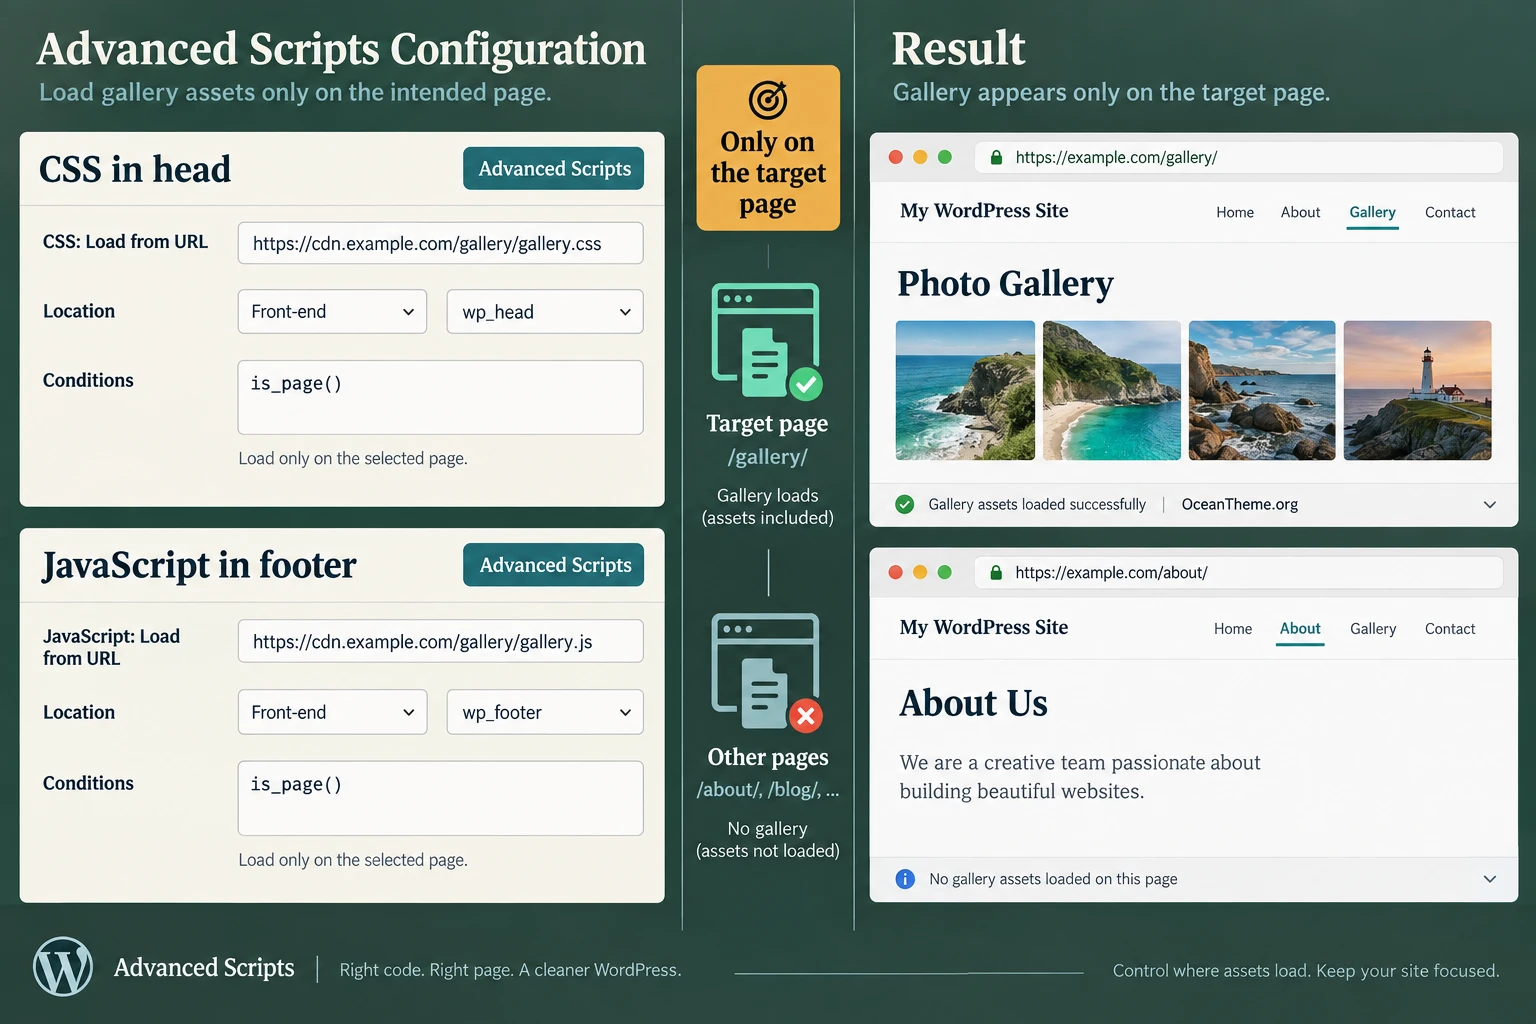
Consider a reproducible task based on a specialized Advanced Scripts tutorial: a site has several static portfolio pages, and an image-enlargement gallery is needed only on those pages. The goal is not to load the library on the homepage, blog, or admin area. To accomplish this, create two separate items: one CSS resource and one JavaScript resource. They receive clear names, different types, the same limited context, and are tested together.
Goal and use-case preparation
Before configuring anything, make sure the test page already contains markup that the selected library can work with. A library does not create a meaningful gallery out of nothing: it needs links, images, or other expected HTML. Save the URL of the test page. Open it in a private window and make sure the current version does not produce errors. Record where the CSS and JavaScript came from: the vendor's official CDN or a trusted library source. Do not use unknown URLs from comments, and do not load different CSS and JS versions without a clear reason.
Also check whether the theme or builder already includes a similar library. If a theme component already uses its own lightbox, an additional file can cause duplicate initialization or style conflicts. For the first test, choose a separate new gallery and do not replace a working site-wide interface all at once. An external resource should be loaded for a specific function, not just because a CDN seems convenient.
Create the CSS item
The tutorial uses the following conceptual set of parameters: a title such as Gallery CSS, type CSS: Load from URL, scope Front-end, hook wp_head, a stylesheet URL, and condition is_page(). In your case, make the name more specific, for example Portfolio gallery - CSS - static pages. If the interface lets you load a file from the Media Library instead of a URL, choose the option that matches your update policy and source-control requirements.
Save the item, but do not proceed until you have tested it separately. Open the test page and check Network. The CSS should load without an error. Look for the required stylesheet link in the source. Then open a blog page and confirm that the file is absent there if the condition is intended only for static pages. This proves not only that loading works, but also that the scope has not become broader than intended.
Create the JavaScript item
Now add a second, separate item. The practical example specifies JavaScript: Load from URL, Location: Front-end, the wp_footer hook, priority, and the same is_page() condition. For maintainability, name it Portfolio gallery - JS - static pages. If the library requires separate initialization, do not hide it in an arbitrary place. First make sure the resource itself loads, then add the smallest initialization snippet as a third independent item with its dependency documented.
When multiple files are involved, watch the order. If the main file depends on a supporting file, it must not load first. The tutorial notes that order can be adjusted in the items list. Do not solve this with random JavaScript delays until the resource order has been confirmed. A delay can hide a failure on a fast connection and reappear for a visitor with slower internet access.
Verify on the page and beyond it
On the target page, open the gallery and perform the exact action for which the library was added: click an image, confirm that the enlarged view opens, close it, and repeat on a second item. Then open the Console. There should be no errors about an unknown function, a blocked resource, or a missing DOM element. After that, return to Advanced Scripts, disable only the JS item, and repeat the test. The expected effect should disappear while the page itself remains functional. Re-enable the JS and confirm that the effect returns.
Next, test several non-target pages. They should show no trace of the loaded library in Network or the HTML source if the condition is truly limited. This check often finds conditional-expression errors or an overly broad scope. Finally, check the mobile view as a user-facing outcome, but do not use a mobile browser instead of desktop tools for console and network-request testing.
Common issues that break this setup
The first issue is caching. After saving a change, old HTML or combined CSS can remain in hosting, CDN, or optimization-plugin cache. Use a private window and clear only the cache you manage. The second is a version conflict. If the theme already loads the same library, adding another file can cause errors even though Network shows successful responses. The third is an incorrect initialization selector. The resource loads, but the page has no elements with the required class or attribute.
The fourth issue is the condition. is_page() in the learning example covers static pages, but not necessarily your custom post type, archive, or template. The fifth is placement dependency. CSS may load correctly, but JavaScript may run in the head even though it expects elements in the body. Each case is tested through a separate observation: URL, source code, Network, Console, DOM, and the actual click. Do not change every setting at once.
External resources and HTML tracking snippets: source control matters more than convenience
The official Advanced Scripts page specifically mentions loading external resources through a CDN URL or a file from the Media Library. This removes the need to write custom PHP to register scripts and styles in many simple cases. It also lists HTML fragments for analytics and ownership verification. These capabilities are useful, but they belong to an area where technical correctness is not the same as security or compliance with site policy.
Choosing between a URL and a Media Library file
A CDN URL is convenient when a library provider publishes a stable official address and you know which version you are loading. Its advantage is that you do not need to keep a copy of the file on the site. Its downside is that the resource's availability and content depend on an external provider. A Media Library file provides more local control, but requires you to track updates and usage rights yourself. There is no universal winner: the choice depends on project policy, privacy requirements, and the update process.
In either case, store the origin in the item description: the documentation page address, library name, date of internal review, and purpose. You do not need to include dates in the public article, but in an actual working item, a note helps explain why that file is connected. If a resource affects a form, account area, or any critical section, test it on a copy of the site and avoid replacing URLs automatically without regression testing.
A method for analytics and verification tags
First compare provider HTML code against the service's own official documentation. Then insert it into a dedicated item with a name such as Search verification - HTML - document head or Analytics container - HTML - public site. After saving, inspect the source of a public page where it should appear. If the tag is needed only for verification, do not leave it there indefinitely without thought after successful verification: follow the service rules and the project's internal policy.
For analytics, a technical check alone is not enough. Confirm that there is no duplicate from another container, that an event is not sent twice, and that applying it to visitors matches the selected consent mechanism. Do not enable snippets that attempt to silently bypass user choice. Advanced Scripts provides a placement point, but it is not a way to bypass privacy or security requirements.
Performance: measure a specific path
You cannot claim that every external resource speeds up a site or that every footer script makes a page faster. It depends on file size, caching, dependencies, and whether resources load on unnecessary pages. In the gallery setup, the real optimization does not come from the hook itself, but from limiting scope: the library does not load where there is no gallery. Therefore, measure the same page before and after under the same conditions, rather than comparing random results from separate runs.
Look at the number of requests, transferred file sizes, loading errors, and hero-section rendering. If external CSS is needed by only one component, keep it within a limited scope. If JavaScript depends on a visitor action, check whether an error appears when cache is disabled. Do not combine a performance check with a bulk replacement of ten resources, because the reason for each change will be lost.
After an update or migration: storage, SCSS, and Site Health
In a published Advanced Scripts update overview, the developer described a storage-mechanism change: a standard site uses the wp-content/advanced-scripts directory, while multisite installations use a path containing the site identifier. PHP files live in a separate directory, are generated when an item is created or updated, and the storage system includes checks. These details matter not because an administrator should edit files manually, but because they explain a class of symptoms after migration, permission changes, or environment updates.
The same article mentions WordPress Site Health integration. It checks whether the directory exists, is writable, and contains index files; it also tests PHP file creation, execution, and deletion. If scripts behave unusually after an update or migration, Site Health should be the first controlled place to investigate, rather than an excuse to immediately change code. It gives you a direction for the investigation: the PHP itself, directory state, permissions, or leftovers from the old mechanism.
How to interpret Site Health results
A storage check does not answer whether your function is written correctly. It answers a more basic question: can the plugin create and use the necessary files? If Site Health reports a directory or write issue, stop risky experiments, record the exact message, and provide it to the hosting administrator or developer. Do not randomly change permissions for all of wp-content, and do not delete files until you understand which ones belong to the plugin.
If Site Health reports a normal state but a PHP item still causes an error, move to separate snippet diagnostics: temporarily deactivate it, inspect the log on a staging site, reduce the code to the smallest case, and confirm that the selected hook exists. Keeping these paths separate saves time. In one case, the environment needs repair; in the other, the code behavior needs correction.
Leftovers and migration
The official release overview specifically says that old temporary files are not cleaned up automatically for security reasons: automatic deletion could affect important files. This is a sensible boundary. After migration, do not treat every old folder as junk. First make sure the new mechanism works, a backup exists, and the specific path really belongs to an old plugin configuration. Then follow the interface guidance or the developer's instructions.
For SCSS, check not only the editor after migration, but also the partials. Confirm that unique names do not conflict, the import rule really points to the intended module, and public CSS compiles. If you are moving a site between servers, run one control test for each type: CSS, external JS, and a small disabled PHP item. Do not enable the entire set of old snippets at once, or one error will be hidden by the noise from the rest.
Acceptance protocol: how to prove the configuration works
The phrase "everything looks fine on the site" is not enough for acceptance. Every code type has its own observable outcome. CSS should appear in the cascade and modify a specific element. JavaScript should load, produce no error, and perform an action. HTML should appear once in the required part of the document. PHP should run on the intended hook, avoid critical errors, and leave non-target use cases unchanged. SCSS/LESS should compile into valid CSS.
A good test includes both a positive and a negative check. The positive check proves that the target page has the expected output. The negative check proves that a similar non-target page does not. Finish with a reversible test: disable one item and confirm that only its effect disappears. This protects against false success when similar behavior already exists in the theme or another plugin.
Evidence table by type
| Type | Positive outcome | Boundary check | Safe rollback |
|---|---|---|---|
| CSS | The rule is visible in DevTools and changes the target block. | The rule or effect is absent on a non-target URL. | Deactivate one CSS item and clear the cache you manage. |
| JavaScript | The file loads, the Console is clean, and the action runs. | The feature does not run where it should not appear. | Disable the JS item, then confirm that the page remains accessible. |
| HTML | The fragment is found in the source document at the intended location. | The identifier is not duplicated by another source. | Deactivate the HTML item and search for the fragment again. |
| PHP | The intended server-side behavior can be reproduced without errors. | Non-target roles, URLs, and admin screens remain unchanged. | Deactivate the item; if access is lost, use Safe Mode according to the official instructions. |
| SCSS/LESS | The browser receives compiled CSS and the style applies. | The import does not break other style modules. | Disable the main item, then check the partial separately. |
Test while signed out
An administrator often sees a different page: the toolbar, browser cache, loaded administrative styles, and access to restricted content. For that reason, always open the public outcome in a private window or another browser. This is particularly important for HTML tracking snippets, public CSS, and JavaScript that depends on ordinary visitor behavior. If a function is intended for an authenticated role, run a separate test for that role instead of substituting an administrator test.
For conditions, compare neighboring pages. If a script should work on static pages, open a static page and a blog post. If it should work only in the portfolio, open a portfolio page and a standard page. If it should work only in the admin area, confirm that the public HTML contains no trace of it. This approach is better than a single "check everywhere" because it exposes an overly broad scope before it becomes a performance or privacy problem.
Practical application models: not just where to insert code, but how to verify value
After the first successful test, it is tempting to turn Advanced Scripts into a universal container for every task. It is much more productive to choose several repeatable models and use the same reasoning for each: one input, a clear rule, visible output, verification, and safe deactivation. The examples below are not ready-made snippets for blind copying. They are decision-making models that help you choose the correct item type and avoid expanding the scope beyond what is useful.
Localized component styling without editing the theme
Goal: slightly change one self-contained component, such as an information block, contact form, or post card, without affecting the rest of the theme. Preparation: find a stable class that belongs only to the intended block. Do not begin with a chain of random builder classes if they change after every edit. In the block editor, you can often assign an additional CSS class; in a builder, use the provided class or component identifier.
Create a separate CSS item with a name that identifies the component and its scope, such as Knowledge base note - CSS - public. Select the public context and apply the rules first only on a test page. The output here is simple: the browser receives one rule, and a specific block changes its appearance. Verification consists of inspecting the DevTools cascade, using a private window, and opening a neighboring page with a similar but non-target block. If the effect reaches a nearby component, the cause is usually an overly broad selector, not Advanced Scripts.
Common pitfall: do not use a long chain of div elements and random classes as a way to "reach" an element. It is tied to the current markup and can break after a theme update. It is better to add your own meaningful class and limit the rule to it. The rollback is obvious: deactivate one CSS item. This reversibility is exactly why this model is usually safer than putting styling directly into theme files.
An external library for one functional area
Goal: add a client-side capability that the entire site does not need, such as a gallery, a small expand/collapse effect, data visualization, or a specialized form. Preparation: make sure the markup already exists and that the library provider documents which files and dependencies are required. Then create separate items for the stylesheet and JavaScript rather than one mixed item. For the documented CSS/JS URL workflow in Advanced Scripts, this lets you see which resource failed to load and disable it independently.
The product workflow looks like this: the CSS resource receives a public placement suitable for styles, JavaScript receives a location where the page has already been assembled, and a condition limits the target URLs. The final state is that the library exists only where it performs its intended task. Verification has four observations: both files appear on the target page, dependencies load in the correct order, the action works, and the non-target page has no unnecessary requests. This model does not support generic claims such as "the footer is always faster." Its value comes specifically from limited scope and a confirmed dependency.
Common pitfall: an external library can conflict with the same library loaded by the theme. The symptom may not be obvious immediately. Sometimes the first click works, while duplicate initialization appears only during page navigation, in a modal, or in a responsive layout. Therefore, after the positive test, run a negative one: disable the new JS item and confirm that the behavior disappears. If nothing changes, the code is already running from another source and you need an inventory first.
HTML for verification or measurement with duplicate control
Goal: place a short HTML fragment received from an external service where it will not be lost after a theme change. Preparation: obtain the code only from the service's official dashboard or documentation, verify its purpose and document location. In Advanced Scripts, create a dedicated HTML item and record the service, exact purpose, and source in its description. This is more useful than storing the fragment in a generic note or a forgotten theme field.
The internal workflow is minimal, but discipline matters. The input is an HTML fragment, routing settings place it in the required part of the public document, and the final state is confirmed by finding its unique identifier in the source. Test the page while signed out, and inspect not only the DOM inspector but also the raw HTML source, because some optimization systems can move or process inserts again. Then search for the same identifier in theme settings, builder settings, and old header/footer tools.
Common pitfall: for an analytics fragment, presence alone does not prove that data collection is lawful. Before enabling it, align it with the consent method and site policy. If the service provides updated code, replace the content of the existing named item rather than creating a second similar one. Rollback means deactivating that exact HTML item and confirming that the unique tag has disappeared from the document.
A small server-side enhancement on a documented hook
Goal: run a small server-side action that truly belongs in a snippet rather than build a standalone subsystem. Preparation: find official WordPress, theme, or extension documentation that specifies the hook, its arguments, and its context. Note whether it applies to the public site, admin area, or both. In Advanced Scripts, create a separate PHP item, record the hook source in its description, and begin with the smallest change you can observe without affecting forms, payments, or user access.
The chain works as follows: PHP receives execution through the selected hook, runs one function, and produces a predefined output. Verification is not limited to the absence of a white screen. You need to open the target use case, a neighboring use case, the admin area, and the log in a staging environment if the task affects server-side behavior. If the hook runs on every request, add the context check provided by the source and confirm that the function does not run where it is unnecessary.
Common pitfall: never name a PHP item simply functions. The name should reflect the hook and action. For example, Public notice - documented hook - PHP already points you in the right direction when investigating. If the output is unpredictable, the first action should be to roll back only this item, not edit code directly in production. Treat Safe Mode as an access-recovery path, not a standard development environment.
Global style tokens for an Oxygen site
Goal: maintain several related custom styles that should follow Oxygen's global palette. Preparation: confirm that the site really uses Oxygen and that the required global colors exist. Then create one small test SCSS or LESS item tied to a nonessential component. The official Advanced Scripts page states that Oxygen Global Colors can be used in CSS, SCSS, and LESS, but the exact names and availability of values depend on your builder configuration.
The workflow differs from plain CSS: first there is a builder global color and a style module, followed by compilation and public CSS. The outcome should be verifiable in both directions. First, the custom component inherits the expected color. Then change the test global color in staging and confirm that the final custom styling is synchronized. If this does not happen, do not scale the idea across the entire design; investigate the syntax in use, compilation path, and palette source.
Common pitfall: do not turn one global color into a hidden dependency for every component. Keep partial and class names understandable, and document palette changes. Then an edit in Oxygen will not become an unexpected reason why an Advanced Scripts component changed appearance across ten pages. The rollback remains the same: disable one main style and check its partial separately, without touching core, theme, or builder files.
Safe maintenance: fewer edits, more context
Code maintainability does not depend on line count, but on the ability to quickly answer four questions: who added the change, why it is needed, what it depends on, and what happens after it is disabled. In Advanced Scripts, these answers can be kept next to the item: in its name, description, folder, or team naming convention. The external Advanced Scripts QuickNav add-on shows why this becomes important as the number of snippets grows: it can display active and inactive items, groups, and a Safe Mode notice in the admin bar.
QuickNav is not a required part of Advanced Scripts and is unnecessary for basic configuration. However, the existence of such an add-on confirms a practical issue: when there are many items, navigation and classification matter more than another snippet. If you have accumulated twenty unclear entries, do not write another one first. Start with an audit: identify the owner, verify the purpose, disable outdated items on a staging copy, and give the remaining items meaningful names.
A minimum safe change process
- Define one observable goal and select the smallest appropriate code type.
- Verify the snippet source, dependency, and required hook.
- Create a separate item with a clear name and rollback description.
- Enable it first on a staging copy or a limited URL.
- Run positive, negative, and reversible tests.
- Only then move the outcome to production and repeat a short verification.
In practice, this does not slow work down. The time spent on one description and a control URL is usually less than the time needed to find an unknown function among ten active snippets. The process also protects against chained fixes, where a second snippet is added after an error, then a third, while the original cause remains hidden.
A small enhancement without touching core files
The safest enhancement for most sites is not a new PHP hook, but a carefully limited CSS item. For example, you can highlight an information block on one test page by tying rules to a class that the editor assigns only to that block. The .as-check code above works as a control template: it is reversible, does not modify WordPress core, does not require theme edits, and does not touch critical data.
Add this kind of adjustment as CSS custom code only after confirming where the plugin outputs CSS in your installation. Check the result at desktop and mobile widths, then disable the item. If the block returns to its original appearance without other side effects, you can apply the approach to a real class. Rollback always consists of deactivating the specific CSS item, not editing WordPress or theme files.
Advanced Scripts troubleshooting: symptoms, causes, checks, and recovery
When a problem occurs, do not enable and disable every item one after another. First name the symptom, then isolate the type and scope. One CSS item rarely explains an inaccessible admin area, and a PHP item is not necessarily related to a missing external stylesheet. The cases below follow from the plugin's official documentation, WordPress hooks, and typical practical examples.
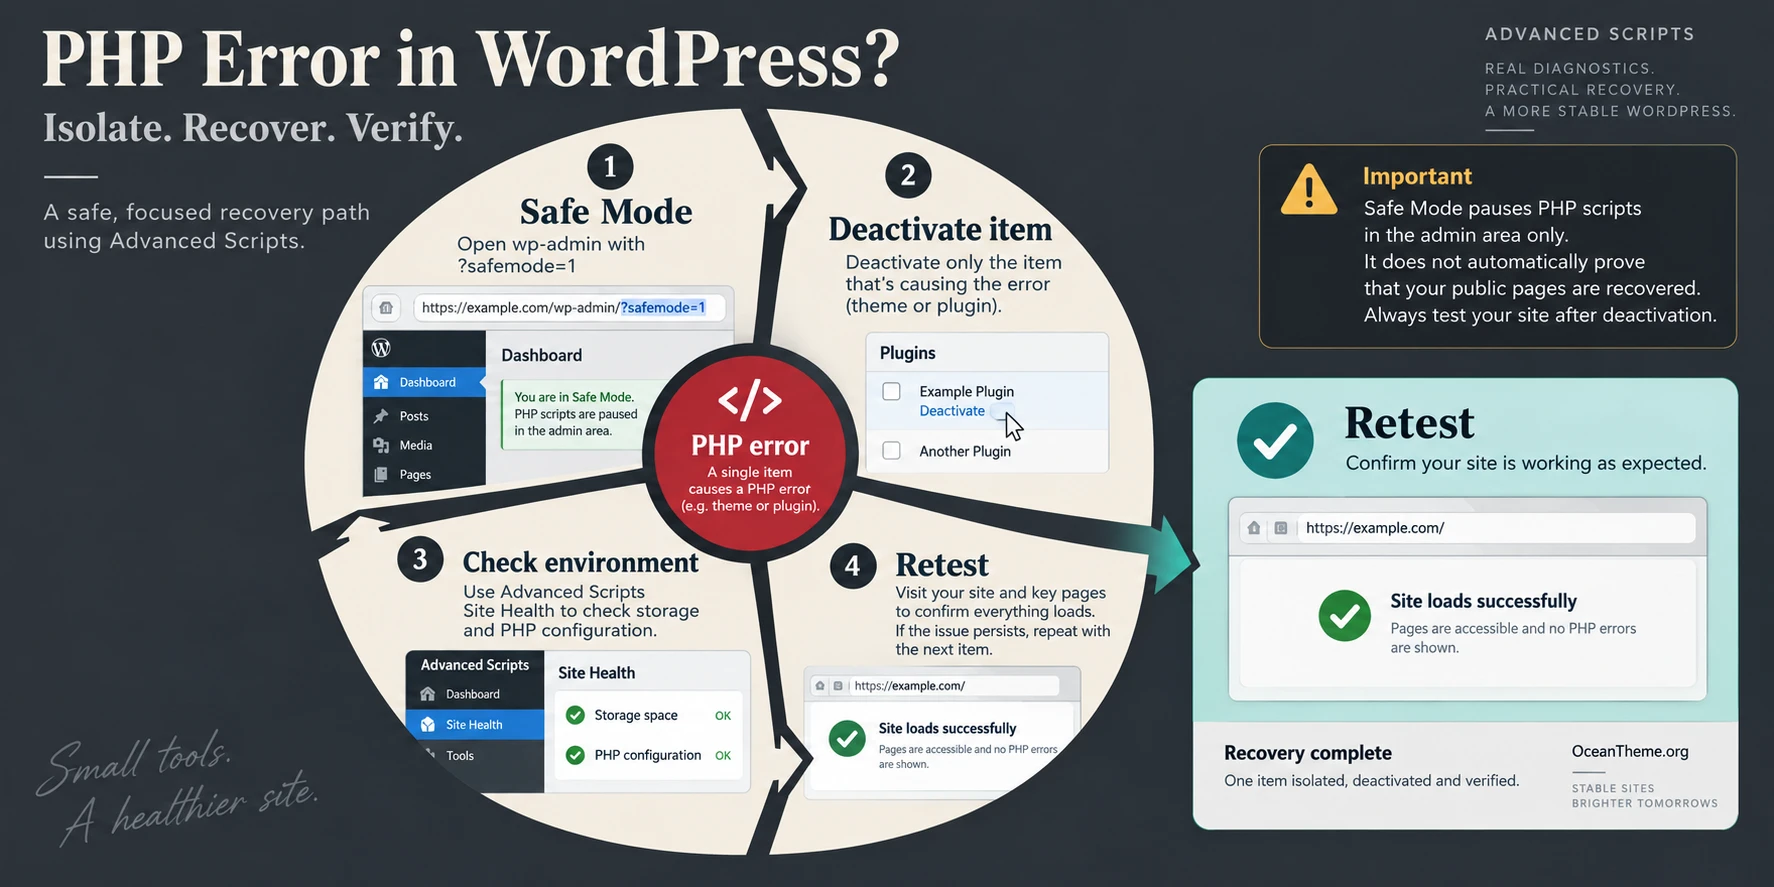
The admin area becomes inaccessible after a PHP snippet
Symptom: after enabling a PHP item, a critical error or white screen appears, or you cannot open the normal interface to disable the item. Likely cause: a syntax error, a call to an unavailable function, an incorrect hook, or logic that runs in the administrative context differently than expected.
What to check: do not add a second "fixing" snippet. Official Clean Plugins support provides a way to enable Safe Mode manually: append ?safemode=1 to the admin URL, for example /wp-admin/?safemode=1. After opening the panel, find the most recent PHP item and deactivate that exact item. Immediately save the error text or the relevant log entry on a staging copy.
Limitation and fix: Support also clarifies that Safe Mode disables PHP script execution only inside the admin area. It is not a guaranteed fix for the public site. If the public error remains, do not consider the task resolved: use a backup, standard hosting file access, or developer support. After recovery, reduce the problematic snippet to the smallest case and repeat testing on a staging copy. Rollback means leaving the item disabled until the cause is clearly understood.
CSS or JavaScript does not appear on the required page
Symptom: the item is marked active, but the style does not change or the client-side feature does not start. Likely cause: an incorrect Location, hook, or condition; cached old HTML; a URL error; missing markup; or a conflict with a theme resource. What to check: find the CSS/JS URL in the source, confirm a successful response in Network, and inspect JavaScript messages in the Console.
Fix: start with one variable. If the file is absent from the source, check scope, condition, and hook. If the file is present but the style does not apply, inspect the CSS cascade and selector. If the JavaScript file is present but the function does not work, check dependency order and the DOM. For the tutorial combination, start with CSS in wp_head and JS in wp_footer, but change these values only for a clear reason. Rollback means disabling only the resource that failed verification and clearing the cache you manage.
A library or tracker fires twice on the site
Symptom: a modal opens twice, an analytics event is duplicated, a tag appears repeatedly in the source, or the Console reports repeated initialization. Likely cause: the previous source remains in the theme, another header/footer tool, the builder, or an old snippet plugin. What to check: search for the unique URL, container identifier, or global JavaScript variable name in the HTML source and in the list of active extensions.
Fix: select one source of truth for the specific resource. On a staging copy, disable the old placement while leaving Advanced Scripts active, then run a negative test. Do not change the URL, condition, and initialization code at the same time, or the duplicate may disappear accidentally while the cause remains. Rollback means restoring one previously verified source and keeping the other disabled until the inventory is complete.
SCSS does not compile or an import points to the wrong place
Symptom: after saving, there is no expected CSS, variables remain in the final file, or the style does not appear. Likely cause: a syntax error, a mismatched partial name, an incorrect import rule, or a duplicate title. The official overview contains an important detail: an SCSS partial name is generated from its title, and identical names are not allowed. What to check: return to one partial and one main item, verify the import rule shown by the interface, and confirm that names are unique.
Fix: temporarily remove nested imports, save a minimal set of tokens and one selector, then add one rule at a time after successful compilation. Do not try to solve the error by replacing SCSS with PHP or copying the entire text into the theme. Rollback means deactivating the main SCSS item and then fixing the partial separately on a staging copy.
PHP items behave inconsistently after migration or an update
Symptom: previously working snippets no longer run, edits do not save, or an error appears after hosting changes. Likely cause: an issue with the storage directory, write permissions, or an old temporary mechanism, not necessarily an error in the PHP itself. What to check: open WordPress Site Health and locate the Advanced Scripts check results. The official overview says it tests the directory's existence and availability, index files, and the creation, execution, and deletion of PHP files.
Fix: record the exact message and pass it to whoever manages the server. Do not assign broad permissions to the entire content directory or delete old files automatically. If storage status is normal, move to a reduced test of the PHP itself. Rollback means disabling only the suspicious item and not migrating the rest until predictable behavior has been restored.
The site still shows the old state after saving
Symptom: new code is already active in Advanced Scripts, but visitors still see the previous page. Likely cause: browser, page, CDN, or CSS/JS optimizer caching, or testing while signed in as an administrator. What to check: open the URL in a private window, then search for the resource in the page source. If the source is new but behavior is old, the issue is more likely client-side cache or the cascade. If the source is old, investigate server cache or the condition.
Fix: clear only the cache you are responsible for and repeat the same URL. Then compare target and non-target pages. Do not add a second identical CSS/JS item to get a quick outcome. Rollback means keeping one verified version and disabling the experimental one.
A brief interface demonstration as support for your first setup
The official product page includes an Advanced Scripts video. It is useful not as a promotional break, but as visual support before creating the first item: you can connect the scripts list interface, editor, and overall configuration workflow with the steps in this guide. Watch it after preparing a test page and change map. Then the on-screen actions will feel less like a set of clicks and more like choices about type, location, and verification.
Do not look to the video for a universal PHP recipe or copy demonstrated code without a source. Your useful goal is to see what the product workflow looks like, then repeat it with your own safe CSS test. For the question "how do I use Advanced Scripts?", this helps connect field names with a practical outcome more quickly.
Questions that come up when using Advanced Scripts
Can I store PHP, CSS, and JavaScript in Advanced Scripts?
Yes. The official product page lists PHP, CSS, JavaScript, HTML, SCSS, and LESS. However, do not combine different types into one item unless necessary. Each type requires its own verification, scope, and rollback method. In practice, it is more convenient to create several related items with a shared naming prefix than one large fragment that mixes styles, client-side code, and server-side code.
Where should CSS and JavaScript be placed?
For external resources, a specialized Advanced Scripts example uses CSS on the public site with wp_head and JavaScript with wp_footer. This is a solid, testable starting point because WordPress outputs wp_head in the head and wp_footer before the body ends. However, the final location depends on the library and theme requirements. Always verify that the hook is present in your theme, the file loads, and the action works without errors.
Why is an active item not visible to visitors?
First rule out caching, then check the condition, location, and hook. In a private window, open the page source and Network. If the resource is absent, the configuration did not reach the document. If the resource is present but has no effect, investigate the CSS cascade, JS order, or whether the selector matches the actual markup. Do not add a duplicate until the reason for the first item is understood.
Will Safe Mode help if PHP breaks the site?
Safe Mode is designed for this type of recovery. Official support recommends opening the admin URL with the ?safemode=1 parameter to regain access and disable the problematic PHP item. However, according to the developer's clarification, this mode disables PHP script execution only inside the admin area. If the public site remains broken, use a backup or standard file access and do not consider temporary admin access to be a final fix.
Should I enable debugging on a live site?
No, not as a routine testing method. Official WordPress documentation recommends debugging tools for local or staging environments. If you need to find a PHP cause, enable logging and inspect the error where messages will not reach visitors. In production, begin with reversible rollback, Site Health, and a targeted check of the most recently changed item.
Can I import someone else's JSON snippet?
Technically, the Advanced Scripts ecosystem includes JSON import examples. For example, a third-party developer provides JSON for installation through the import feature and separately reminds users to activate the snippet afterward. But importing does not make third-party code safe or compatible. Before enabling it, read the source, check theme/builder dependencies, scope, and hook, then test it on a copy. If you do not understand the purpose of every part, do not activate the item.
When should I choose SCSS instead of regular CSS?
Choose SCSS when you have repeated tokens, several logically related components, and someone who will maintain the partial structure. For one outline or color, regular CSS is simpler. After enabling SCSS, always inspect the compiled output in the browser, not just the absence of an editor message.
Is Advanced Scripts suitable for every WordPress change?
No. It is suitable for managed snippets and resources with a clear scope. Larger functionality with user settings, data storage, a complex integration, or critical financial processes is better implemented as a separate plugin or a development project with tests. This reduces the risk that one code editor becomes the only opaque location for important site behavior.
When Advanced Scripts is the right choice
Advanced Scripts earns its place in a WordPress project when you want to keep understandable PHP, CSS, JavaScript, HTML, and preprocessor styles in one managed location, while treating every item as a small release. Its strongest use cases include targeted resource loading, hook-based work, a clean structure for small enhancements, SCSS partials, and style alignment with Oxygen where that integration is in use.
Start not with a large PHP fragment, but with a reversible CSS test. Then learn the type - location - hook - condition - verification workflow on one page. Once that route becomes familiar, you can work more safely with external files, HTML fragments, and advanced hooks. If you have prepared a backup access path, checked Site Health, understand the Safe Mode limitation, and documented rollback, you can download the latest version of Advanced Scripts and repeat the first use case on a staging copy of your site.

